

CVE-2026-0073
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
android-securityauthenticationcryptography+5
umarrehmansiddiqui/cve-2026-0073Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 abraxas/openmeetings-remember-me-password
Apache OpenMeetings 9.1.0 - High - Remote - ATO - remember-me cookie replay authenticates without password
 abraxas/pfsense-api-enroll-autoadd
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - Paramiko AutoAddPolicy enroll
 abraxas/vsftpd-ssl-data-any-ticket
vsftpd 3.0.5 - High - Remote - Privilege leftover - FTPS data accepts any resumed ticket
 murrez/cve-2026-100835
Python PoC for CVE-2026-100835: audits Contrast manifests for AllowedChipIDs/AllowedPIIDs, detects versions, and probes Coordinator endpoints to…
 abraxas/cve-2026-19445-sni-uaf
Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
 openssh/openssh-portable
Portable OpenSSH
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 tpdlshdmlrkfmcla/openssl_dtls_cve_2014_0221
OpenSSL DTLS CVE-2014-0221 Remote Denial
 mbhudson/cve-2020-1971
CVE-2020-1971 Auto Scan & Remote Exploit Script. Auto Local Scan & Patch Script.
 crimsonfiedofficial/cve-2026-29114
Dahua CVE-2026-29114
 shoucheng3/apache__activemq_cve-2020-11998_5-15-12
Exploit for CVE-2020-11998 targeting Apache ActiveMQ 5.15.12, enabling remote code execution via crafted messages to the vulnerable message broker.
 blacklanternsecurity/dp_cryptomg
Another tool for exploiting CVE-2017-9248, a cryptographic weakness in Telerik UI for ASP.NET AJAX dialog handler.
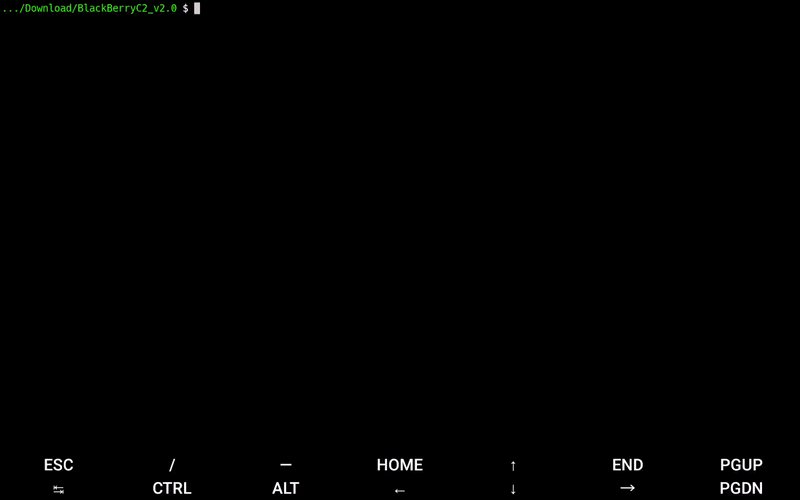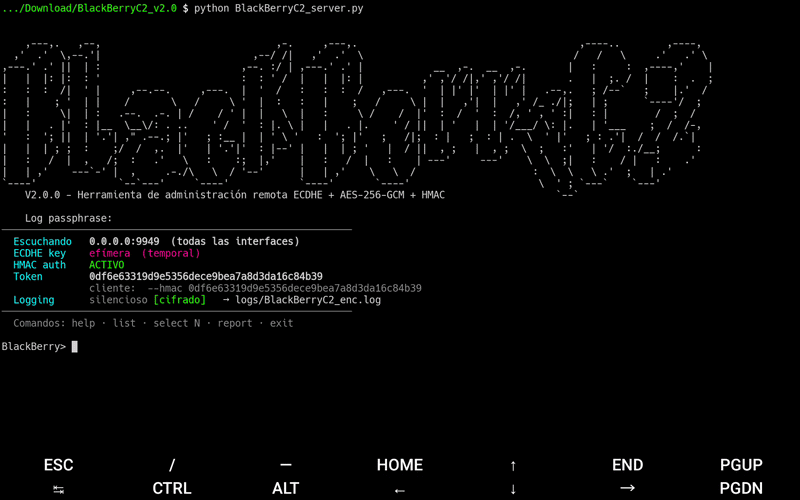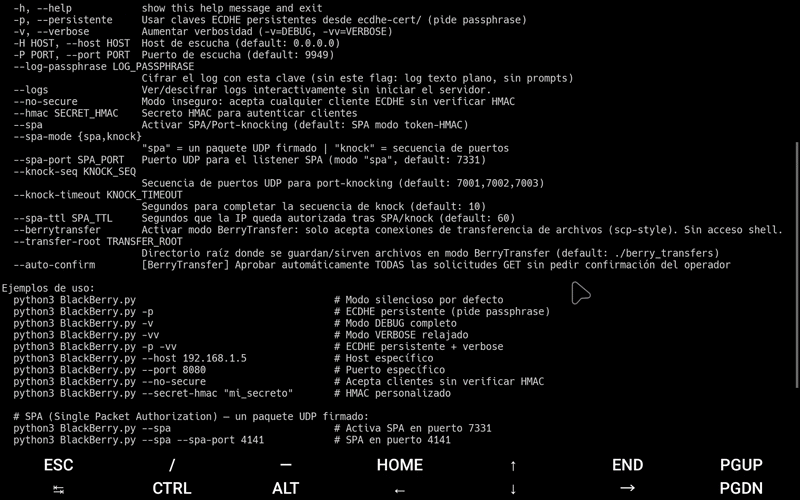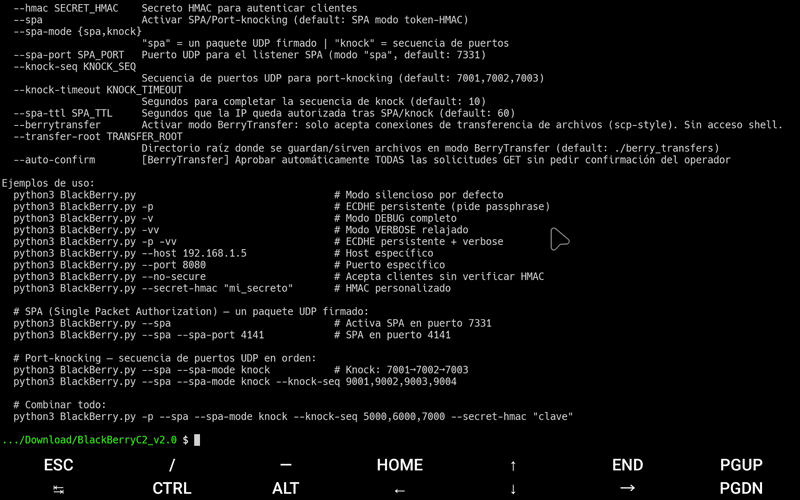 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
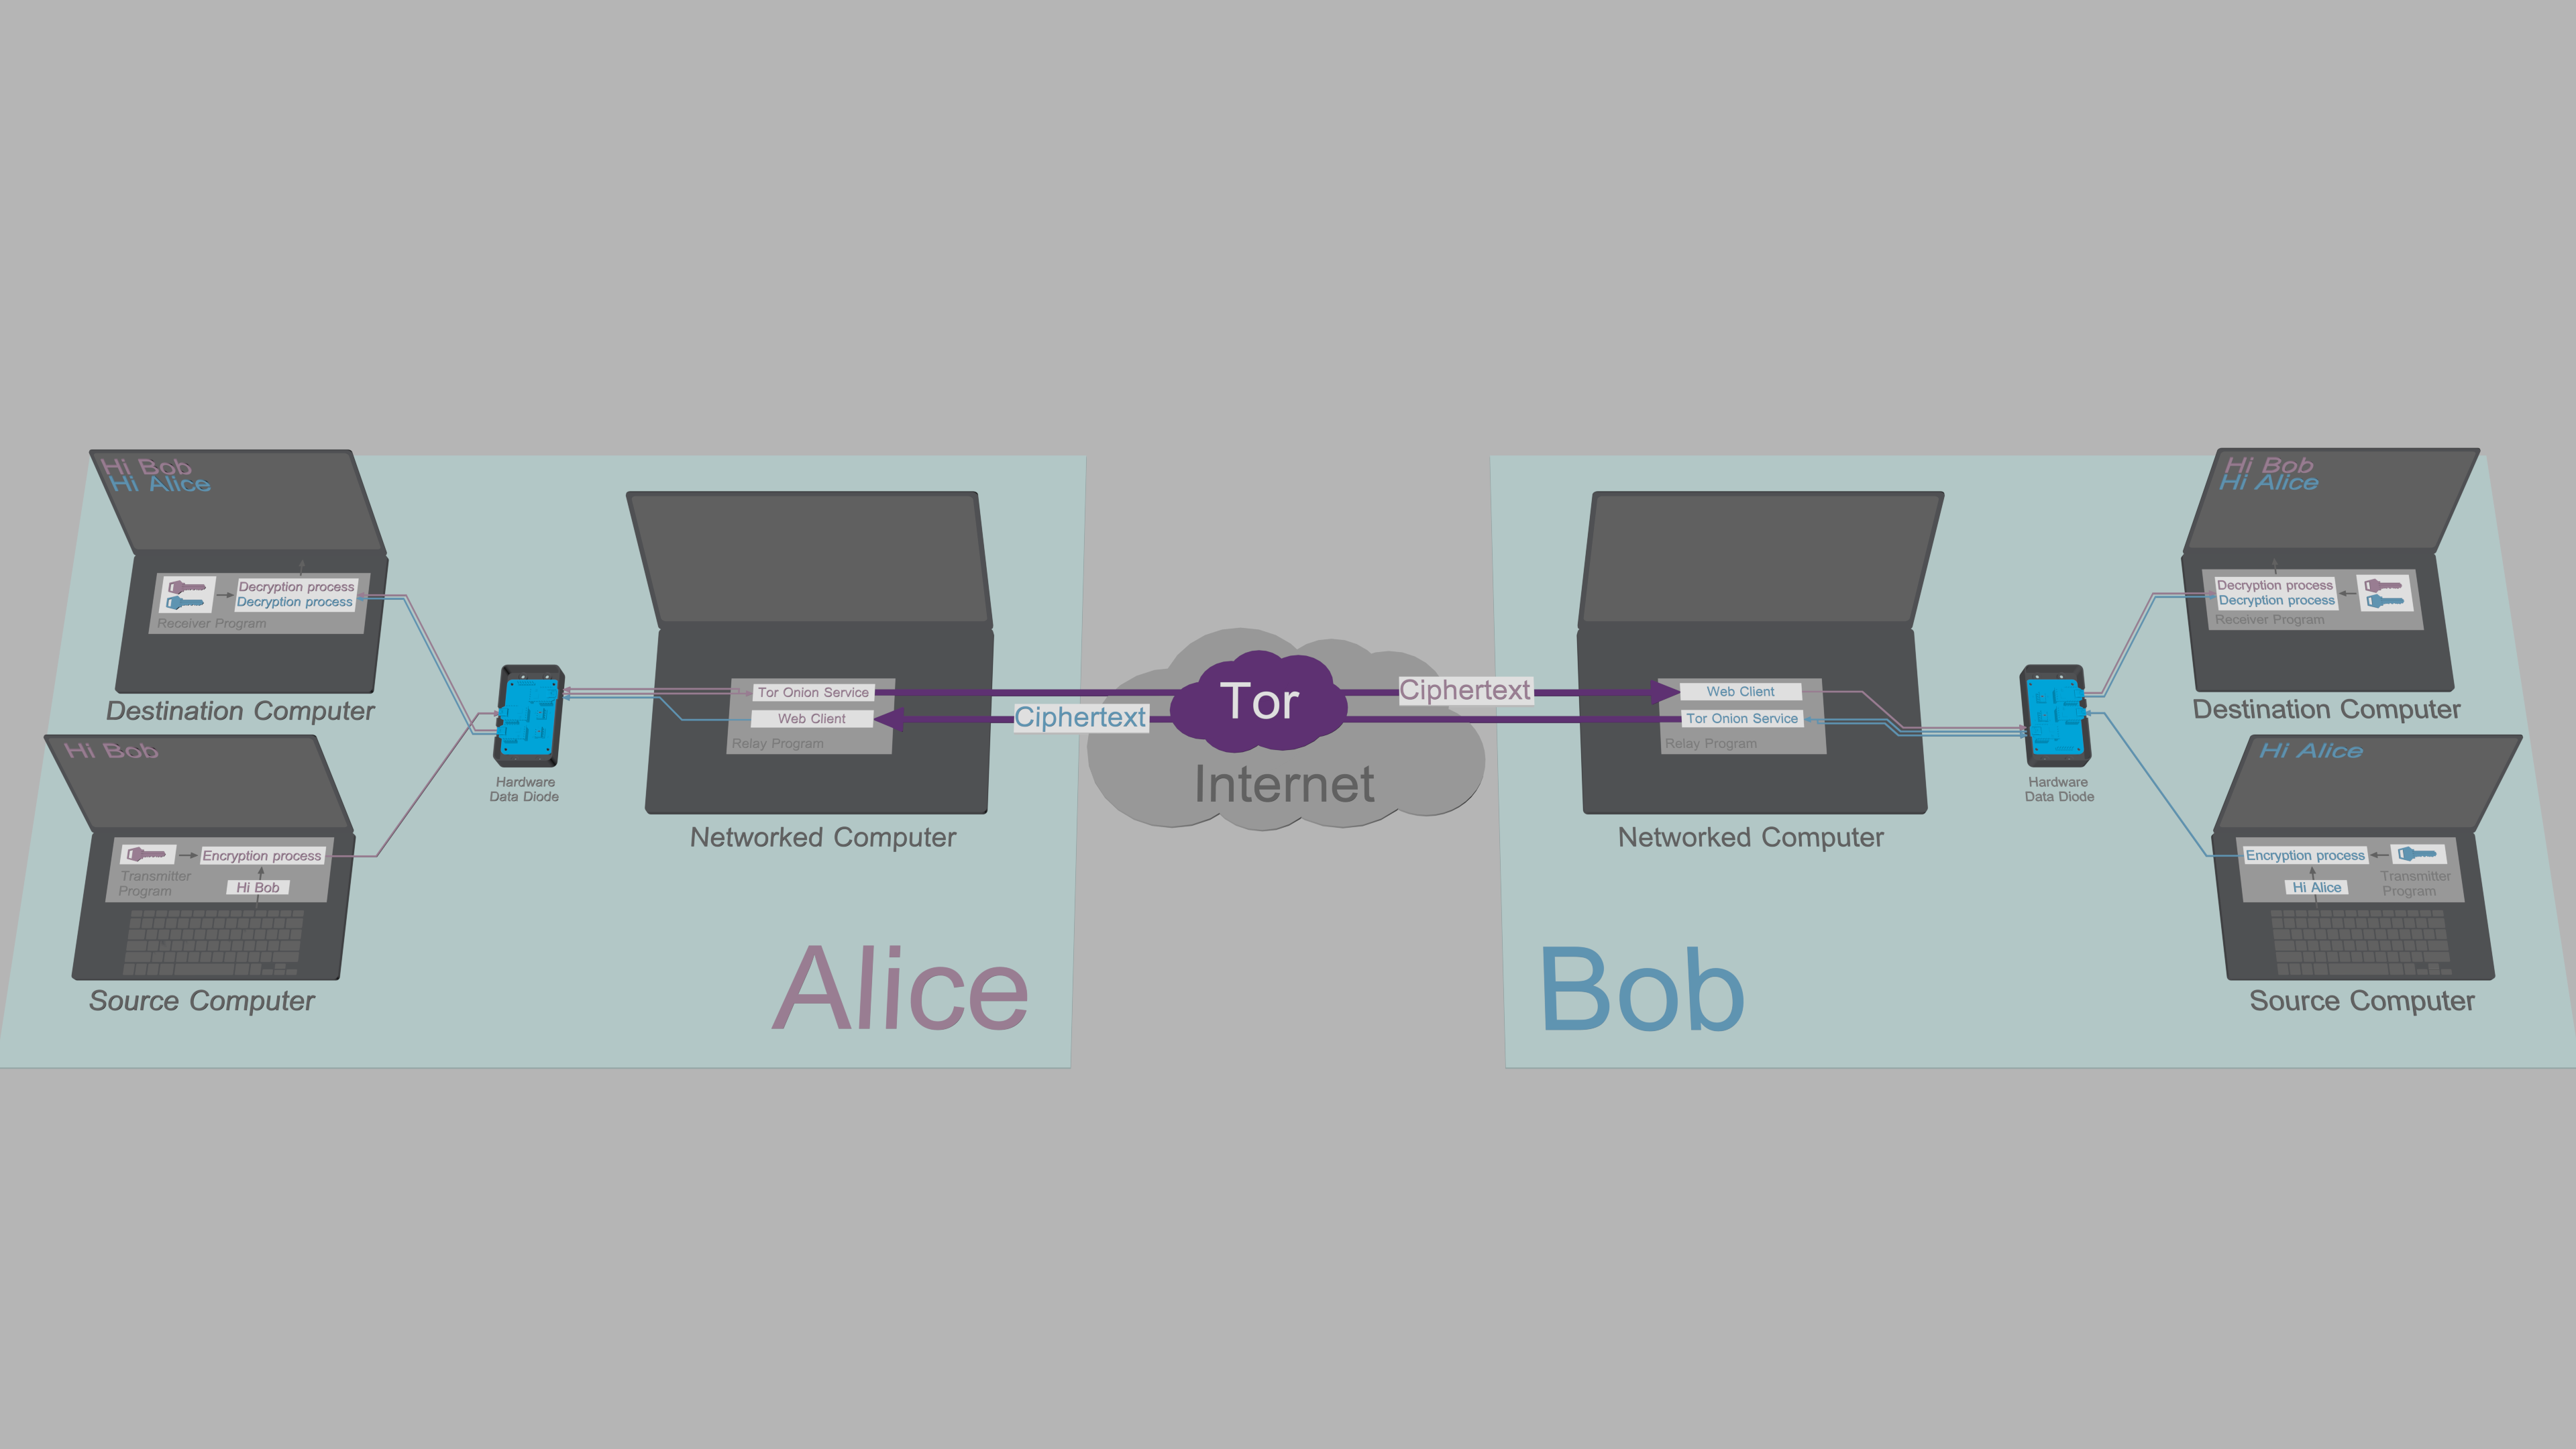 maqp/tfc
Tinfoil Chat - Onion-routed, endpoint secure messaging system