
emudhra-weak-keys
 corelight/emudhra-weak-keys
A Zeek package that detects when compromised eMudhra intermediate certificates are used in TLS 1.2 and below.
cryptographydefensive-toolsincident-response+4
corelight/emudhra-weak-keysA Zeek package that detects when compromised eMudhra intermediate certificates are used in TLS 1.2 and below.
 sigstore/root-signing
Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…
 cyrusimap/cyrus-sasl
Cyrus SASL API implementation providing client- and server-side authentication and authorization services via pluggable SASL mechanisms per RFC 4422.
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 signalapp/libsignal
Home to the Signal Protocol as well as other cryptographic primitives which make Signal possible.
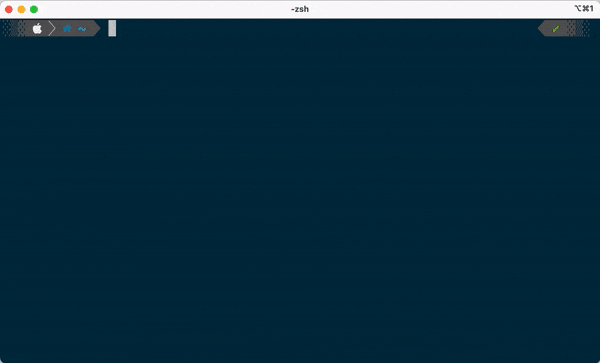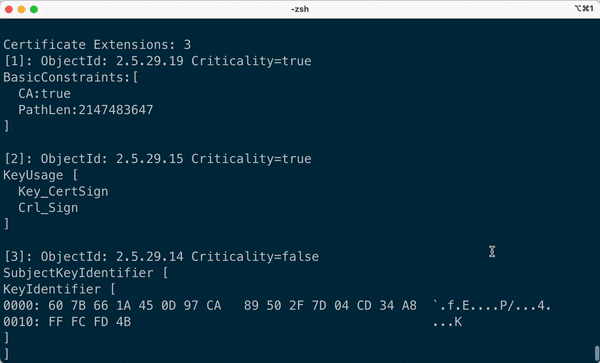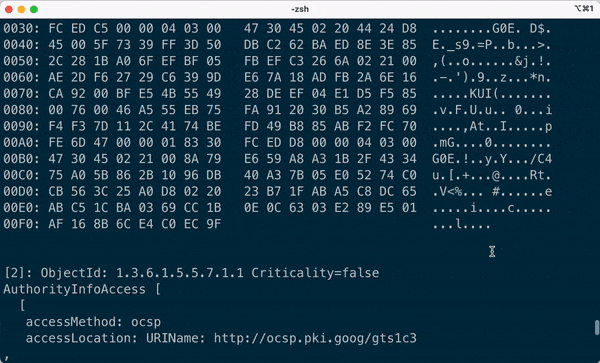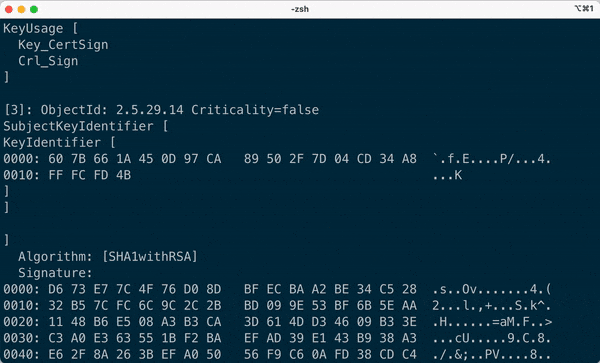 hakky54/certificate-ripper
🔐 A CLI tool to extract server certificates
 cybercentrecanada/cart
Python implementation of the CaRT library for (un)inerting files.
 mwielgoszewski/python-paddingoracle
A portable, padding oracle exploit API
 bishopfox/you-re-doing-iot-rng
Results and device code from the DEF CON 29 presentation "You're Doing IoT RNG"
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
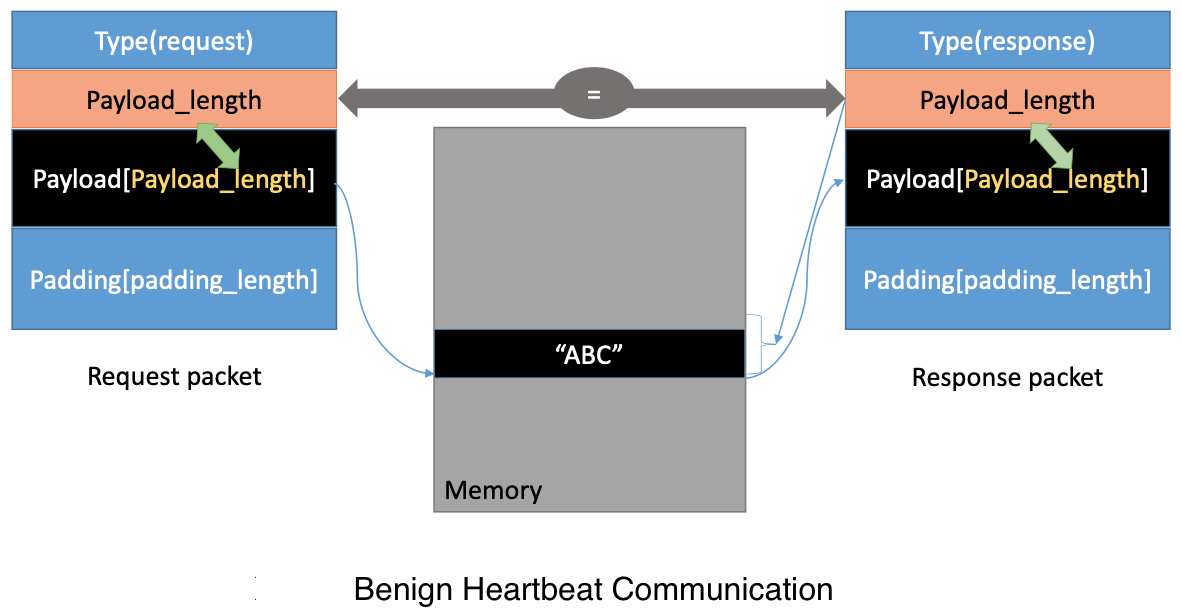 pierceoneill/bleeding-heart
The Heartbleed bug `CVE-2014-0160` is a severe implementation flaw in the OpenSSL library, which enables attackers to steal data from the memory of…
 stigtsp/cve-2019-6690-python-gnupg-vulnerability
Proof-of-concept exploit for CVE-2019-6690, demonstrating input validation bypass in python-gnupg symmetric encryption via newline injection in…
 apsdehal/awesome-ctf
A curated list of CTF frameworks, libraries, resources and softwares
 aprkr/cve-2023-48034
Weak encryption in Acer Wireless Keyboard SK-9662 allows attacker in physical proximity to both decrypt wireless keystrokes and inject wireless…
 ally-petitt/cve-2024-27632
CVE-2024–27632 Reference
 yoanndqr/cve-2020-0601
CurveBall CVE exploitation
 sharadkumar97/osint-spy
Performs OSINT scan on email/domain/ip_address/organization using OSINT-SPY. It can be used by Data Miners, Infosec Researchers, Penetration Testers…
 viperbluff/waf_buster
Disrupt WAF by abusing SSL/TLS Ciphers