
jwt_tool
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
api-securityapi-security-testingcryptography+5
ticarpi/jwt_tool:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 d-xuan/cve-2024-52510
Proof-of-concept exploit for CVE-2024-52510 demonstrating signature bypass in Nextcloud's E2EEv2 protocol, enabling server-side decryption of…
 openvpn/openvpn
Secure tunneling daemon implementing VPN protocols with TLS encryption, certificate authentication, and routing/firewall configuration for private…
 opennhp/opennhp
A lightweight, cryptography-powered, open-source toolkit built to enforce Zero Trust security for infrastructure, applications, and data in the…
 iangcarroll/cookiemonster
Decodes and unsigns vulnerable session cookies from Django, Flask, Laravel, Express, and JWT frameworks. Supports HMAC-based decoders, base64…
 c0r0n3r/dheater
Proof-of-concept denial-of-service tool that exploits the DHEat attack (CVE-2002-20001) by enforcing Diffie-Hellman key exchange against TLS and SSH…
 openpcc/openpcc
An open-source framework for verifiably private AI inference
 filosottile/heartbleed
A checker (site and tool) for CVE-2014-0160
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 getsops/sops
Simple and flexible tool for managing secrets
 infisical/infisical
Infisical is the open-source platform for secrets, certificates, and privileged access management.
 scopeblind/scopeblind-gateway
Ed25519 signed receipts + Cedar policies for AI agents. Finance mandate gate (Legate), proof packs, 3 IETF Internet-Drafts. npx protect-mcp
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port
 mrash/fwknop
Single Packet Authorization > Port Knocking
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 chelof100/acp-framework-en
Agent Control Protocol (ACP) — Official English specification. Cryptographically verifiable authorization architecture for autonomous AI agents.
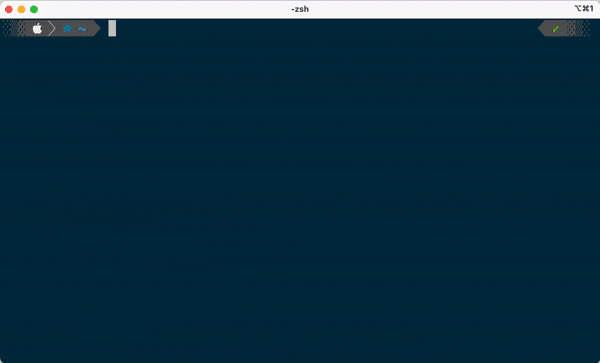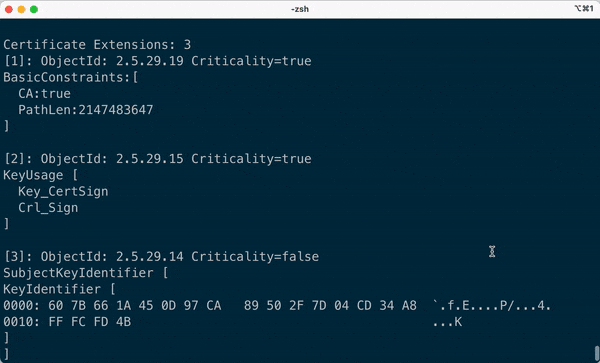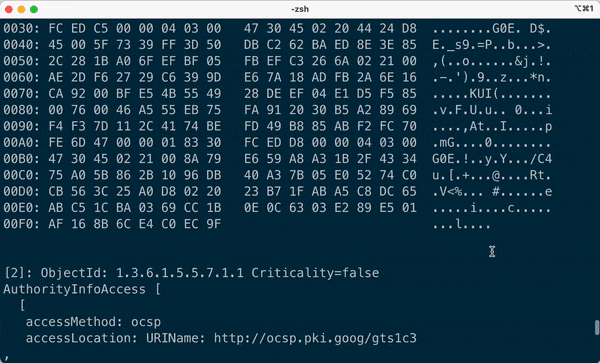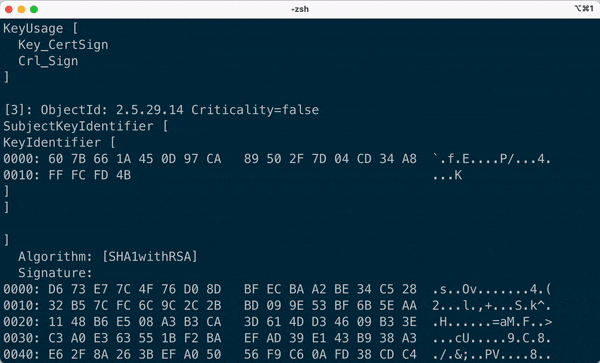 hakky54/certificate-ripper
🔐 A CLI tool to extract server certificates
 liamg/pax
:skull: :unlock: CLI tool for PKCS7 padding oracle attacks