Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Disrupt WAF by abusing SSL/TLS Ciphers

Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…

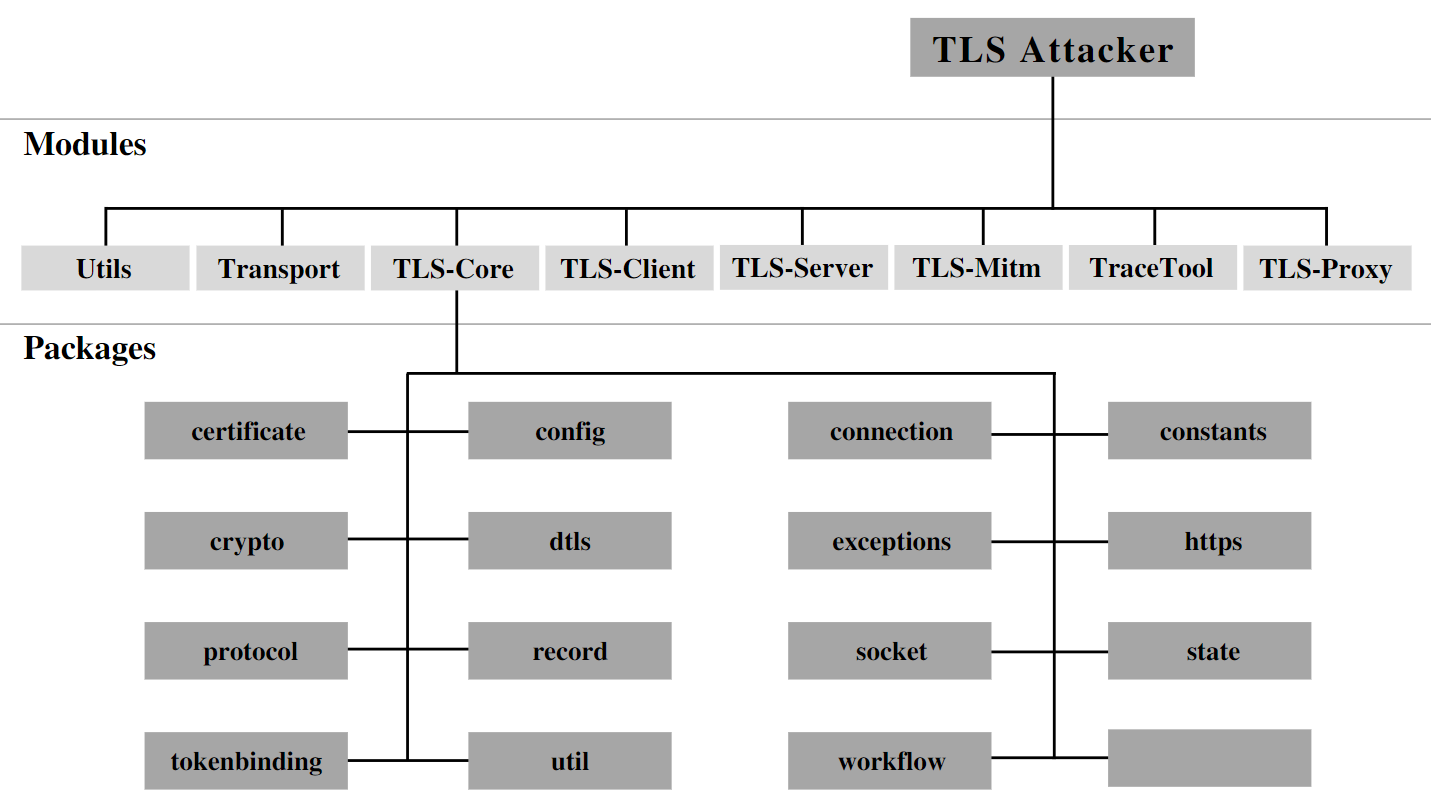
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…

:skull: :unlock: CLI tool for PKCS7 padding oracle attacks

Improper Certificate Chain Validation in EagleEyes Lite Android Application

Proof-of-concept exploit that recovers the site_key for OSSN 5.3 and above, exploiting CVE-2020-10560 arbitrary file read vulnerability.

Multithreaded Padding Oracle Attack on Oracle OAM (CVE-2018-2879)

Exploit for CVE-2024-5124 targeting ChuanhuChatGPT via TLS timing side-channel attack. Uses tlsfuzzer to perform character-by-character credential…

RememberMe Padding Oracle Vulnerability RCE