
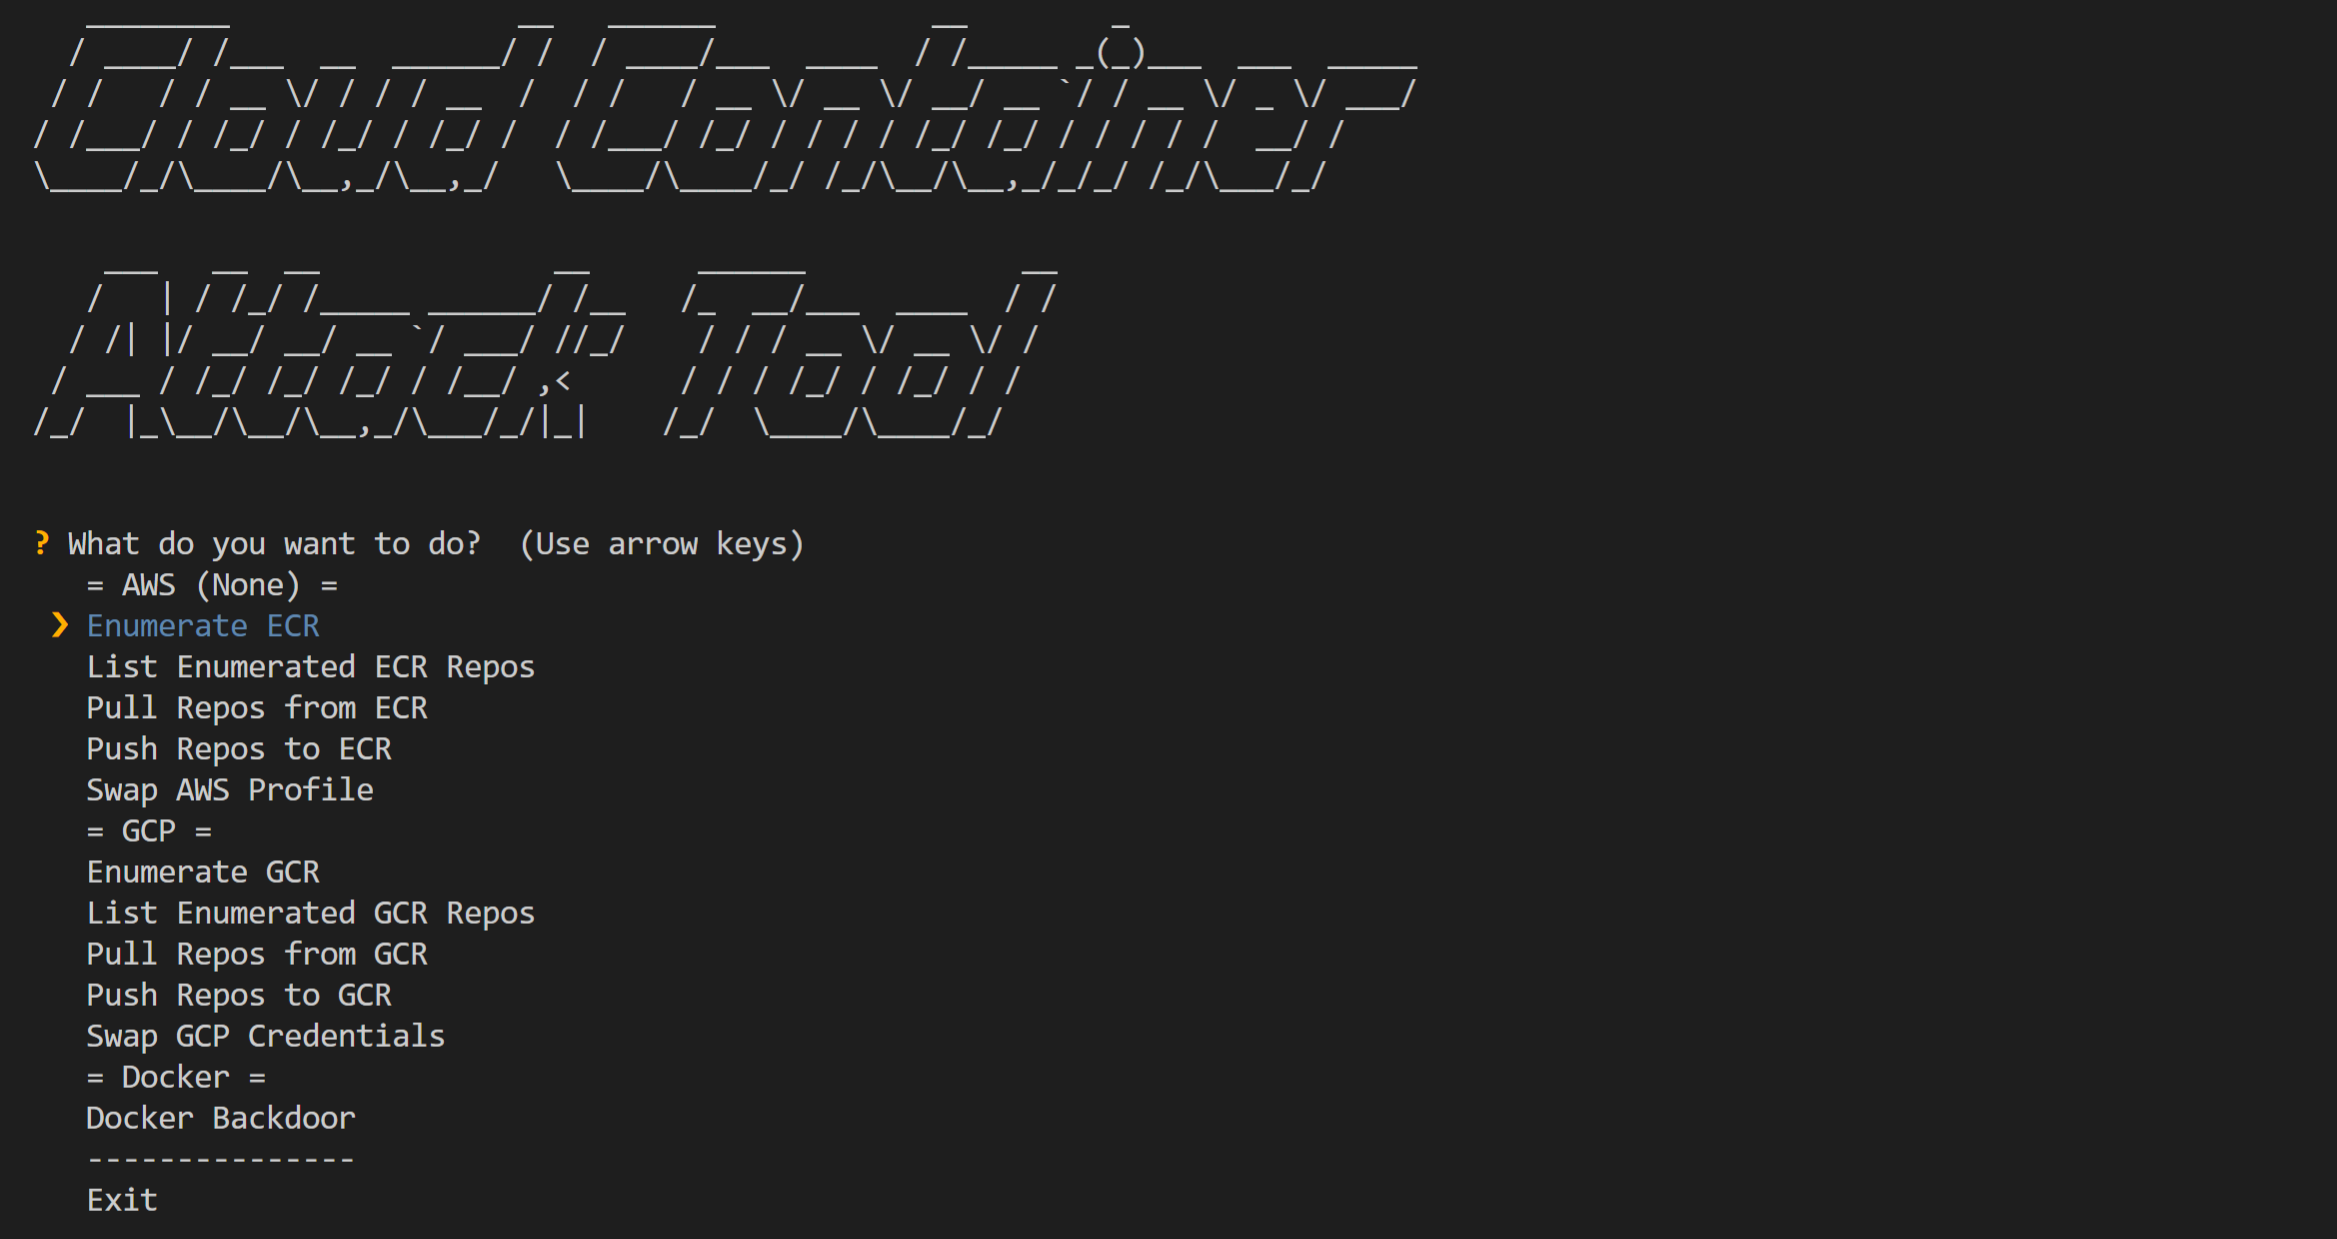
ccat
 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
cloud-securitycontainer-securityexploitation+1
653
rhinosecuritylabs/ccatCloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 cved-sources/cve-2015-8103
Docker container for CVE-2015-8103 exploitation targeting JBoss, part of a vulnerable container management framework for security testing.
 cved-sources/cve-2019-6340
Docker container for CVE-2019-6340 exploitation lab, part of the Cved vulnerable container management framework for practicing Drupal security…
 cved-sources/cve-2017-8046
Docker-based vulnerable environment for CVE-2017-8046 Spring framework remote code execution exploit, part of the Cved vulnerable container…
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
 cved-sources/cve-2017-10271
Docker container for CVE-2017-10271 (Oracle WebLogic RCE) used with Cved framework to manage and deploy vulnerable environments for security testing…
 cved-sources/cve-2018-1273
Docker container for CVE-2018-1273 exploitation lab, part of the Cved vulnerable environment management framework for security training and testing.
 cved-sources/cve-2014-0160
Docker container for CVE-2014-0160 (Heartbleed) vulnerability, part of the Cved framework for managing and deploying vulnerable environments for…
 cved-sources/cve-2019-9184
Docker container with a pre-configured vulnerable environment for CVE-2019-9184, designed for security testing and educational exploitation practice.
 cved-sources/cve-2018-3811
Docker container providing a vulnerable environment for CVE-2018-3811, designed for security testing and exploit practice within the Cved vulnerable…
 cved-sources/cve-2017-7529
Docker-based reproduction of CVE-2017-7529 (Nginx integer overflow) for security testing and education. Part of the Cved vulnerable container…
 cved-sources/cve-2017-4971
Docker-based vulnerable environment for CVE-2017-4971 (Spring WebFlow RCE) to practice exploitation and security testing in a controlled lab setup.
 cved-sources/cve-2017-1000486
Docker container providing a pre-configured vulnerable environment for CVE-2017-1000486, designed for security testing and exploit practice within…
 cved-sources/cve-2017-8917
Docker container reproducing Joomla vulnerability CVE-2017-8917 for security testing, education, and practice in a sandboxed environment.
 cved-sources/cve-2018-3810
Docker container providing a vulnerable environment for CVE-2018-3810, designed for security testing and educational exploitation practice within…
 cved-sources/cve-2018-9208
Docker container exploit for CVE-2018-9208, part of the Cved framework for managing and testing vulnerable containers in security labs.
 cved-sources/cve-2018-15961
Docker container for CVE-2018-15961, part of the Cved framework for managing and testing vulnerable Docker environments in security labs.
 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…