weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…

Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…

Deploy self-hosted AI coding agents (OpenClaw, Claude Code, Codex) into your AWS account with CloudFormation, IAM profiles, and sandbox isolation for…

Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.

An embeddable, portable, branchable virtual machine to safely run Agents locally.

Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Like Envoy xDS, but for eBPF filters

Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…

docker lab setup for kibana-7609

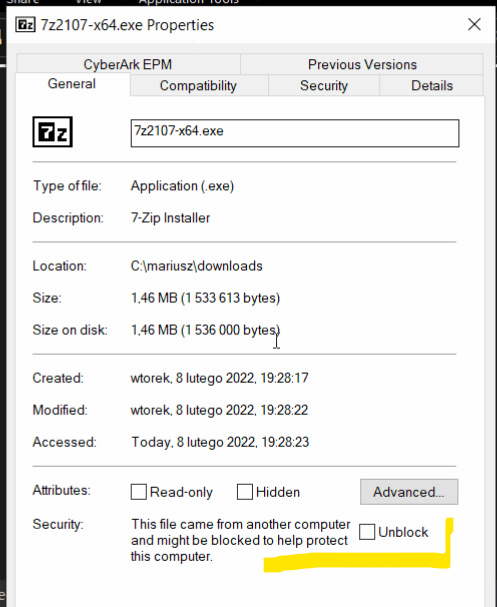
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…

Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…

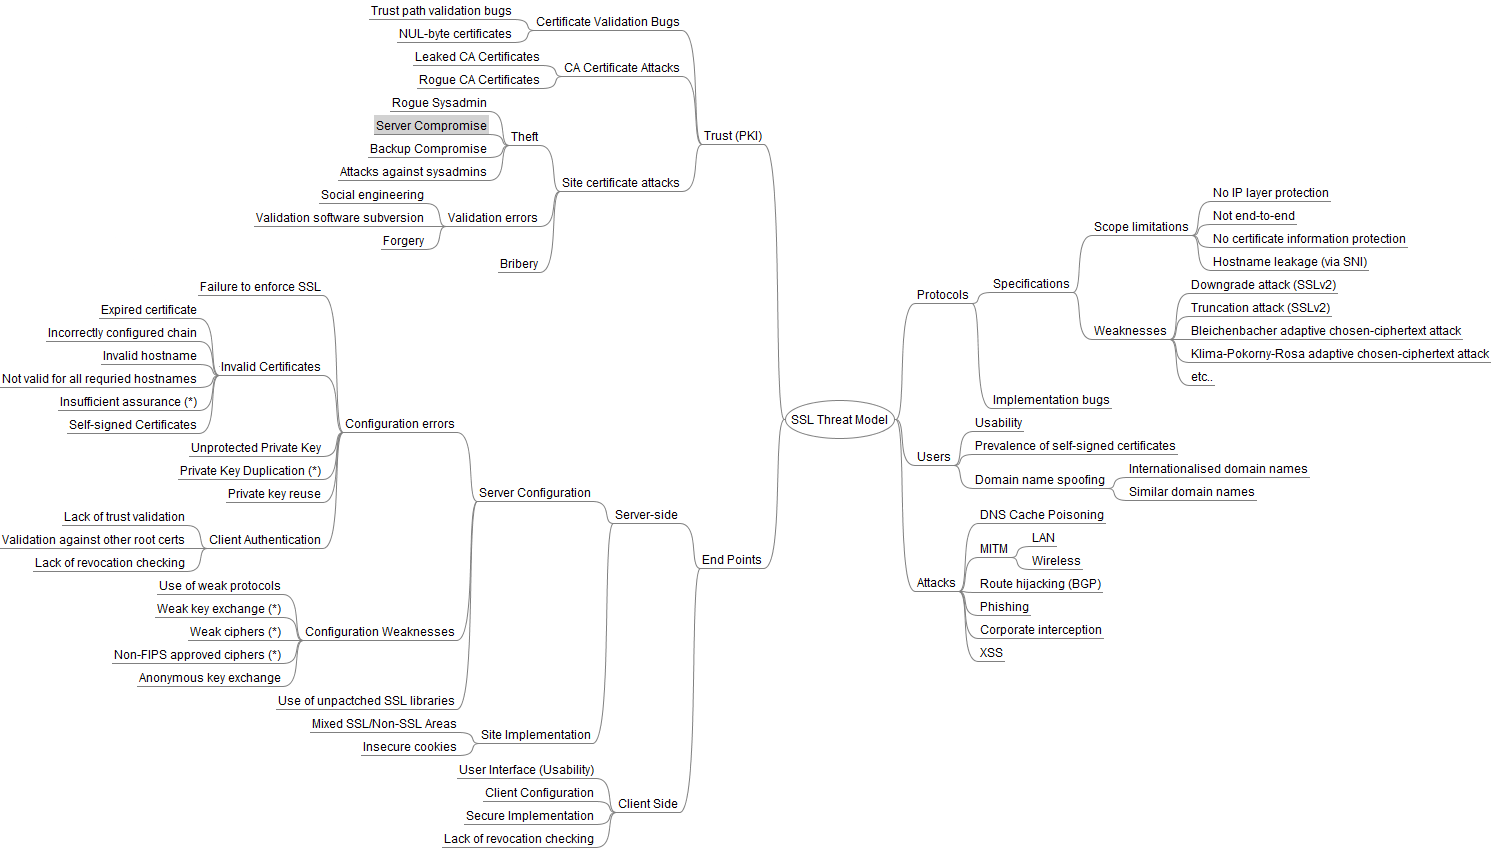
A collection of real-world threat model examples across various technologies, providing practical insights into identifying and mitigating security…

Cryptographically signed, replay-verifiable evidence layer for AI agents. Governs actions in the loop, produces Ed25519-signed receipts linked into a…

Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…

Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…

Cloud-native system telemetry pipeline that collects, processes, and exports system call events into a compact object-relational format for…

Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…

Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.