

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
16.5k
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
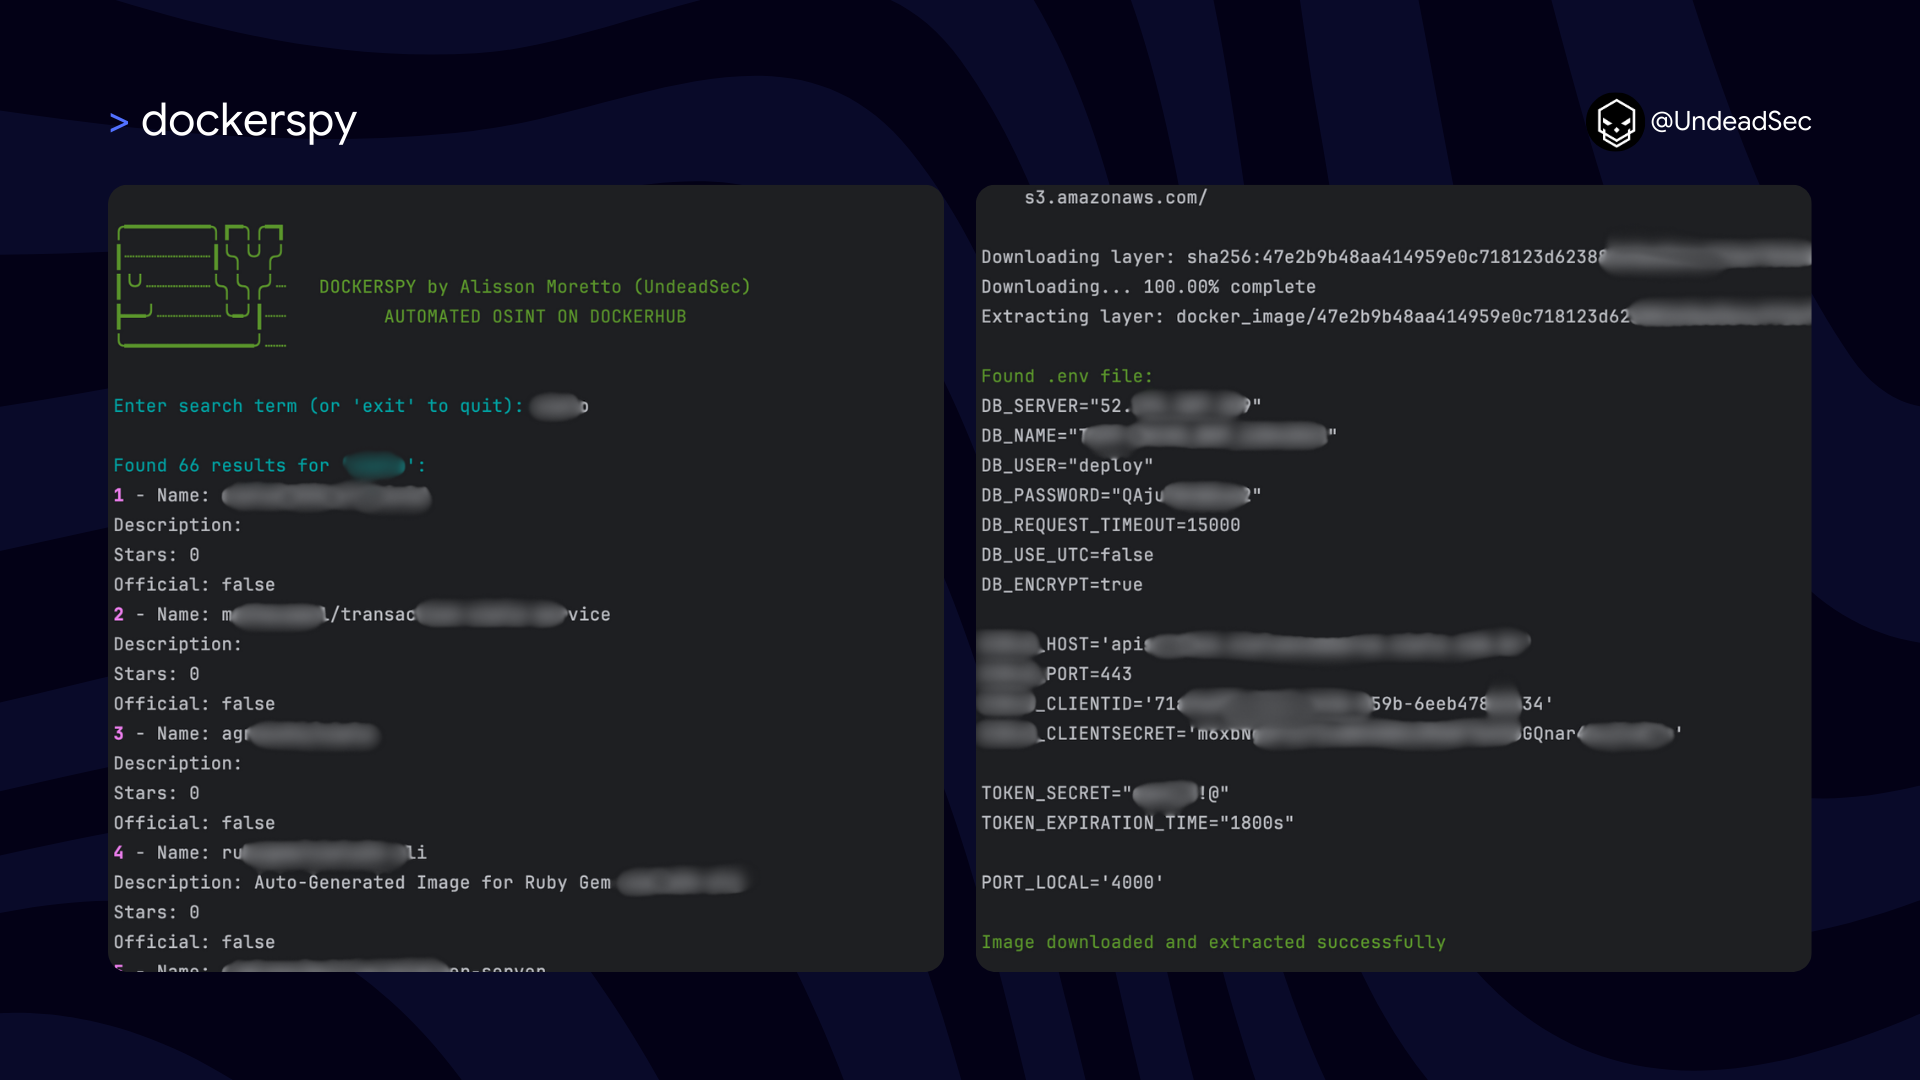 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
 cved-sources/cve-2017-8046
Docker-based vulnerable environment for CVE-2017-8046 Spring framework remote code execution exploit, part of the Cved vulnerable container…
 cved-sources/cve-2018-1273
Docker container for CVE-2018-1273 exploitation lab, part of the Cved vulnerable environment management framework for security training and testing.
 googlesky/cve-2026-126147
Containerised PoC and lab for CVE-2026-126147, an unauthenticated path traversal in the FortiMail management API that enables arbitrary file write…
 cved-sources/cve-2018-3811
Docker container providing a vulnerable environment for CVE-2018-3811, designed for security testing and exploit practice within the Cved vulnerable…
 cved-sources/cve-2017-7529
Docker-based reproduction of CVE-2017-7529 (Nginx integer overflow) for security testing and education. Part of the Cved vulnerable container…
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 cved-sources/cve-2015-8103
Docker container for CVE-2015-8103 exploitation targeting JBoss, part of a vulnerable container management framework for security testing.
 cved-sources/cve-2019-9194
Docker container with CVE-2019-9194 for practicing vulnerability exploitation in a controlled environment. Part of the Cved vulnerable container…
 cved-sources/cve-2016-9838
Docker container with CVE-2016-9838 for practicing vulnerability exploitation in a controlled environment, part of the Cved vulnerable container…
 cved-sources/cve-2019-6340
Docker container for CVE-2019-6340 exploitation lab, part of the Cved vulnerable container management framework for practicing Drupal security…
 boreas37/cve-2026-58455-poc
PoC for CVE-2026-58455: Dockwatch <=0.6.567 unauthenticated RCE. Stdlib-only Python.
 mnk-works/portainer-cve-2026-44848-checker
Non-destructive checker for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints