phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
authentication-authorizationcontainer-securitydata-exfiltration+7
76
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

A Dockerized setup for running a vulnerable CrushFTP 10 server instance (CVE-2024-4040).

Like Envoy xDS, but for eBPF filters

Log4Shell (CVE-2021-44228) docker lab

Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…

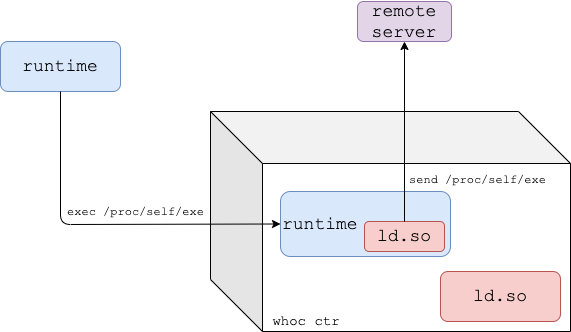
A container image that exfiltrates the underlying container runtime to a remote server

Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…