

teleport
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
api-securityauthentication-authorizationcloud-security+7
20.9k
gravitational/teleportThe easiest, and most secure way to access and protect all of your infrastructure.
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
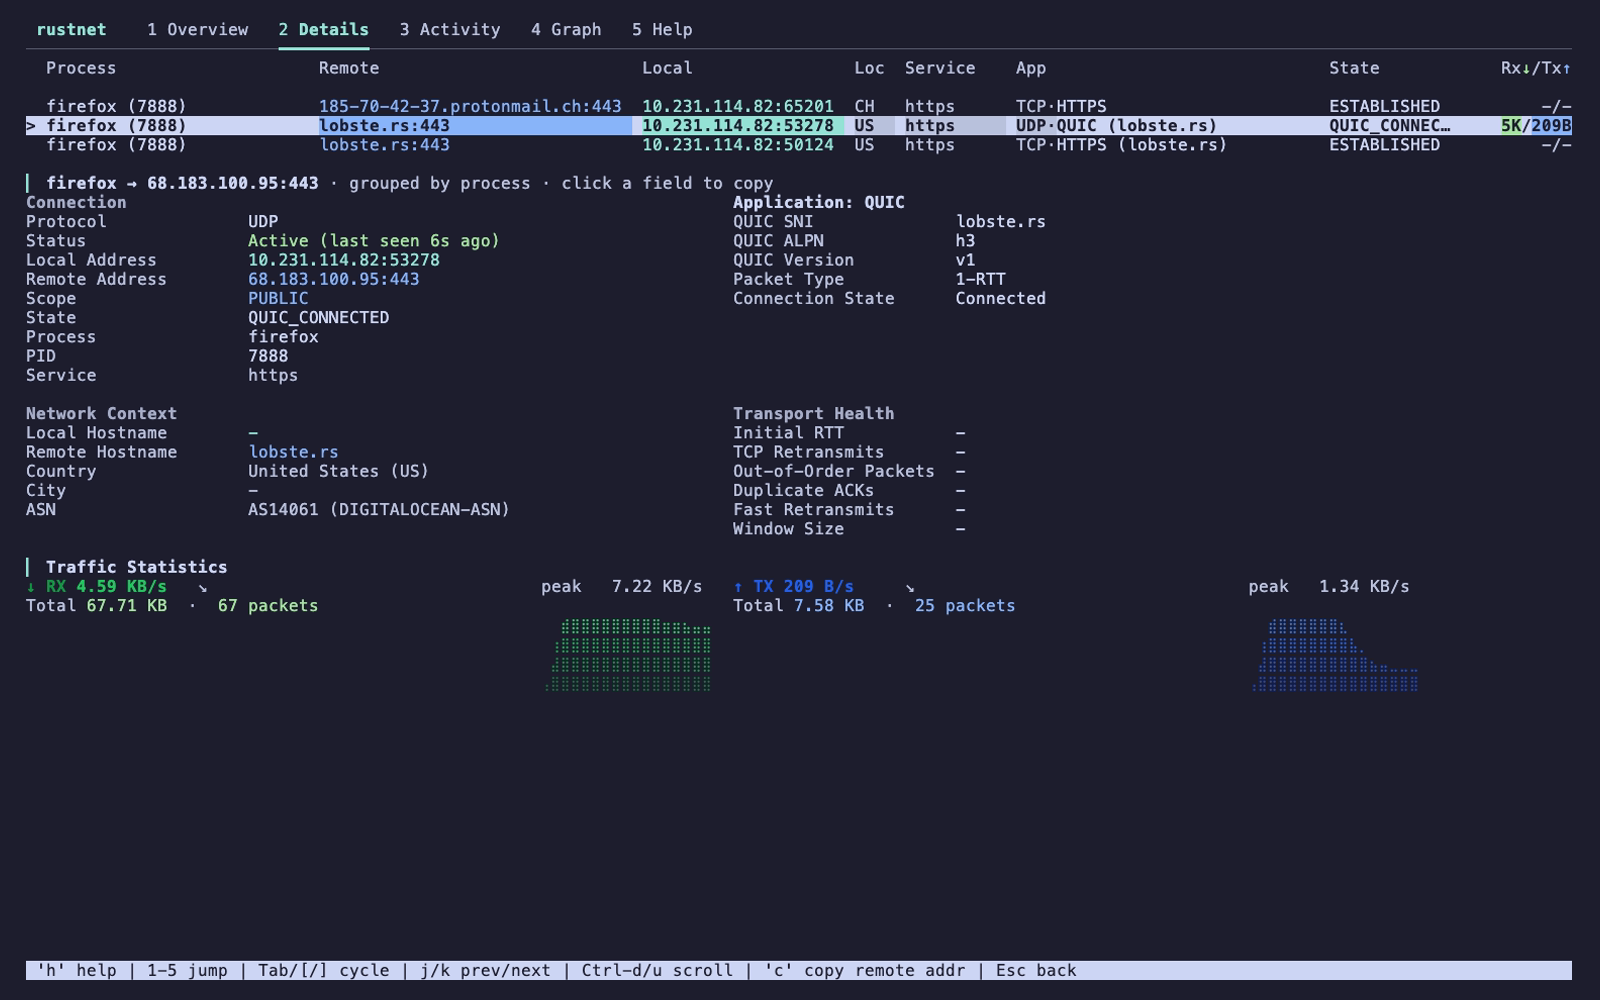 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
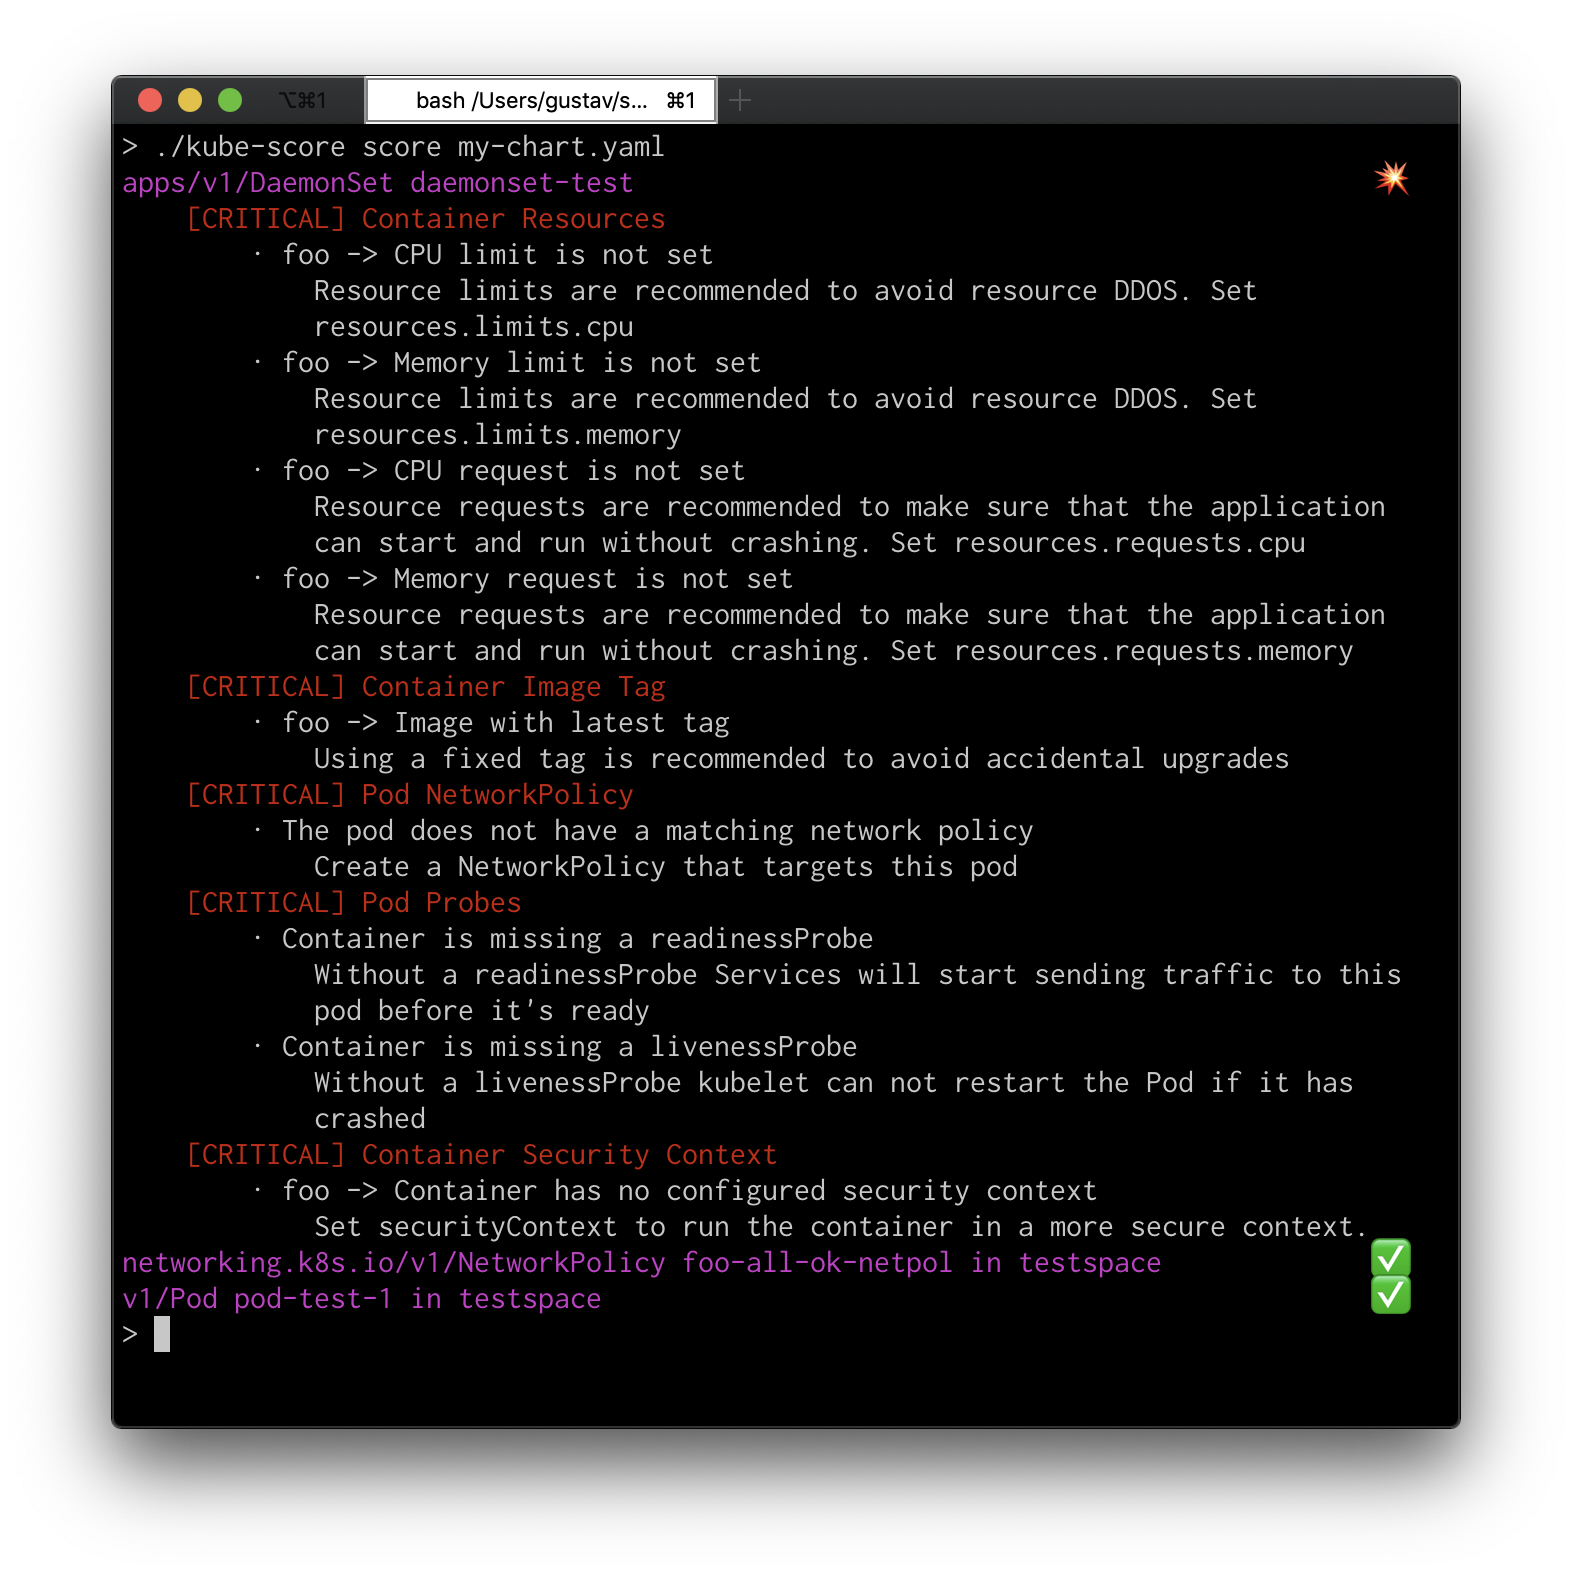 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
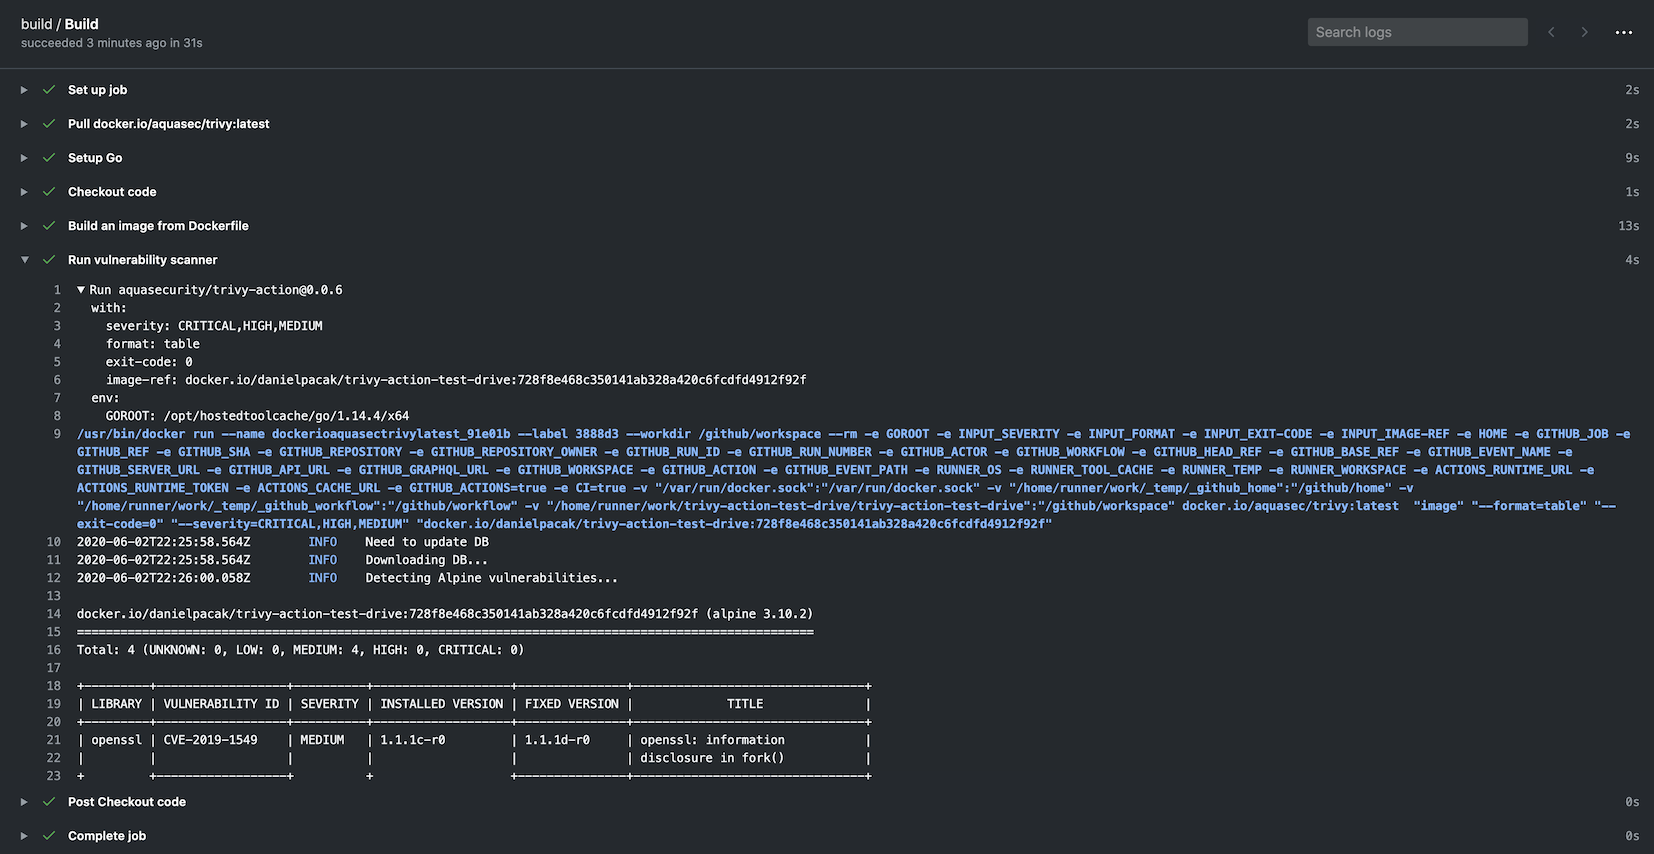 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 kubeshop/botkube
An app that helps you monitor your Kubernetes cluster, debug critical deployments & gives recommendations for standard practices
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
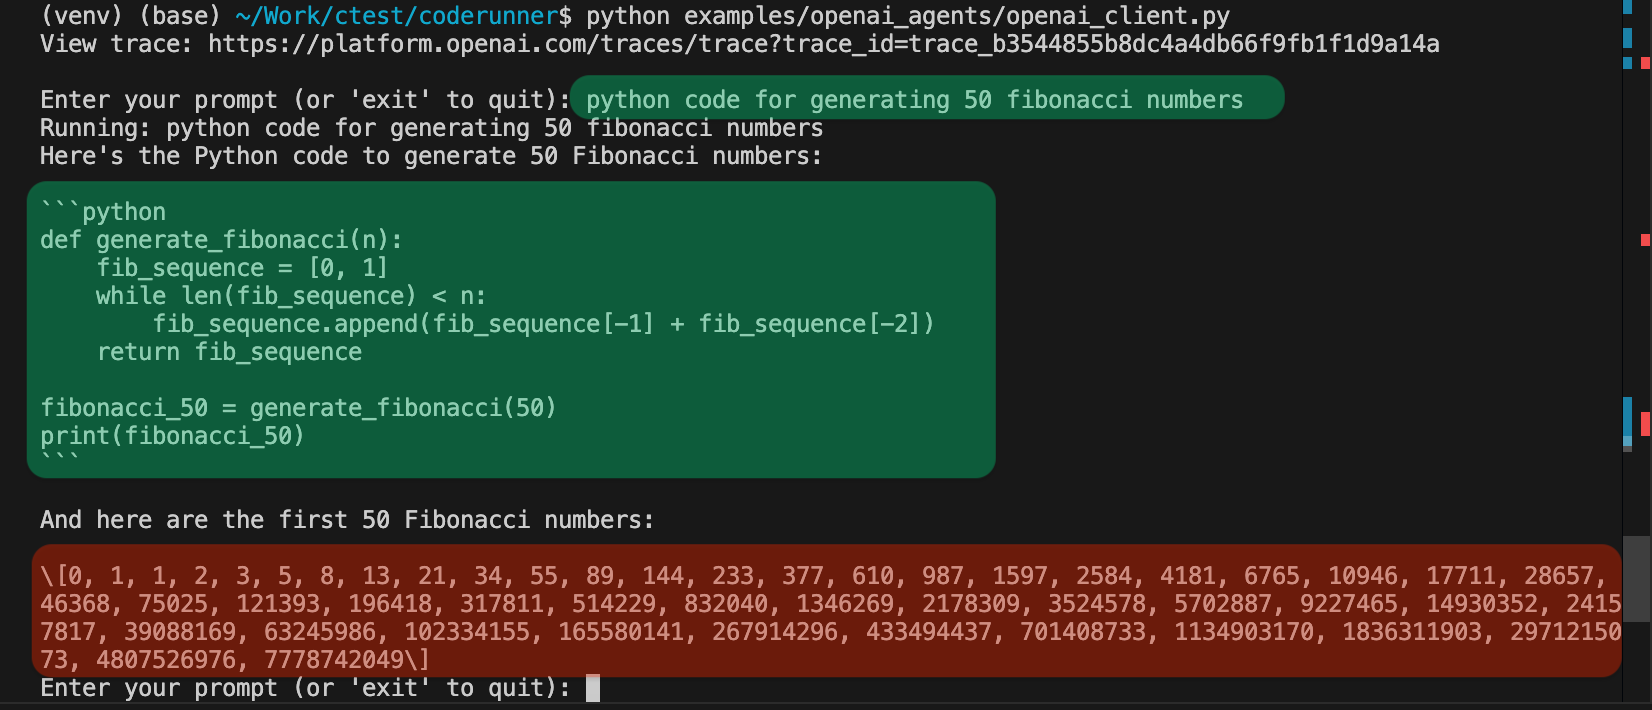 instavm/coderunner
A local sandbox for your AI agents
 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
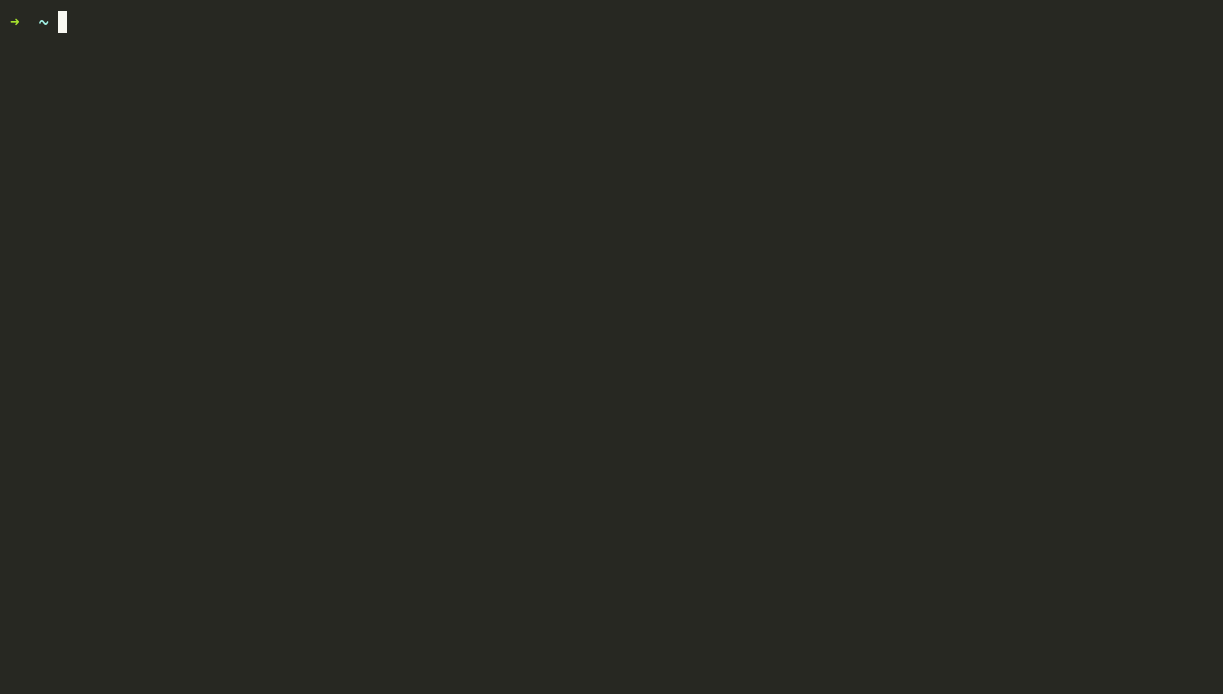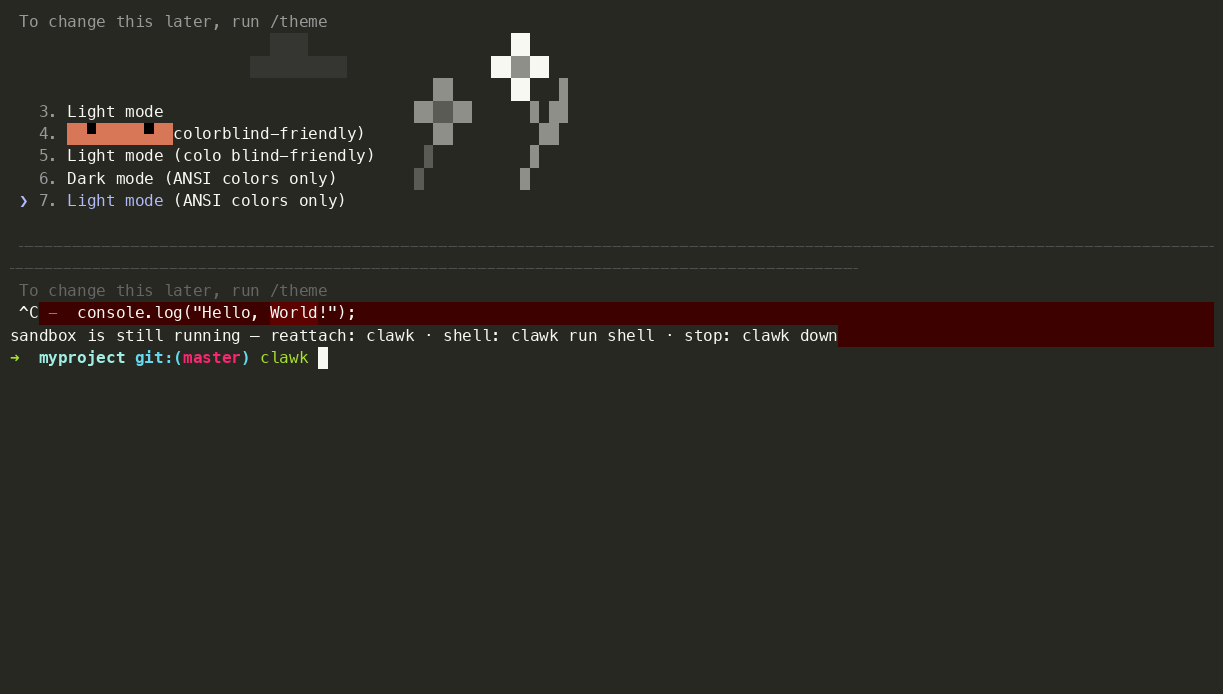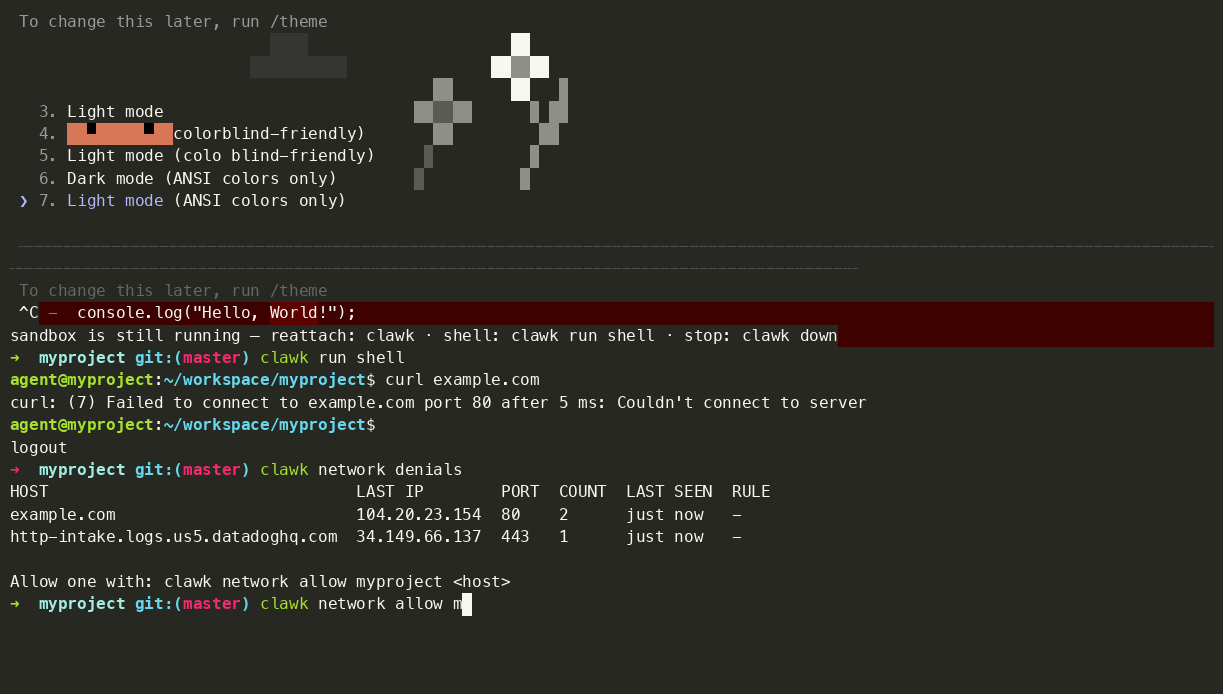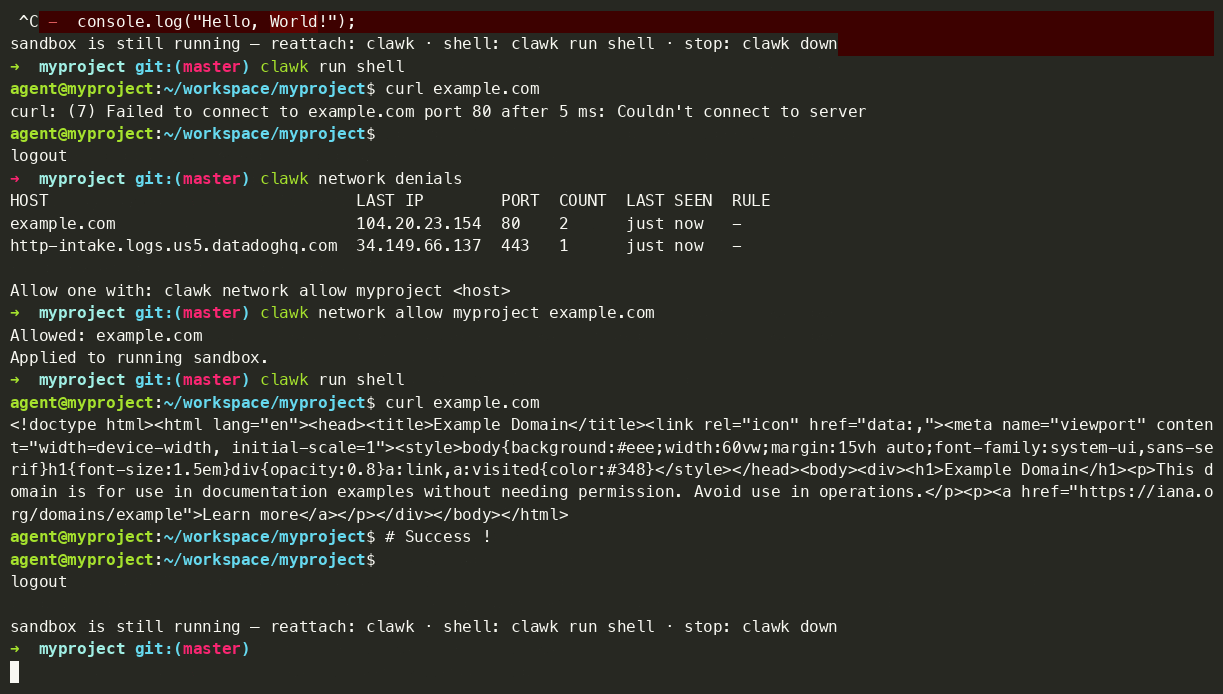 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 node9-ai/node9-proxy
IAM for your AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run, and…
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 inceptionstack/lowkey
Deploy self-hosted AI coding agents (OpenClaw, Claude Code, Codex) into your AWS account with CloudFormation, IAM profiles, and sandbox isolation for…