
kubesploit
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
command-and-controlcontainer-escapecontainer-security+8
cyberark/kubesploitKubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
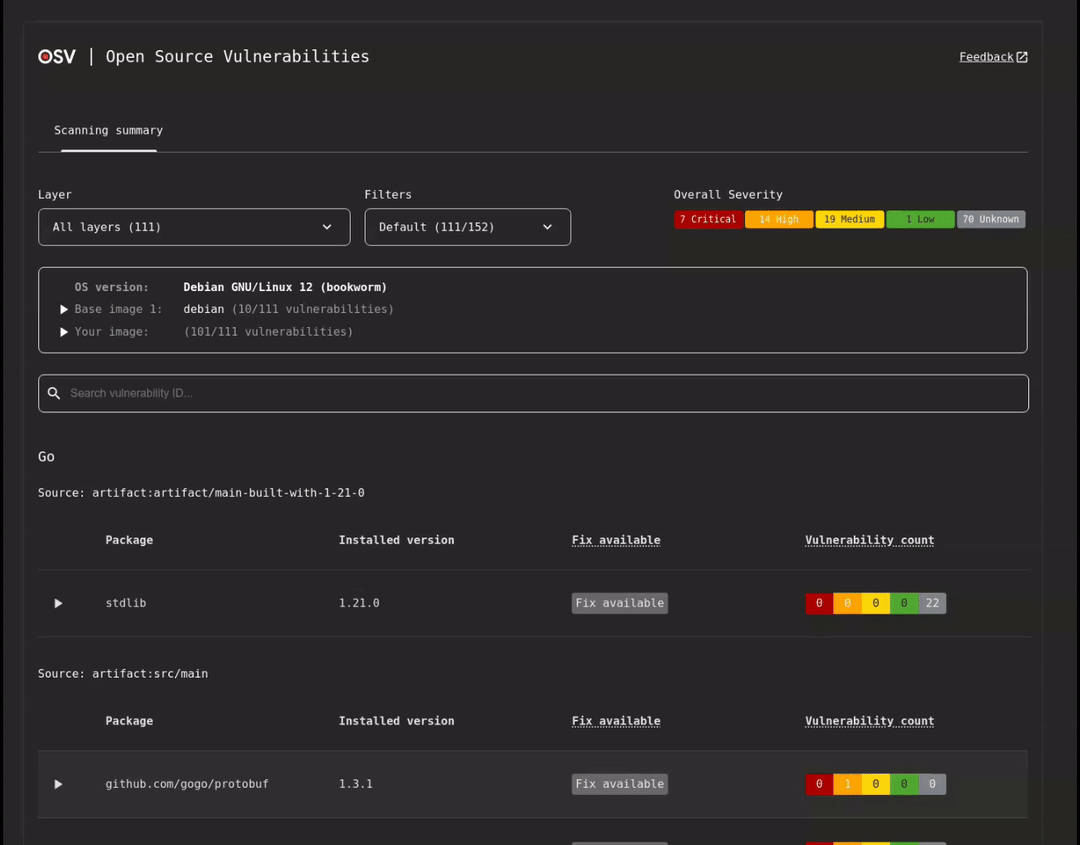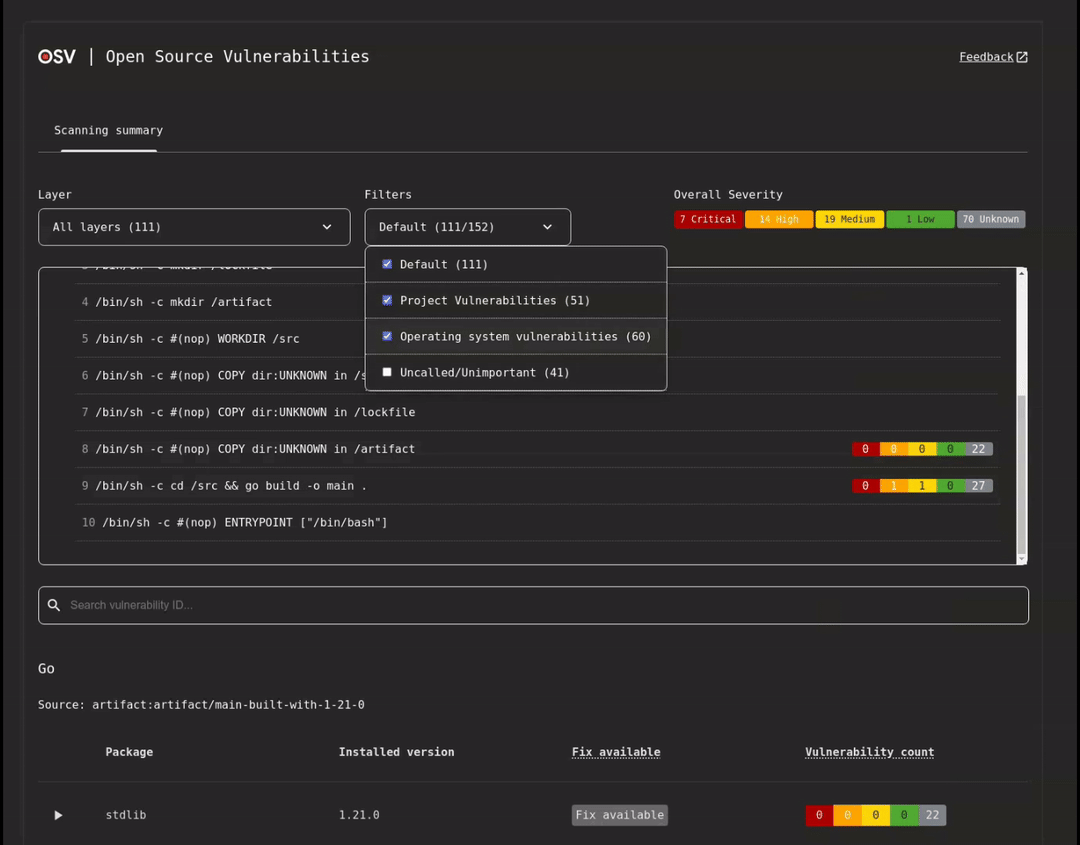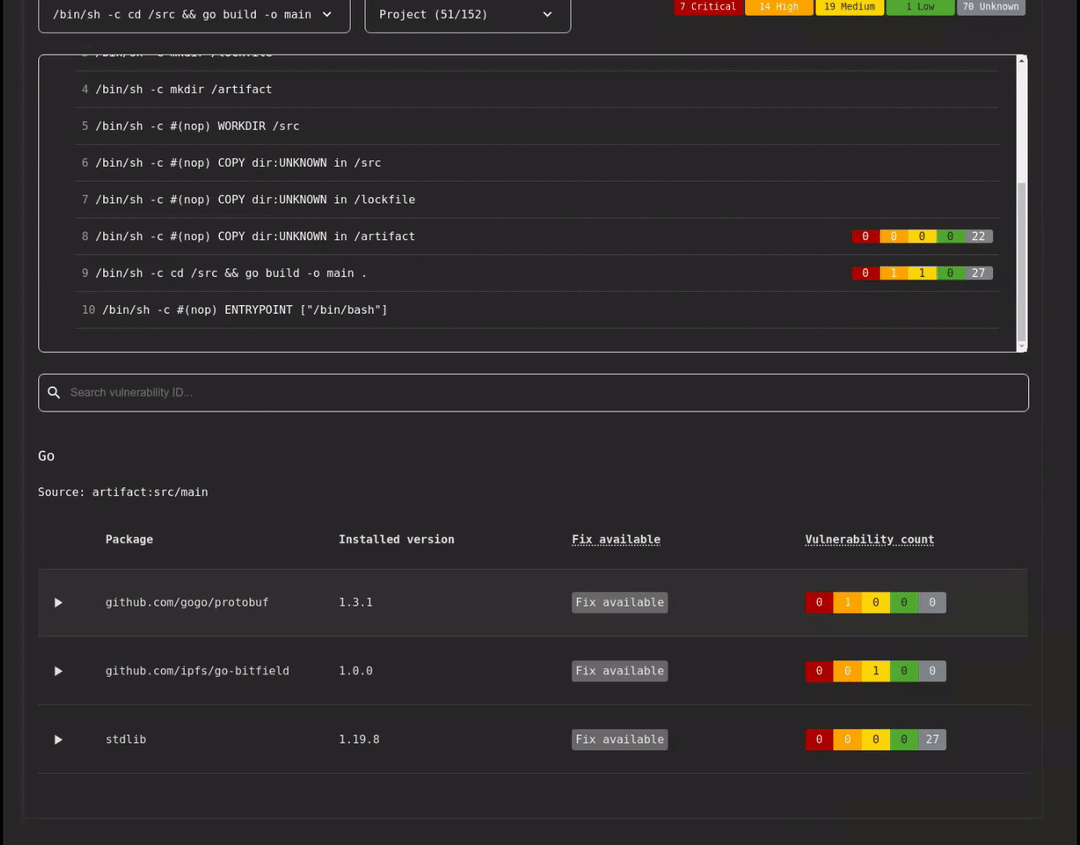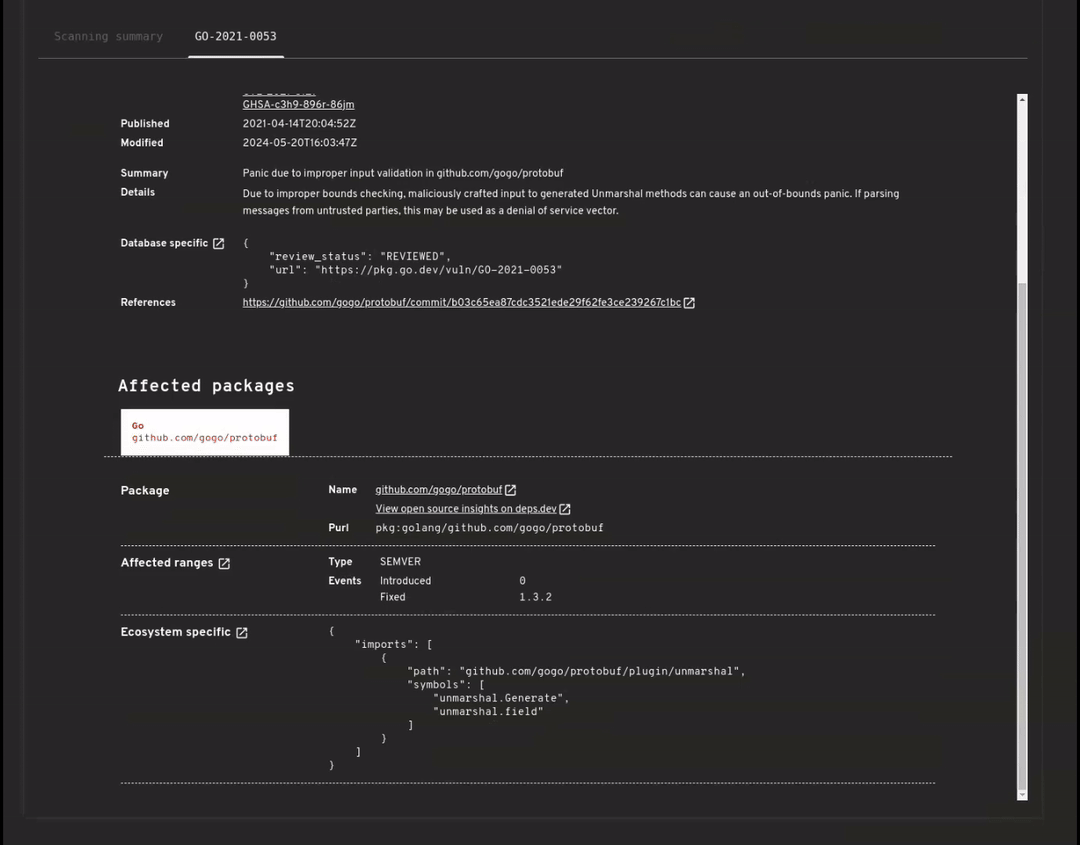 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 adarkst/honeypot_smart_infrastructure
This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 grantbirki/redash-vulnerable
A Dockerized Redash instance that is vulnerable to CVE-2021-21239