
vaas-cve-2014-0160
 hmlio/vaas-cve-2014-0160
Vulnerability as a service: showcasing CVS-2014-0160, a.k.a. Heartbleed
container-securityeducationexploitation+3
15
hmlio/vaas-cve-2014-0160Vulnerability as a service: showcasing CVS-2014-0160, a.k.a. Heartbleed
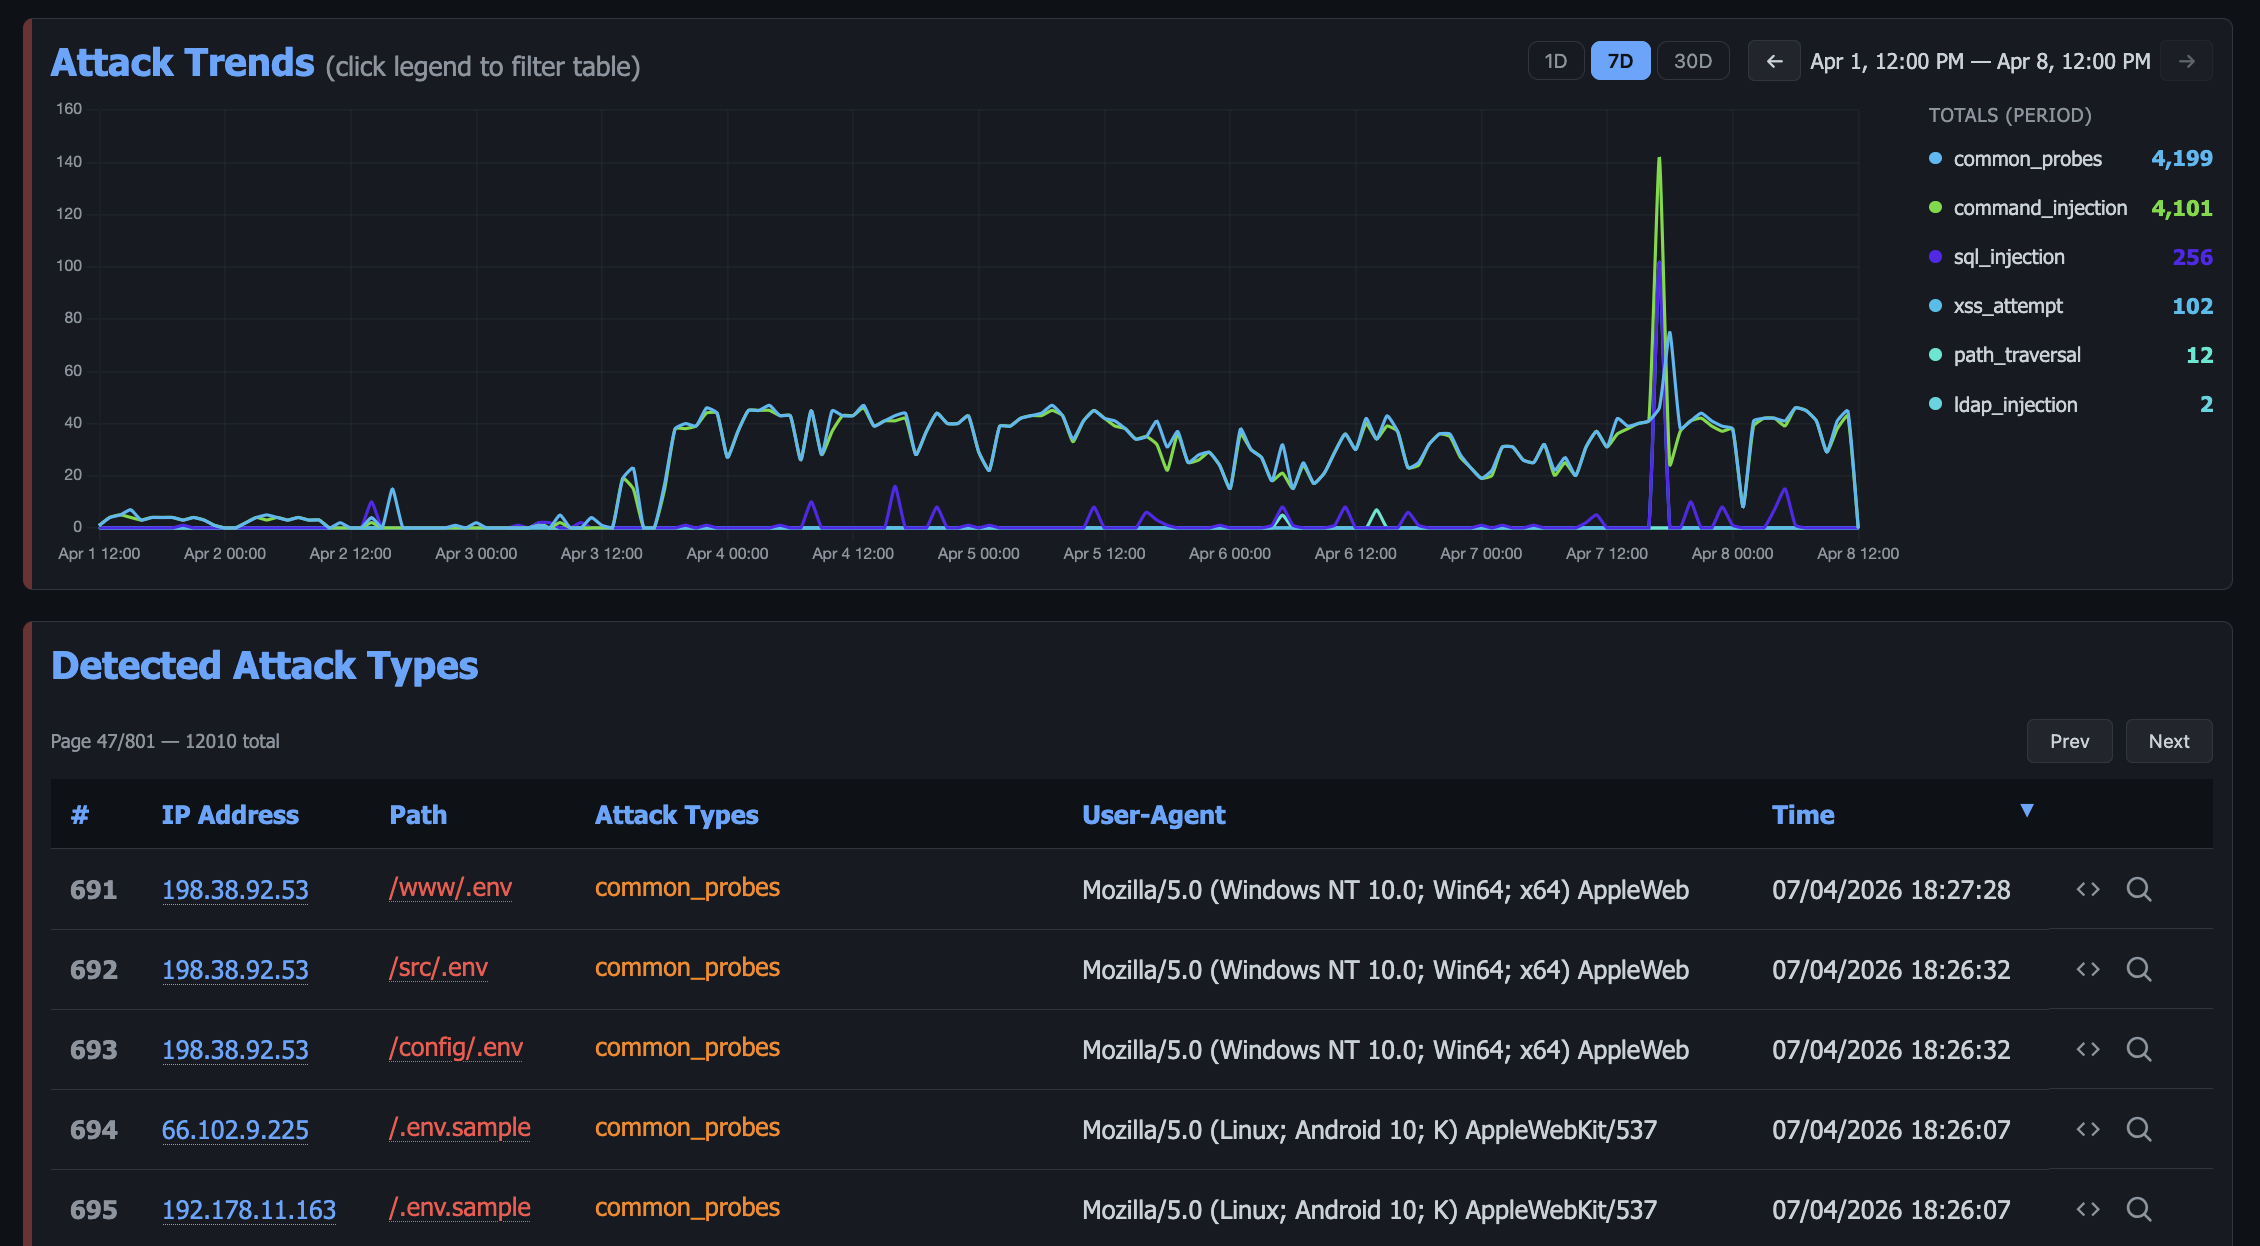 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 evict/poc_cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105 targeting Kubernetes API server. Supports authenticated and unauthenticated privilege escalation to…
 hackerhouse-opensource/cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 vaibhav91one/drupalgeddon2-cve-lab
Intentionally vulnerable Drupal 7.57 lab for reproducing CVE-2018-7600 (Drupalgeddon2) in a Docker container, with an installer script and PHP…
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
 berraesen/apache-cve-2021-42013-lab
Docker ortamında Apache HTTP Server 2.4.49 (CVE-2021-42013) zafiyetinin gösterildiği laboratuvar çalışması.
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
 jas9reet/cve-2021-42013-lab
Docker-based lab environment for exploiting Apache HTTP Server 2.4.50 path traversal and RCE vulnerability (CVE-2021-42013) with automated exploit…
 abcfabian/react2shell-cve-2025-55182-testing-environment
A containerized testing environment for CVE-2025-55182, a critical (10.0 CVSS) Remote Code Execution vulnerability in React Server Components.
 there-was-a-bird/triton-cve-2025-23320
Docker-based proof-of-concept demonstrating CVE-2025-23320 in NVIDIA Triton inference server, exploiting shared memory key leakage to trigger an…
 shoucheng3/payara__payara_cve-2022-37422_5-2022-2
Jakarta EE and MicroProfile application server runtime for development and containerized deployments, supporting cloud-native middleware with…
 meganekos/secure-by-default-rce-demo
Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…