

harpoon
 professionallyevil/harpoon
A collection of scripts, and tips and tricks for hacking k8s clusters and containers.
cloud-securitycontainer-securityexploitation+5
145
professionallyevil/harpoonA collection of scripts, and tips and tricks for hacking k8s clusters and containers.
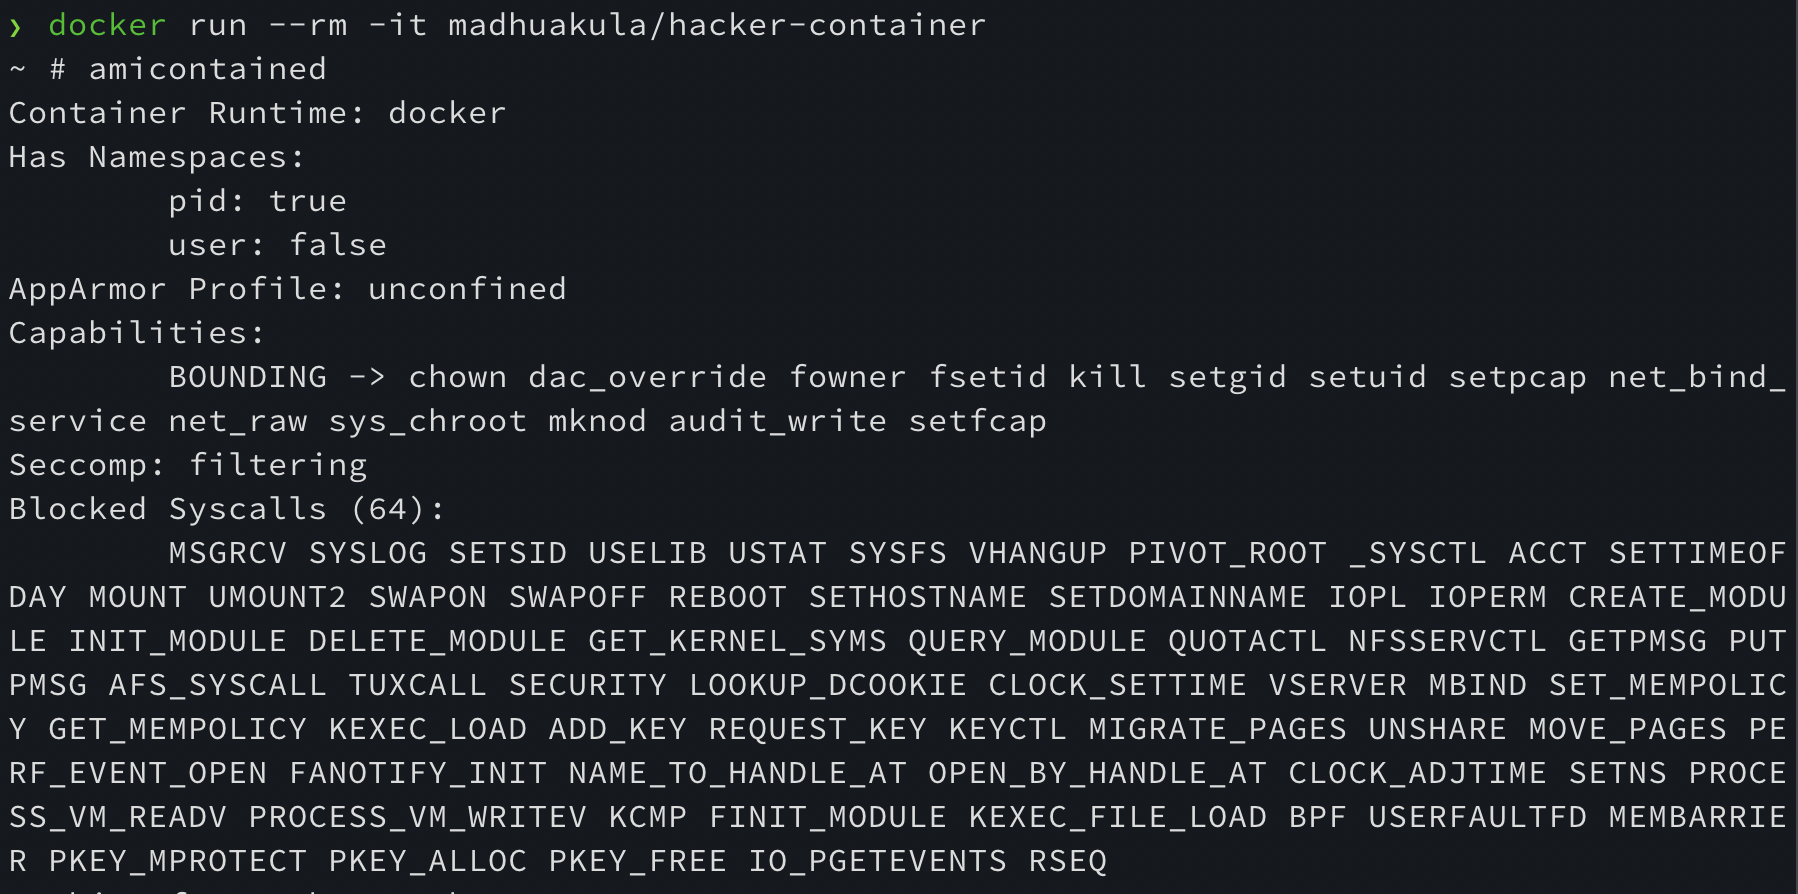 madhuakula/hacker-container
The Swiss Army Container for Cloud Native Security. Container with all the list of useful tools/commands while hacking and securing Containers,…
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…
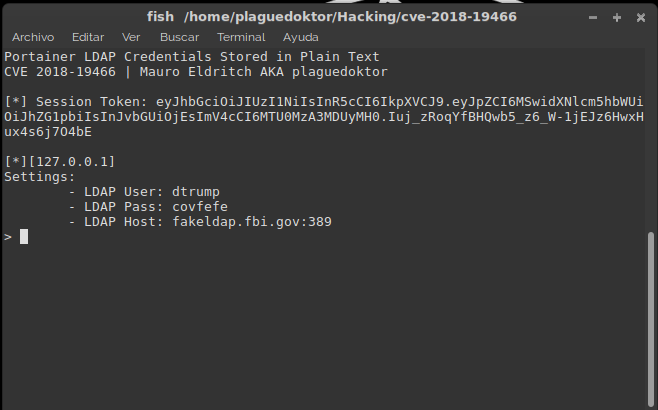 mauroeldritch/lempo
LEMPO (Ldap Exposure on POrtainer) is an exploit for CVE-2018-19466 (LDAP Credentials Disclosure on Portainer). Featured @ DevFest Siberia 2018
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 galois17/cve-2017-12149-playground
Containerized JBoss AS 6.1.0 research lab for demonstrating Java Deserialization (CVE-2017-12149) and JBoss Seam EL Injection vulnerabilities with…
 cybersecsi/dockerized-android
A container-based framework to enable the integration of mobile components in security training platforms
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 khast3x/redcloud
Automated Red Team Infrastructure deployement using Docker
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.