Dirty-Frag-Research-CVE-2026-43284-

Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…

Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…

eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…

Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…

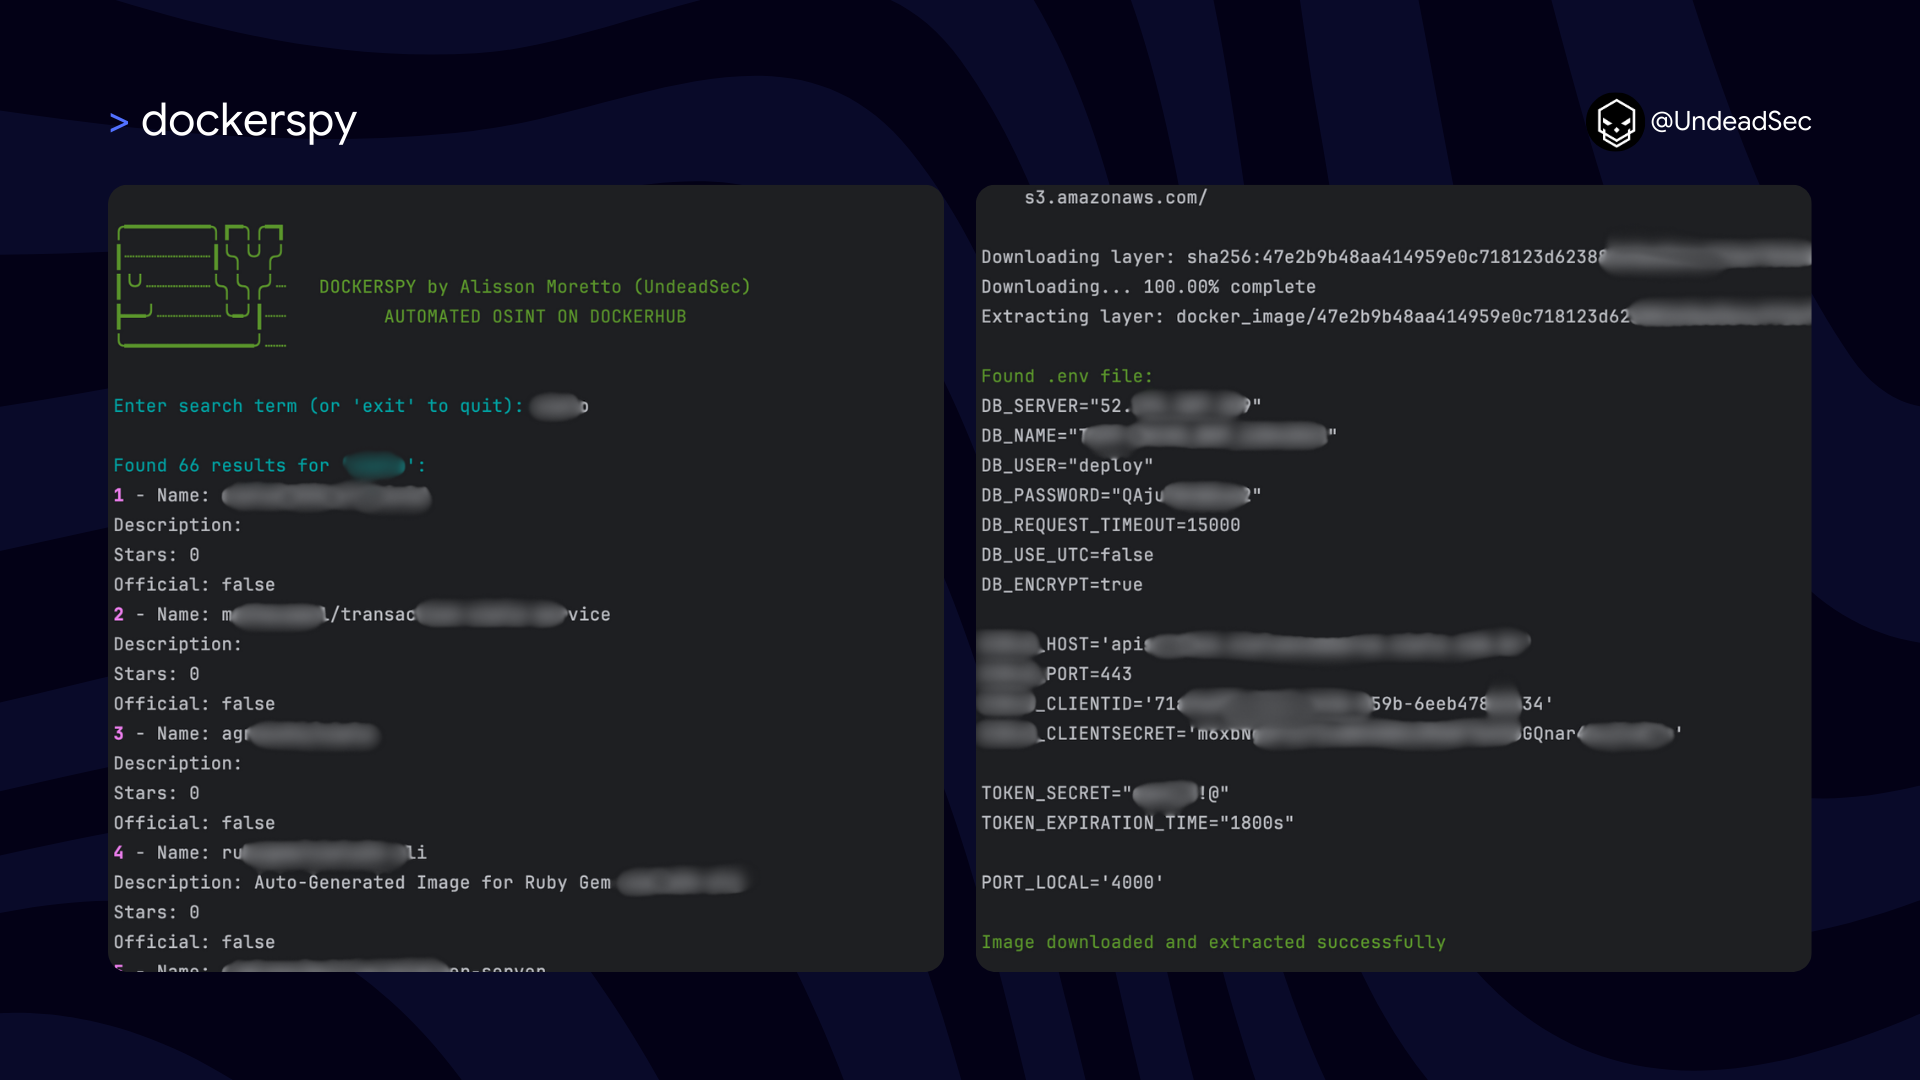
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…

Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)

Real-time, container-based file scanning at enterprise scale

eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.