
botb
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
cloud-securitycontainer-escapecontainer-security+4
brompwnie/botbA container analysis and exploitation tool for pentesters and engineers.
 rolix44/kubestroyer
Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…
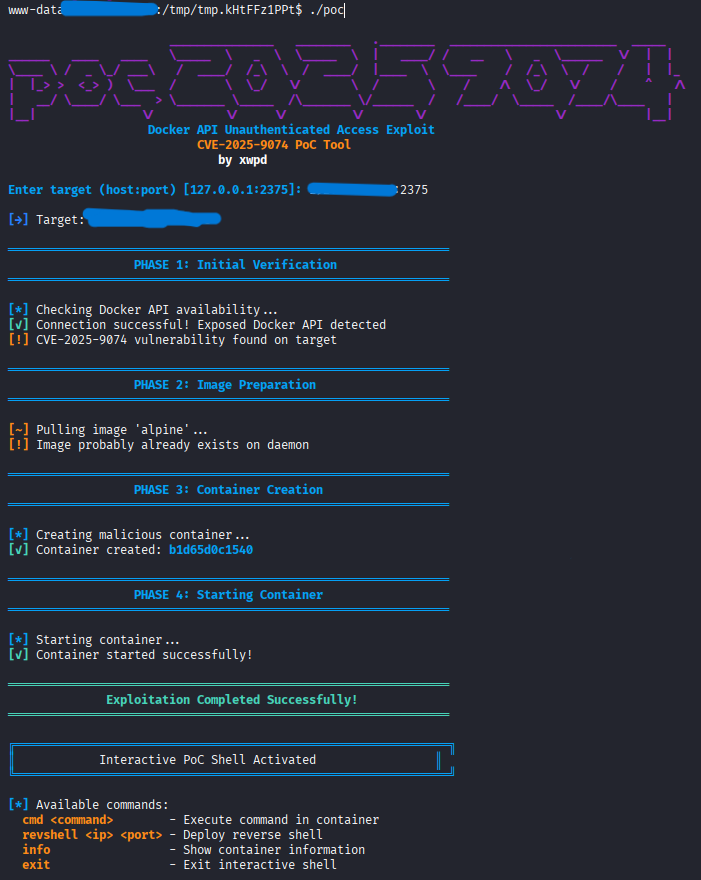 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 cved-sources/cve-2016-8869
Dockerized vulnerable environment for CVE-2016-8869 (Joomla privilege escalation) used for security training and exploitation practice.
 cved-sources/cve-2019-9978
Docker container providing a vulnerable environment for CVE-2019-9978 (WordPress Social Networks Auto Poster RCE) for security training and…
 cved-sources/cve-2019-9184
Docker container with a pre-configured vulnerable environment for CVE-2019-9184, designed for security testing and educational exploitation practice.
 cved-sources/cve-2018-16283
Docker container for CVE-2018-16283, part of a managed vulnerable Docker environment for practicing exploitation and vulnerability analysis.
 cved-sources/cve-2018-11776
Docker container providing a vulnerable Apache Struts2 environment for CVE-2018-11776 exploitation practice and security education.
 cved-sources/cve-2019-10678
Docker container providing a vulnerable environment for CVE-2019-10678, designed for security training and exploitation practice within the Cved…
 cved-sources/cve-2018-15473
Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
 cved-sources/cve-2015-8103
Docker container for CVE-2015-8103 exploitation targeting JBoss, part of a vulnerable container management framework for security testing.
 cved-sources/cve-2017-4971
Docker-based vulnerable environment for CVE-2017-4971 (Spring WebFlow RCE) to practice exploitation and security testing in a controlled lab setup.
 cved-sources/cve-2016-6515
Docker container providing a vulnerable environment for CVE-2016-6515 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2015-1427
Docker container with a pre-configured vulnerable Elasticsearch instance for practicing CVE-2015-1427 exploitation in a safe lab environment.
 cved-sources/cve-2017-12615
Docker container providing a vulnerable Apache Tomcat environment for CVE-2017-12615 exploitation, enabling hands-on practice of PUT method file…
 cved-sources/cve-2019-9194
Docker container with CVE-2019-9194 for practicing vulnerability exploitation in a controlled environment. Part of the Cved vulnerable container…