
terrier
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
container-securityhash-analysissupply-chain-security+1
228
heroku/terrierTerrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 rtvkiz/minimal
Minimal CVE Hardened container image collection
 anchore/grype
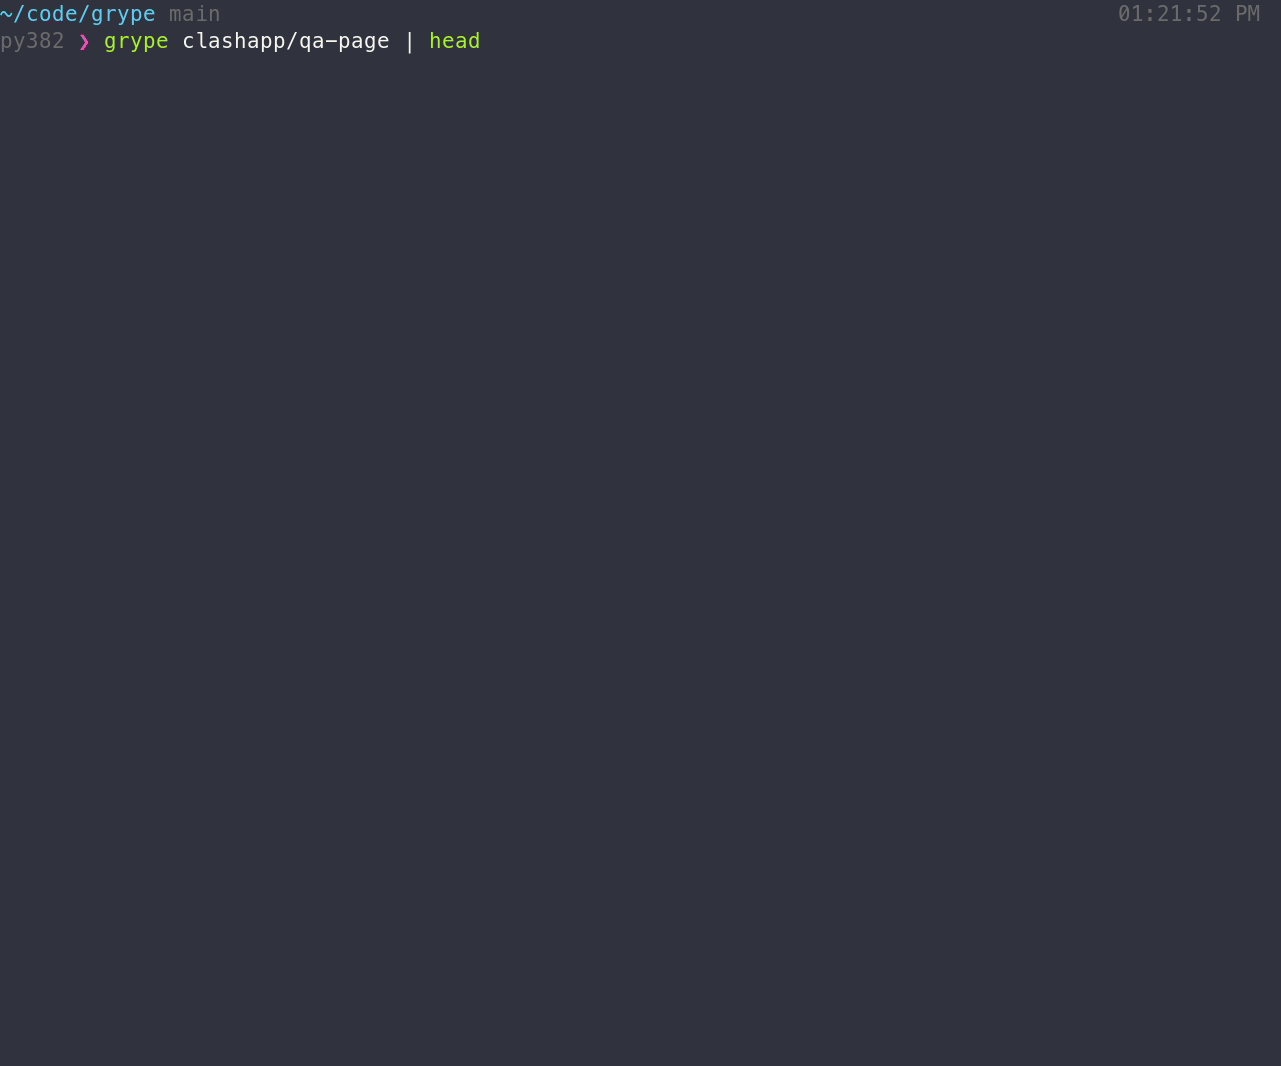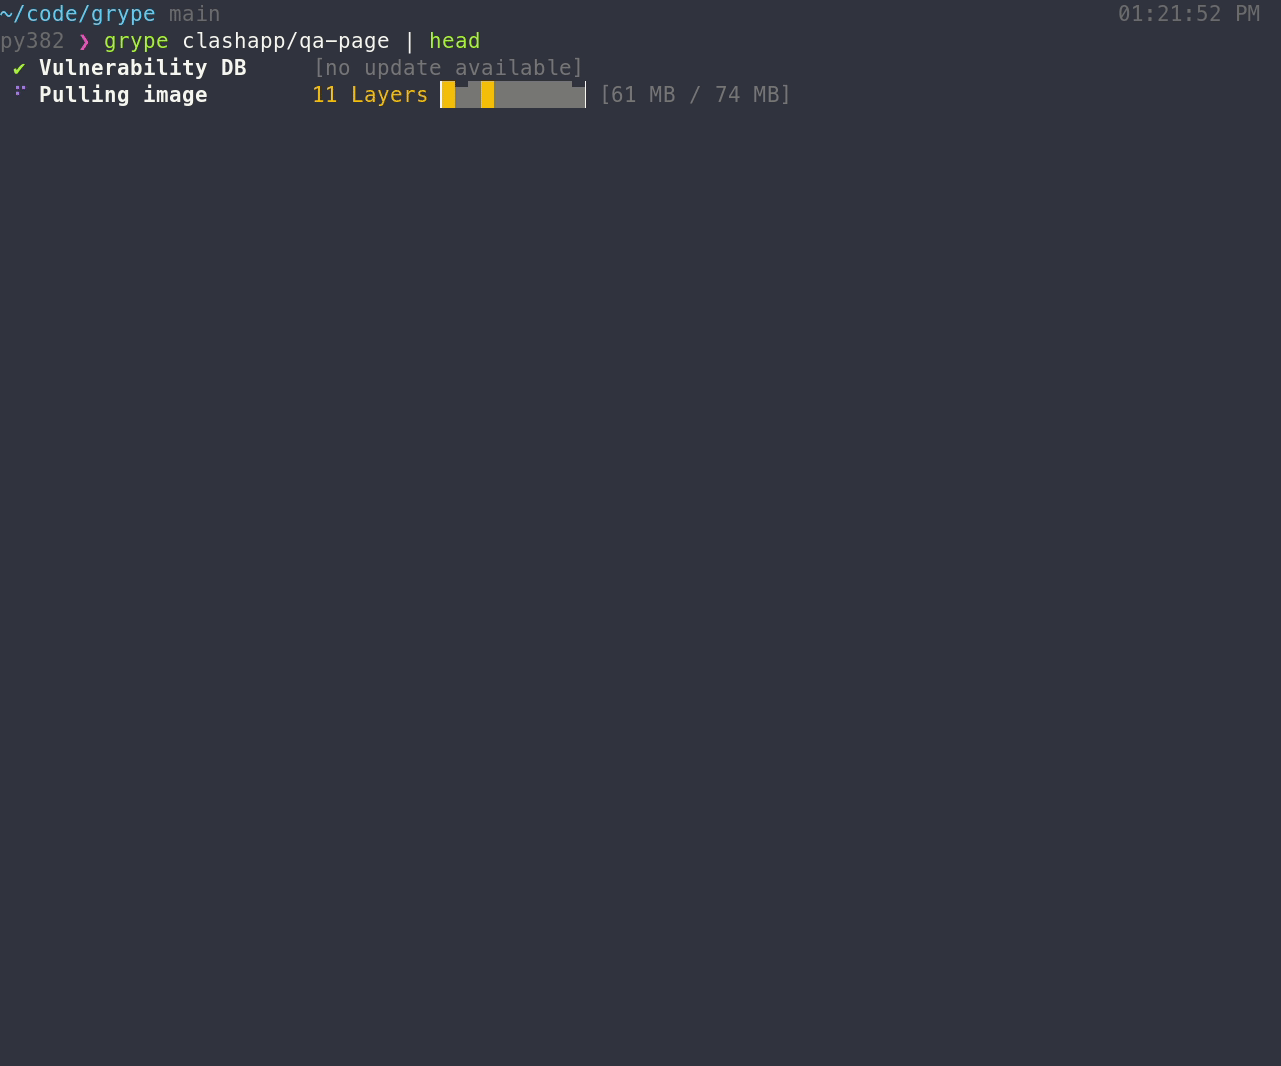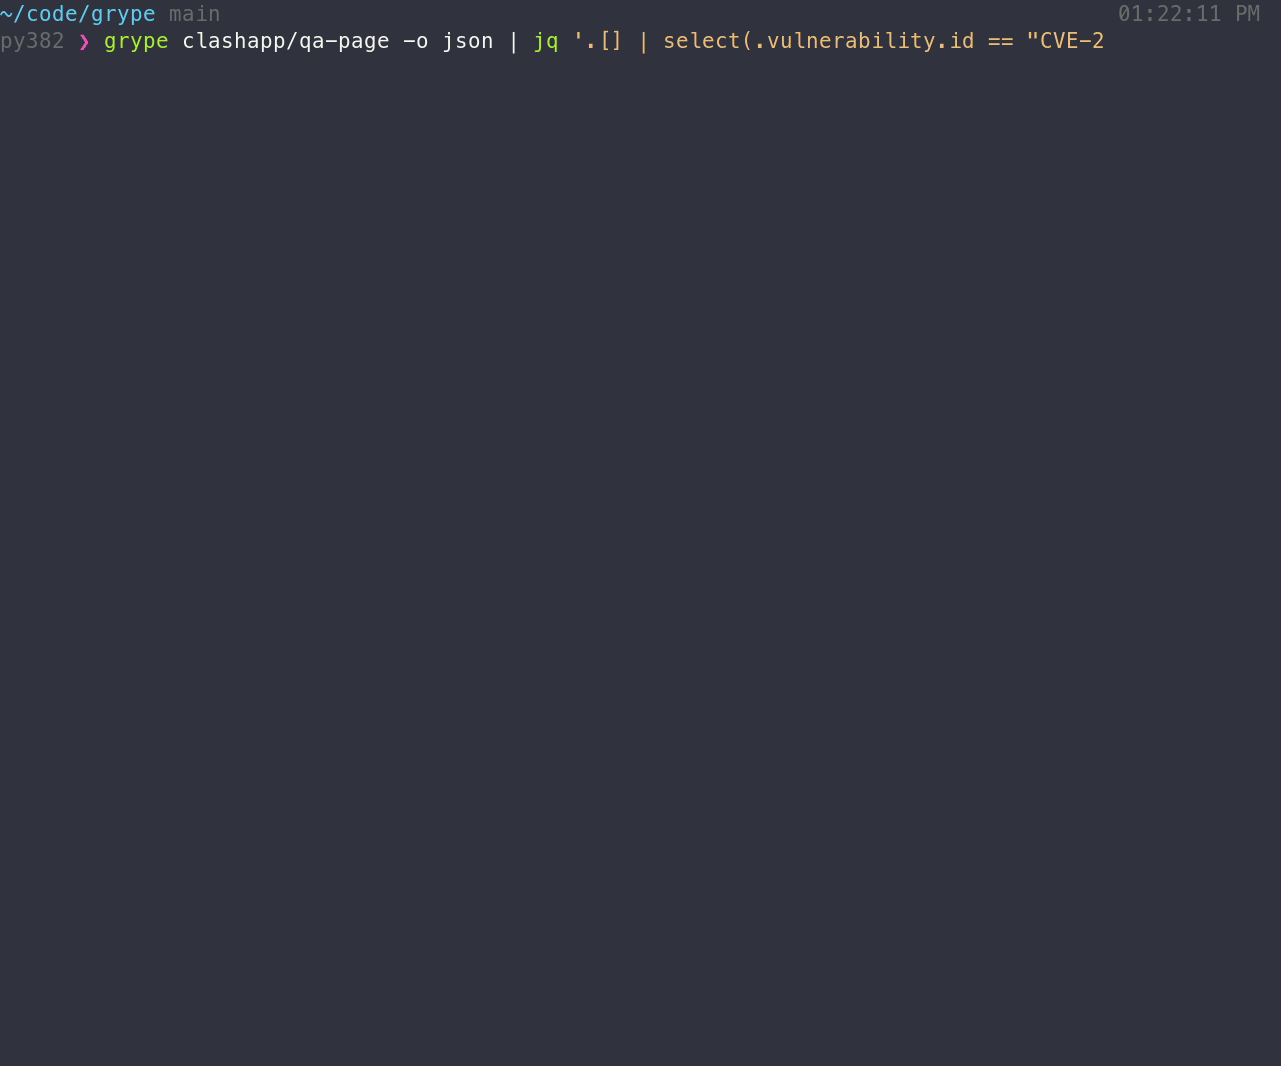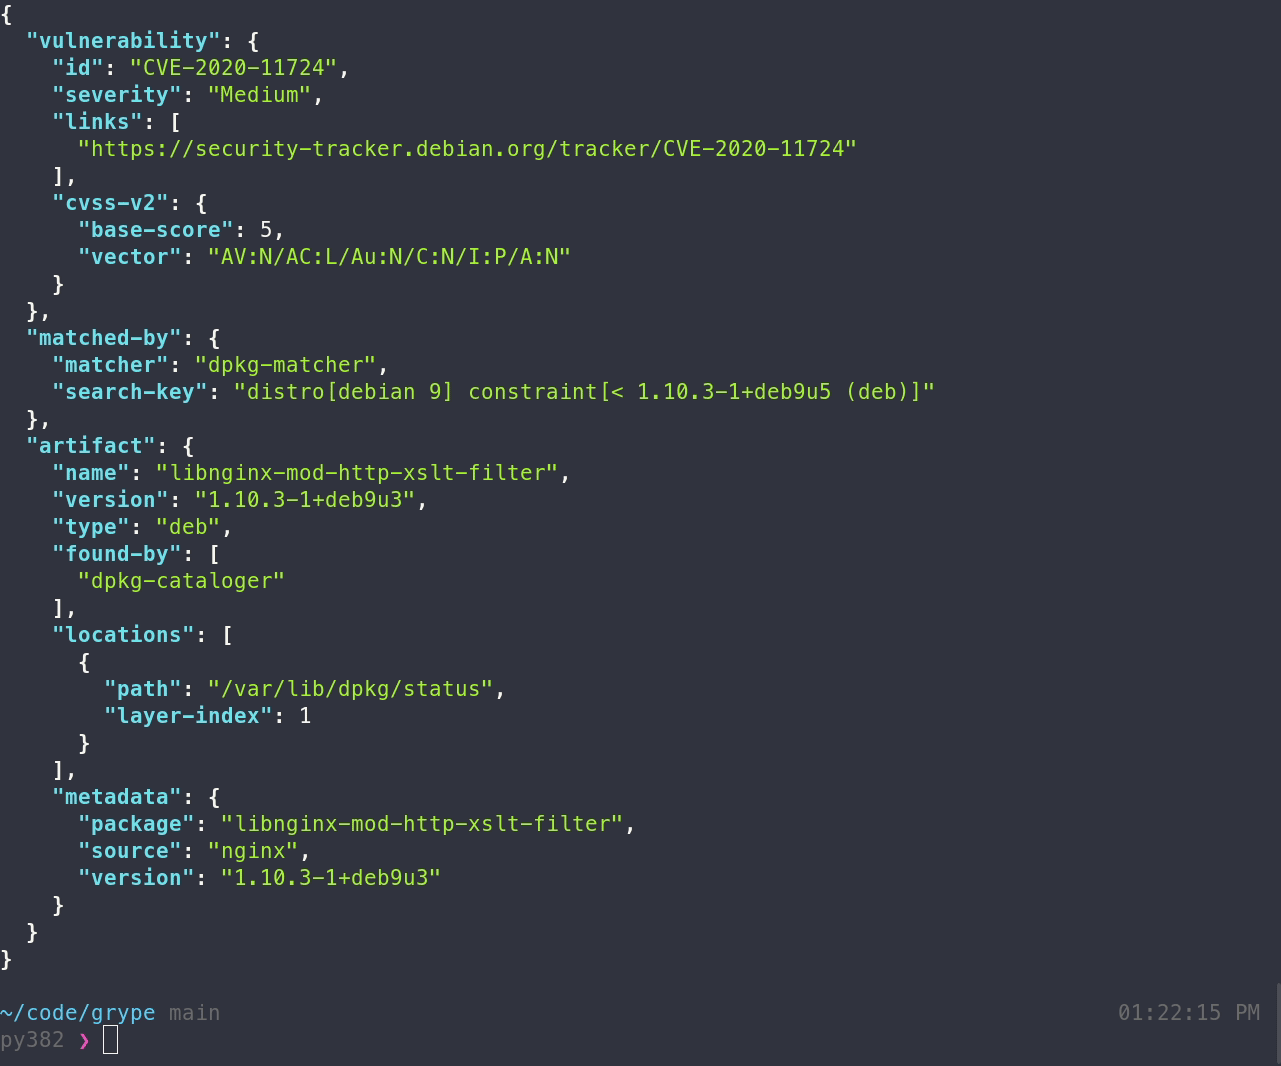
A vulnerability scanner for container images and filesystems
 kubescape/kubescape
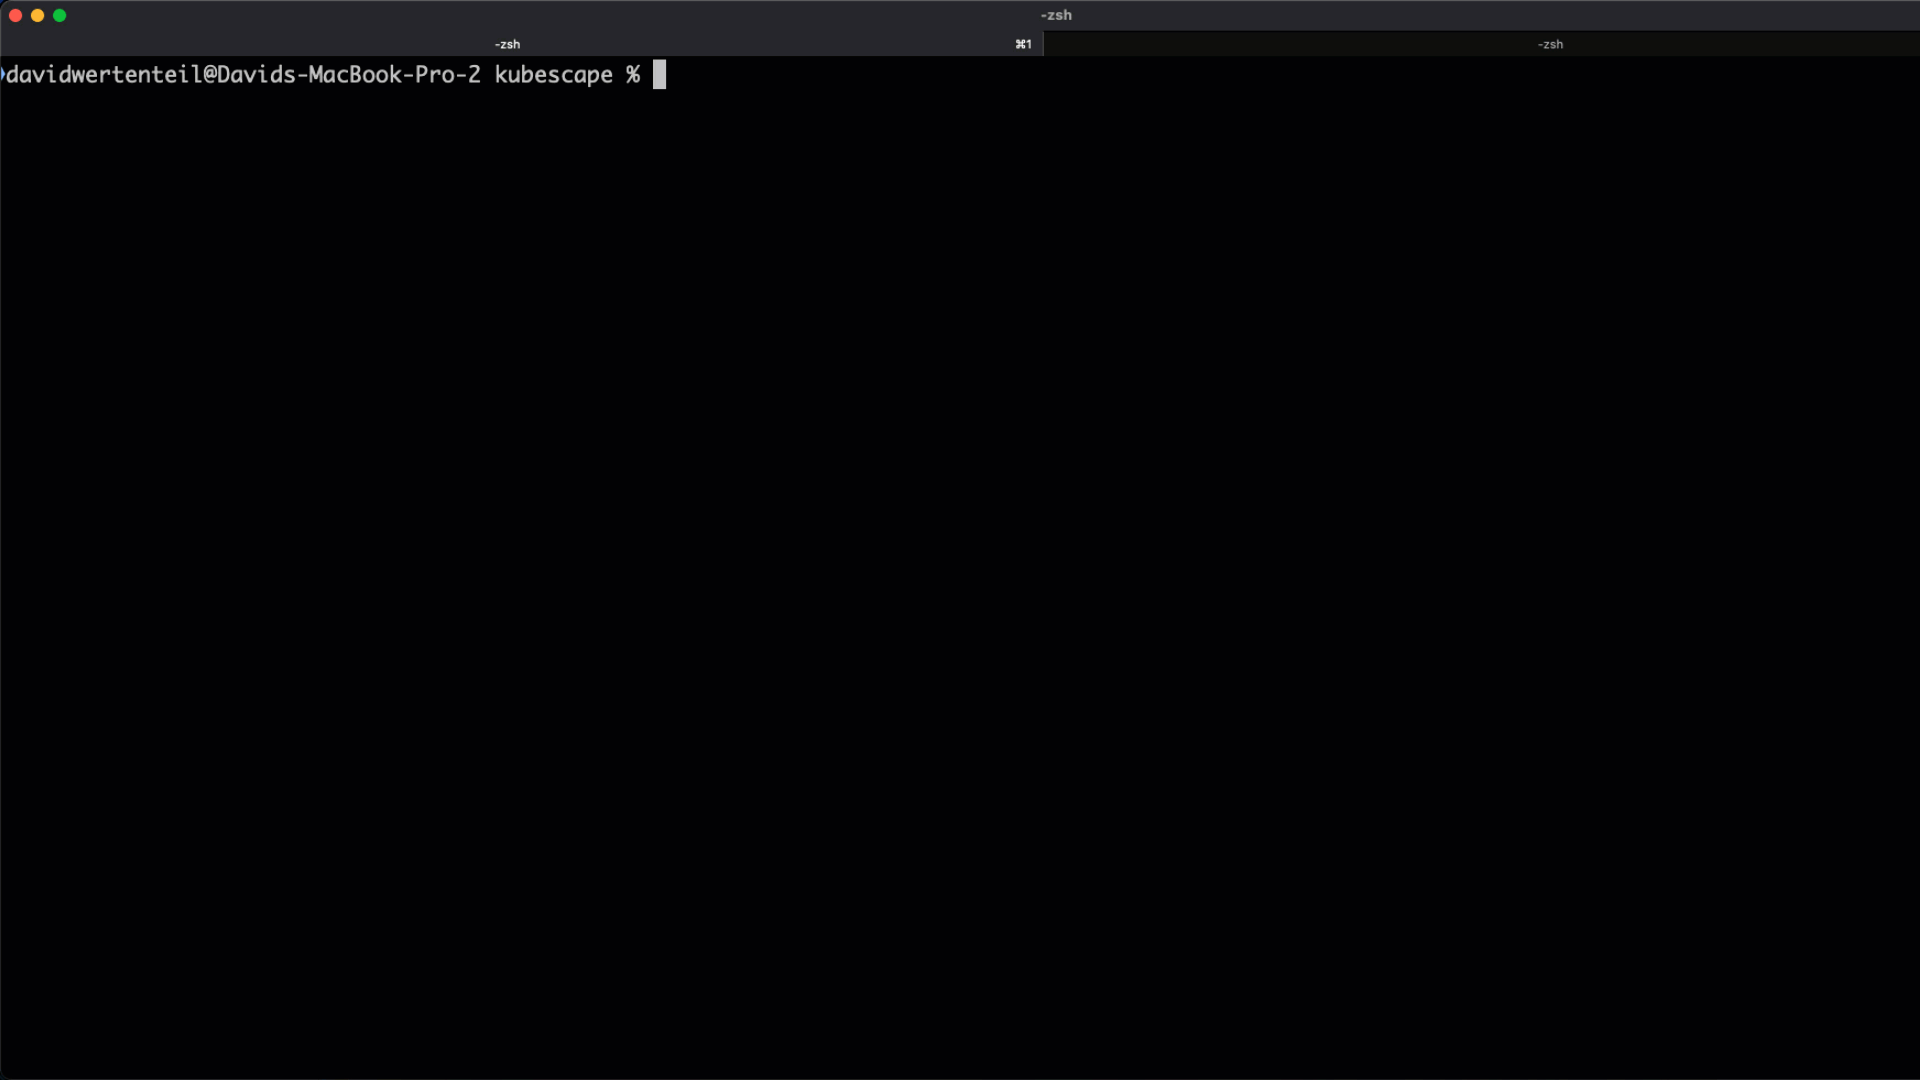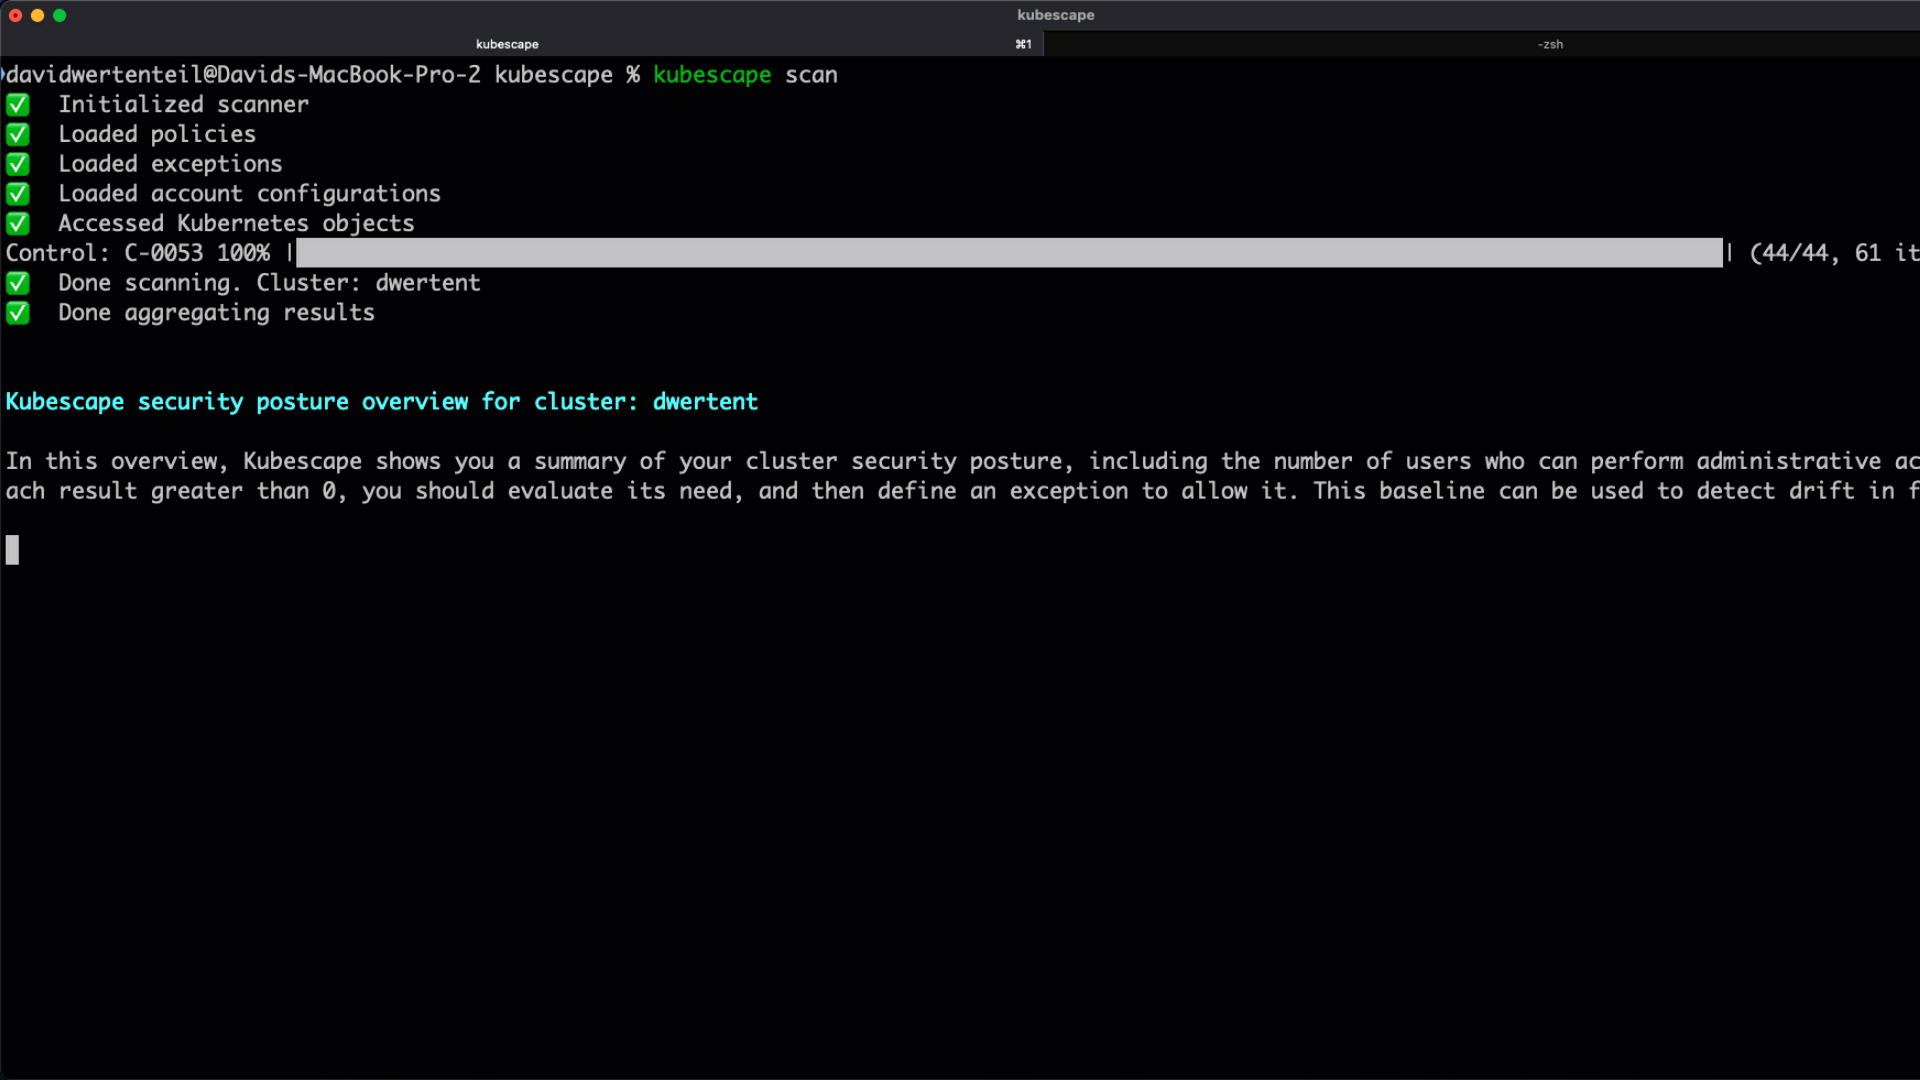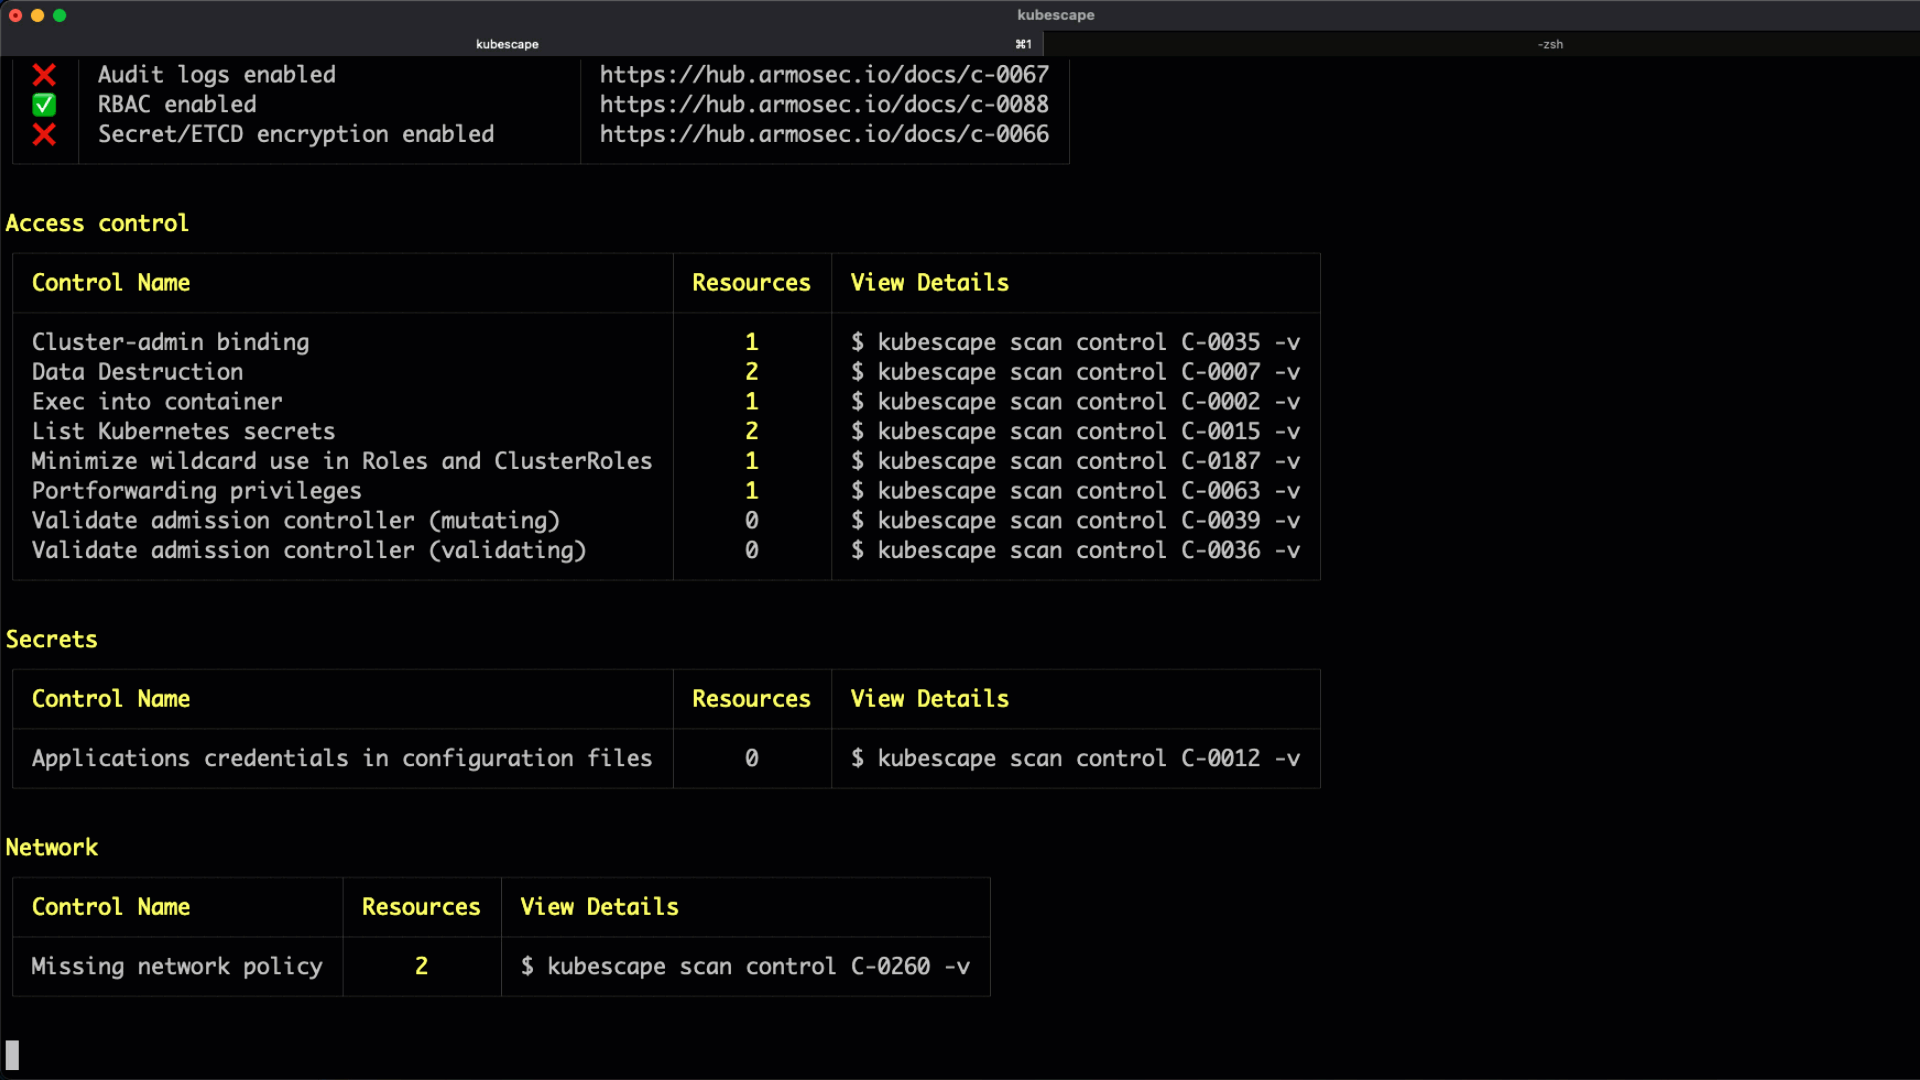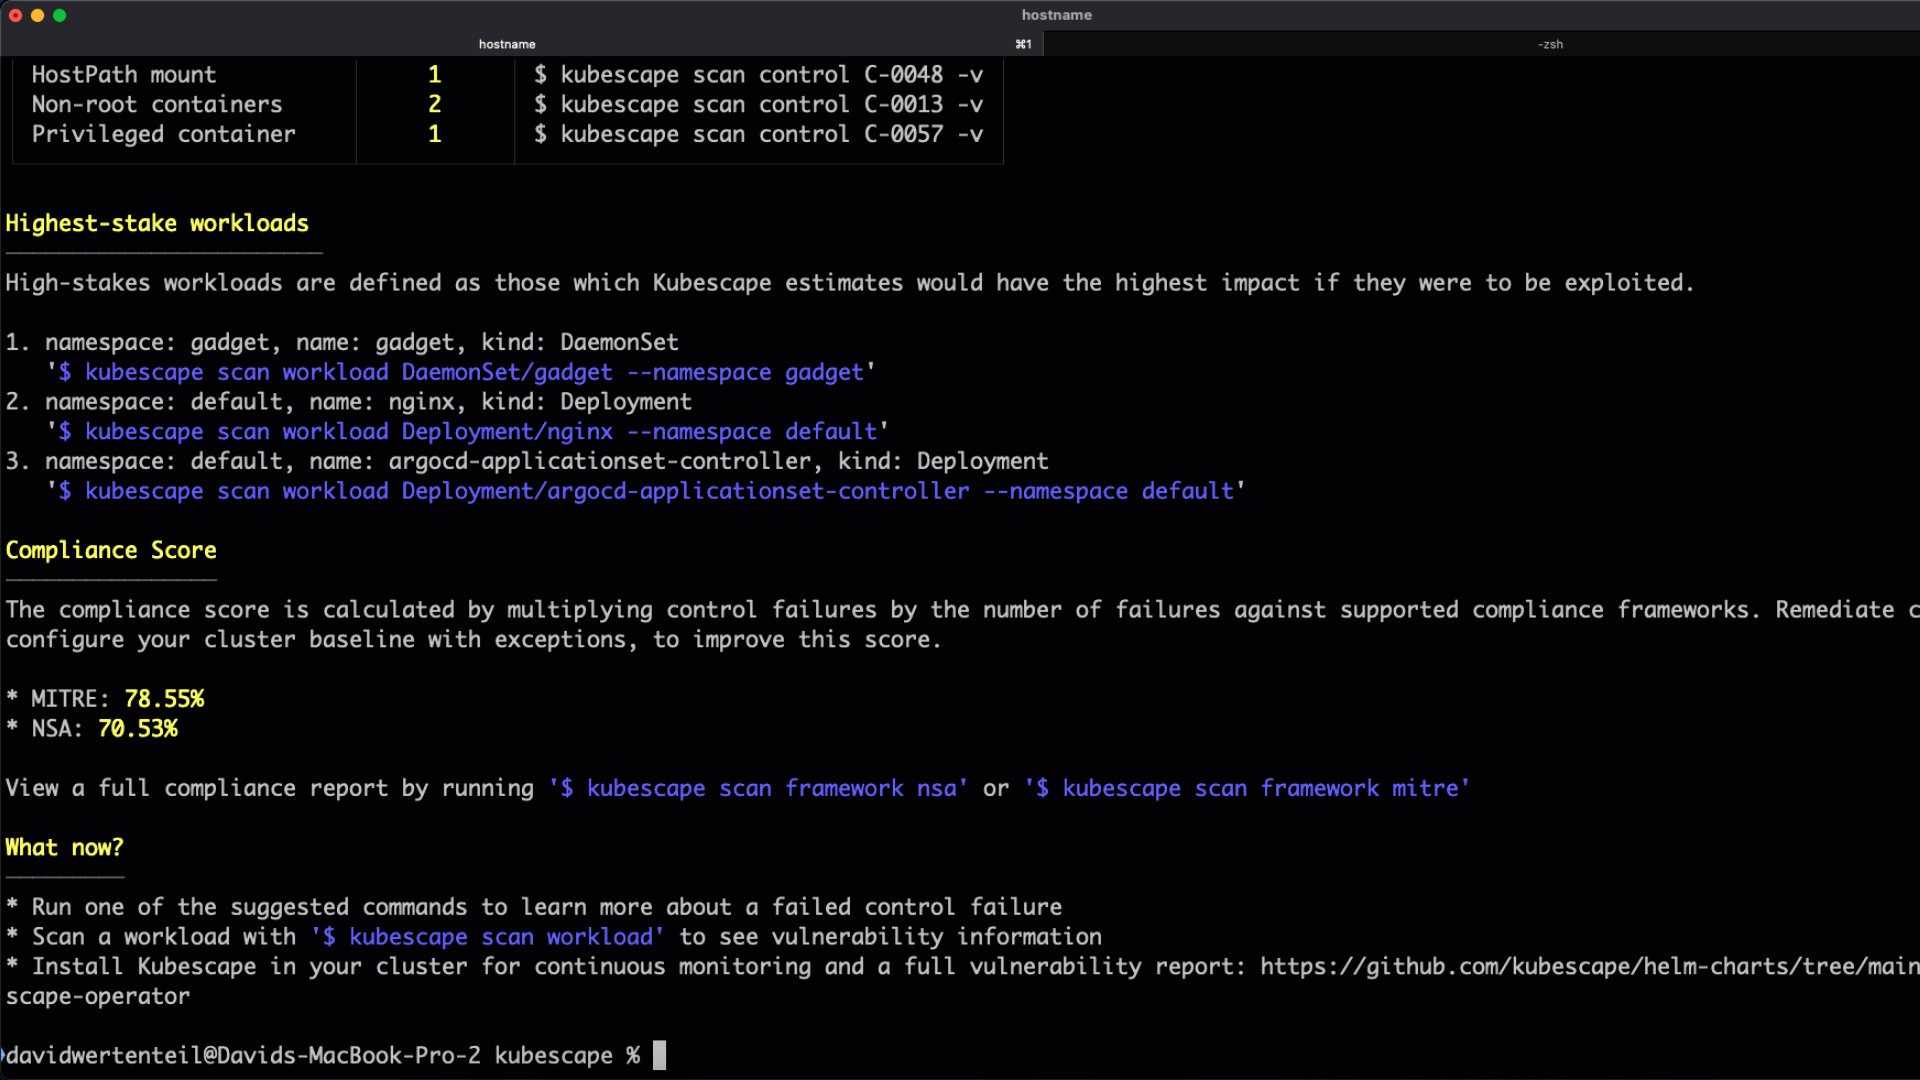
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
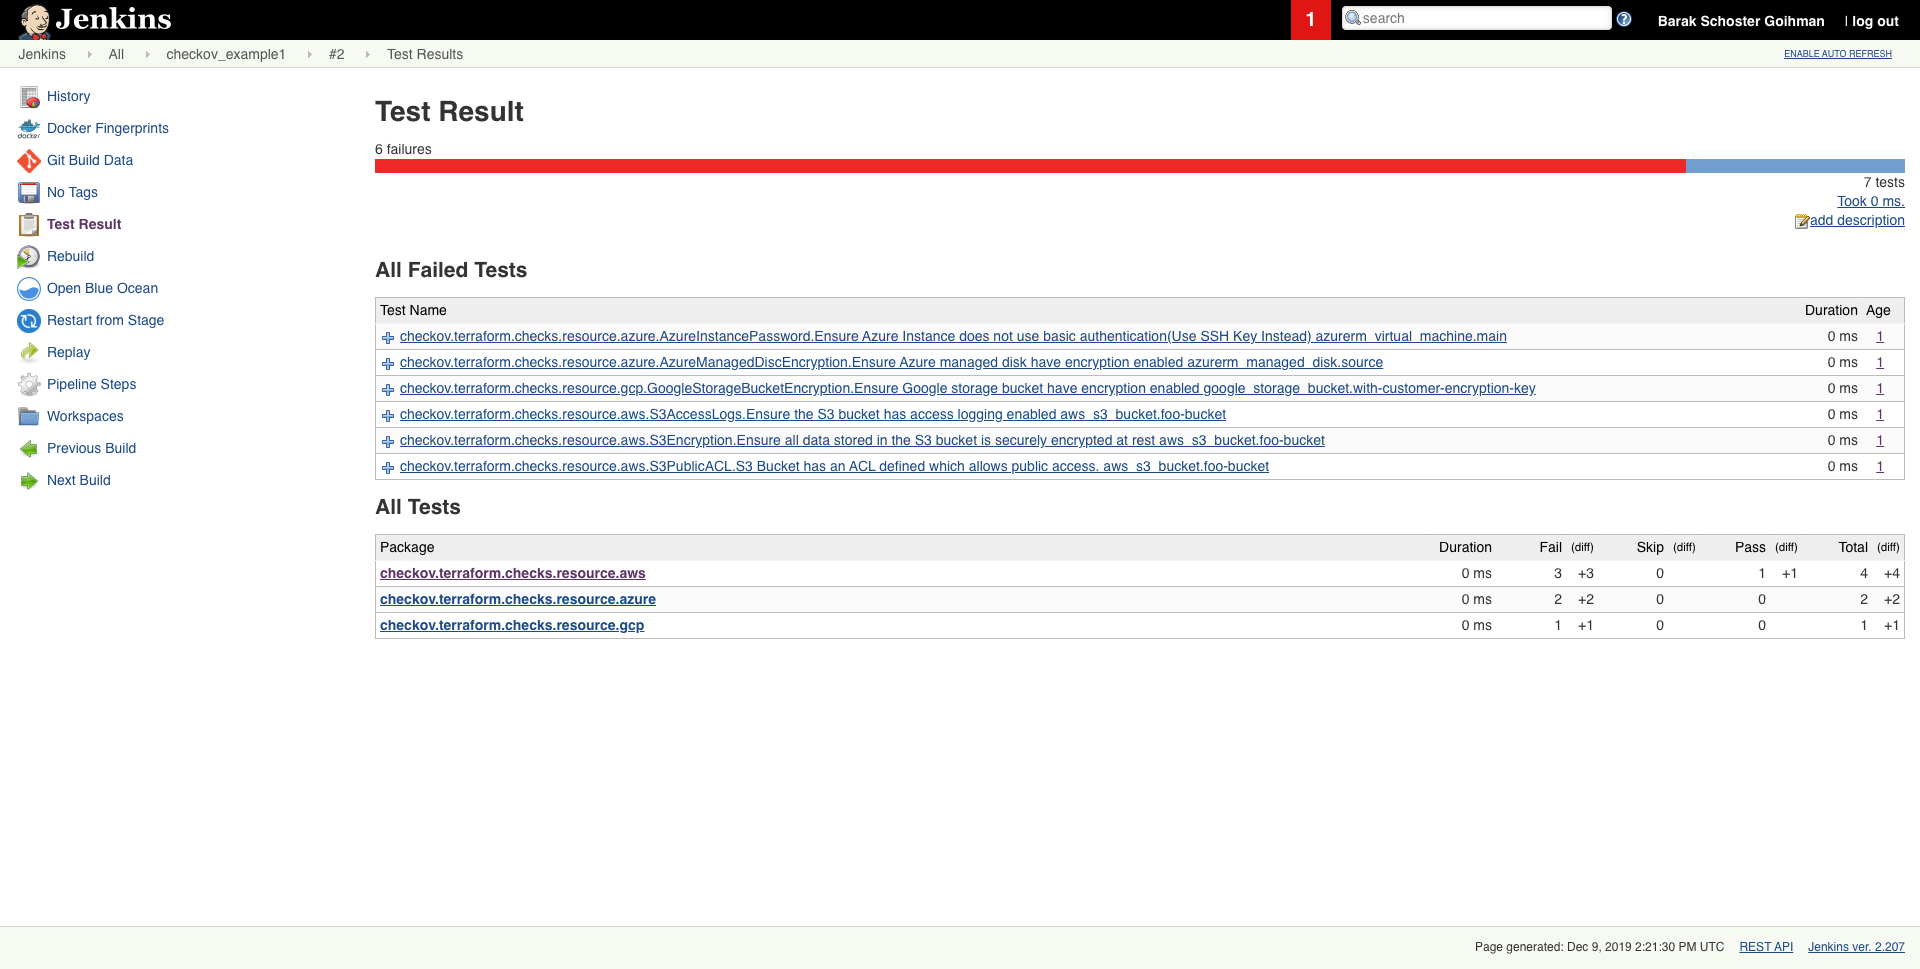 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 deepfence/secretscanner
:unlock: :unlock: Find secrets and passwords in container images and file systems :unlock: :unlock:
 cybersecsi/raudi
A repo to automatically generate and keep updated a series of Docker images through GitHub Actions.
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
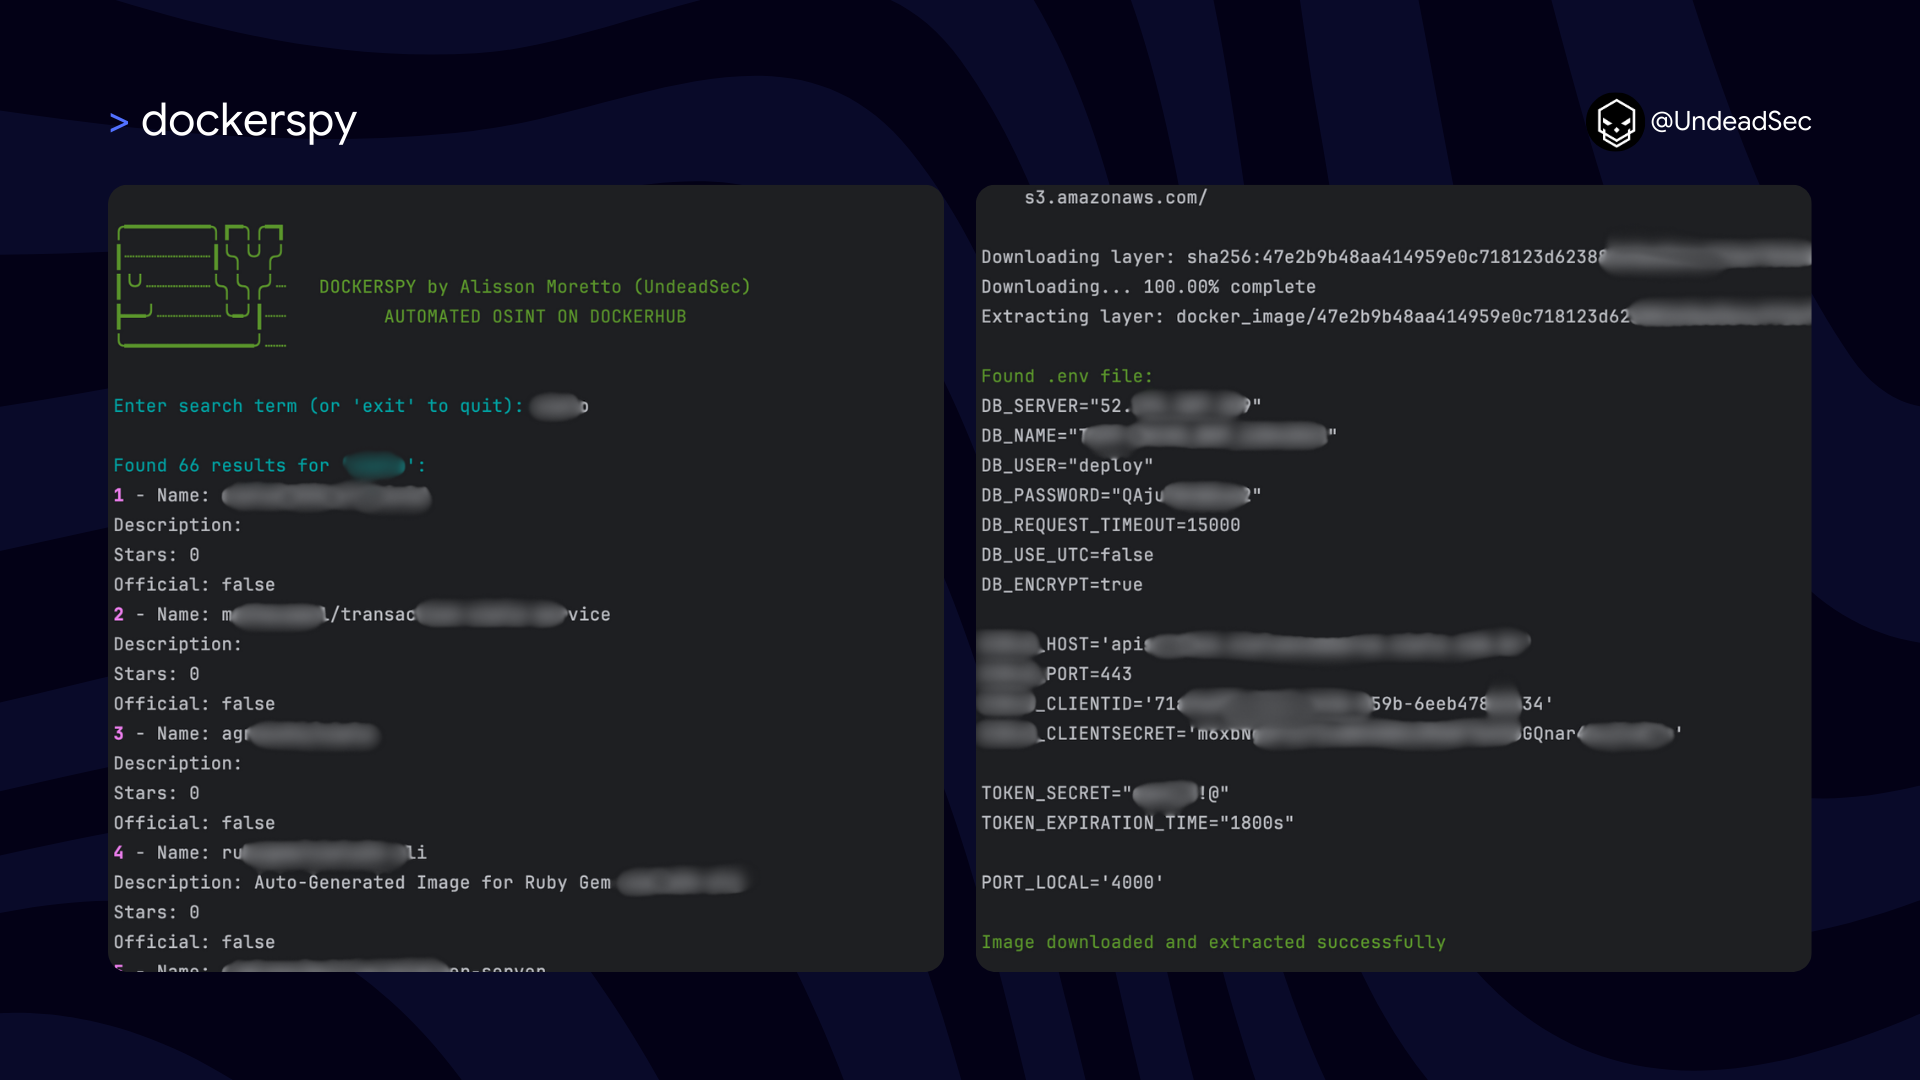 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 blueteamsteve/cve-2021-41773
Vulnerable docker images for CVE-2021-41773
 aquasecurity/trivy-plugin-kubectl
A Trivy plugin that scans the images of a kubernetes resource
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 ankur-katiyar/log4j-docker
Docker images and k8s YAMLs for Log4j Vulnerability POC (Log4j (CVE-2021-44228 RCE Vulnerability)