
CVE-2020-10665
 spaceraccoon/cve-2020-10665
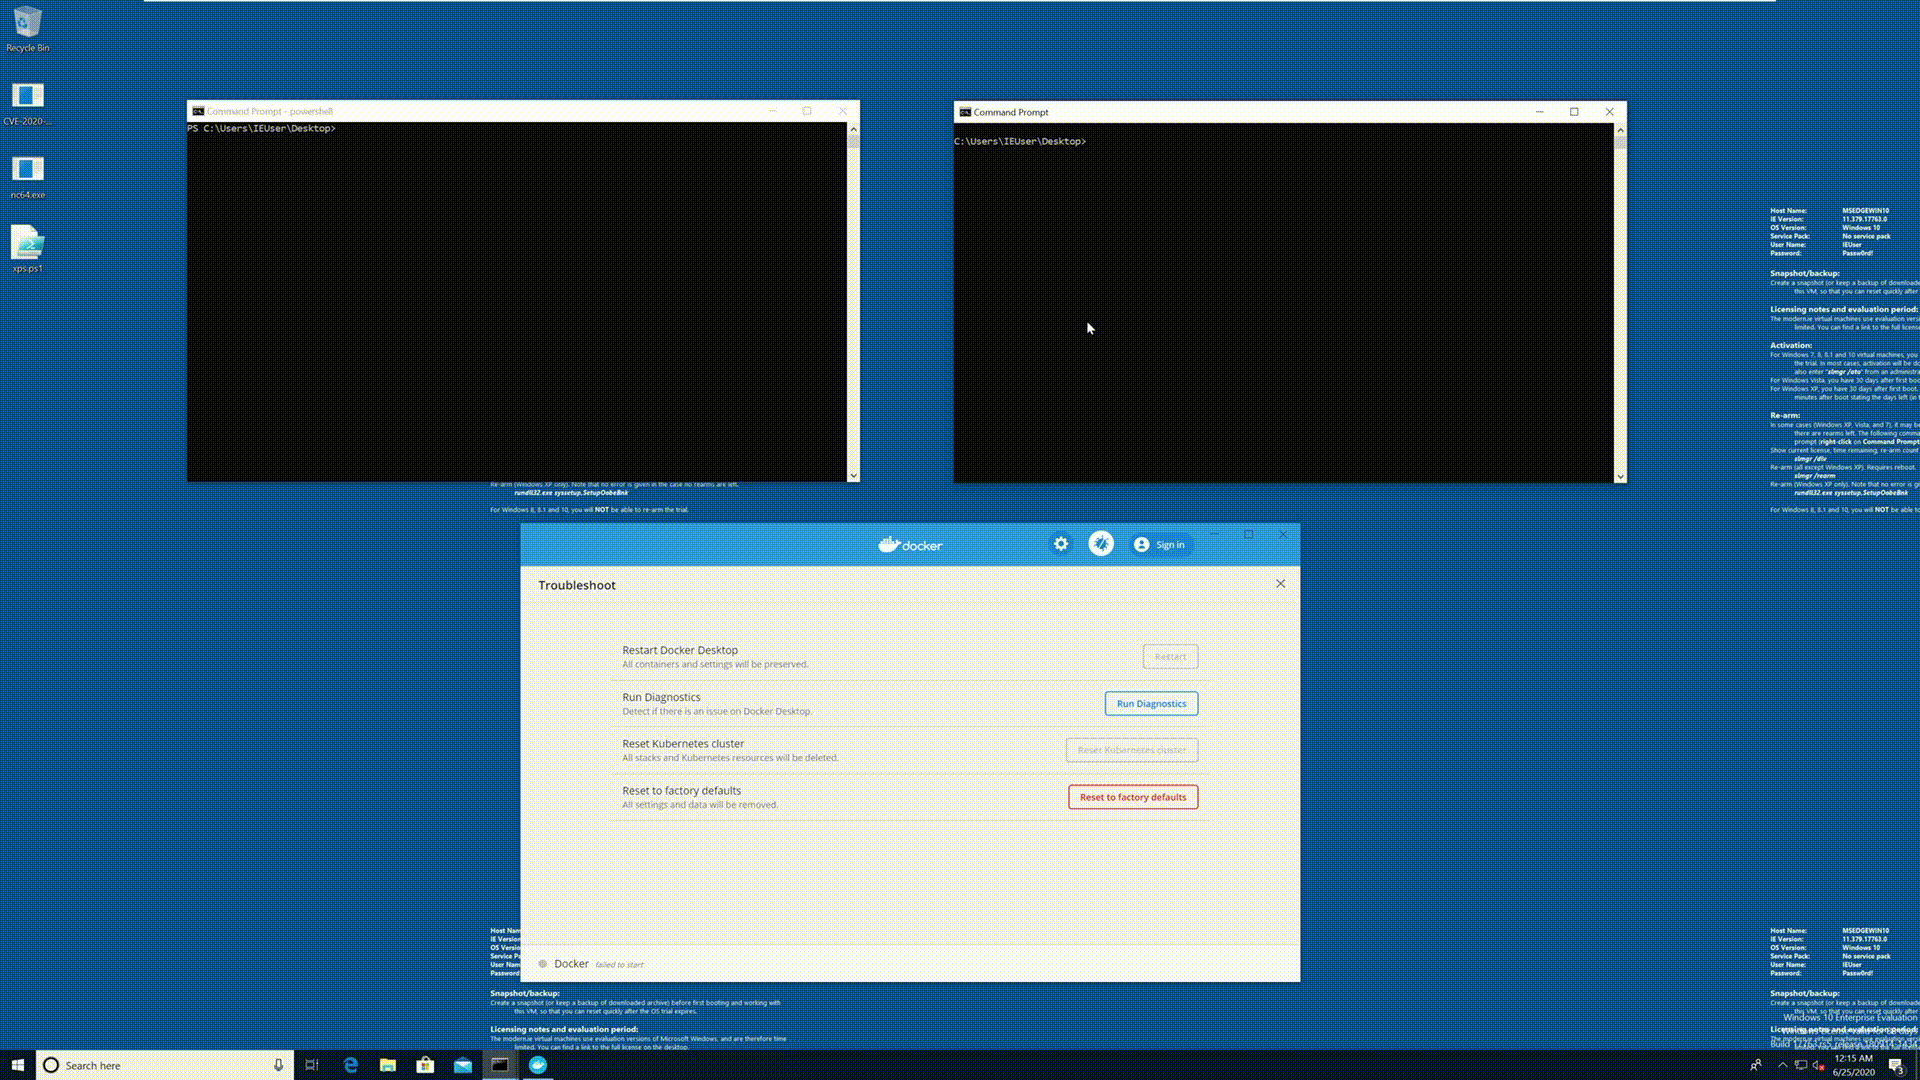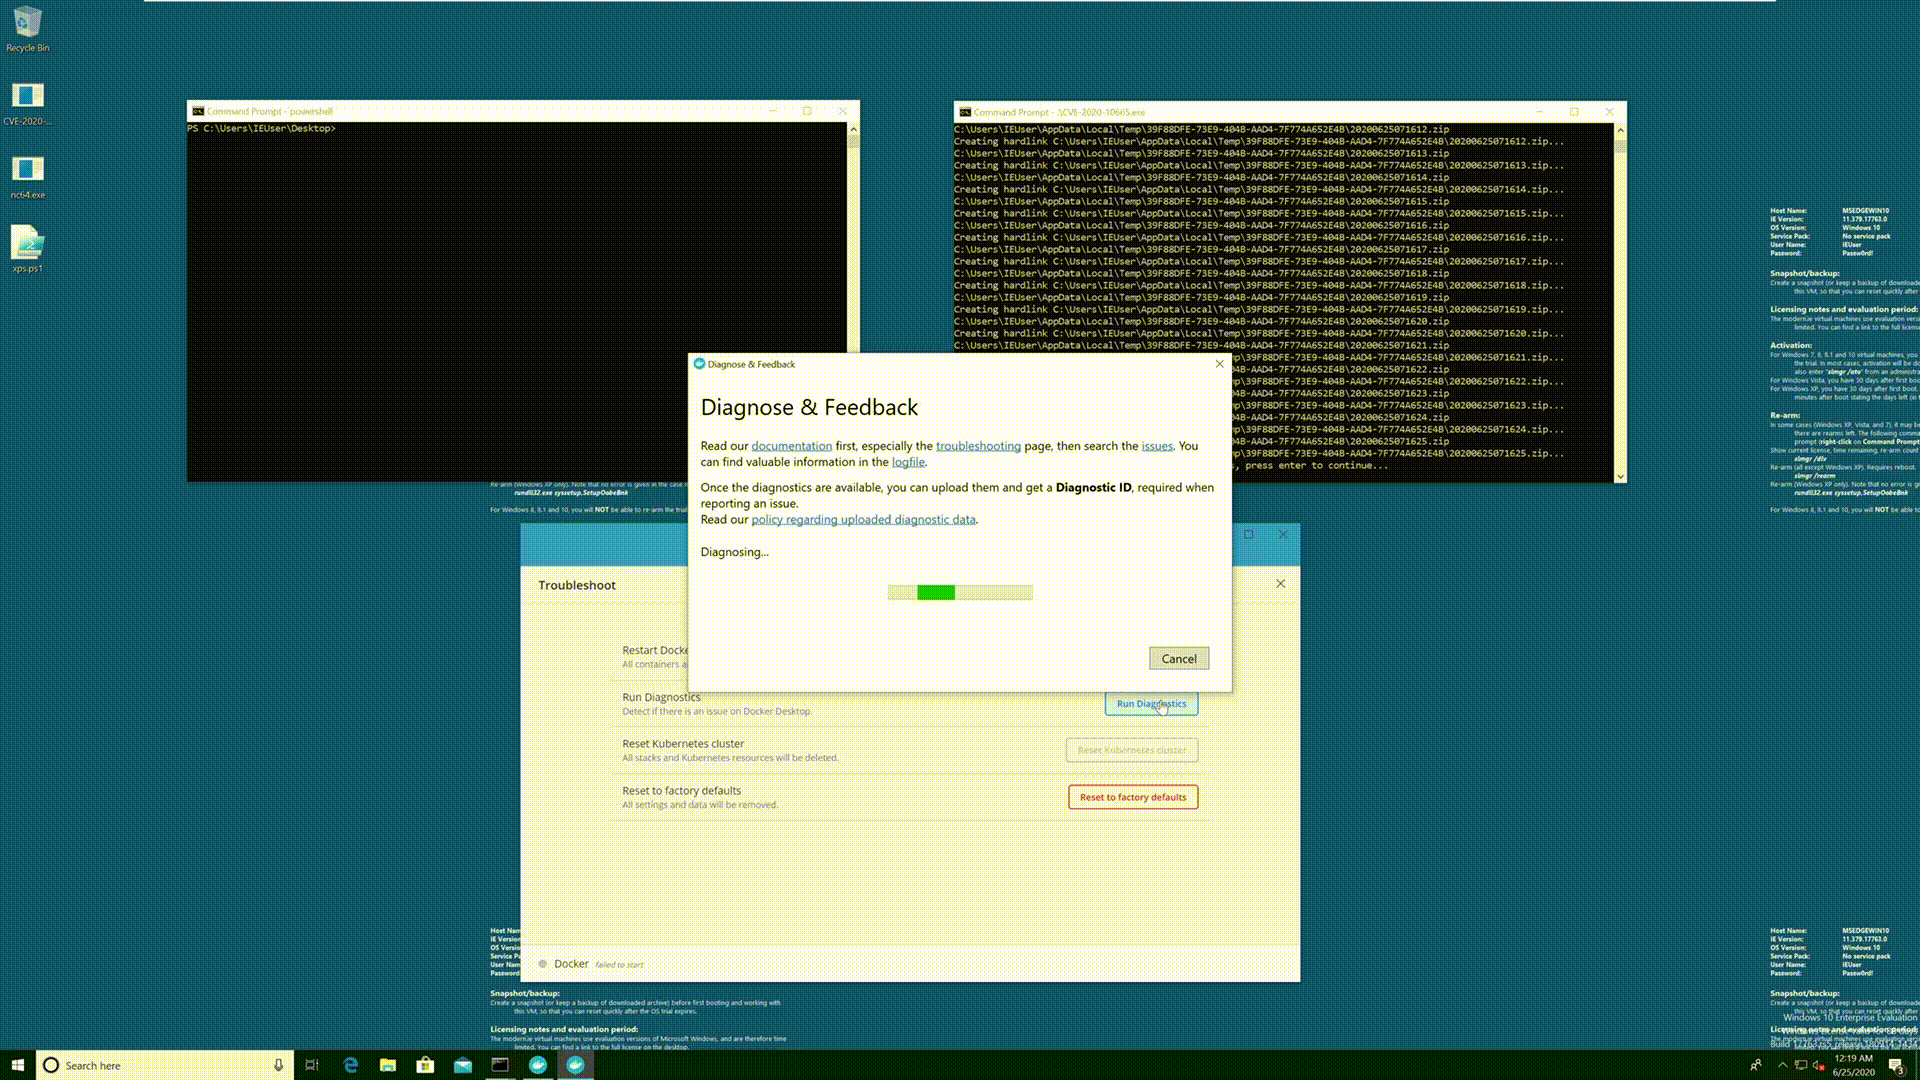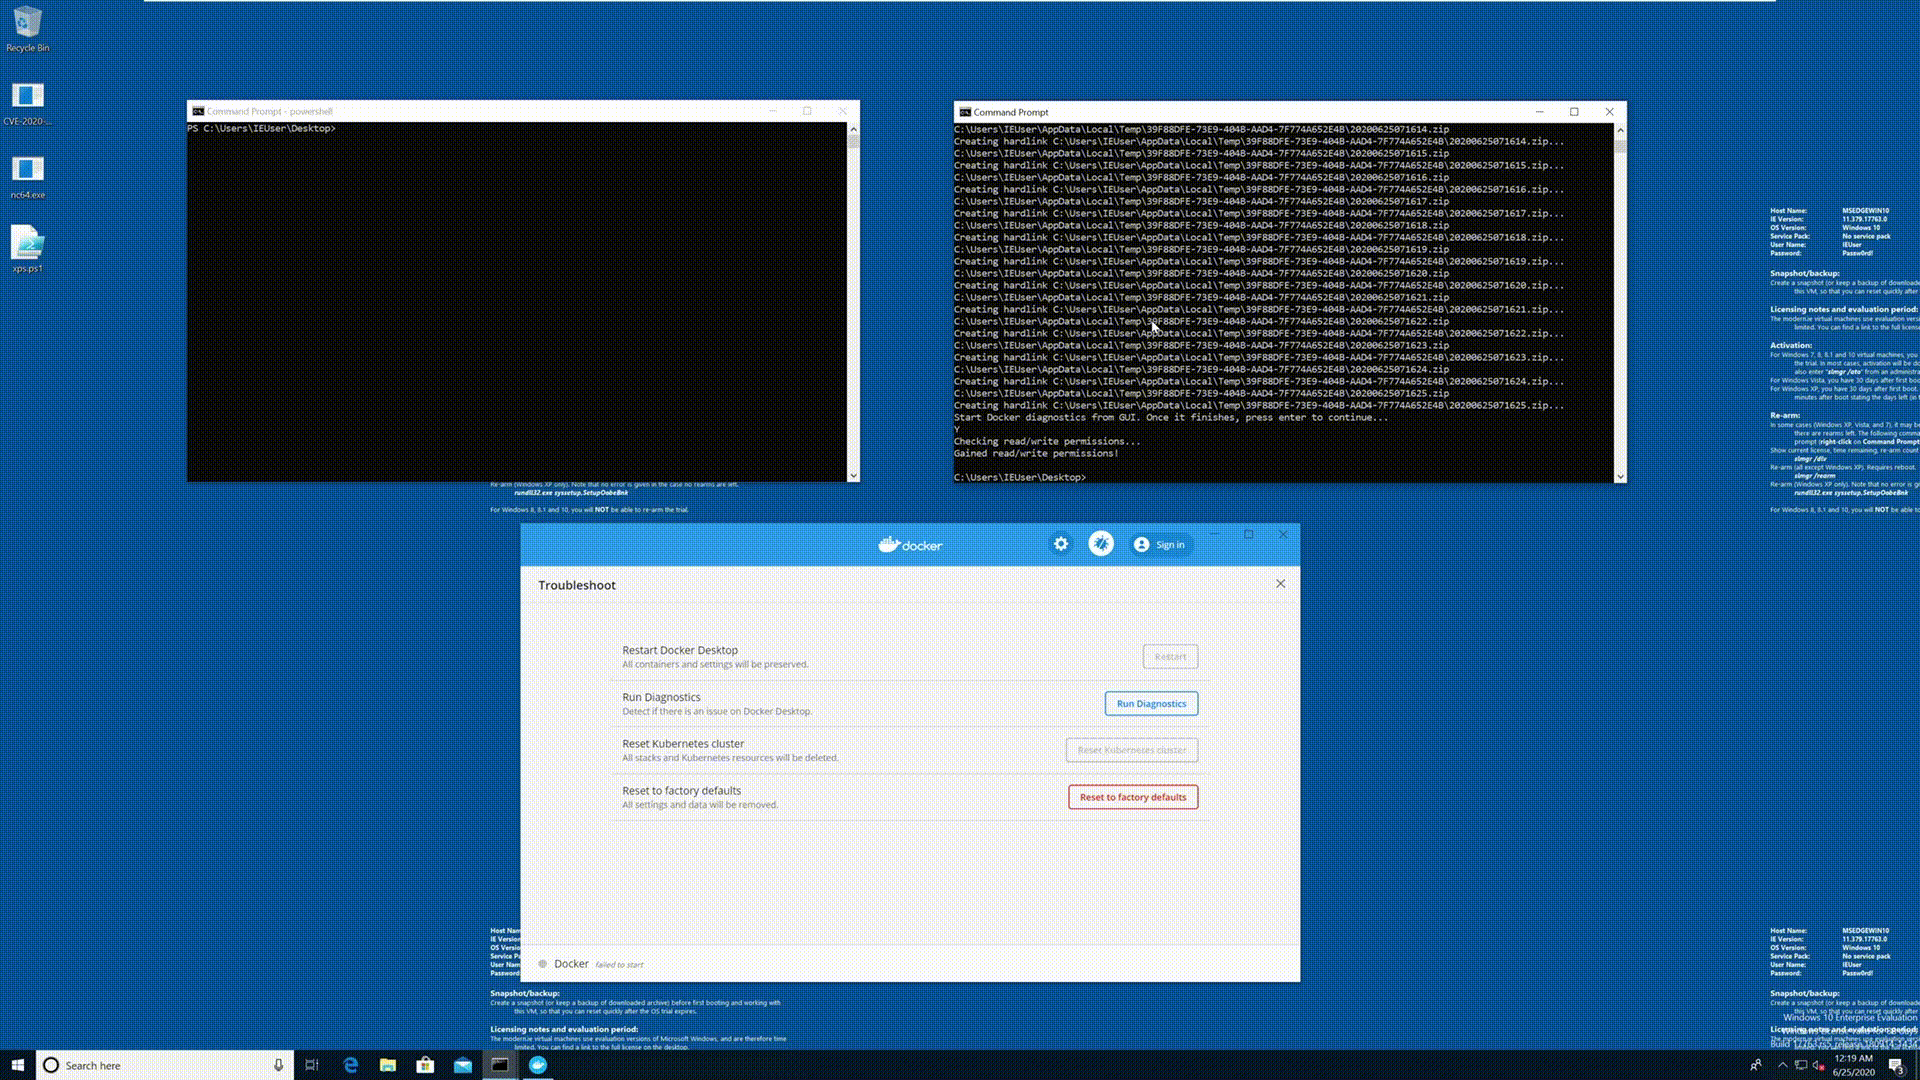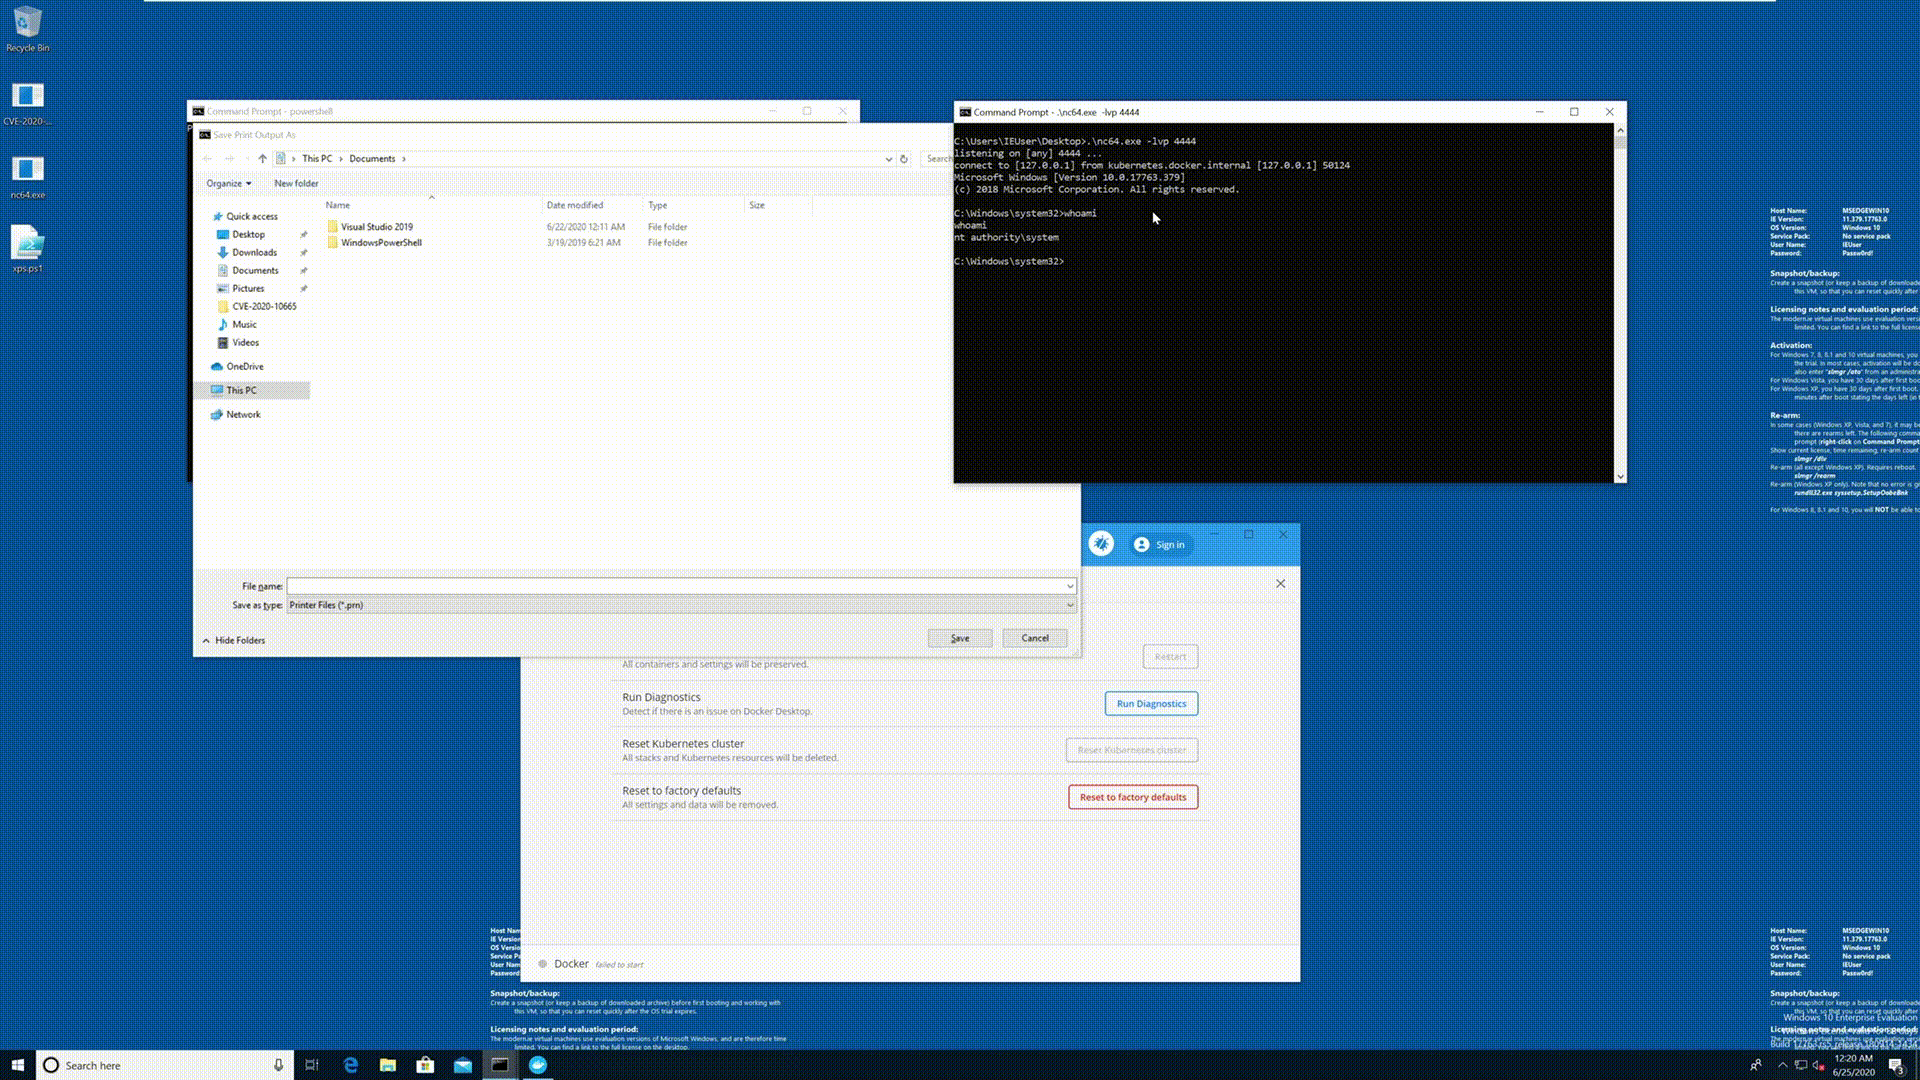
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
binary-exploitationcontainer-securityexploitation+2
52
spaceraccoon/cve-2020-10665POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 nccgroup/abstractshimmer
Proof of concept for CVE-2020-15257 in containerd.
 knqyf263/cve-2020-10749
Proof-of-concept exploit for CVE-2020-10749 demonstrating Kubernetes MitM attacks via IPv6 rogue router advertisements between pods.
 megadimenex/megahidocker
This project is exploit for some docker containers with similar to vulnerability code: CVE-2020-35191
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 twistlock/k8s-cve-2020-8554-mitigations
Prisma Cloud Compute Admission rules to mitigate Kubernetes CVE-2020-8554
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
 arax-zaeimi/docker-container-cve-2020-13401
Study on CVE-2020-13401 vulnerability of containers in dockers older than 19.03.11
 rancher/externalip-webhook
CVE-2020-8554: Man in the middle using LoadBalancer or ExternalIPs