rootpacket-cve-2026-31431

Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…

Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…

Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…

OpenSSH remote DOS exploit and vulnerable container

BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide

Poc for CVE-2026-34197

Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

CLI tool and library for generating a Software Bill of Materials from container images and filesystems

Code signing and transparency for containers and binaries

Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.

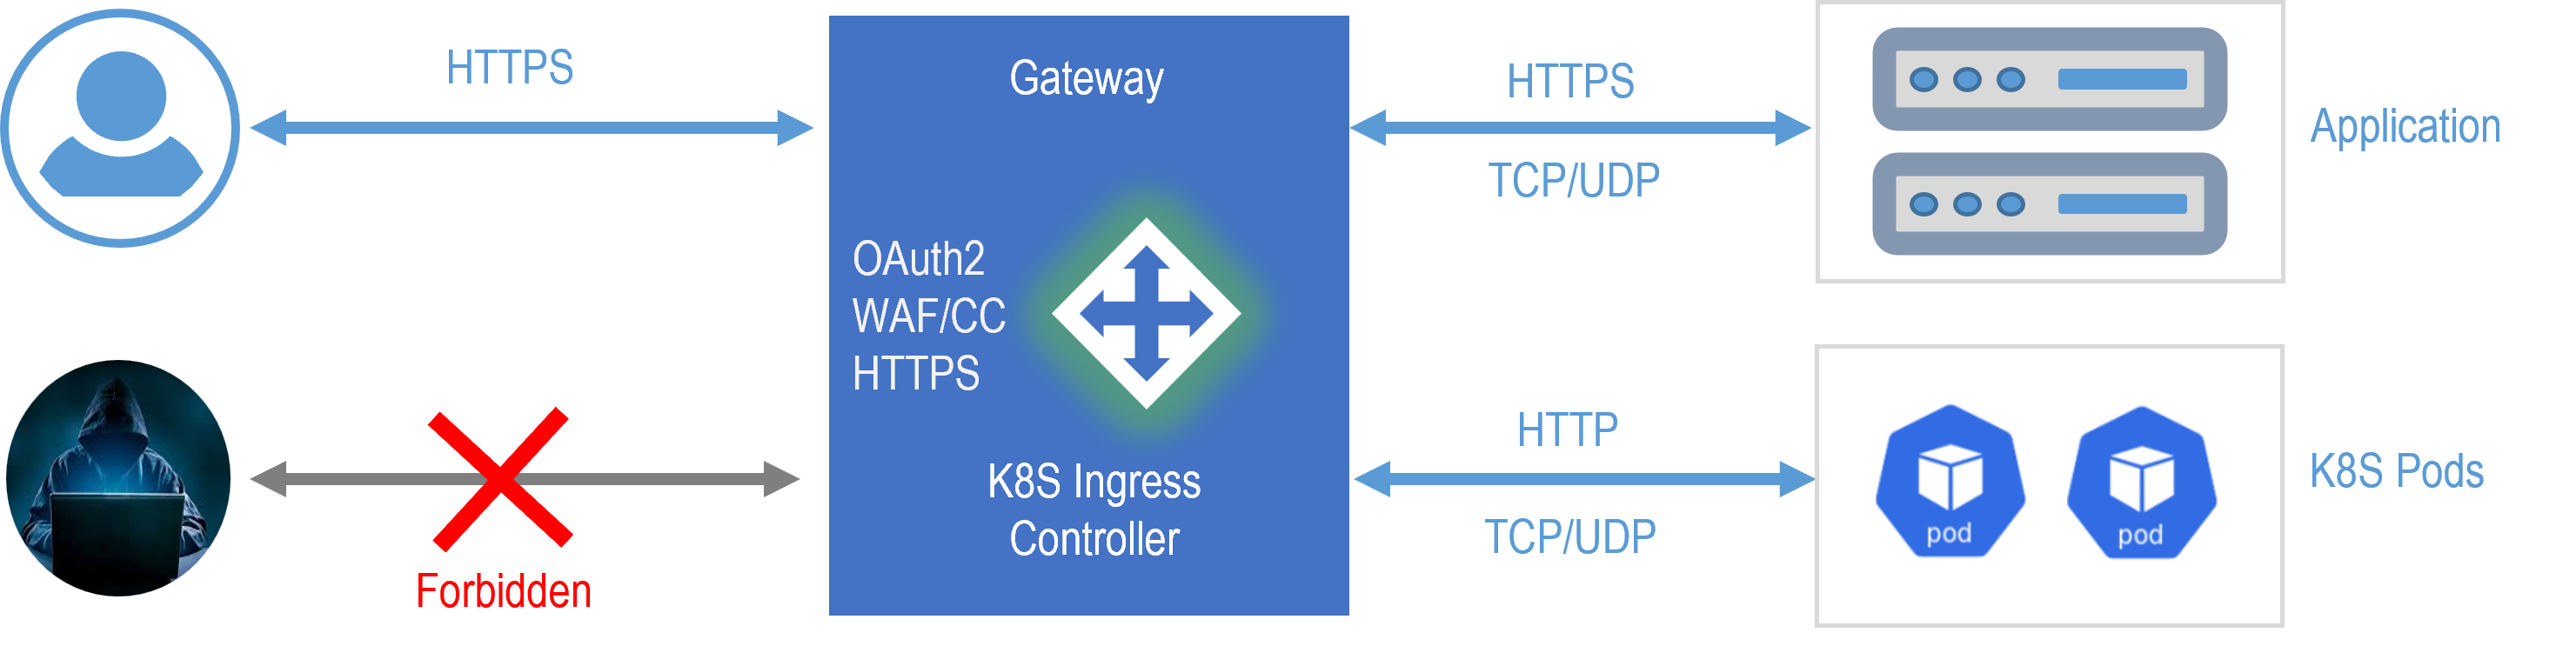
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…

Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…

A container analysis and exploitation tool for pentesters and engineers.

Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…

eBPF-driven security tool for locking and auditing Linux machines. Restricts kernel features, blocks fileless execution, protects memory, and hardens…

A collection of scripts, and tips and tricks for hacking k8s clusters and containers.

Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.

Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.

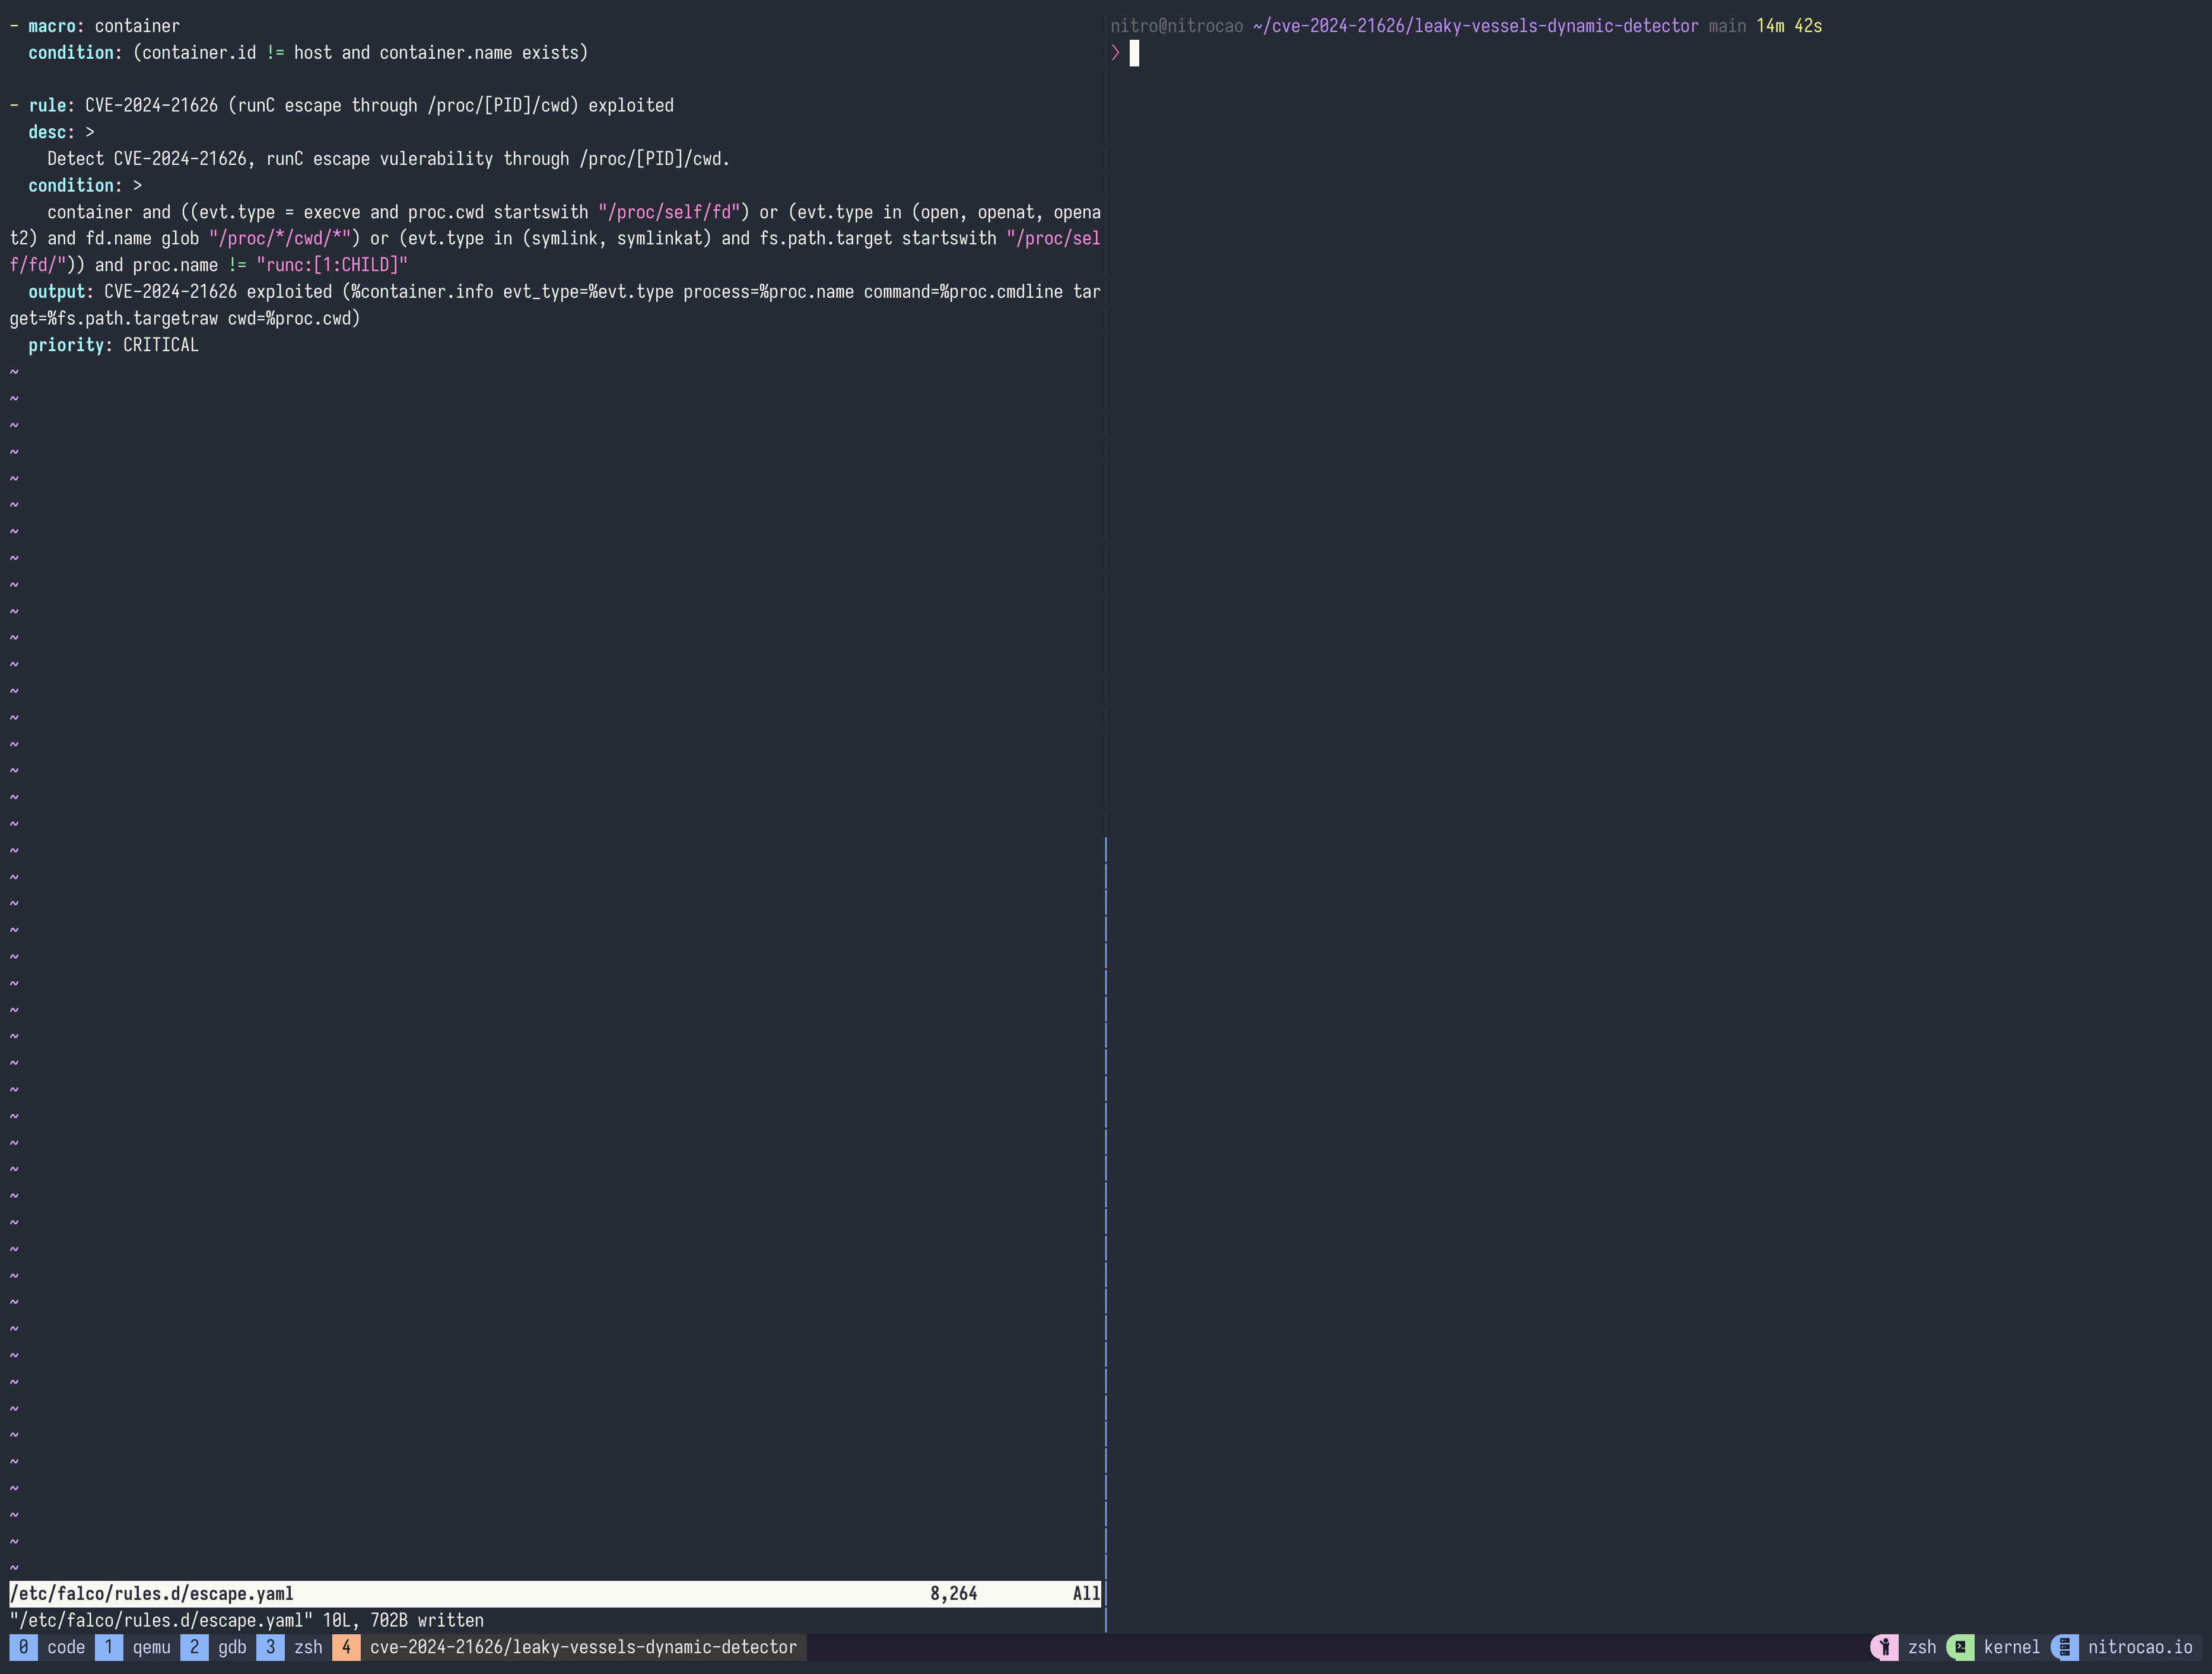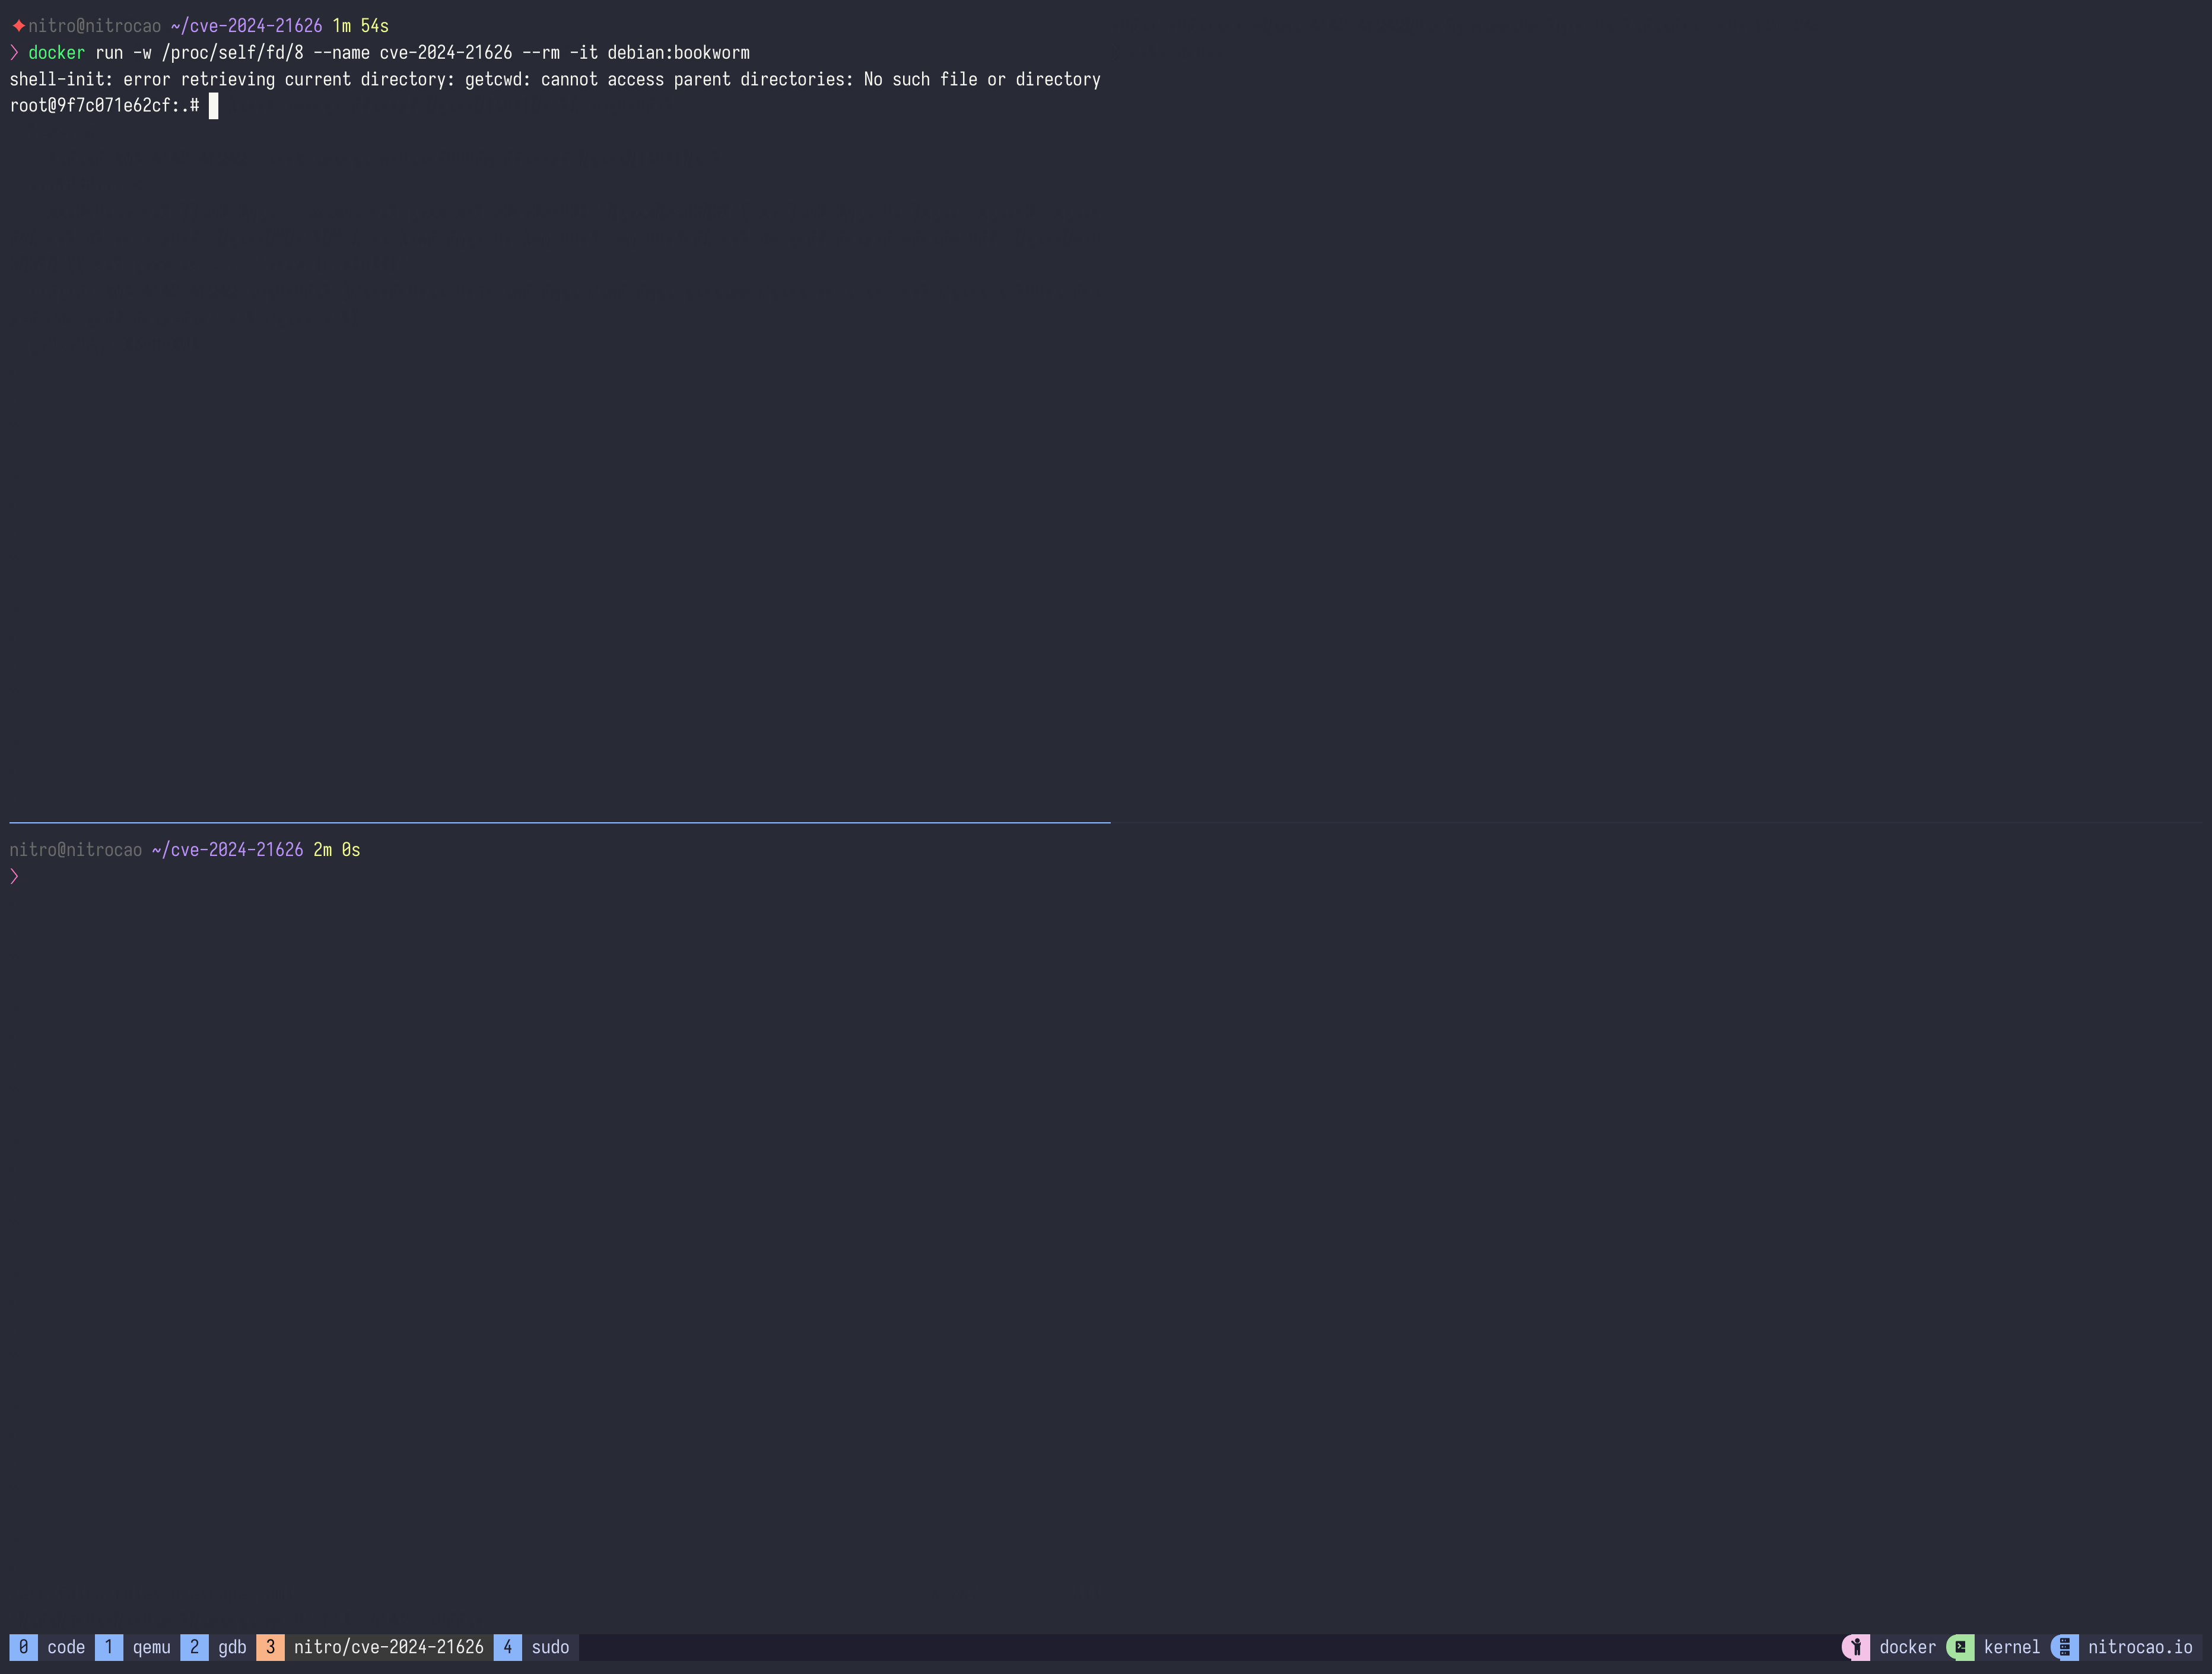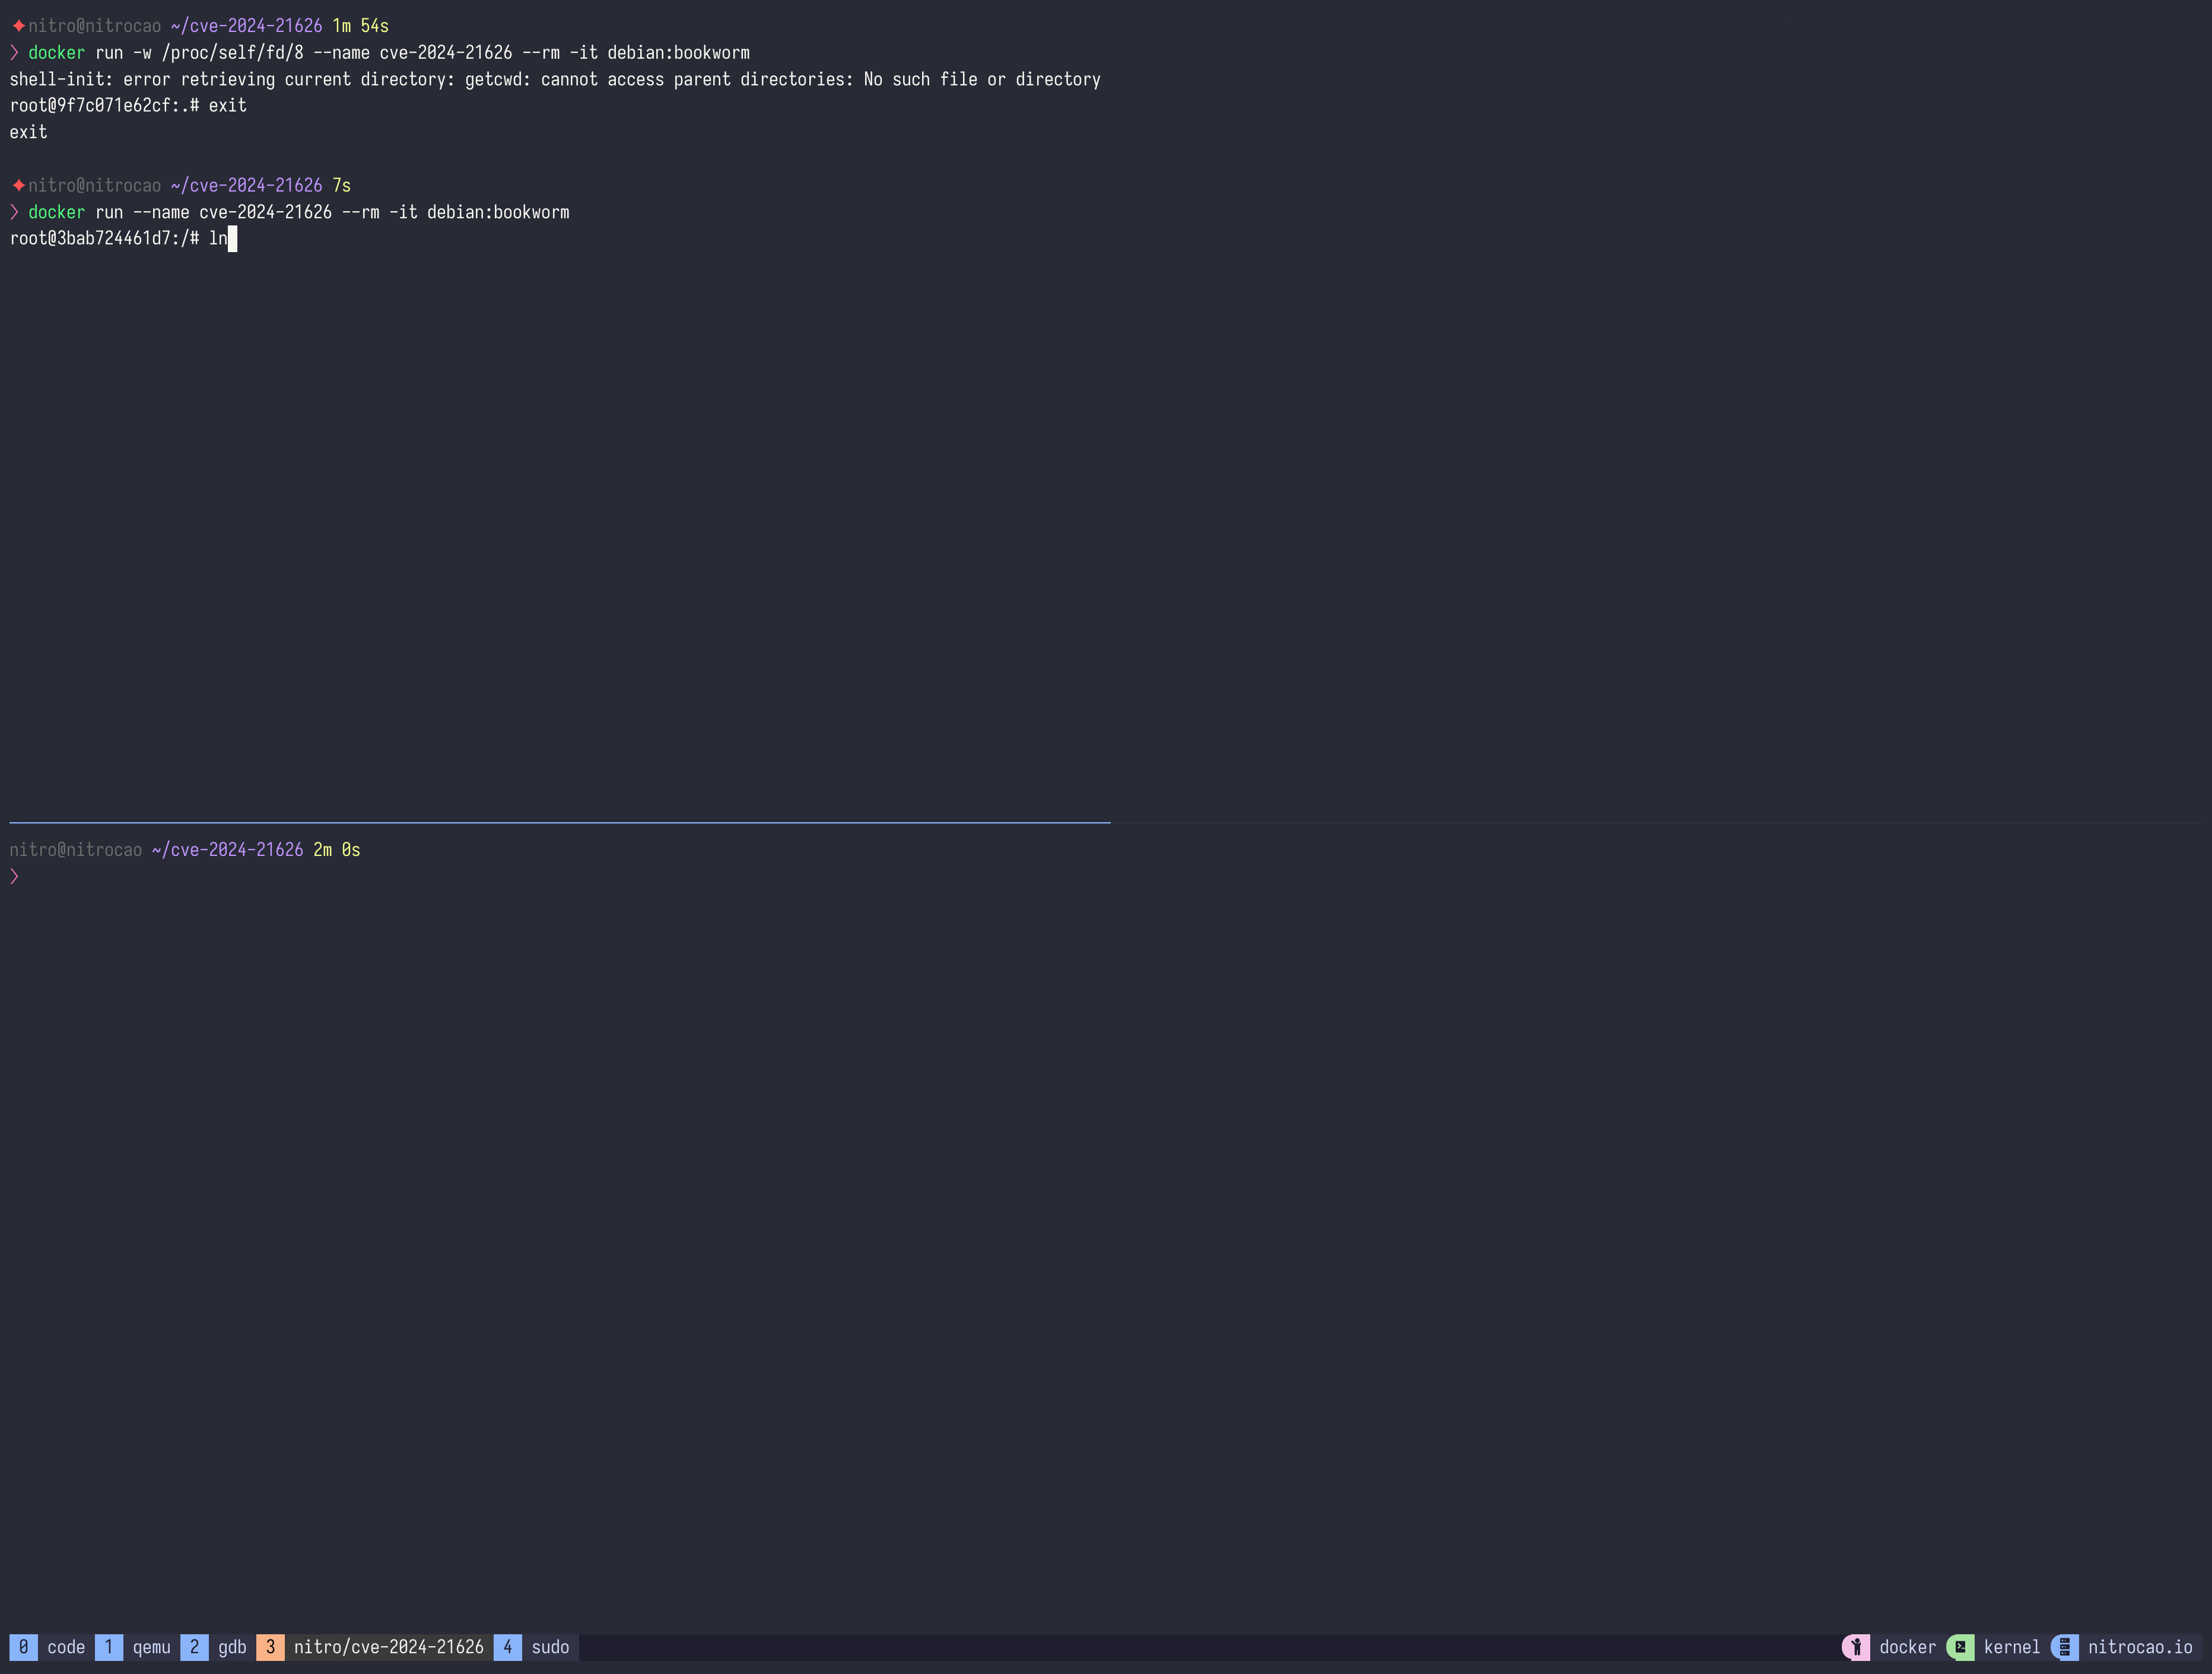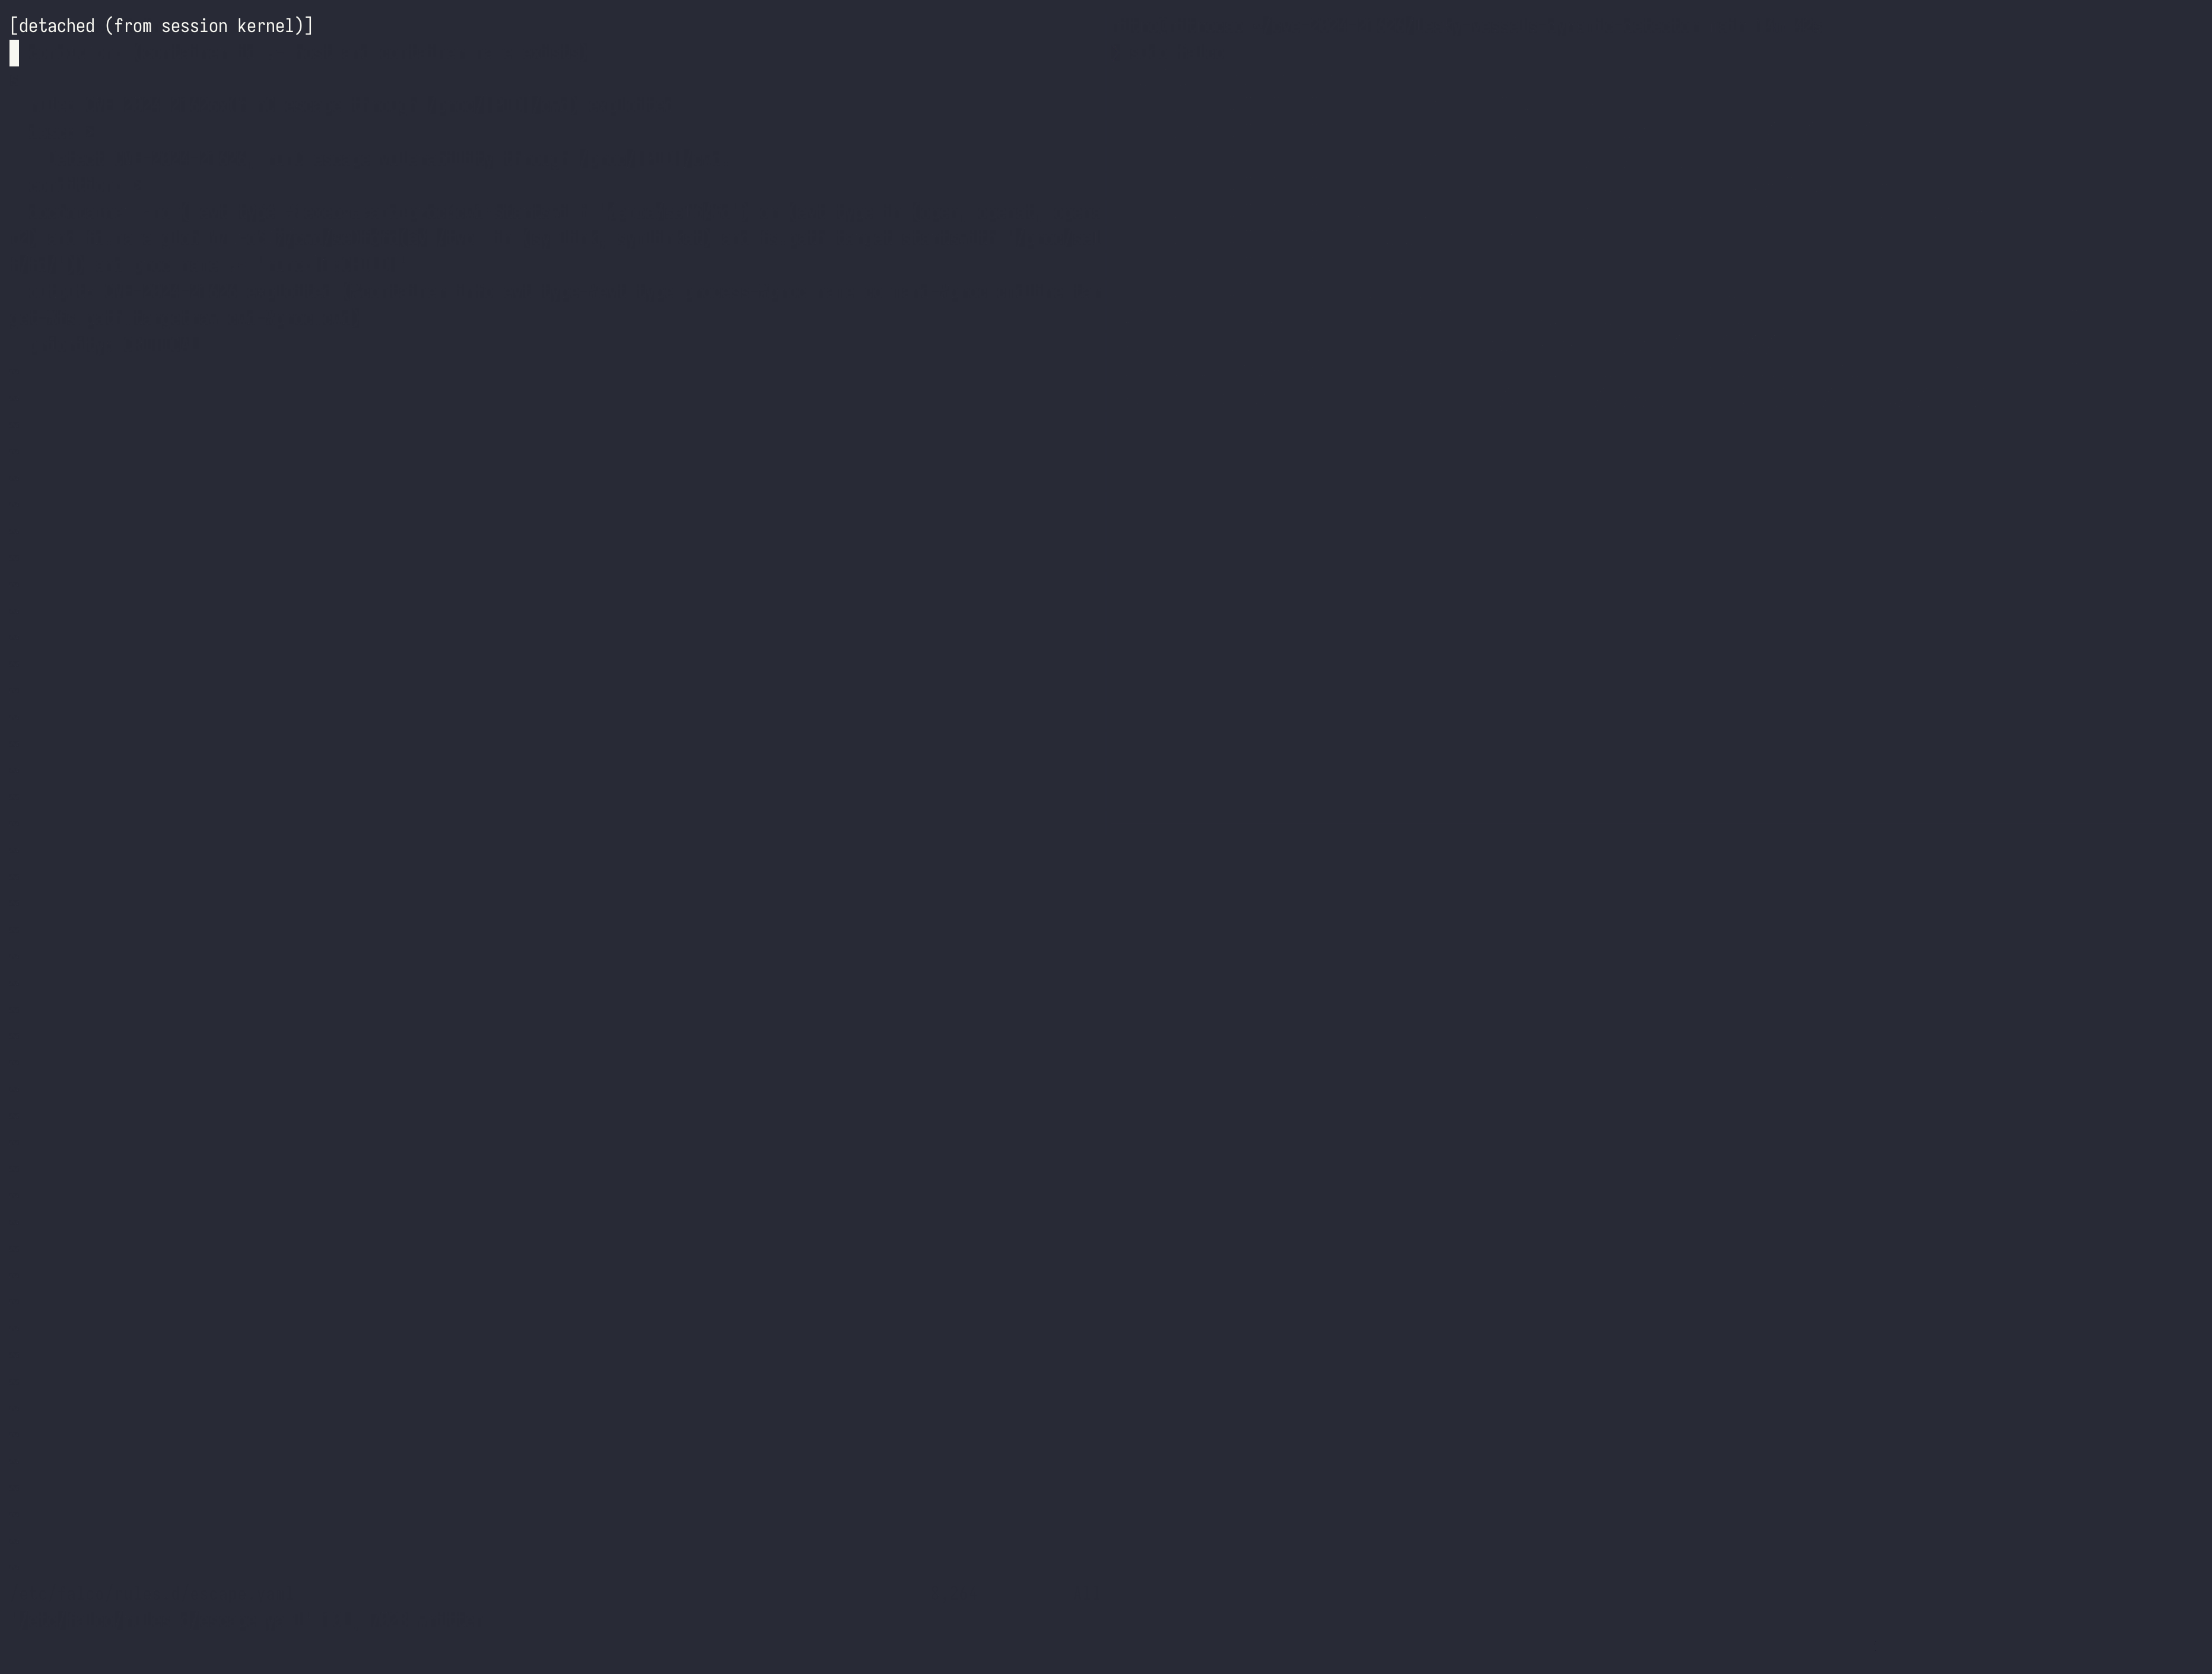
PoC and Detection for CVE-2024-21626