
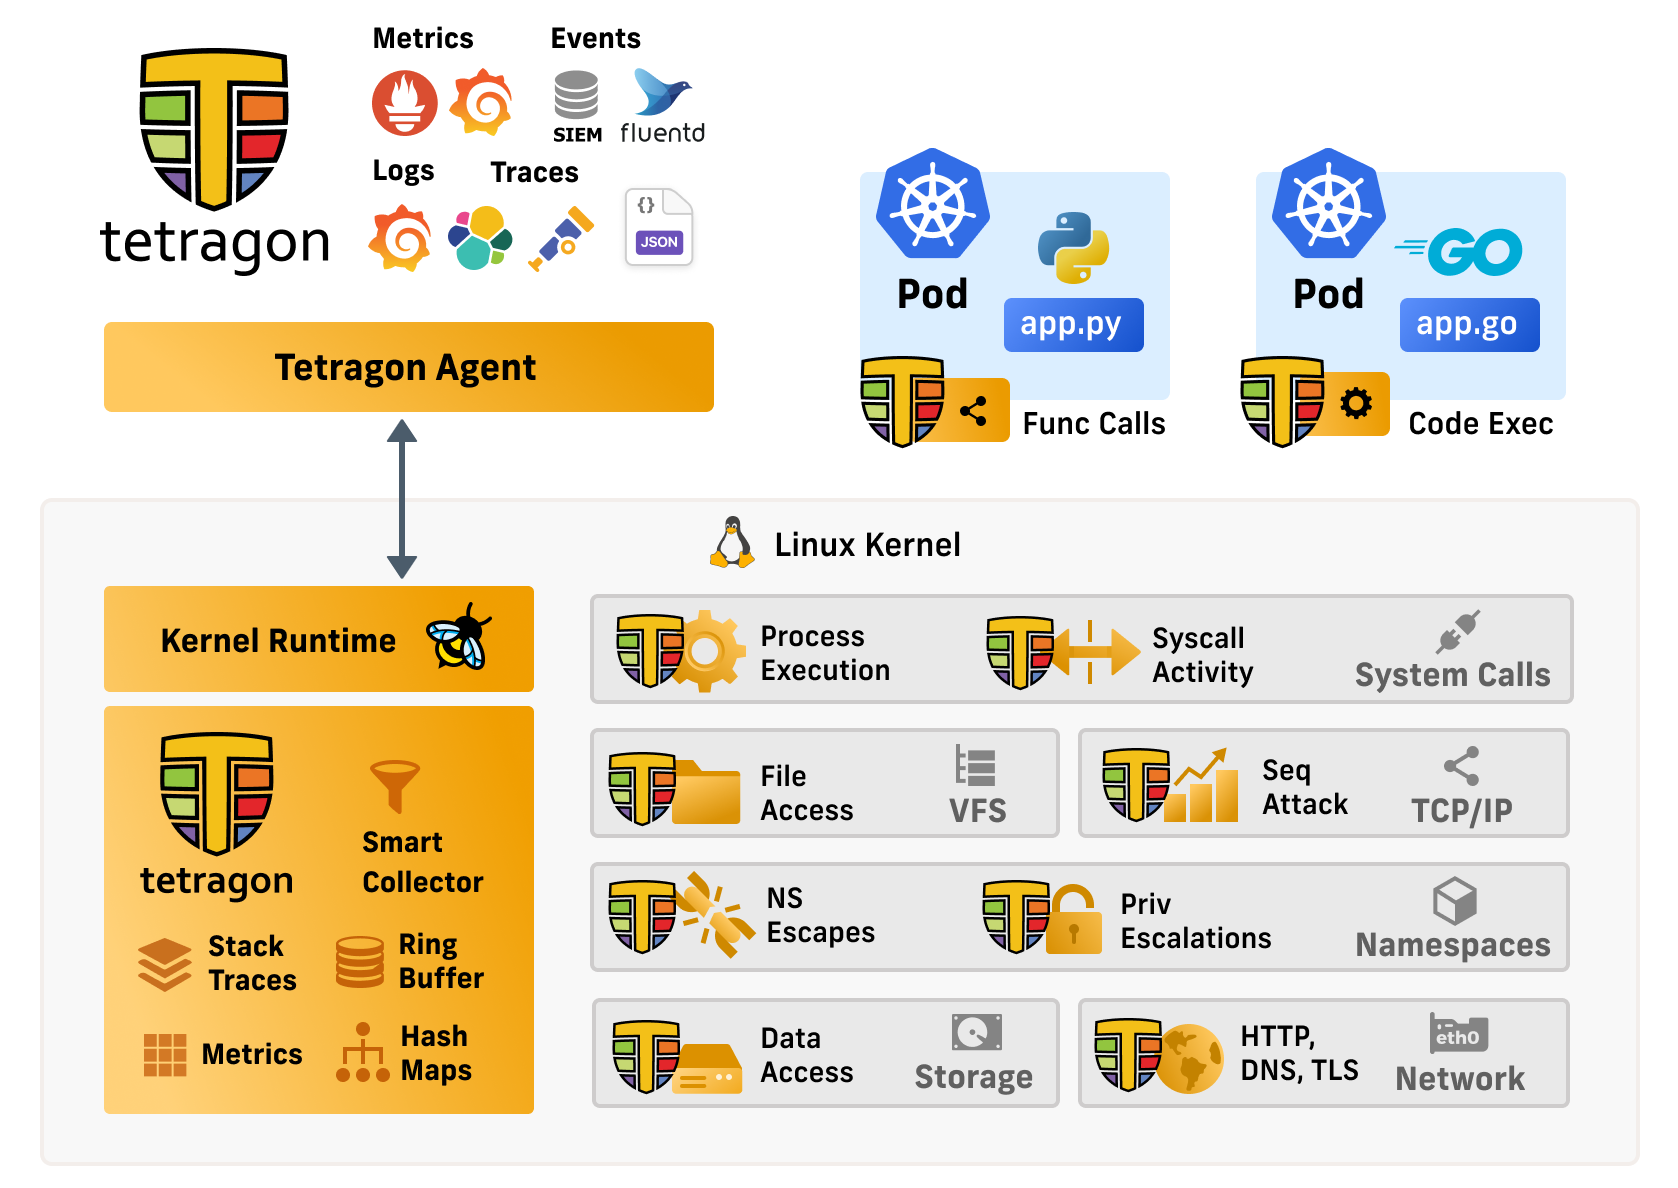
tetragon
 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
chaos-engineeringcloud-securitycontainer-security+2
cilium/tetragoneBPF-based Security Observability and Runtime Enforcement
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 j3r1ch0123/cve-2025-9074
New vulnerability found in Docker. Credit for finding the vulnerability goes to Felix Boulet
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
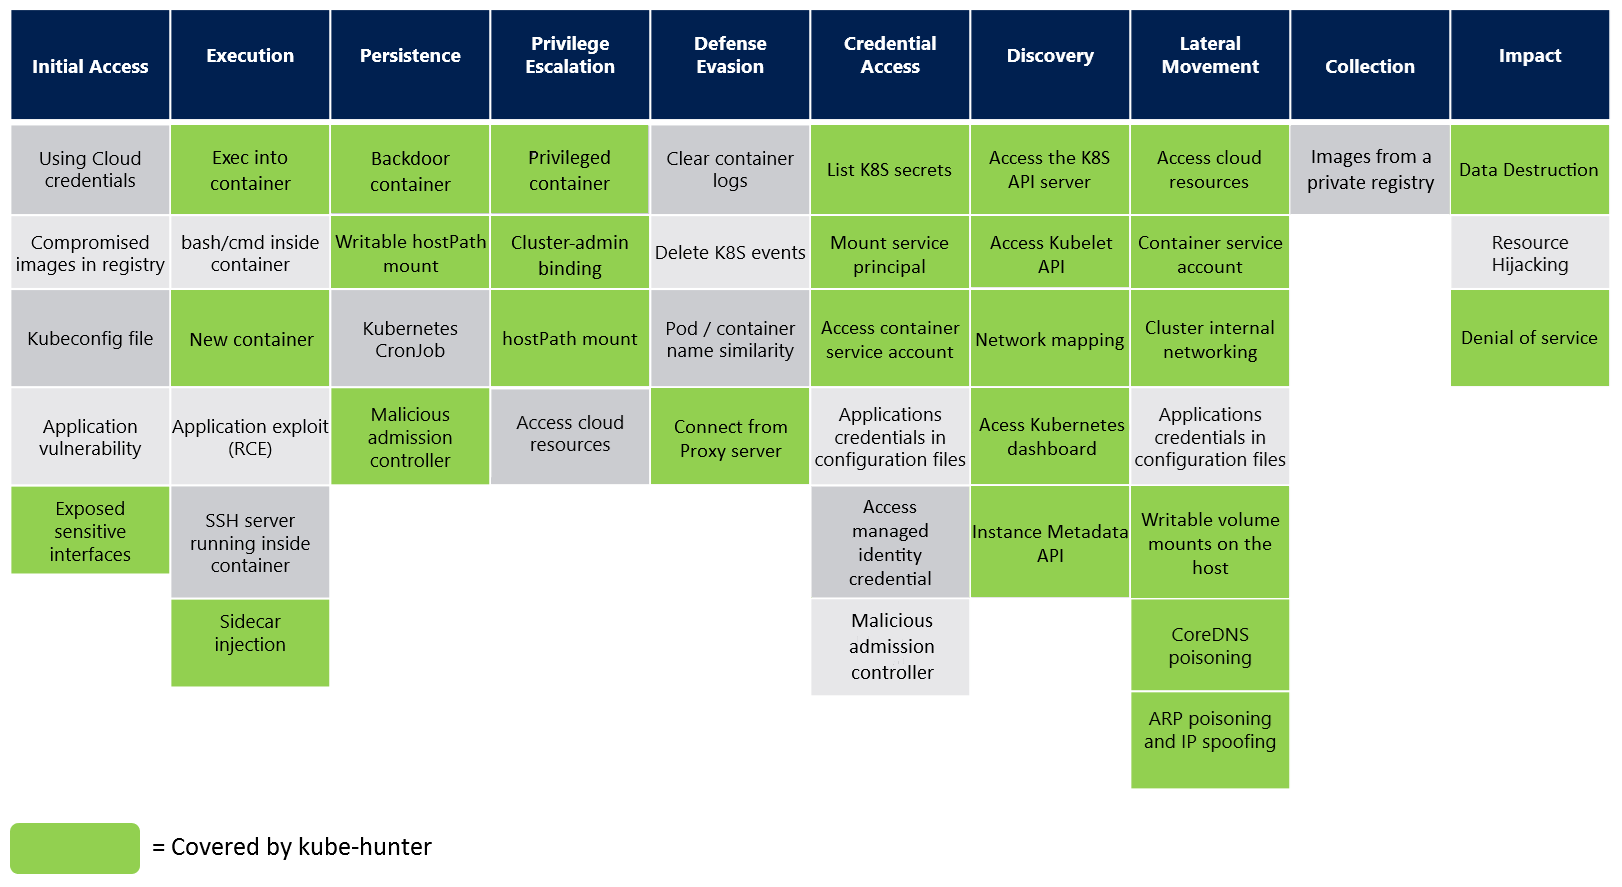 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 sofianehamlaoui/cve-2022-0492-checker
A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
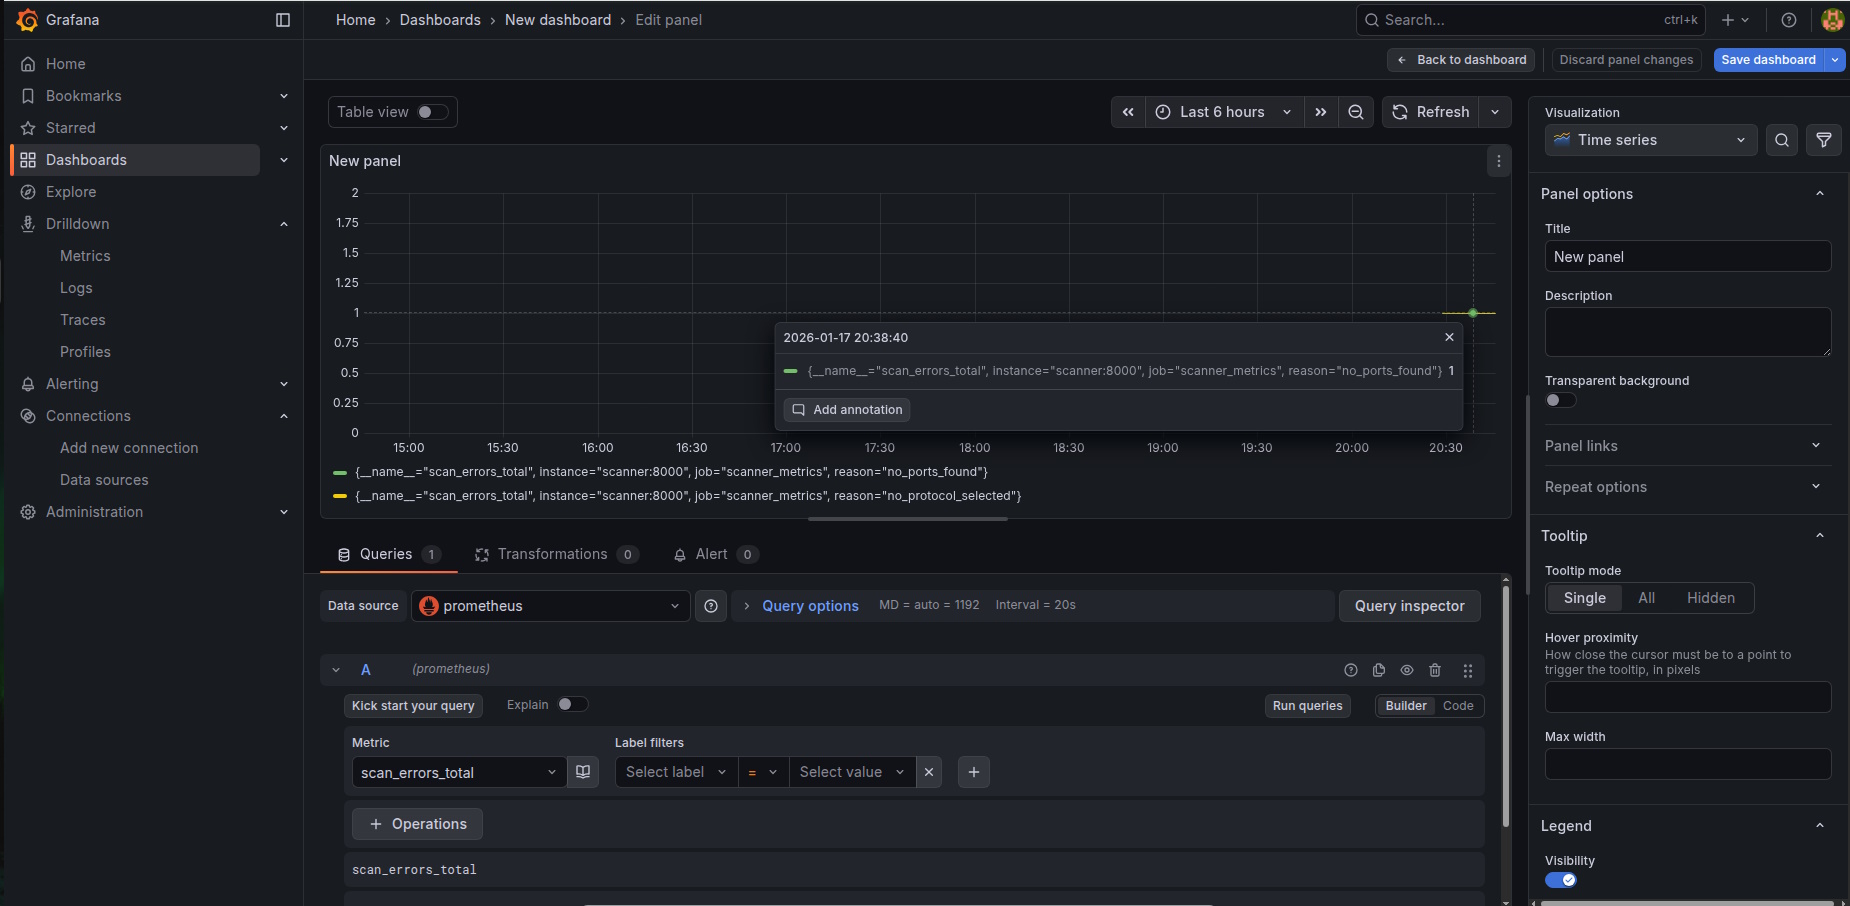 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 trackflaw/cve-2023-7028-docker
Repository to install CVE-2023-7028 vulnerable Gitlab instance
 matrexdz/cve-2024-1071-docker
Docker-based lab for practicing WordPress CVE-2024-1071 exploitation with automated PoC scripts and step-by-step setup instructions.
 shoucheng3/kubernetes-client__java_cve-2020-8570_client-java-parent-9_0_2_fixed
Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…