

ccat
 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
cloud-securitycontainer-securityexploitation+1
652
rhinosecuritylabs/ccatCloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
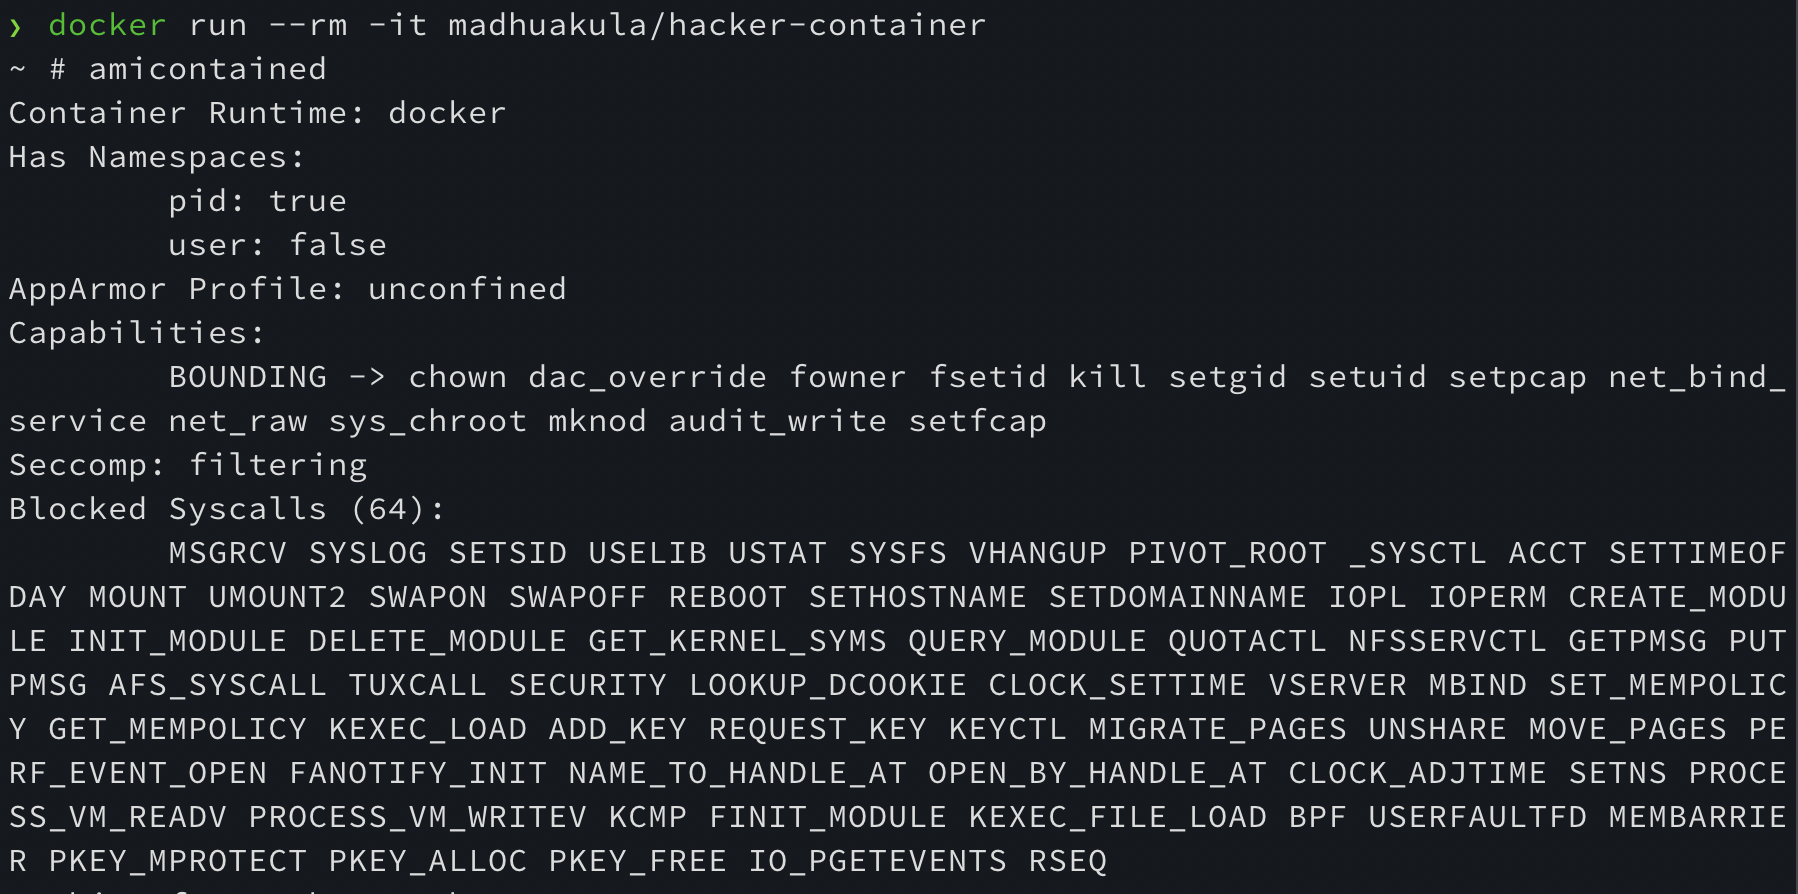 madhuakula/hacker-container
The Swiss Army Container for Cloud Native Security. Container with all the list of useful tools/commands while hacking and securing Containers,…
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 kubeshop/testkube
☸️ The Testing Platform for the agentic SDLC
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 qi4l/cve-2026-31431-container-escape
Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…

 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 kimjuhyeong95/cve-2025-24514
Remote vulnerability scanner for CVE-2025-24514, an ingress-nginx auth-url injection leading to NGINX config manipulation and potential RCE.…
 shoucheng3/apache__dolphinscheduler_cve-2023-49109_3-2-0
Exploit for CVE-2023-49109 targeting Apache DolphinScheduler, a cloud-native data orchestration platform. Enables security testing of workflow…
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…