

vuls
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
cloud-securityconfiguration-auditingcontainer-security+5
12.3k
future-architect/vulsAgent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 gen0sec/jailer
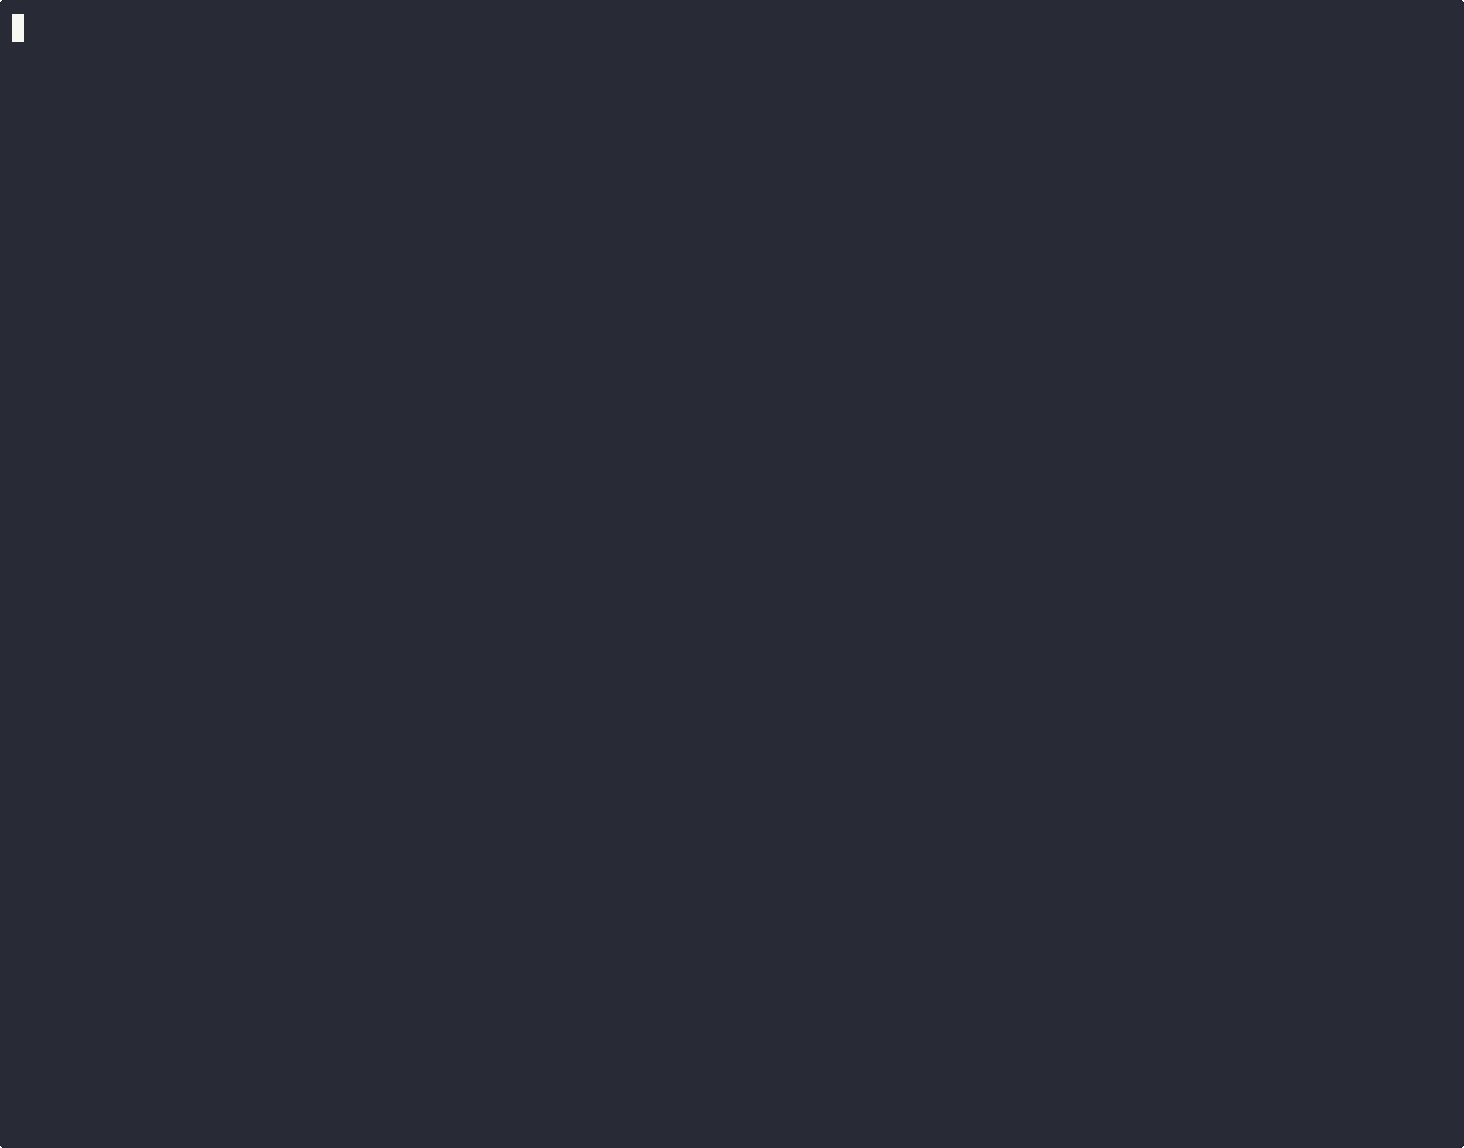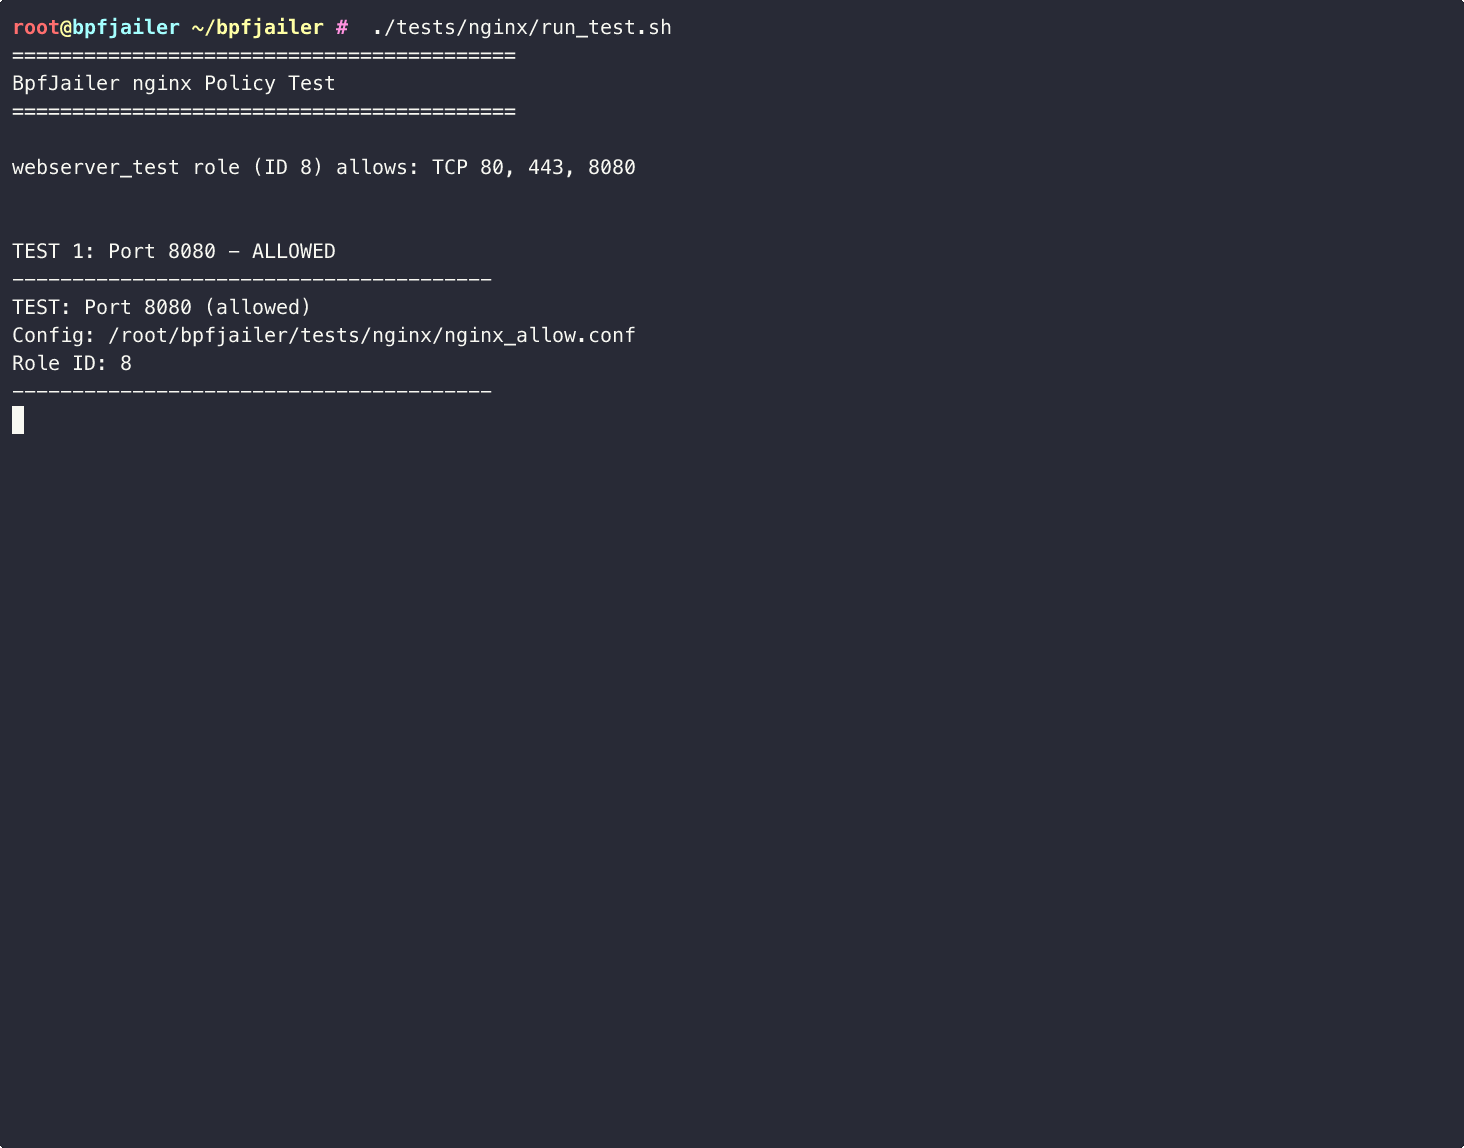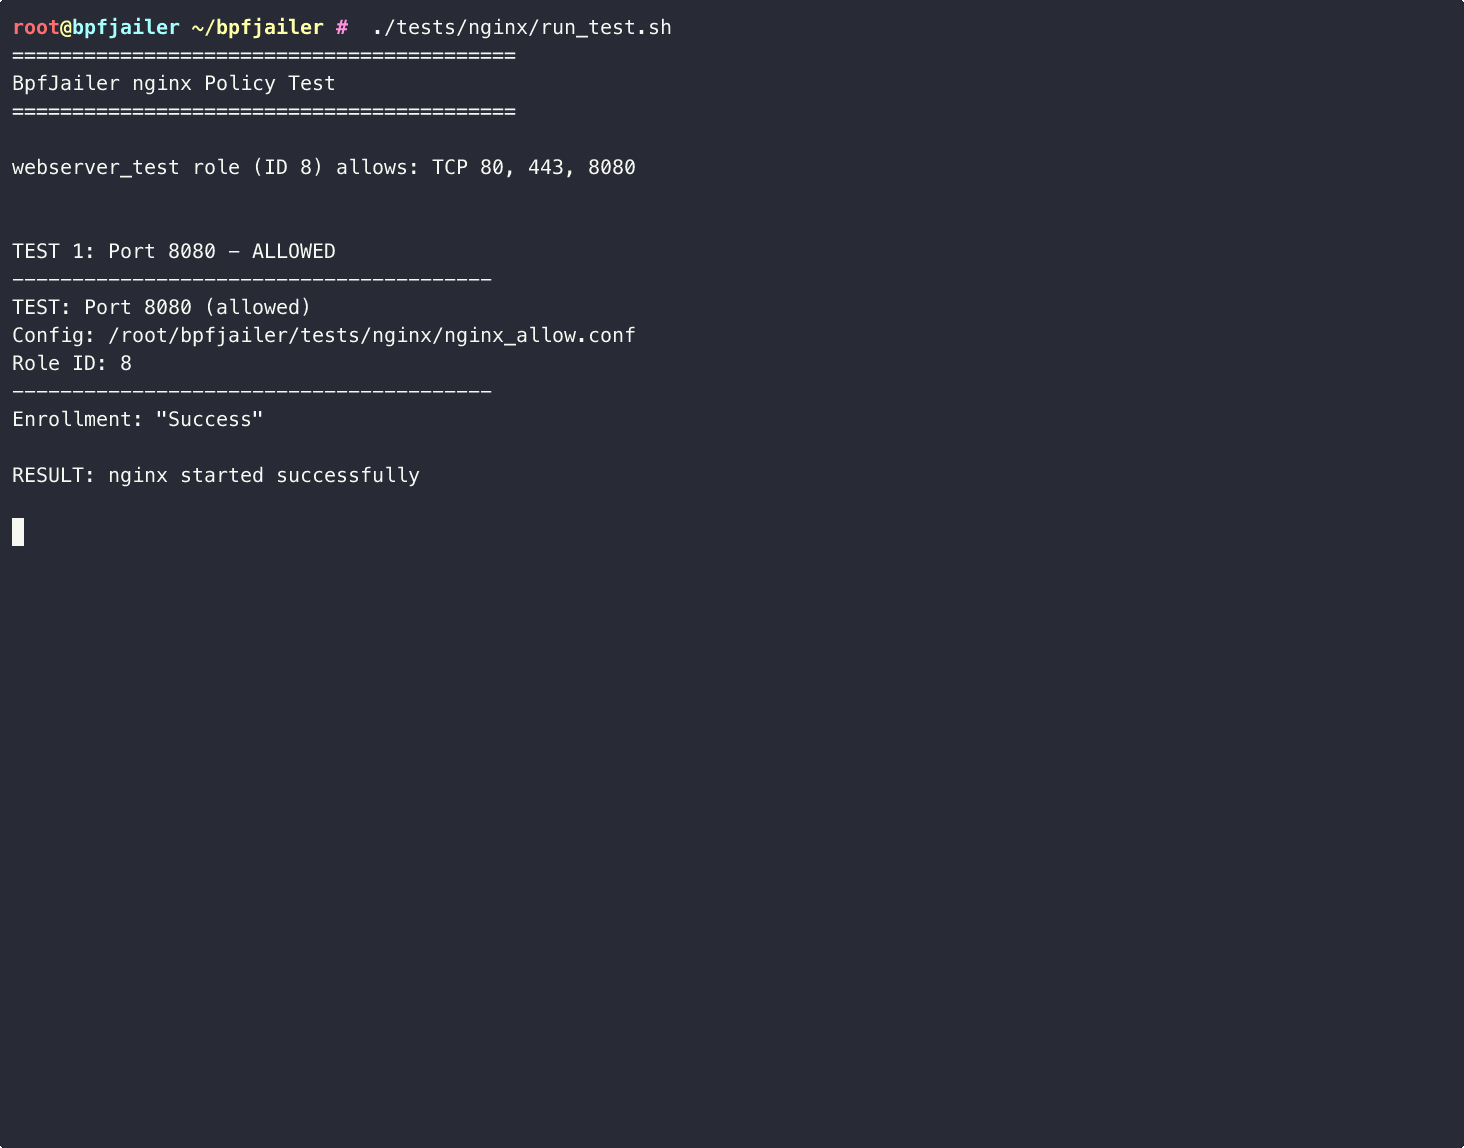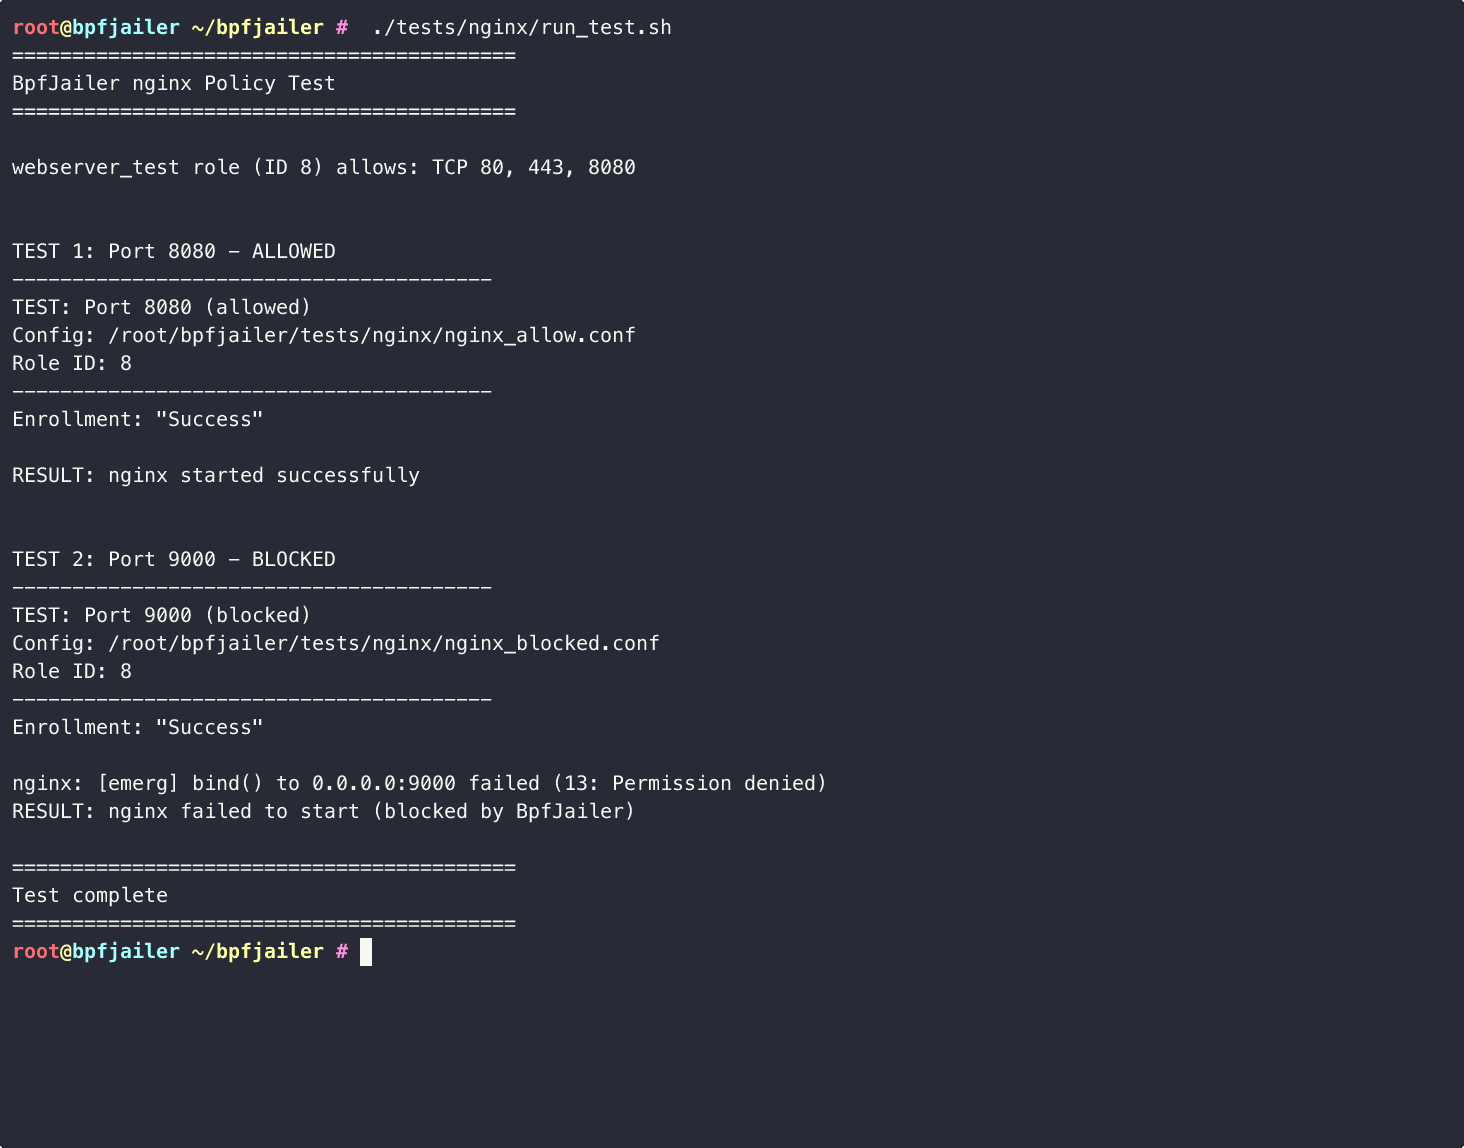
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
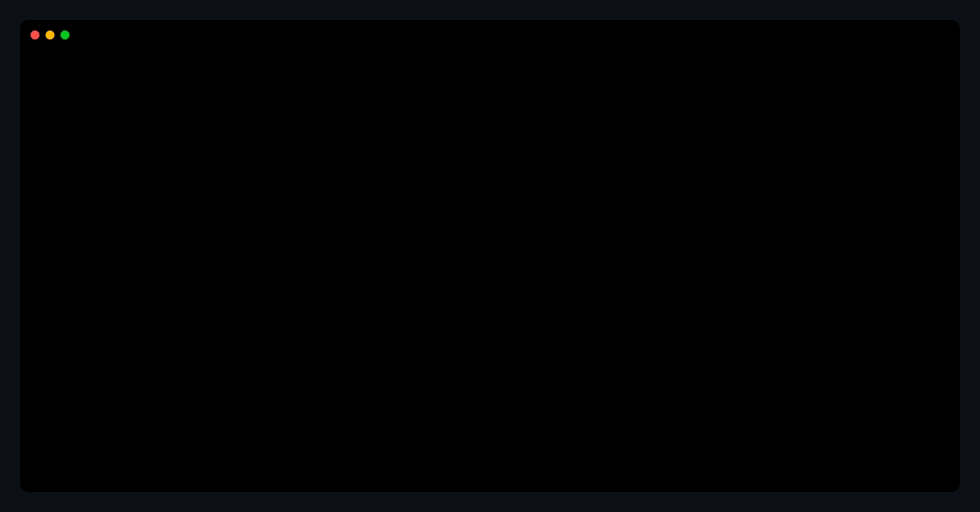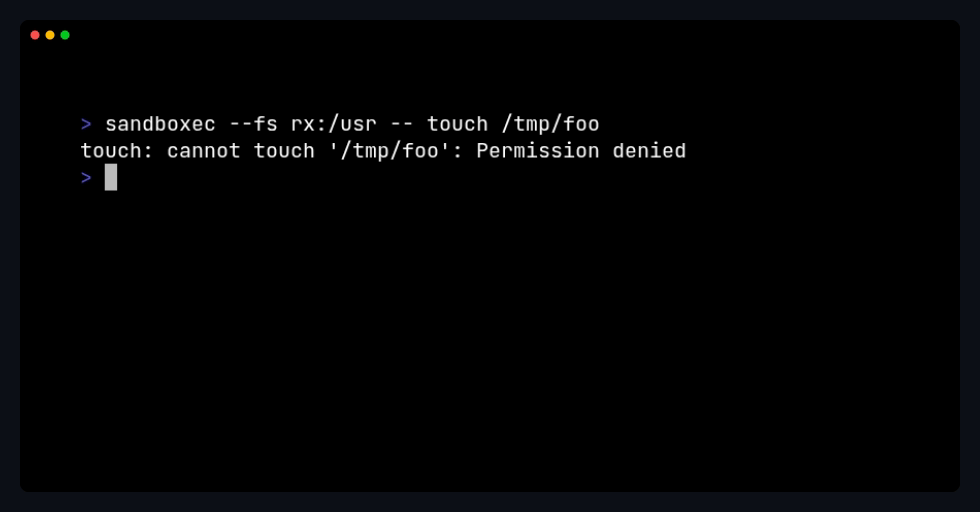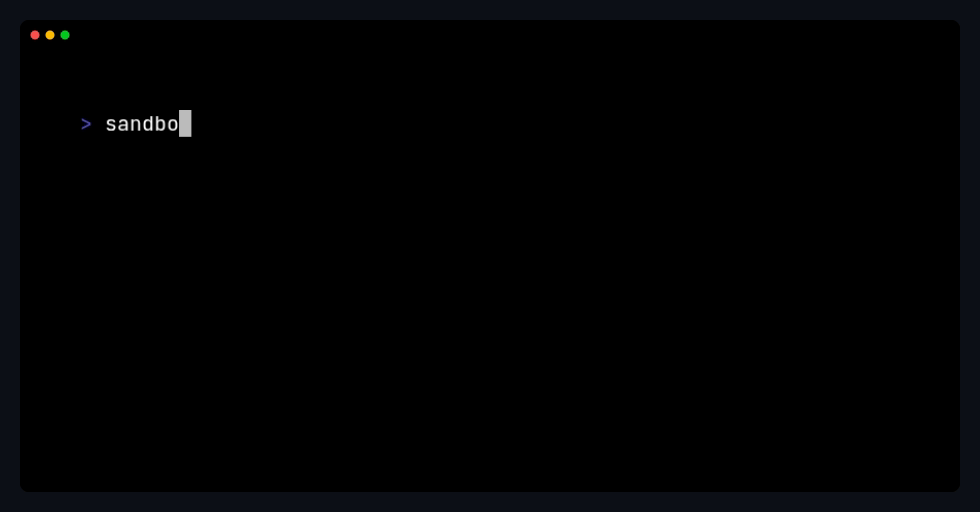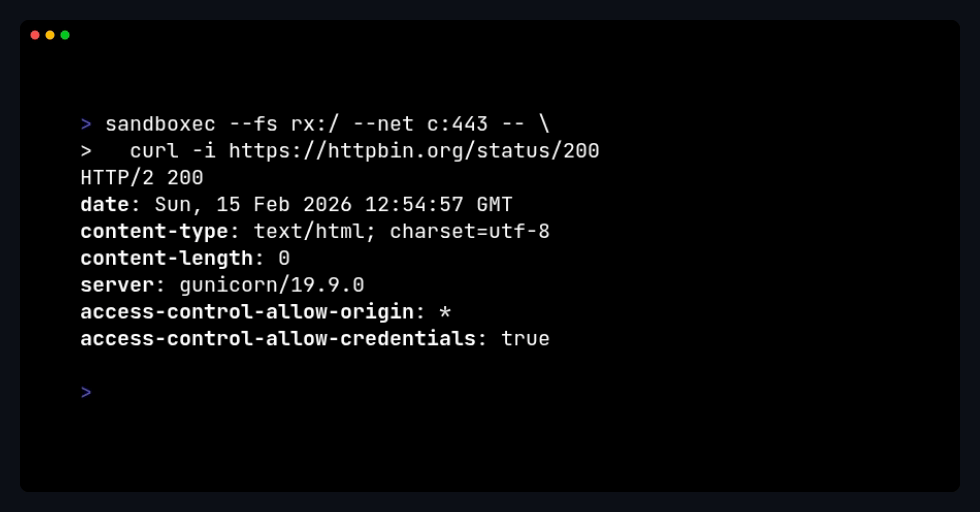 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
 opsxcq/exploit-cve-2016-8016-25
McAfee Virus Scan for Linux multiple remote flaws (CVE 2016-8016, CVE 2016-8017, CVE 2016-8018, CVE 2016-8019, CVE 2016-8020, CVE 2016-8021, CVE…
 beelzebruh/cve-2019-5737
Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.
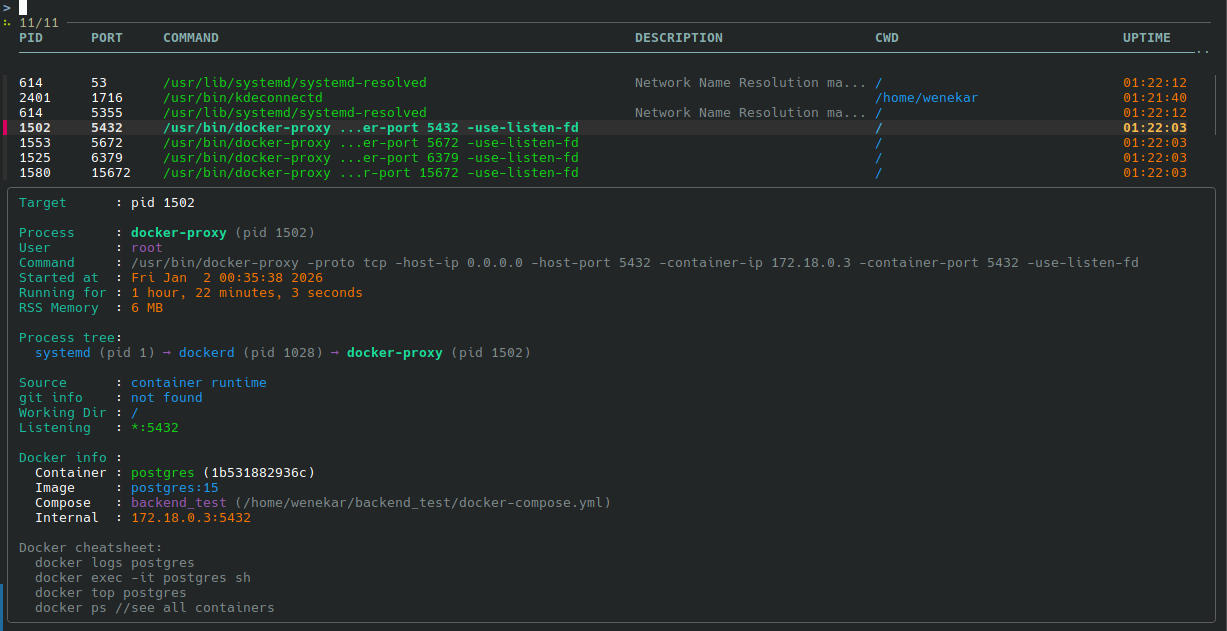 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
 douglasmun/pagecache-lpe-containment-kit
Educational, defensive kit for two Linux page-cache-corruption LPEs (DirtyClone CVE-2026-43503, pedit COW CVE-2026-46331): hardening, detection,…
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
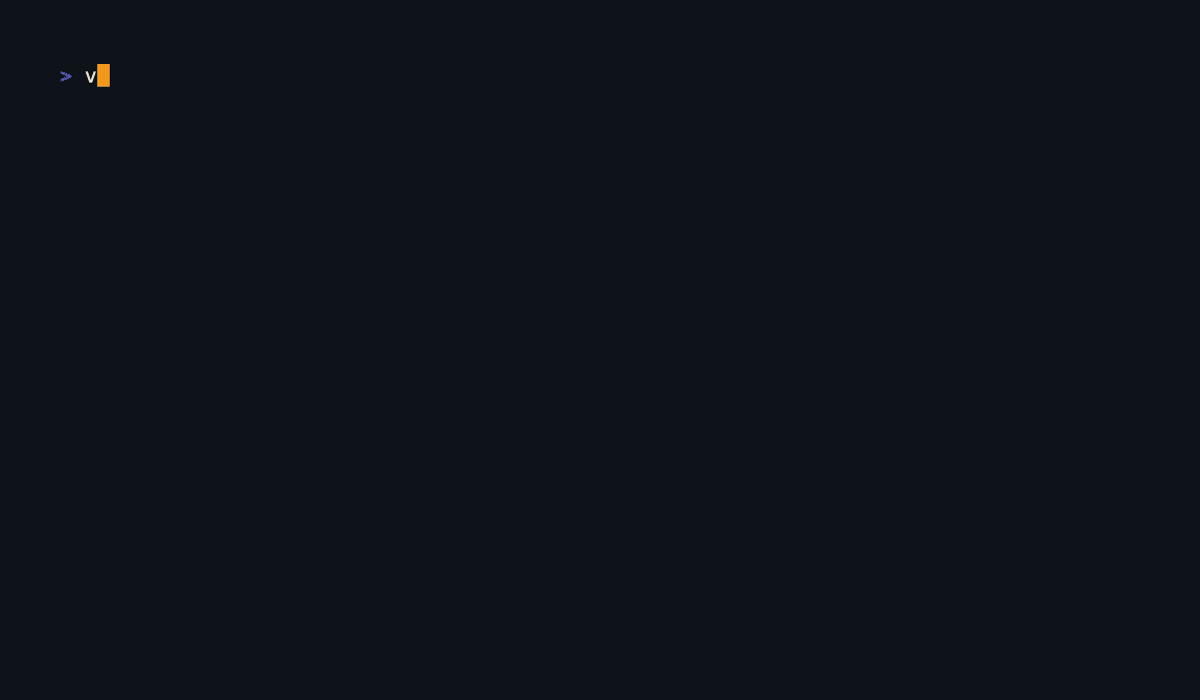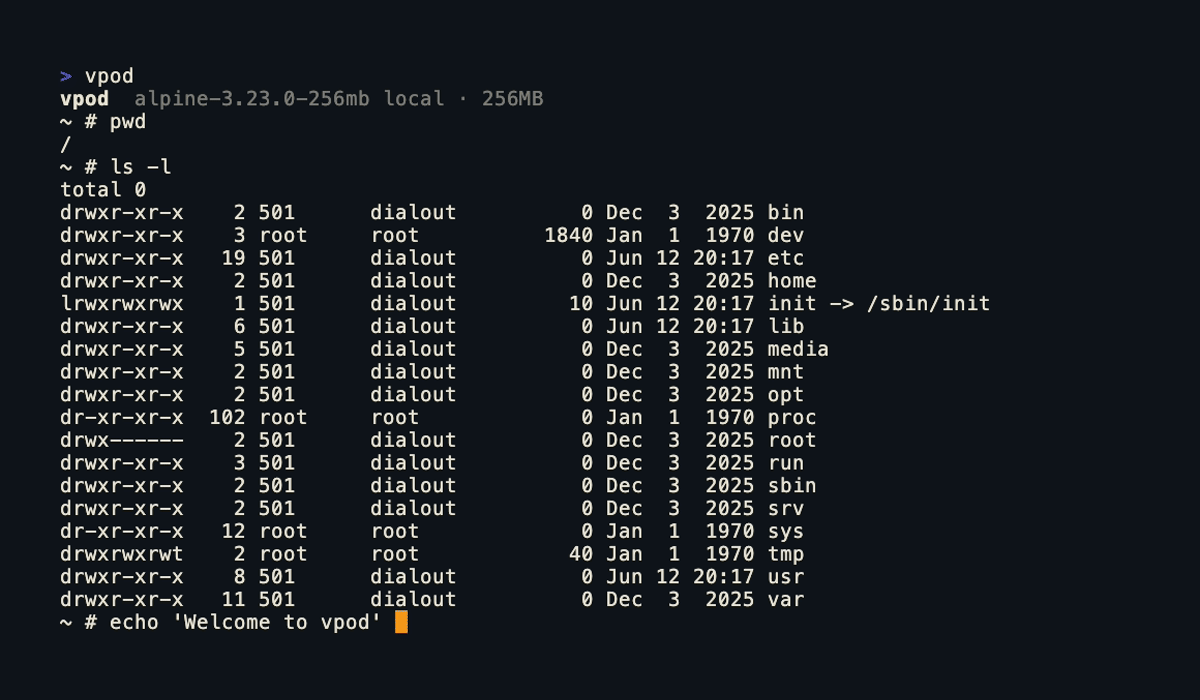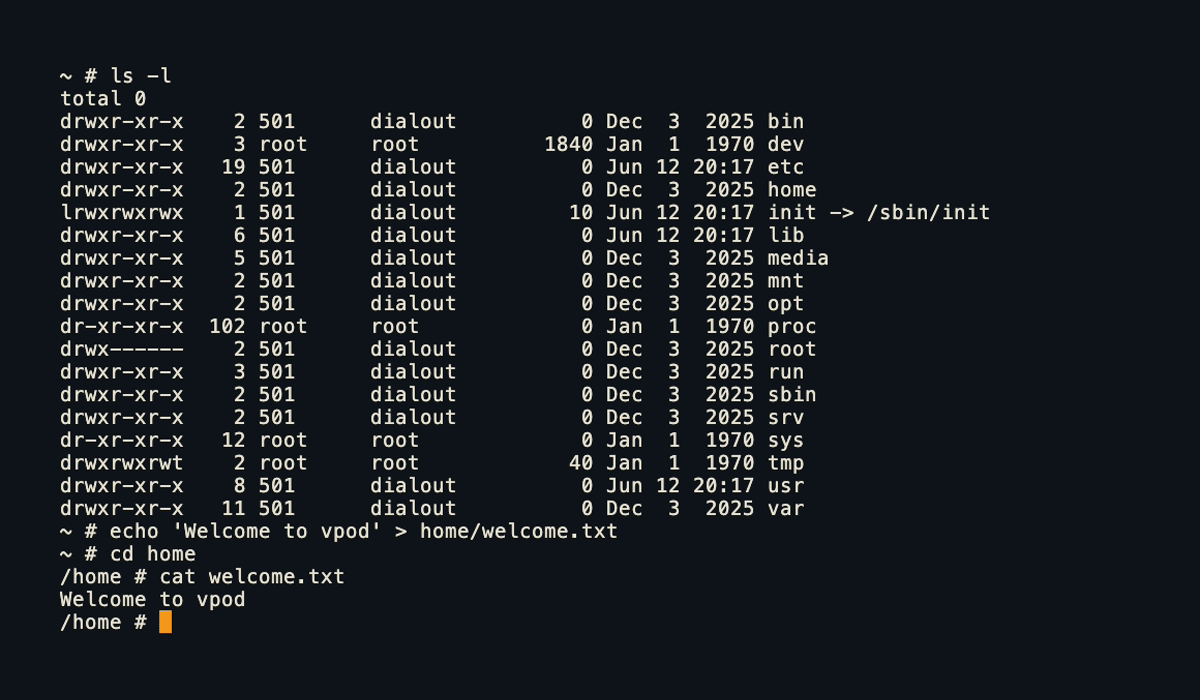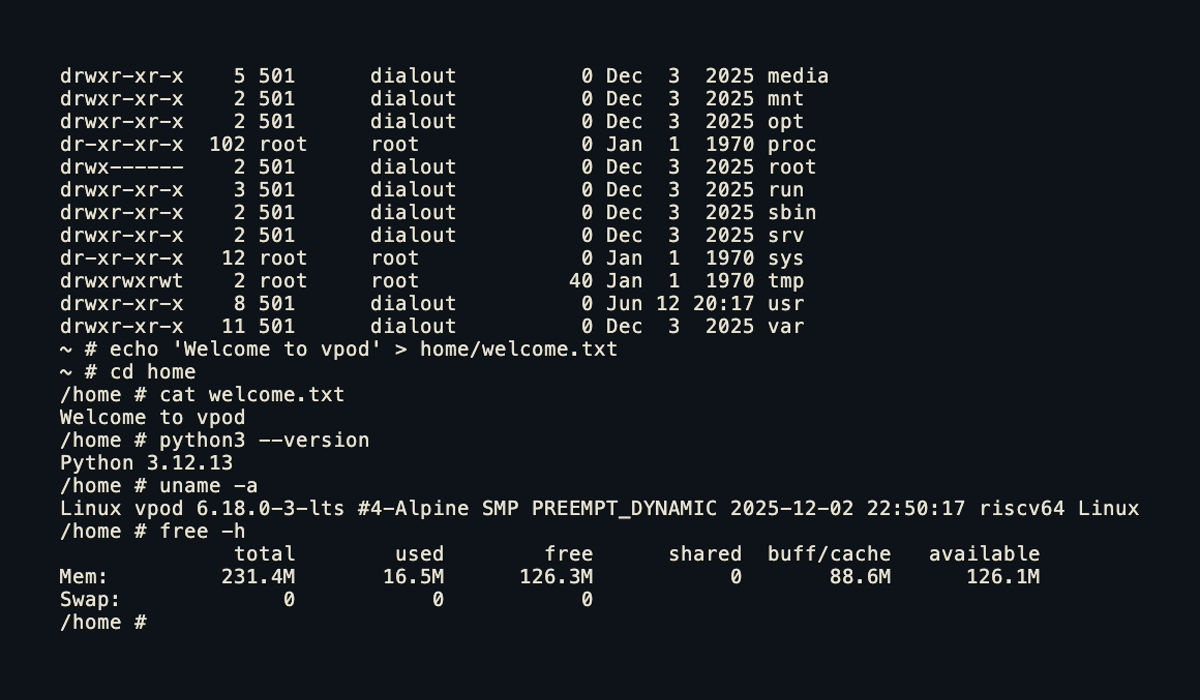 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 cgwalters/container-cve-2021-22555
Containerized reproducer for CVE-2021-22555 Linux privilege escalation, with seccomp mitigation profiles and deployment guidance for Kubernetes and…
 makitos666/cve-2026-31431-copy-fail-detection-toolkit
Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…
 discordianfish/cve-2022-0185-crash-poc
Docker container that runs a crash proof-of-concept for CVE-2022-0185, a Linux kernel vulnerability. Designed for unprivileged execution to test…