kubernetes-log4j-cve-2021-44228-node-agent

Kubernetes DaemonSet that hot-patches JVMs to mitigate Log4j2 vulnerabilities (CVE-2021-44228, CVE-2021-45046) by disabling JNDI lookups, providing…

Kubernetes DaemonSet that hot-patches JVMs to mitigate Log4j2 vulnerabilities (CVE-2021-44228, CVE-2021-45046) by disabling JNDI lookups, providing…

Explain why a Linux TCP port may or may not be reachable

kubeaudit helps you audit your Kubernetes clusters against common security controls

Stage two containers

VirusTotal Wanna Be - Now with 100% more Hipster

kube-scan: Octarine k8s cluster risk assessment tool

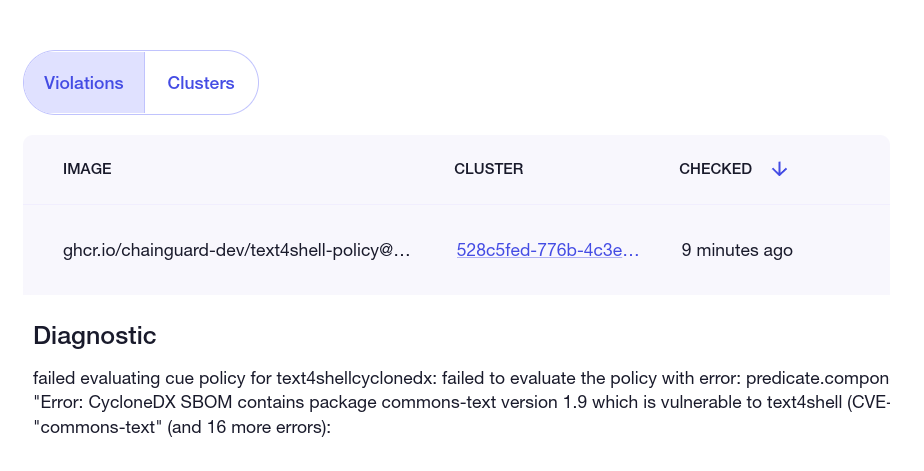
ClusterImagePolicy demo for cve-2022-42889 text4shell

Proof of concept code for breaking out of docker via runC

Simple webhook to block exploitation of CVE-2022-0811

Vulnerable configuration Apache HTTP Server version 2.4.49/2.4.50

Vulnerable configuration Apache HTTP Server version 2.4.49

快速搭建各种漏洞环境(Various vulnerability environment)

Open-source, cross-platform, multi-purpose security auditing tool

⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐

This tool can be used to enumerate the subdomains associated with a company by aggregating the results of multiple OSINT (Open Source Intelligence)…

Vulnerability scanner based on vulners.com audit API

A Dockerized Redash instance that is vulnerable to CVE-2021-21239

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.