
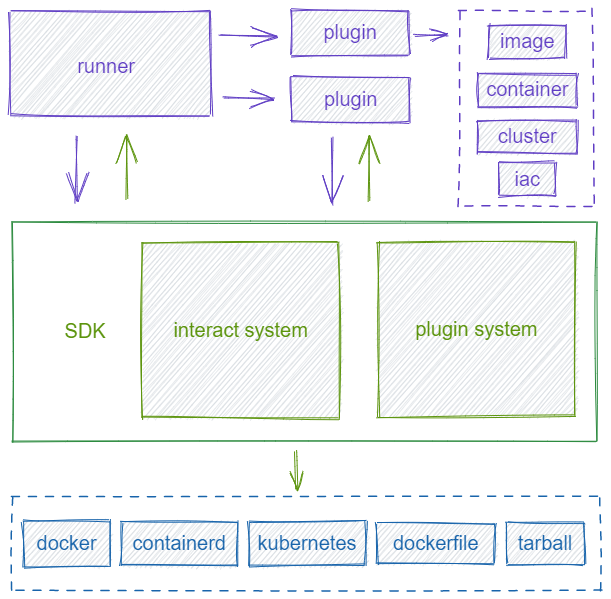
veinmind-tools
 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
cloud-securitycontainer-escapecontainer-security+7
1.7k2 years ago
chaitin/veinmind-toolsveinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626
 paloaltonetworks/can-ctr-escape-cve-2022-0492
Test whether a container environment is vulnerable to container escapes via CVE-2022-0492
 greenhandatsjtu/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 sgkdev/bad_garbage
CVE-2026-53361 AF_UNIX GC vs MSG_PEEK use-after-free container escape
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 nccgroup/abstractshimmer
Proof of concept for CVE-2020-15257 in containerd.
 spiralbl0ck/cve-2023-1206-cve-2025-40040-cve-2024-49882
3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;
 agppp/cve-2019-5736-poc
getshell test