
owLSM
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
cloud-securitycontainer-securitydefensive-tools+4
2807 days ago
cybereason-public/owlsmSigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
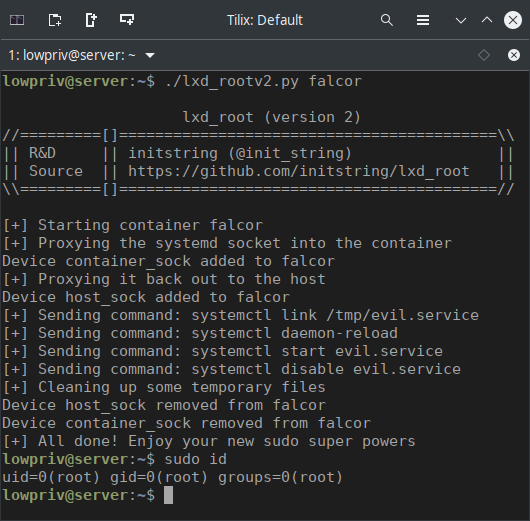 initstring/lxd_root
Linux privilege escalation via LXD
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 thirdbyte/ssj
Your everyday Linux distribution gone Super Saiyan.
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 spiralbl0ck/cve-2023-1206-cve-2025-40040-cve-2024-49882
3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 tangjie1/cve-2026-31431-check
CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script
 axelbankole/cve-2012-1495-webcalendar-
Sets up a Dockerized WebCalendar environment to demonstrate CVE-2012-1495 exploitation using Metasploit on Kali Linux.
 ashardev002/cve-2025-32463_chwoot
🔍 Demonstrate the CVE-2025-32463 privilege-escalation flaw in sudo's chroot feature with this minimal, reproducible proof of concept environment.
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 hmlio/vaas-cve-2014-6271
Vulnerability as a service: showcasing CVS-2014-6271, a.k.a. Shellshock
 hmlio/vaas-cve-2014-0160
Vulnerability as a service: showcasing CVS-2014-0160, a.k.a. Heartbleed