
cve-2013-4660_PoC
 leehunkoo/cve-2013-4660_poc
Proof-of-concept exploit for CVE-2013-4660 demonstrating YAML deserialization remote code execution in a Dockerized Node.js environment with…
cloud-securitycontainer-securityexploitation+3
leehunkoo/cve-2013-4660_pocProof-of-concept exploit for CVE-2013-4660 demonstrating YAML deserialization remote code execution in a Dockerized Node.js environment with…
 davidrxchester/cve-2026-5843
Docker Container Escape POC via mlx-metal importlib
 learner202649/cve-2026-40217-poc
The code for personally reproducing the corresponding vulnerability
 rhpco/cve-2018-16509
CVE-2018-16509 Docker Playground - Ghostscript command execution
 fengjixuchui/cve-2020-11493
Proof-of-concept for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Exploits named pipe impersonation to achieve SYSTEM-level…
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 william31212/cve-requests-1896609
CVE-2025-59376, CVE-2025-59377
 tangjie1/cve-2026-31431-check
CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script
 flojboj/cve-2024-21626
Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.
 kavin71725/cve-2025-12543-fix-for-wildfly
Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…
 selectel/mks-copy-fail-mitigation
DaemonSet с реализацией временной меры для митигации уязвимости Copy Fail (CVE-2026-31431)
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
 mochizuki875/cve-2024-10220-githooks
CVE-2024-10220 Test repo
 srcporter/cve-2021-44228
DO NOT USE FOR ANYTHING REAL. Simple springboot sample app with vulnerability CVE-2021-44228 aka "Log4Shell"
 cashwilliams/cve-2019-14287-demo
This is a container built for demonstration purposes that has a version of the sudo command which is vulnerable to CVE-2019-14287
 ashleyt3/docker-socket-risk-demos
Companion source for YouTube video "Stop Mounting docker.sock — Run Trivy Without Giving Away Root Access — (inspired by CVE-2026-33634)"
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
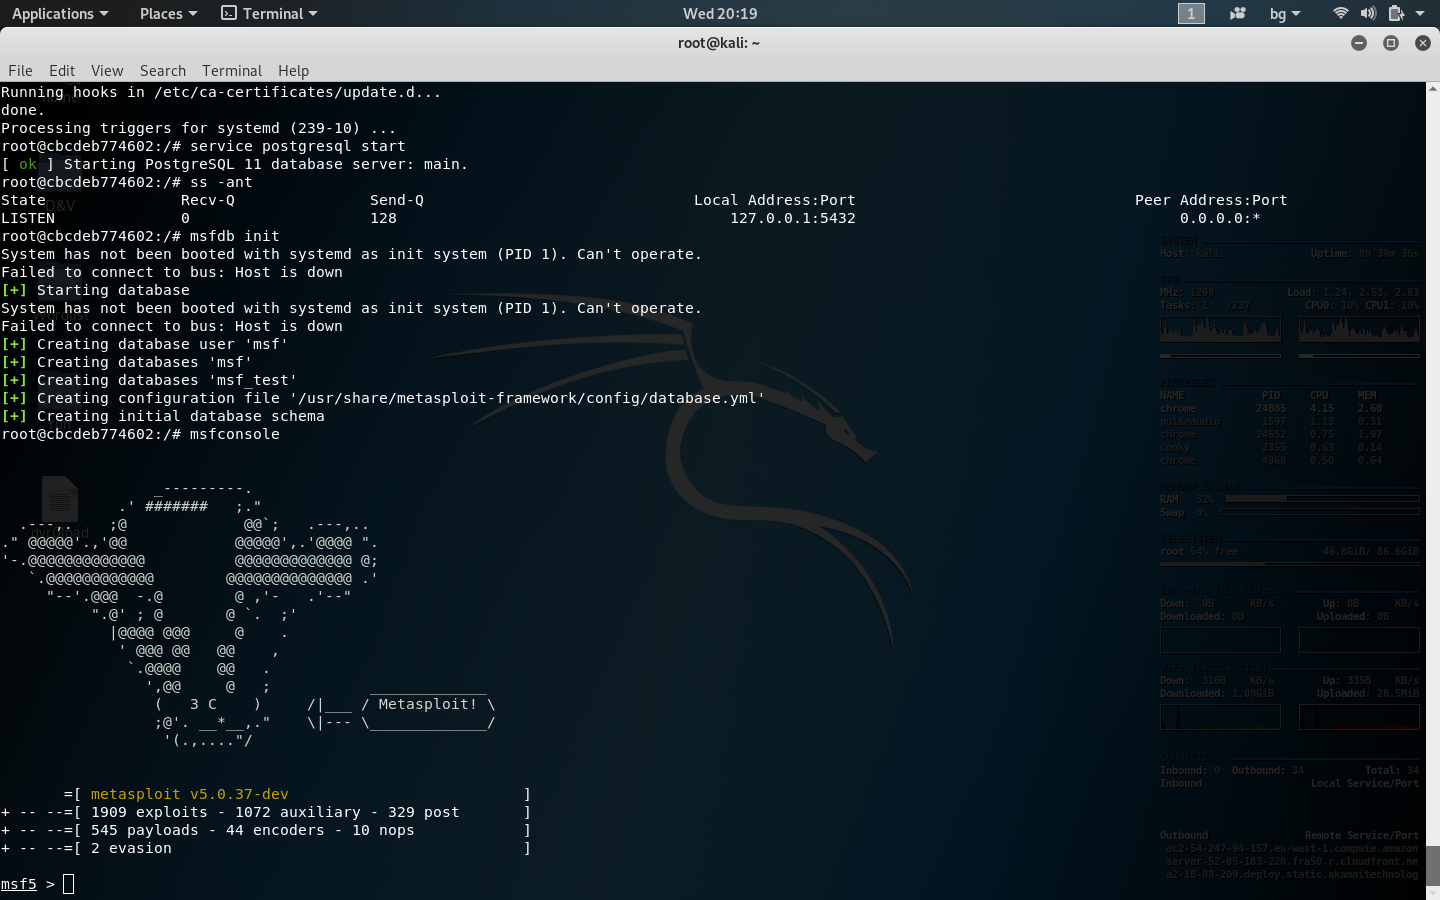 nu11secur1ty/kali-linux-docker
kali-linux-docker