
-INE_Shivam_Gupta_23104003
 shivamg2004/-ine_shivam_gupta_23104003
CVE-2021-43798 Grafana Unauthenticated Path Traversal - Security Lab | Shivam Gupta | 23104003
container-securityeducationexploitation+5
shivamg2004/-ine_shivam_gupta_23104003CVE-2021-43798 Grafana Unauthenticated Path Traversal - Security Lab | Shivam Gupta | 23104003
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 r0binak/cve-2024-0132
CVE-2024-0132 – Fully Weaponized NVIDIA Container Toolkit Exploit
 hi-unc1e/cve-2025-1974-poc
PoC of CVE-2025-1974, modified from the world-first PoC~
 666asd/cve-2024-23653
Proof-of-concept demonstrating CVE-2024-23653, a BuildKit container escape via a malicious Dockerfile frontend, using buildctl to inspect process…
 ycdxsb/log4shell-cve-2021-44228-env
Log4Shell Docker Env
 h3ck13r/cve-2026-35204
Proof-of-concept demonstrating a path traversal vulnerability (CVE-2026-35204) in Helm plugin installation, allowing arbitrary file write via crafted…
 vanigori/cve-2023-38545-sample
Dockerfile containing all the necessary setup files to demo the exploit
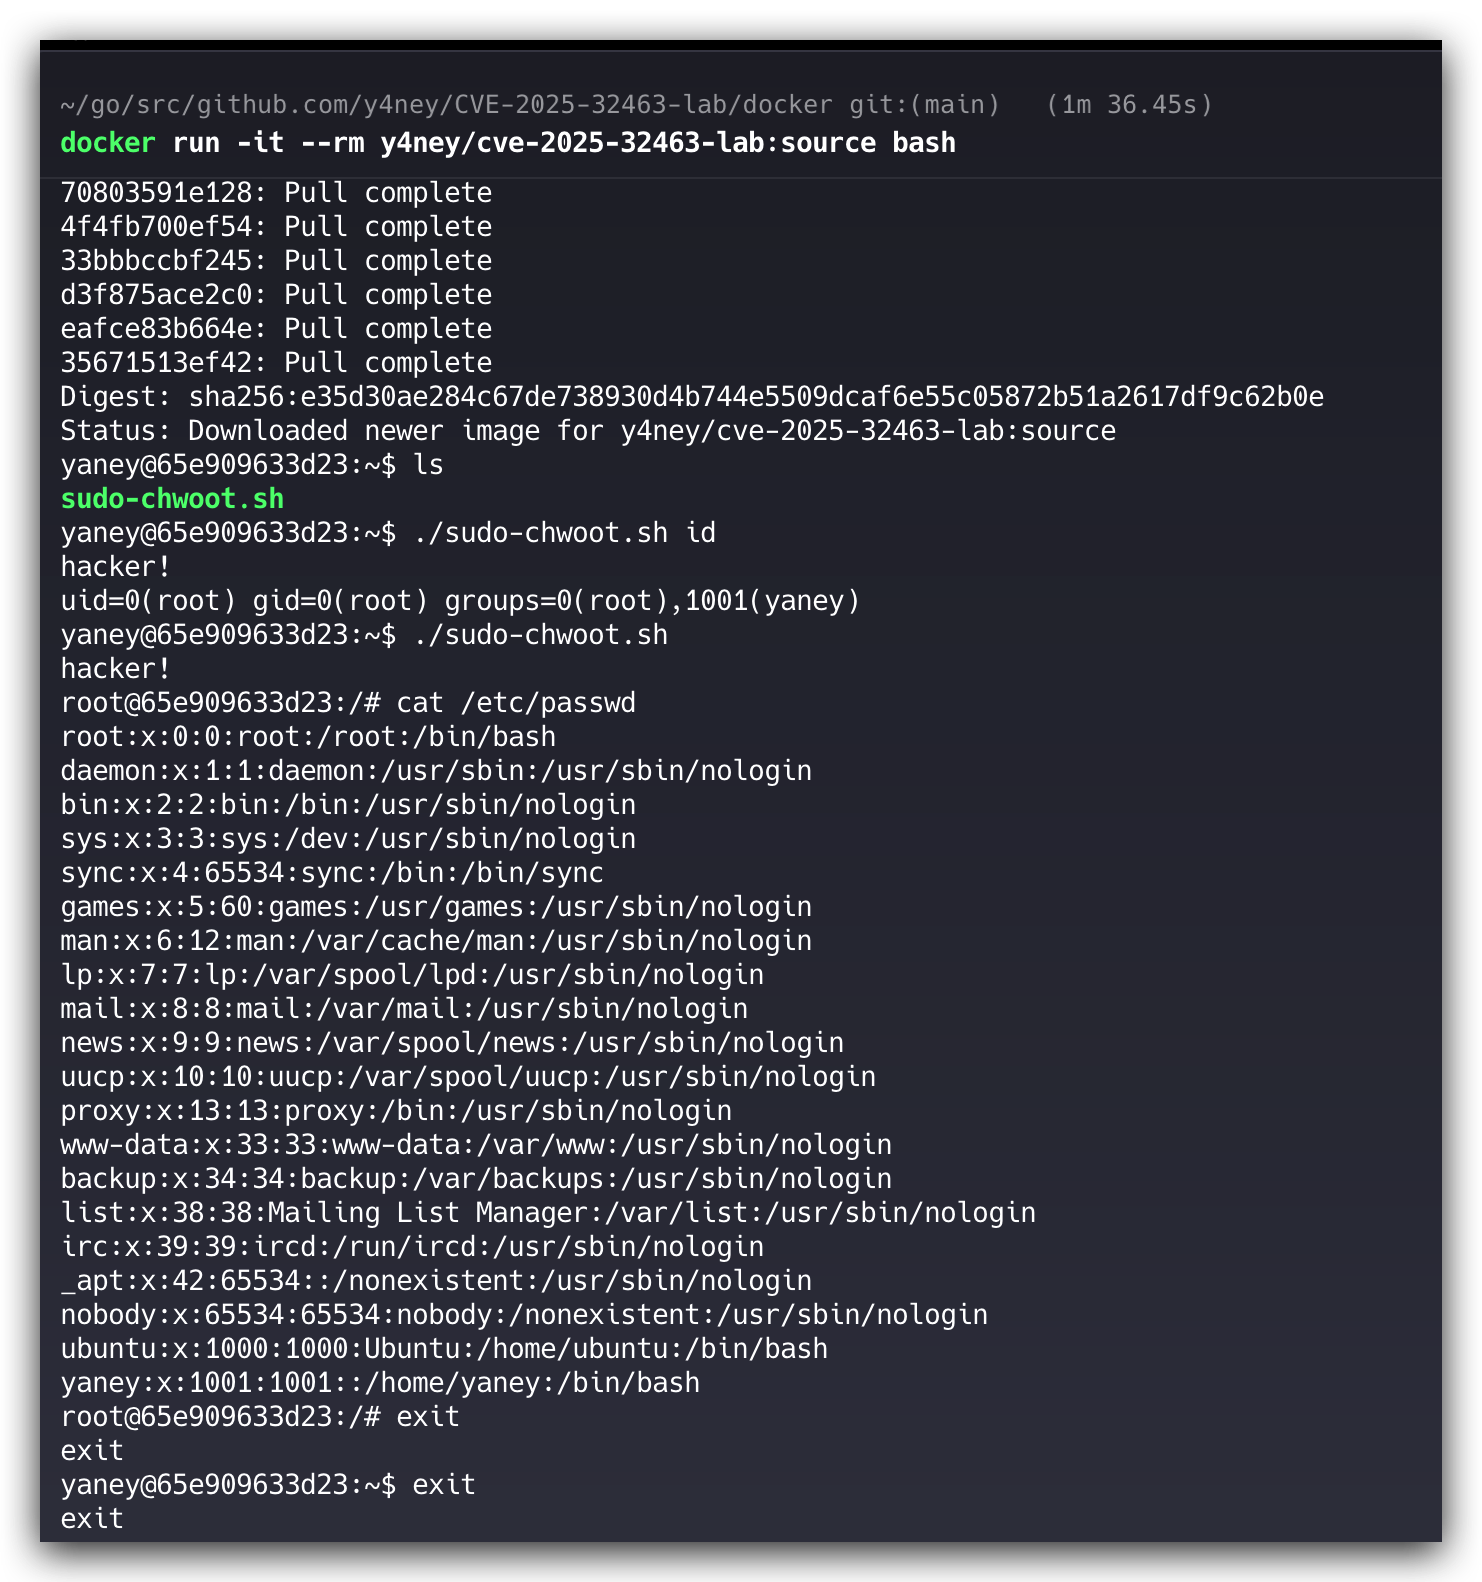 y4ney/cve-2025-32463-lab
本项目基于 Docker 搭建了一个用于复现和测试 sudo 本地权限提升漏洞 CVE-2025-32463 的实验环境。
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 romain-deperne/cve-2026-34940
OS command injection in KubeAI via an Ollama model URL — CVE-2026-34940 / CVSS 8.7
 kianabin/cve-2022-0492-container-escape
CVE-2022-0492-Container-Escape
 berraesen/apache-cve-2021-42013-lab
Docker ortamında Apache HTTP Server 2.4.49 (CVE-2021-42013) zafiyetinin gösterildiği laboratuvar çalışması.
 trackflaw/cve-2023-7028-docker
Repository to install CVE-2023-7028 vulnerable Gitlab instance
 sunnyvale-it/cve-2022-42889-poc
CVE-2022-42889 (a.k.a. Text4Shell) RCE Proof of Concept
 rhysemmas/martian-packets
Crafting raw TCP/IP packets to send to poorly configured Kubernetes servers - CVE-2020-8558 PoC
 toowoxx/docker-confluence-patched
Patched Confluence 7.12.2 (CVE-2021-26084)
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…