
CVE-2025-1974-poc
 hi-unc1e/cve-2025-1974-poc
PoC of CVE-2025-1974, modified from the world-first PoC~
cloud-securitycontainer-securityexploitation+3
4
hi-unc1e/cve-2025-1974-pocPoC of CVE-2025-1974, modified from the world-first PoC~
 knqyf263/cve-2018-16509
Dockerized proof-of-concept exploit for Ghostscript -dSAFER sandbox bypass vulnerability (CVE-2018-16509), enabling remote code execution via…
 666asd/cve-2024-23653
Proof-of-concept demonstrating CVE-2024-23653, a BuildKit container escape via a malicious Dockerfile frontend, using buildctl to inspect process…
 neuralinhibitor/xzwhy
XZ Utils CVE-2024-3094 POC for Kubernetes
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 boreas37/cve-2026-58455-poc
PoC for CVE-2026-58455: Dockwatch <=0.6.567 unauthenticated RCE. Stdlib-only Python.
 chanbakjsd/cve-2019-18634
Reproduction of CVE-2019-18634, a sudo privilege escalation exploit via buffer overflow in pwfeedback. Includes Docker-based environment for…
 ycdxsb/log4shell-cve-2021-44228-env
Log4Shell Docker Env
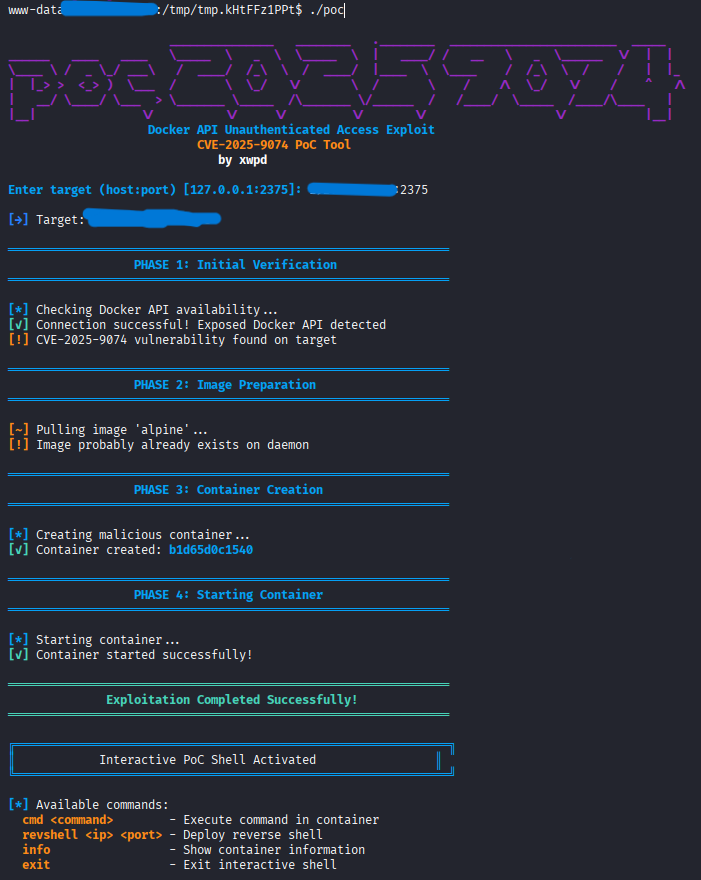 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 karthikuj/cve-2023-23752-docker
Dockerized proof-of-concept for Joomla unauthorized access vulnerability (CVE-2023-23752) enabling database credential extraction via API endpoint.
 mauroeldritch/vancleef
Exploit for CVE-2019-11881 (Rancher 2.1.4 Web Parameter Tampering)
 vanigori/cve-2023-38545-sample
Dockerfile containing all the necessary setup files to demo the exploit
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…
 y4ney/cve-2025-32463-lab
本项目基于 Docker 搭建了一个用于复现和测试 sudo 本地权限提升漏洞 CVE-2025-32463 的实验环境。
 thegebirge/cve-2025-32375
This repository includes everything needed to run a PoC exploit for CVE-2025-32375 in a Docker environment. It runs the latest vulnerable version of…
 kianabin/cve-2022-0492-container-escape
CVE-2022-0492-Container-Escape
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
 saku0512/cve-2026-54761-poc
Proof-of-concept demonstrating an authorization bypass in Traefik's Kubernetes Gateway provider (CVE-2026-54761) via a crossProviderNamespaces…