
 bishopfox/badpods
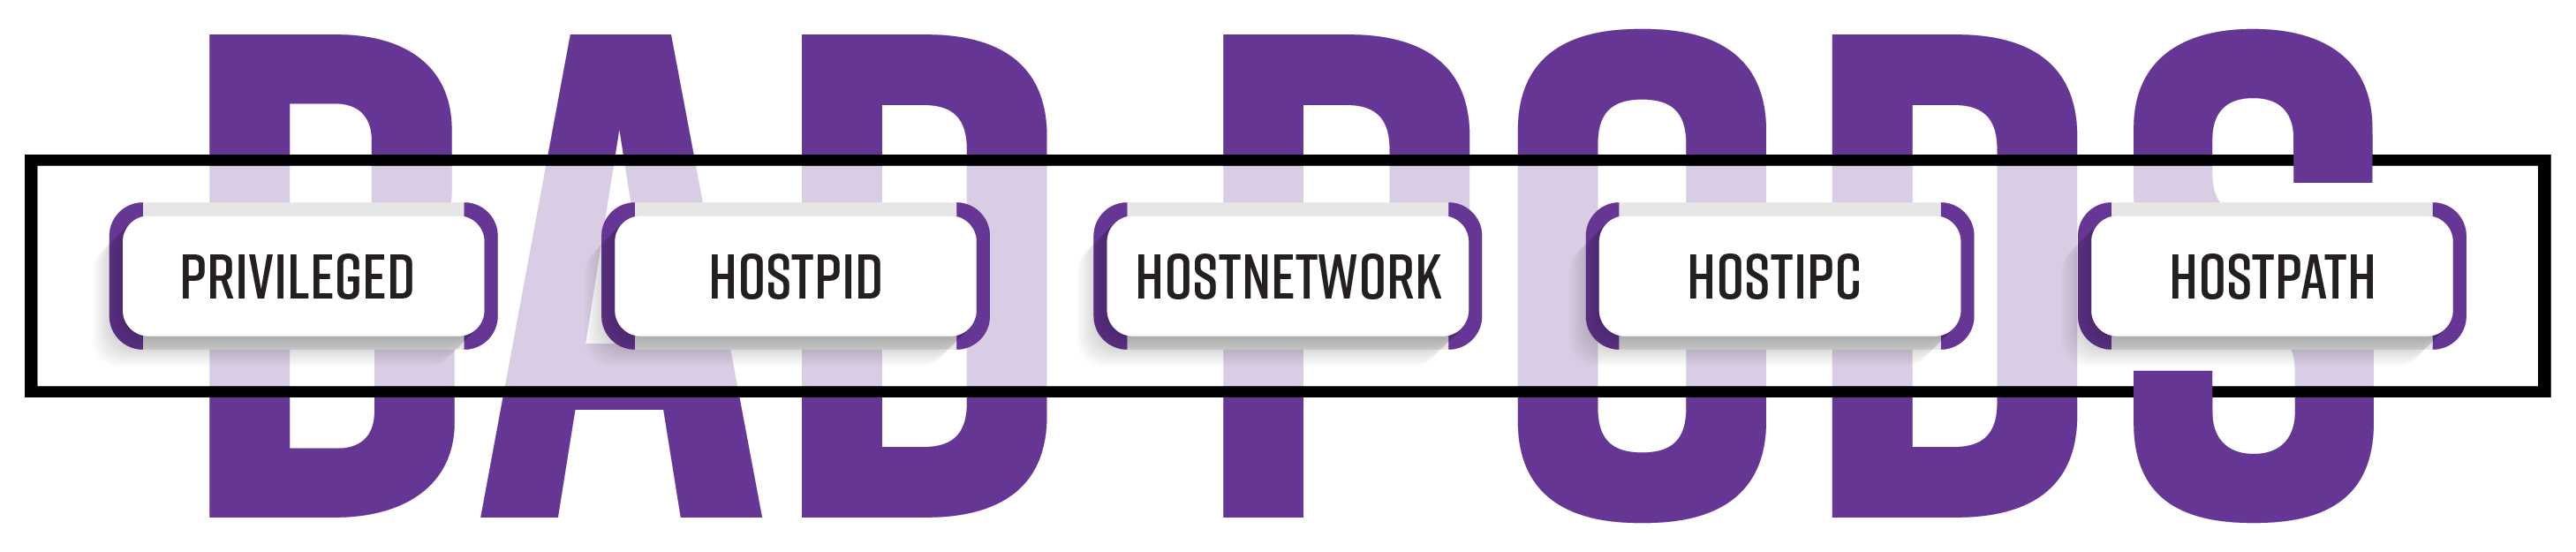
A collection of manifests that will create pods with elevated privileges.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment
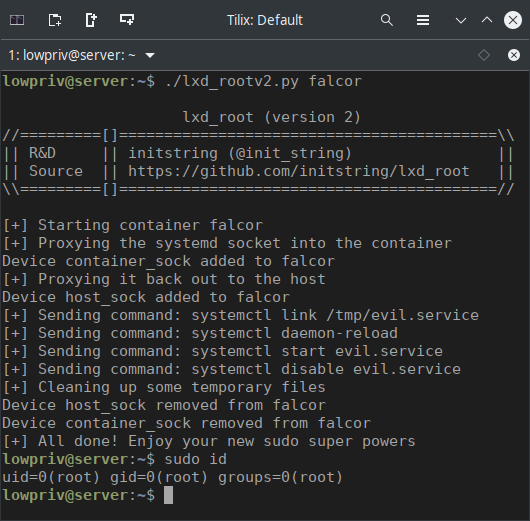 initstring/lxd_root
Linux privilege escalation via LXD
 cookiengineer/actual-php2shell
:robot: NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 sensepost/dwn
d(ockerp)wn - a docker pwn tool manager
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 nccgroup/wubes
Qubes containerization on Windows
 pwnfunction/sandbox
Run untrusted AI code safely, fast
 sandumjacob/ingressnightmare-pocs
CVE-2025-1974
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback