

CVE-2022-46463
 404tk/cve-2022-46463
harbor unauthorized detection
cloud-securitycontainer-securityexploitation+3
59
404tk/cve-2022-46463harbor unauthorized detection
 greenhandatsjtu/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
 knqyf263/cve-2020-10749
Proof-of-concept exploit for CVE-2020-10749 demonstrating Kubernetes MitM attacks via IPv6 rogue router advertisements between pods.
 tangxiaofeng7/cve-2022-22965-spring-core-rce
批量无损检测CVE-2022-22965
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 sgkdev/bad_garbage
CVE-2026-53361 AF_UNIX GC vs MSG_PEEK use-after-free container escape
 raesene/cve-2022-23648-poc
POC for CVE-2022-23648
 projectdiscovery/pd-agent
ProjectDiscovery Cloud - Agent
 aquasecurity/trivy-repo
deb/rpm repository for Trivy
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 airbus-cert/dirtypipe-ebpf_detection
An eBPF detection program for CVE-2022-0847
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
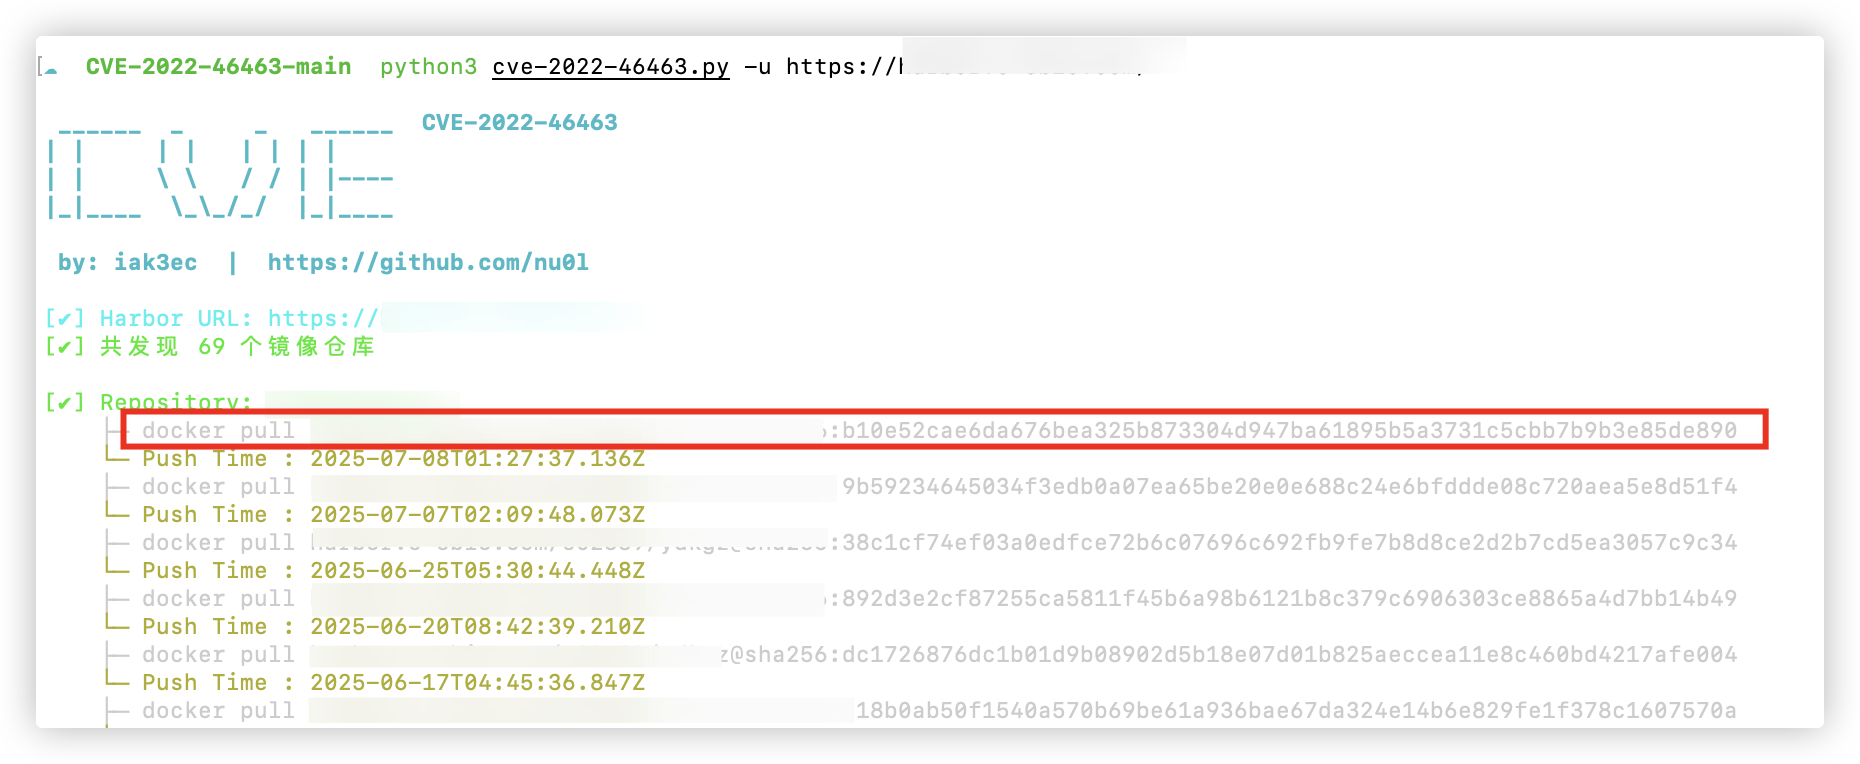 nu0l/cve-2022-46463
CVE-2022-46463(Harbor 未授权)
 infobyte/distro_checker
Cross Distribution Exploit Testing
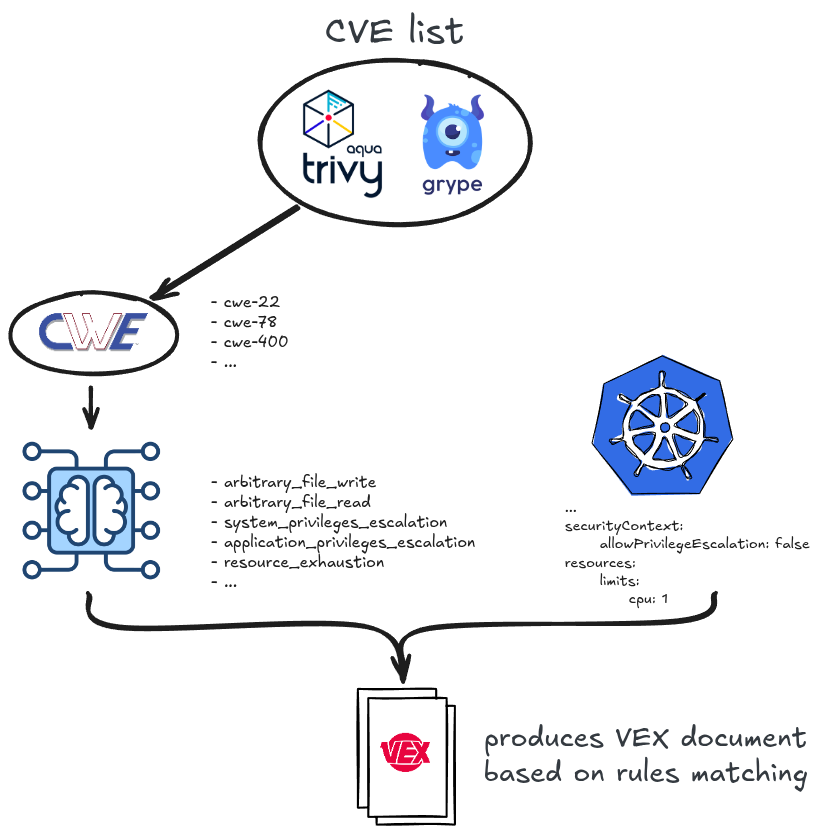 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
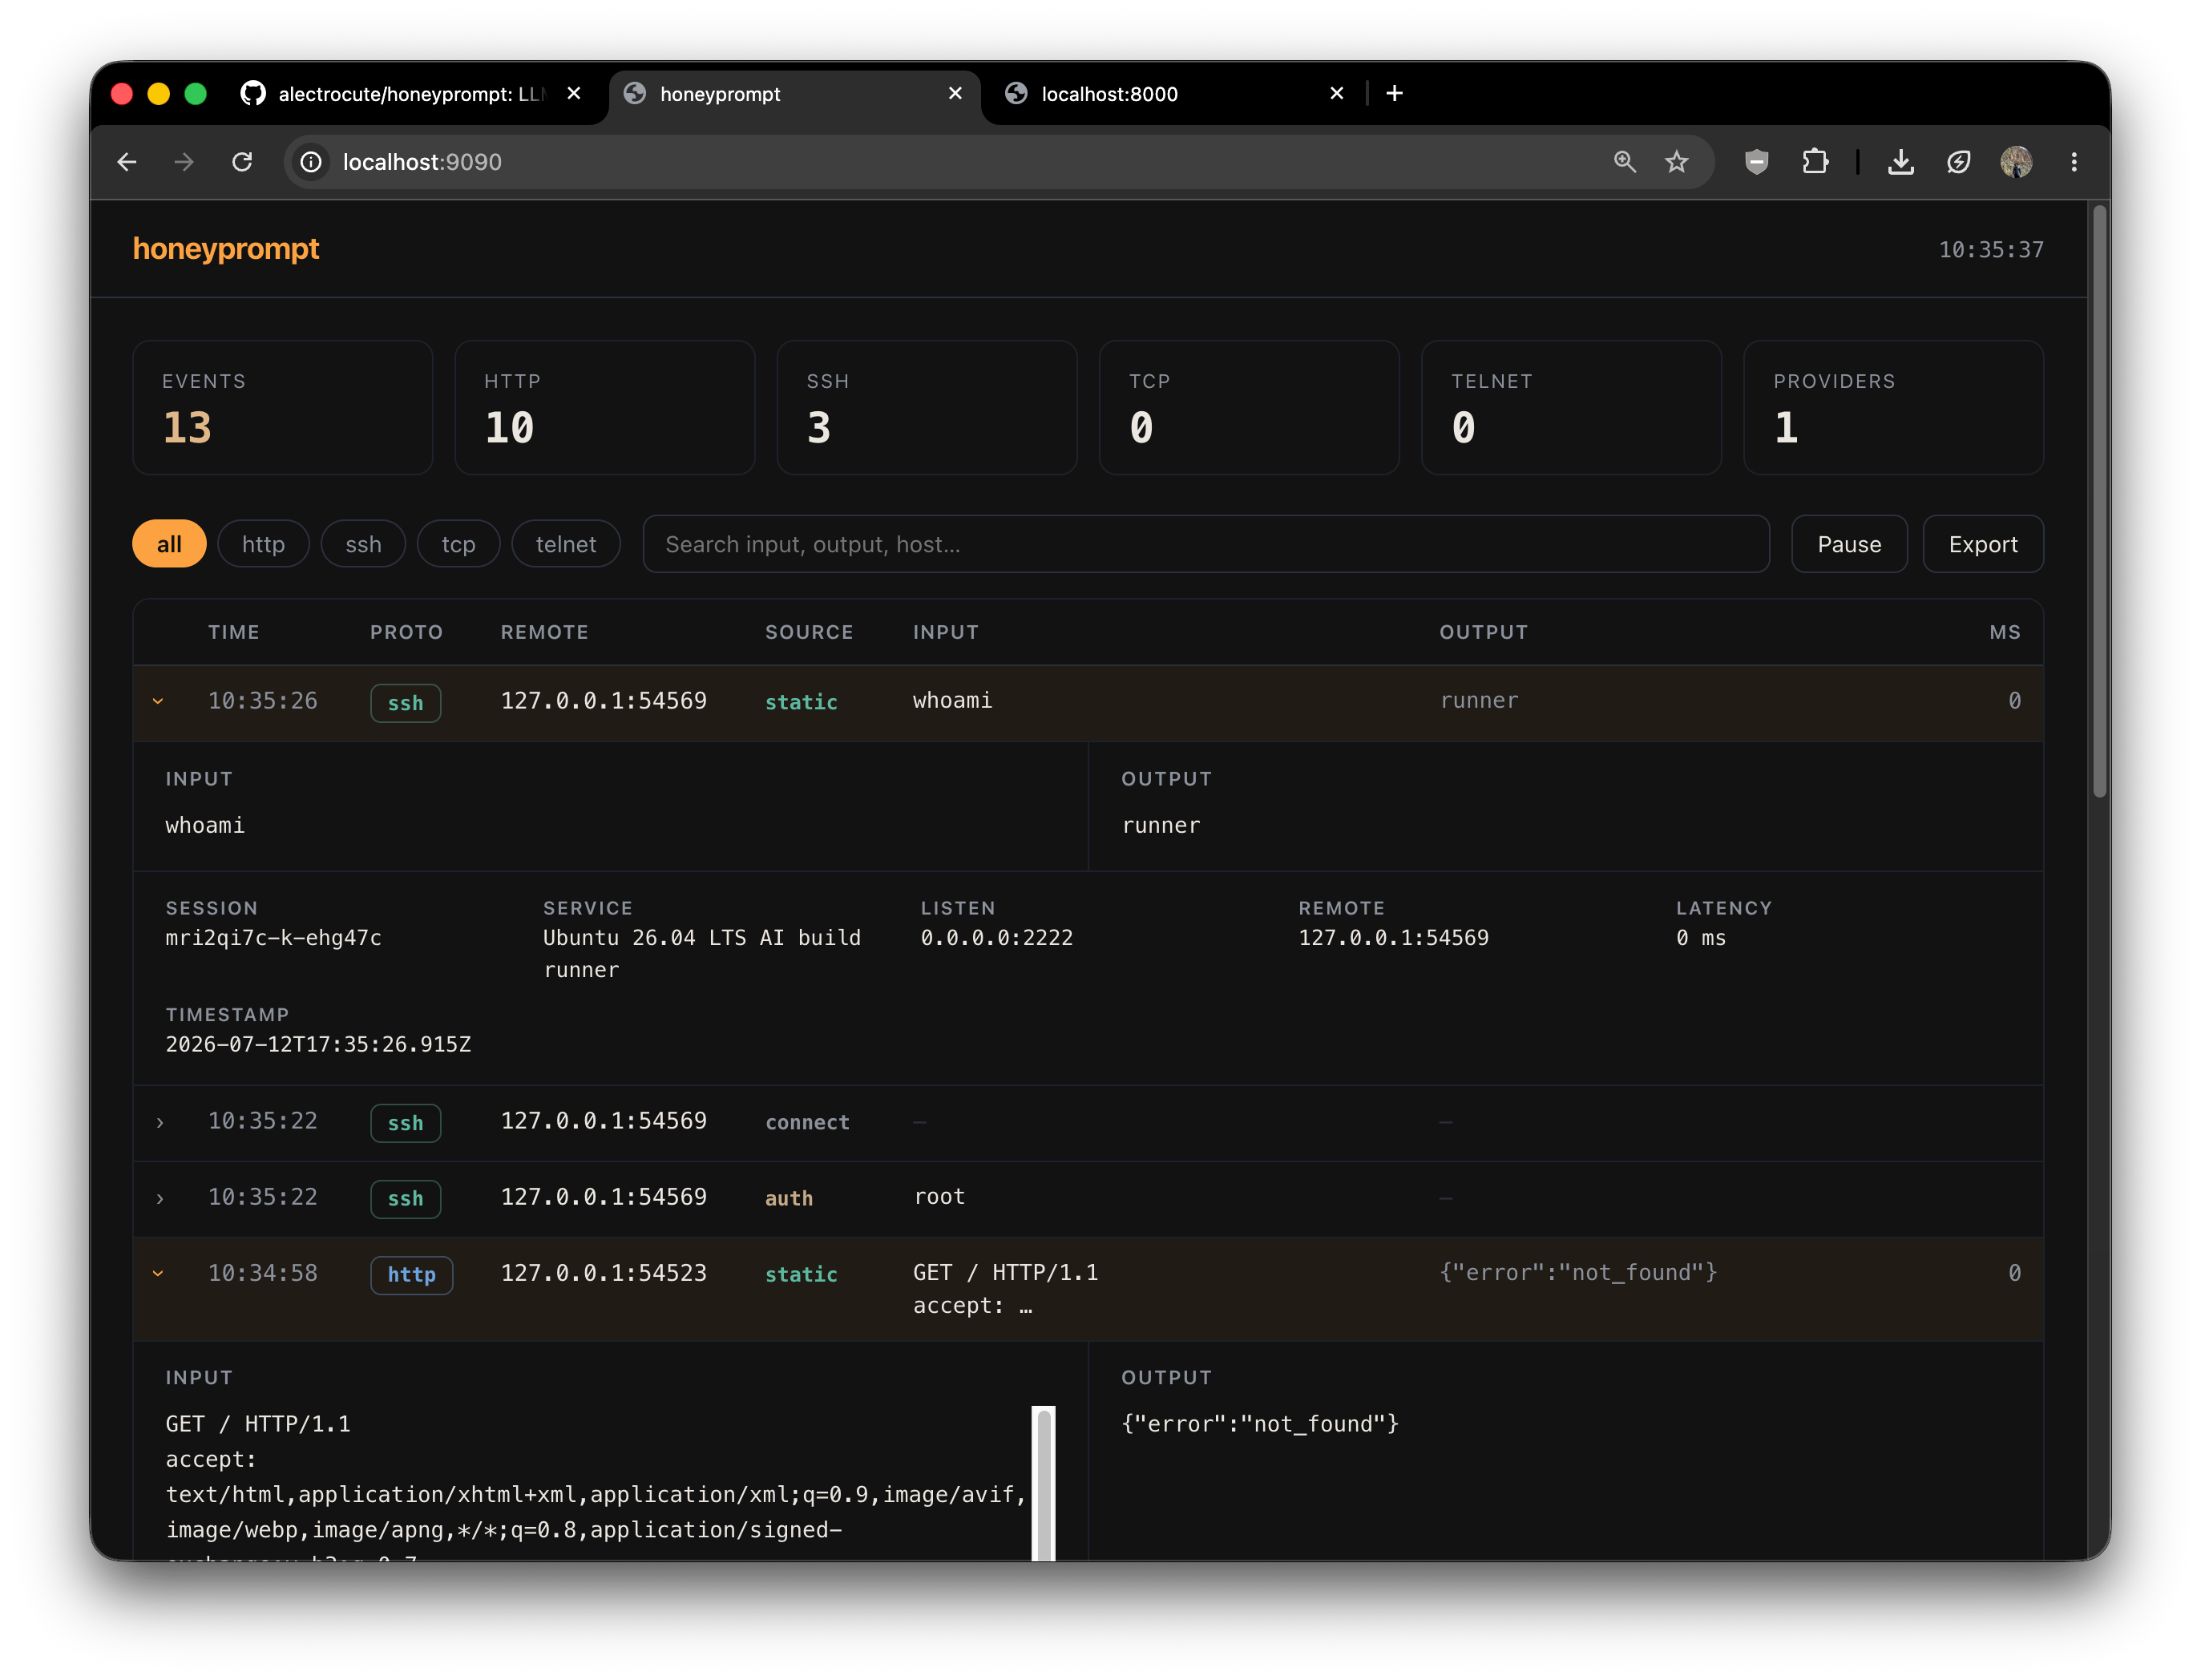 alectrocute/honeyprompt
LLM-first deception framework: "The honeypot that talks back!™"