
agent
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
cloud-securityconfiguration-auditingcontainer-security+2
bomfather/agenteBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
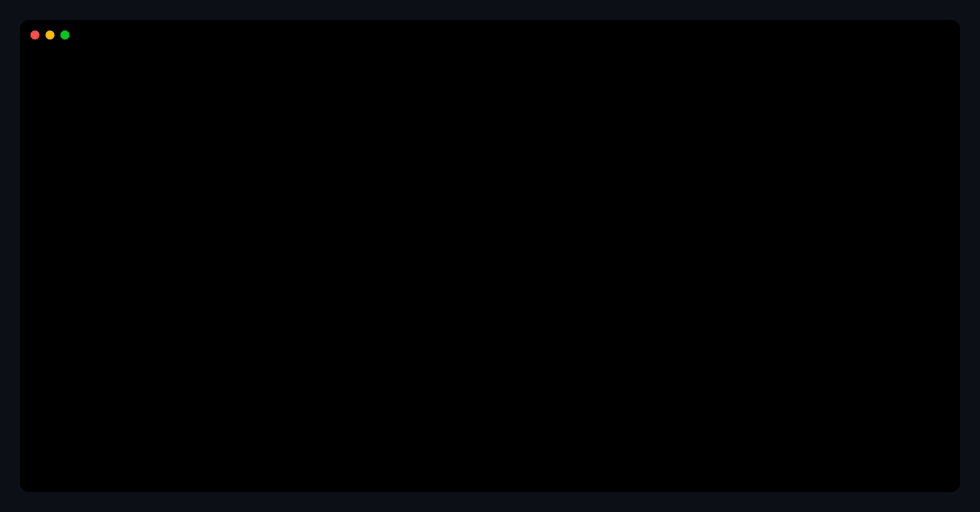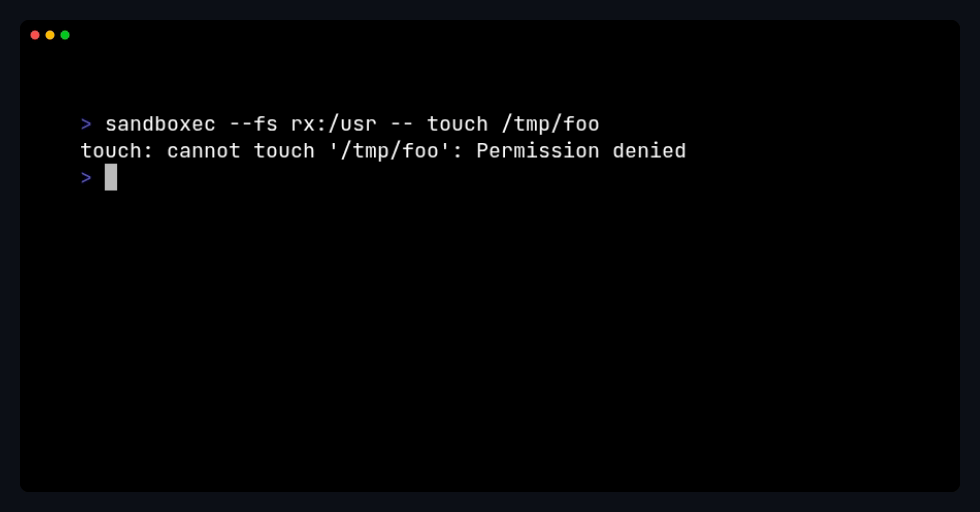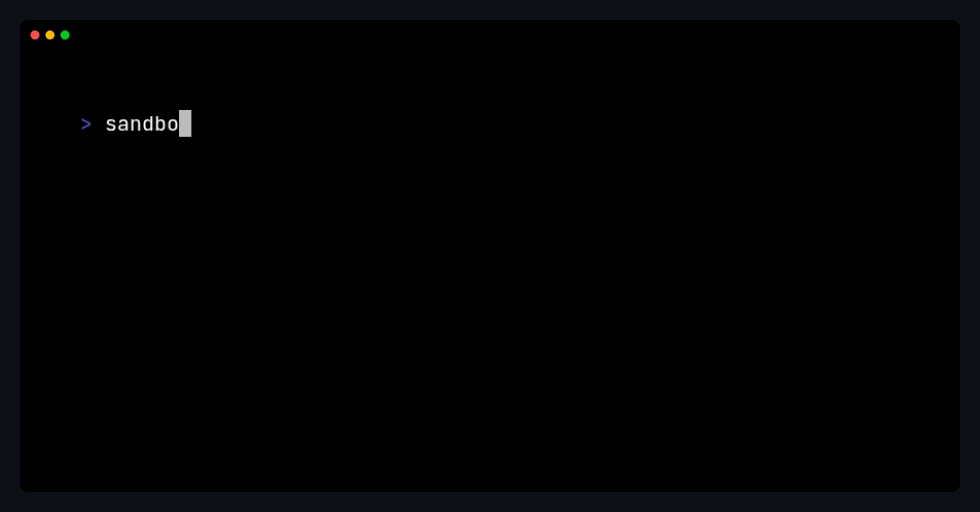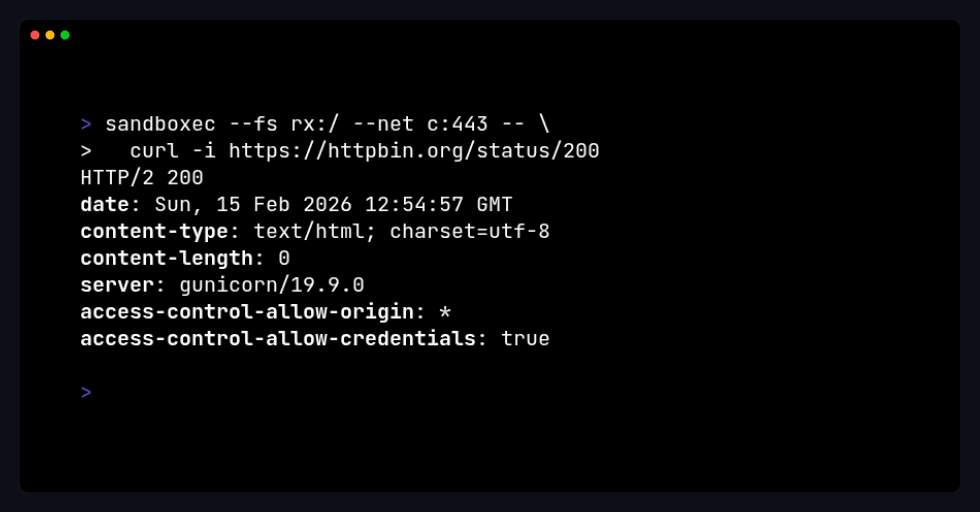 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 spiralbl0ck/cve-2023-1206-cve-2025-40040-cve-2024-49882
3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 opsxcq/exploit-cve-2016-8016-25
McAfee Virus Scan for Linux multiple remote flaws (CVE 2016-8016, CVE 2016-8017, CVE 2016-8018, CVE 2016-8019, CVE 2016-8020, CVE 2016-8021, CVE…
 cgwalters/container-cve-2021-22555
Containerized reproducer for CVE-2021-22555 Linux privilege escalation, with seccomp mitigation profiles and deployment guidance for Kubernetes and…
 discordianfish/cve-2022-0185-crash-poc
Docker container that runs a crash proof-of-concept for CVE-2022-0185, a Linux kernel vulnerability. Designed for unprivileged execution to test…
 ashardev002/cve-2025-32463_chwoot
🔍 Demonstrate the CVE-2025-32463 privilege-escalation flaw in sudo's chroot feature with this minimal, reproducible proof of concept environment.
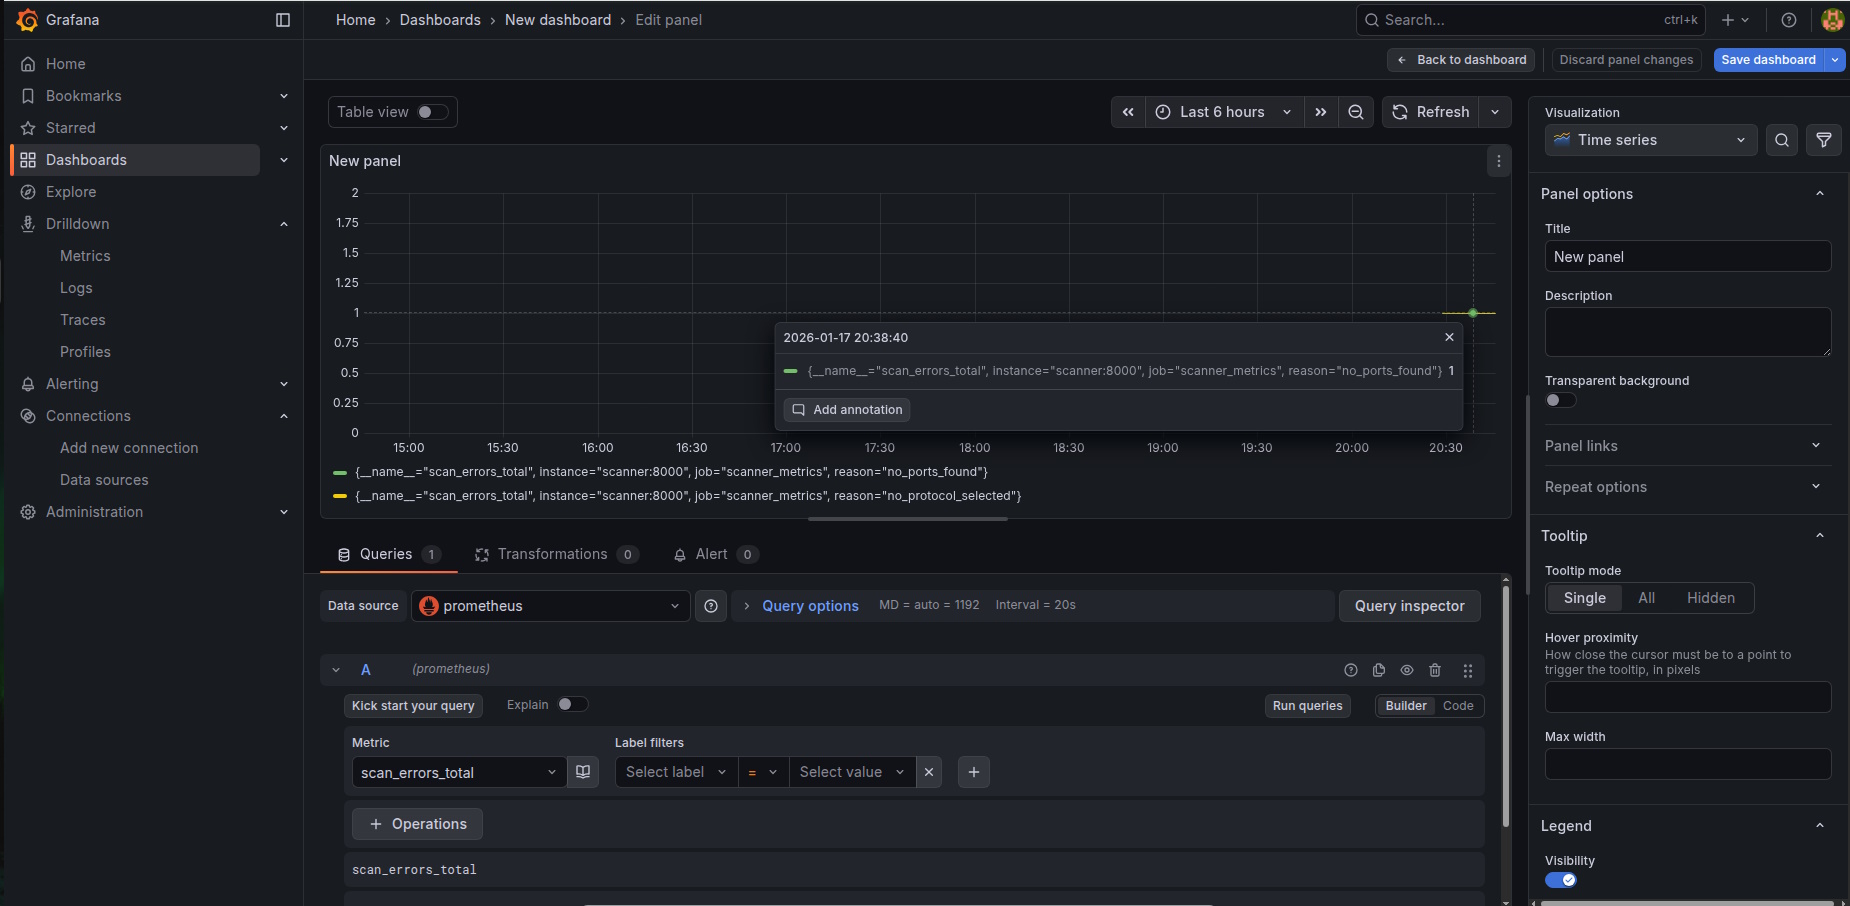 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…