
flatpak
 flatpak/flatpak
Linux application sandboxing and distribution framework
container-securitysecurity-virtualization
flatpak/flatpakLinux application sandboxing and distribution framework
 lockc-project/lockc
Making containers more secure with eBPF and Linux Security Modules (LSM)
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 lglznl/klaios
KLAIOS is a hybrid security environment that merges Kali Linux’s offensive toolkit with hardened, VPN-bunker-style isolation—enhanced by modern AI…
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 juanorts/crushftp10-docker-cve-2024-4040
A Dockerized setup for running a vulnerable CrushFTP 10 server instance (CVE-2024-4040).
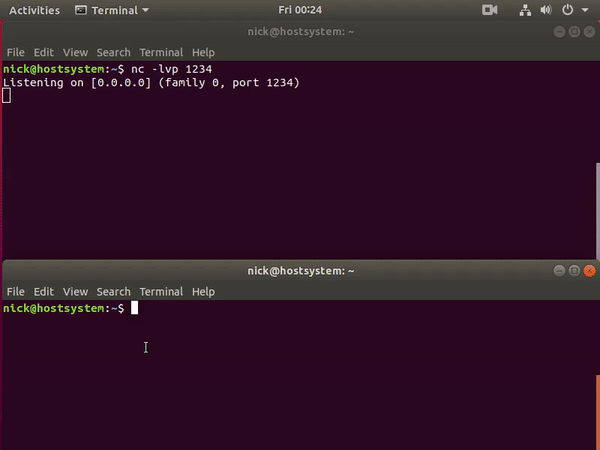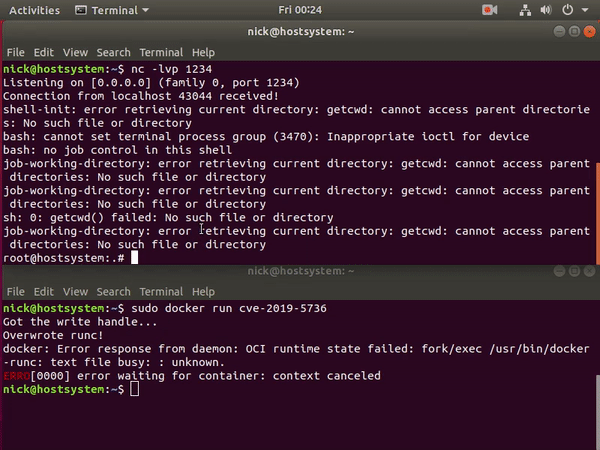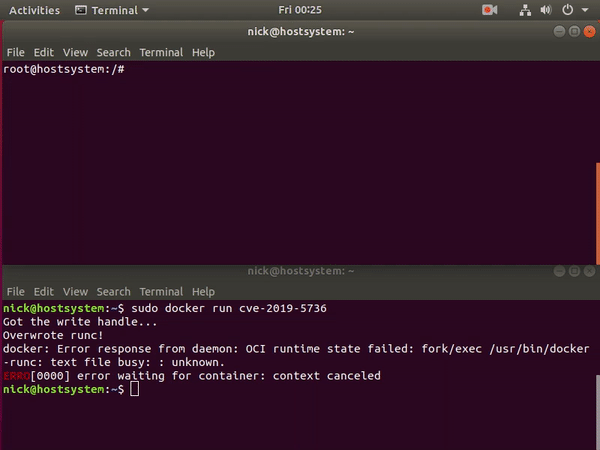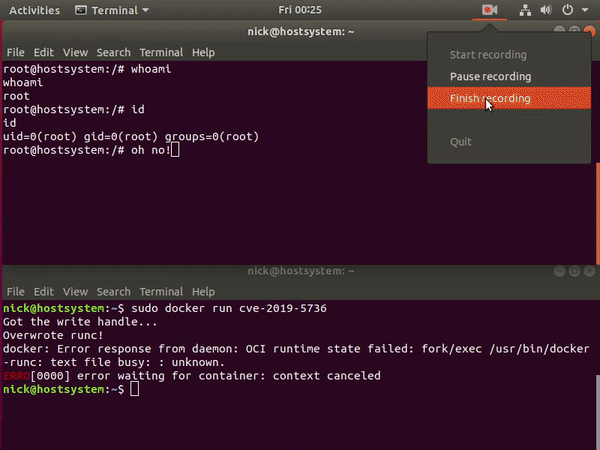 frichetten/cve-2019-5736-poc
PoC for CVE-2019-5736
 aquasecurity/tracee
Linux Runtime Security and Forensics using eBPF
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
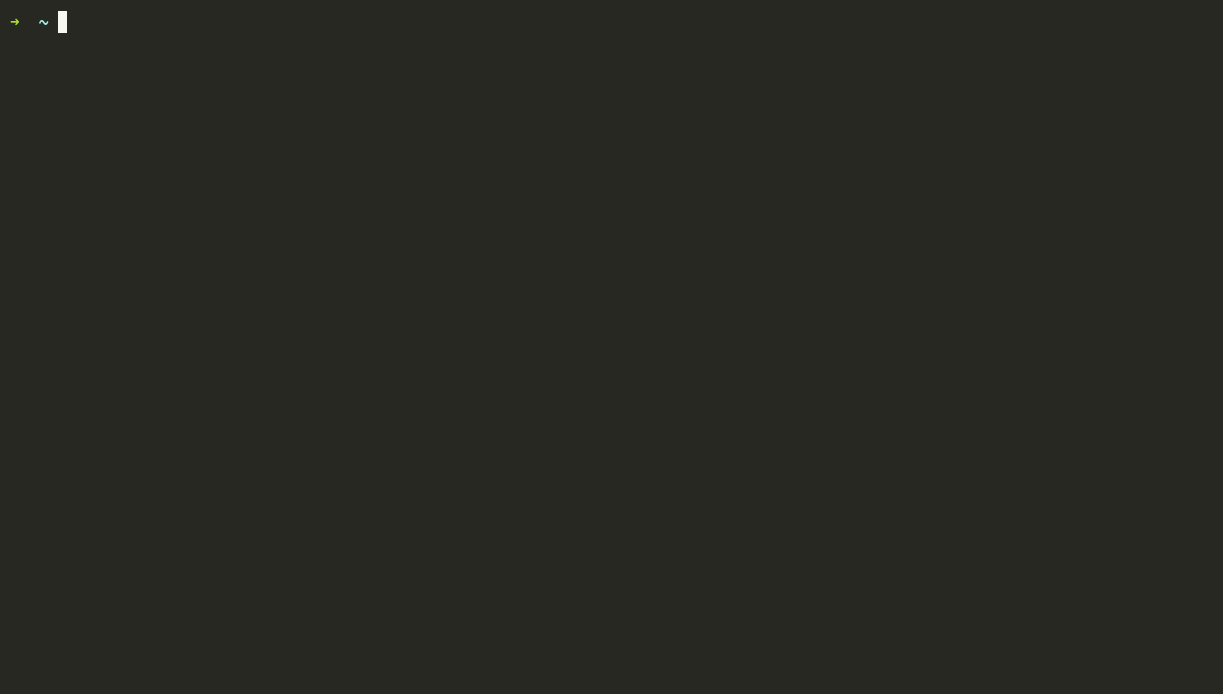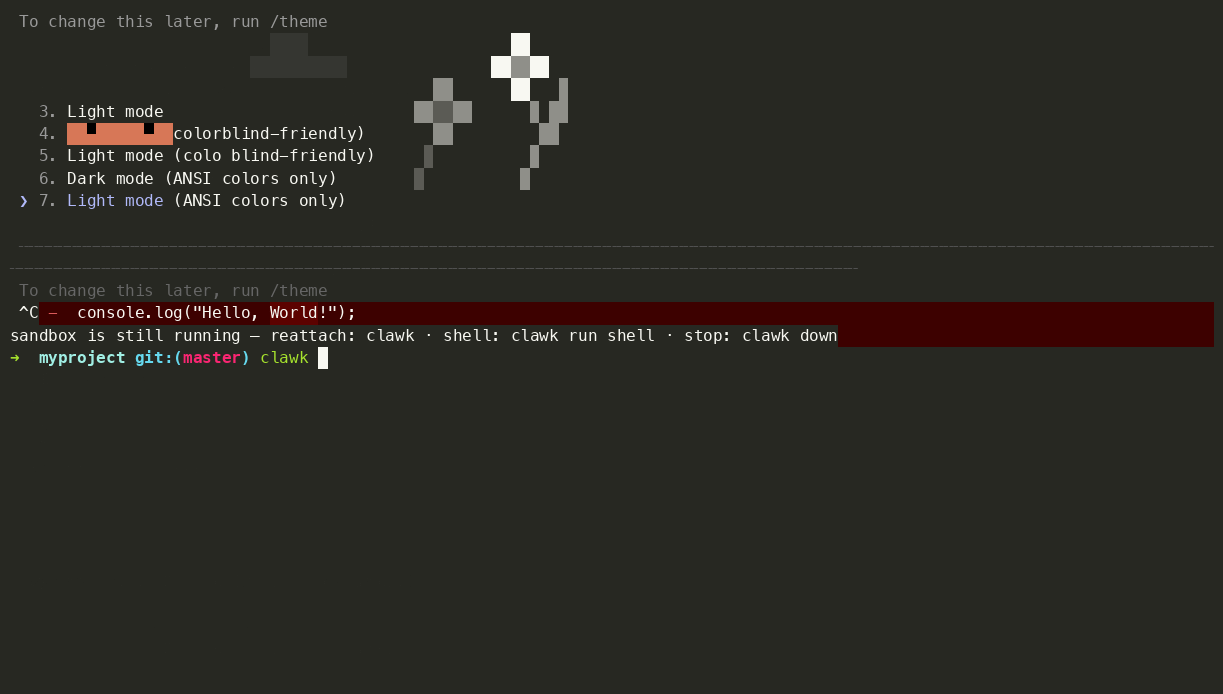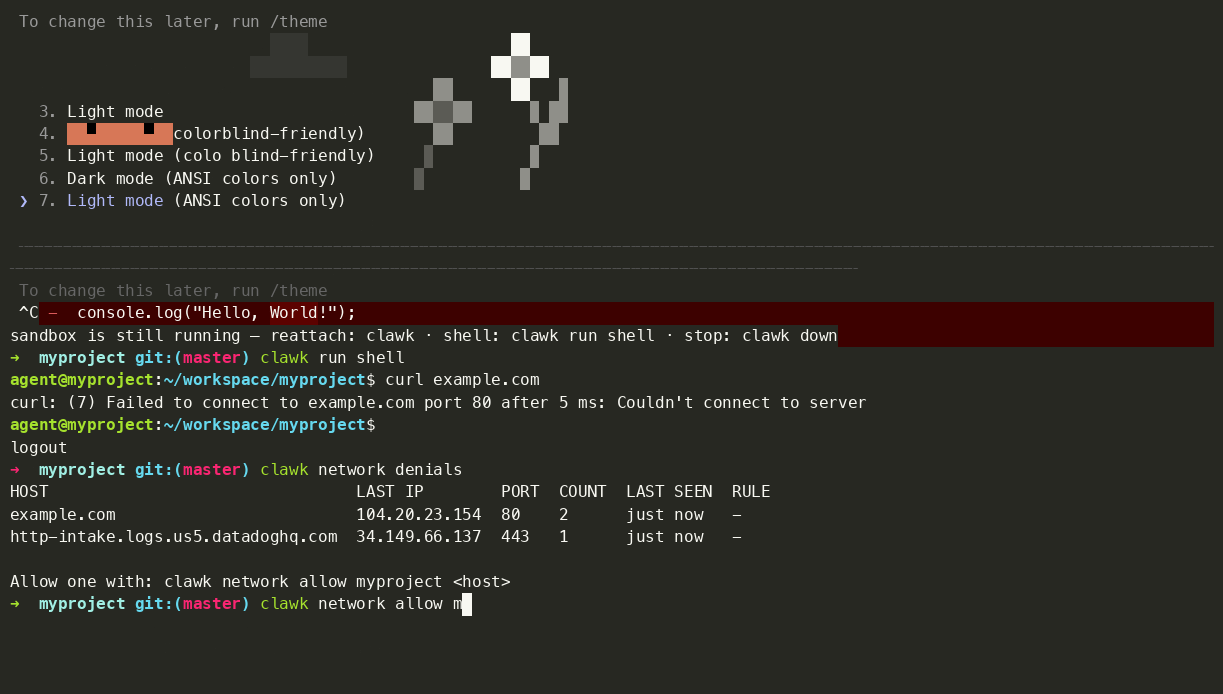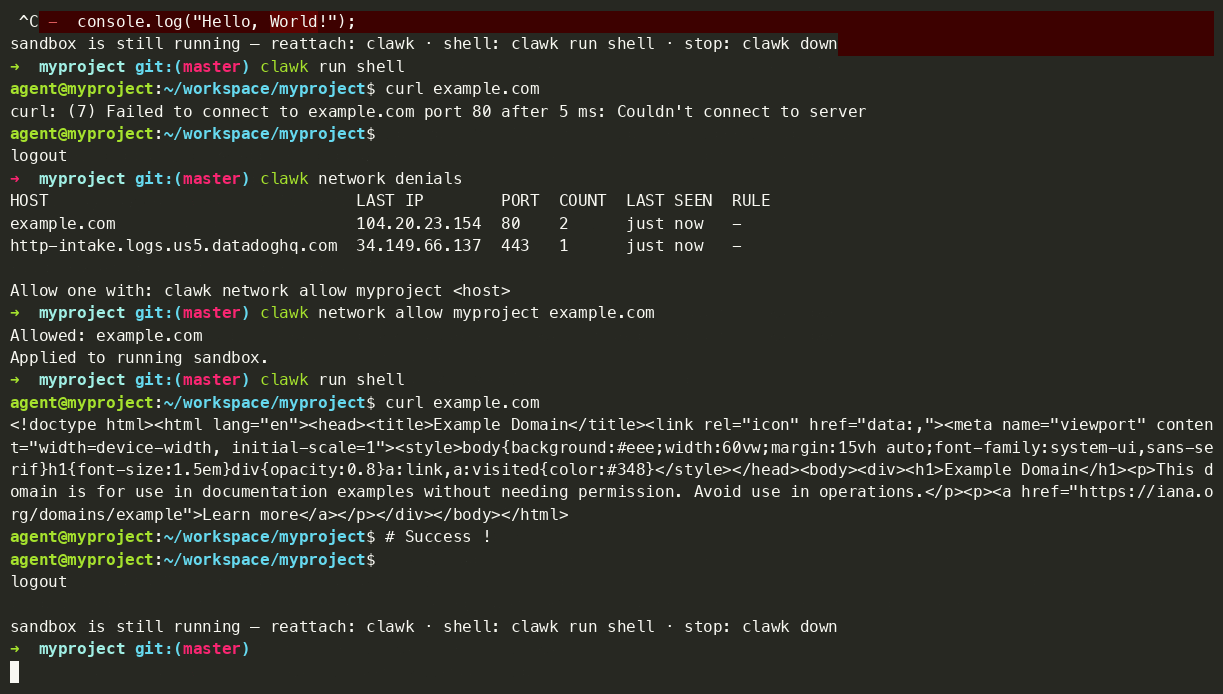 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop