
Archived
legion
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
container-securityexploitationids-ips-evasion+8
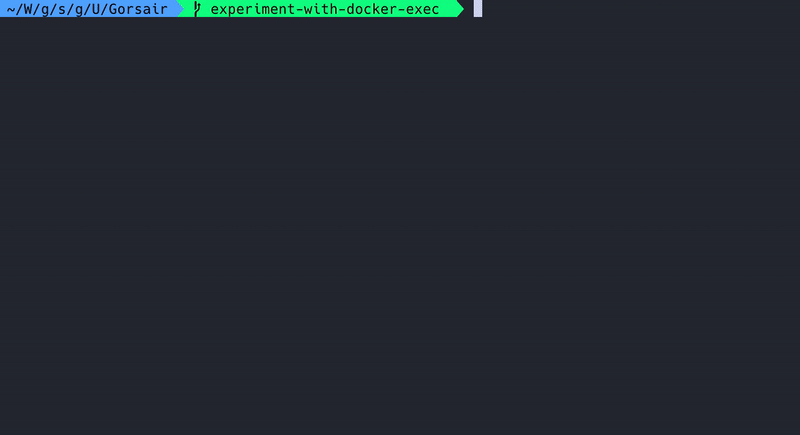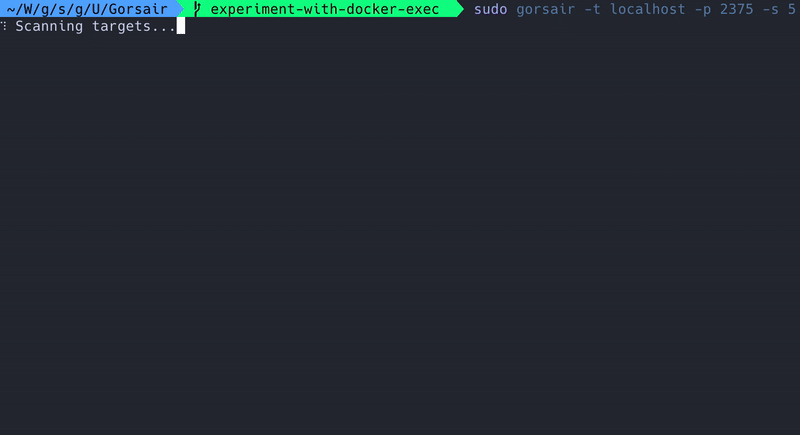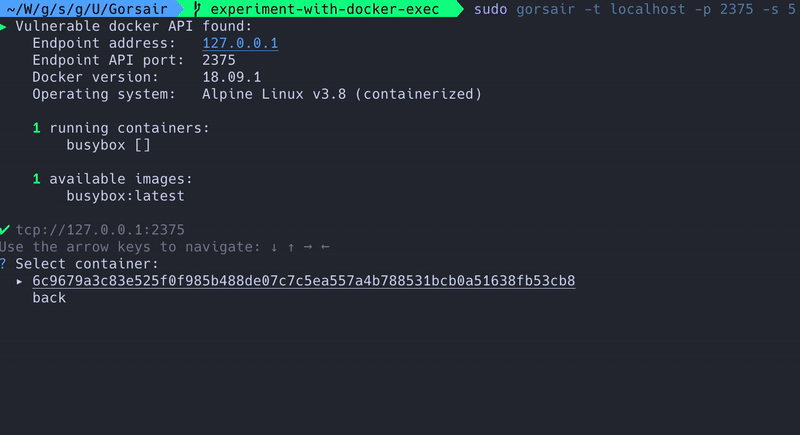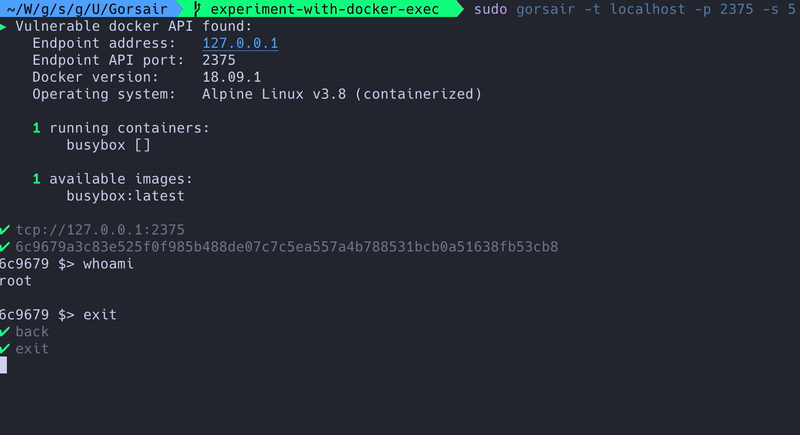 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
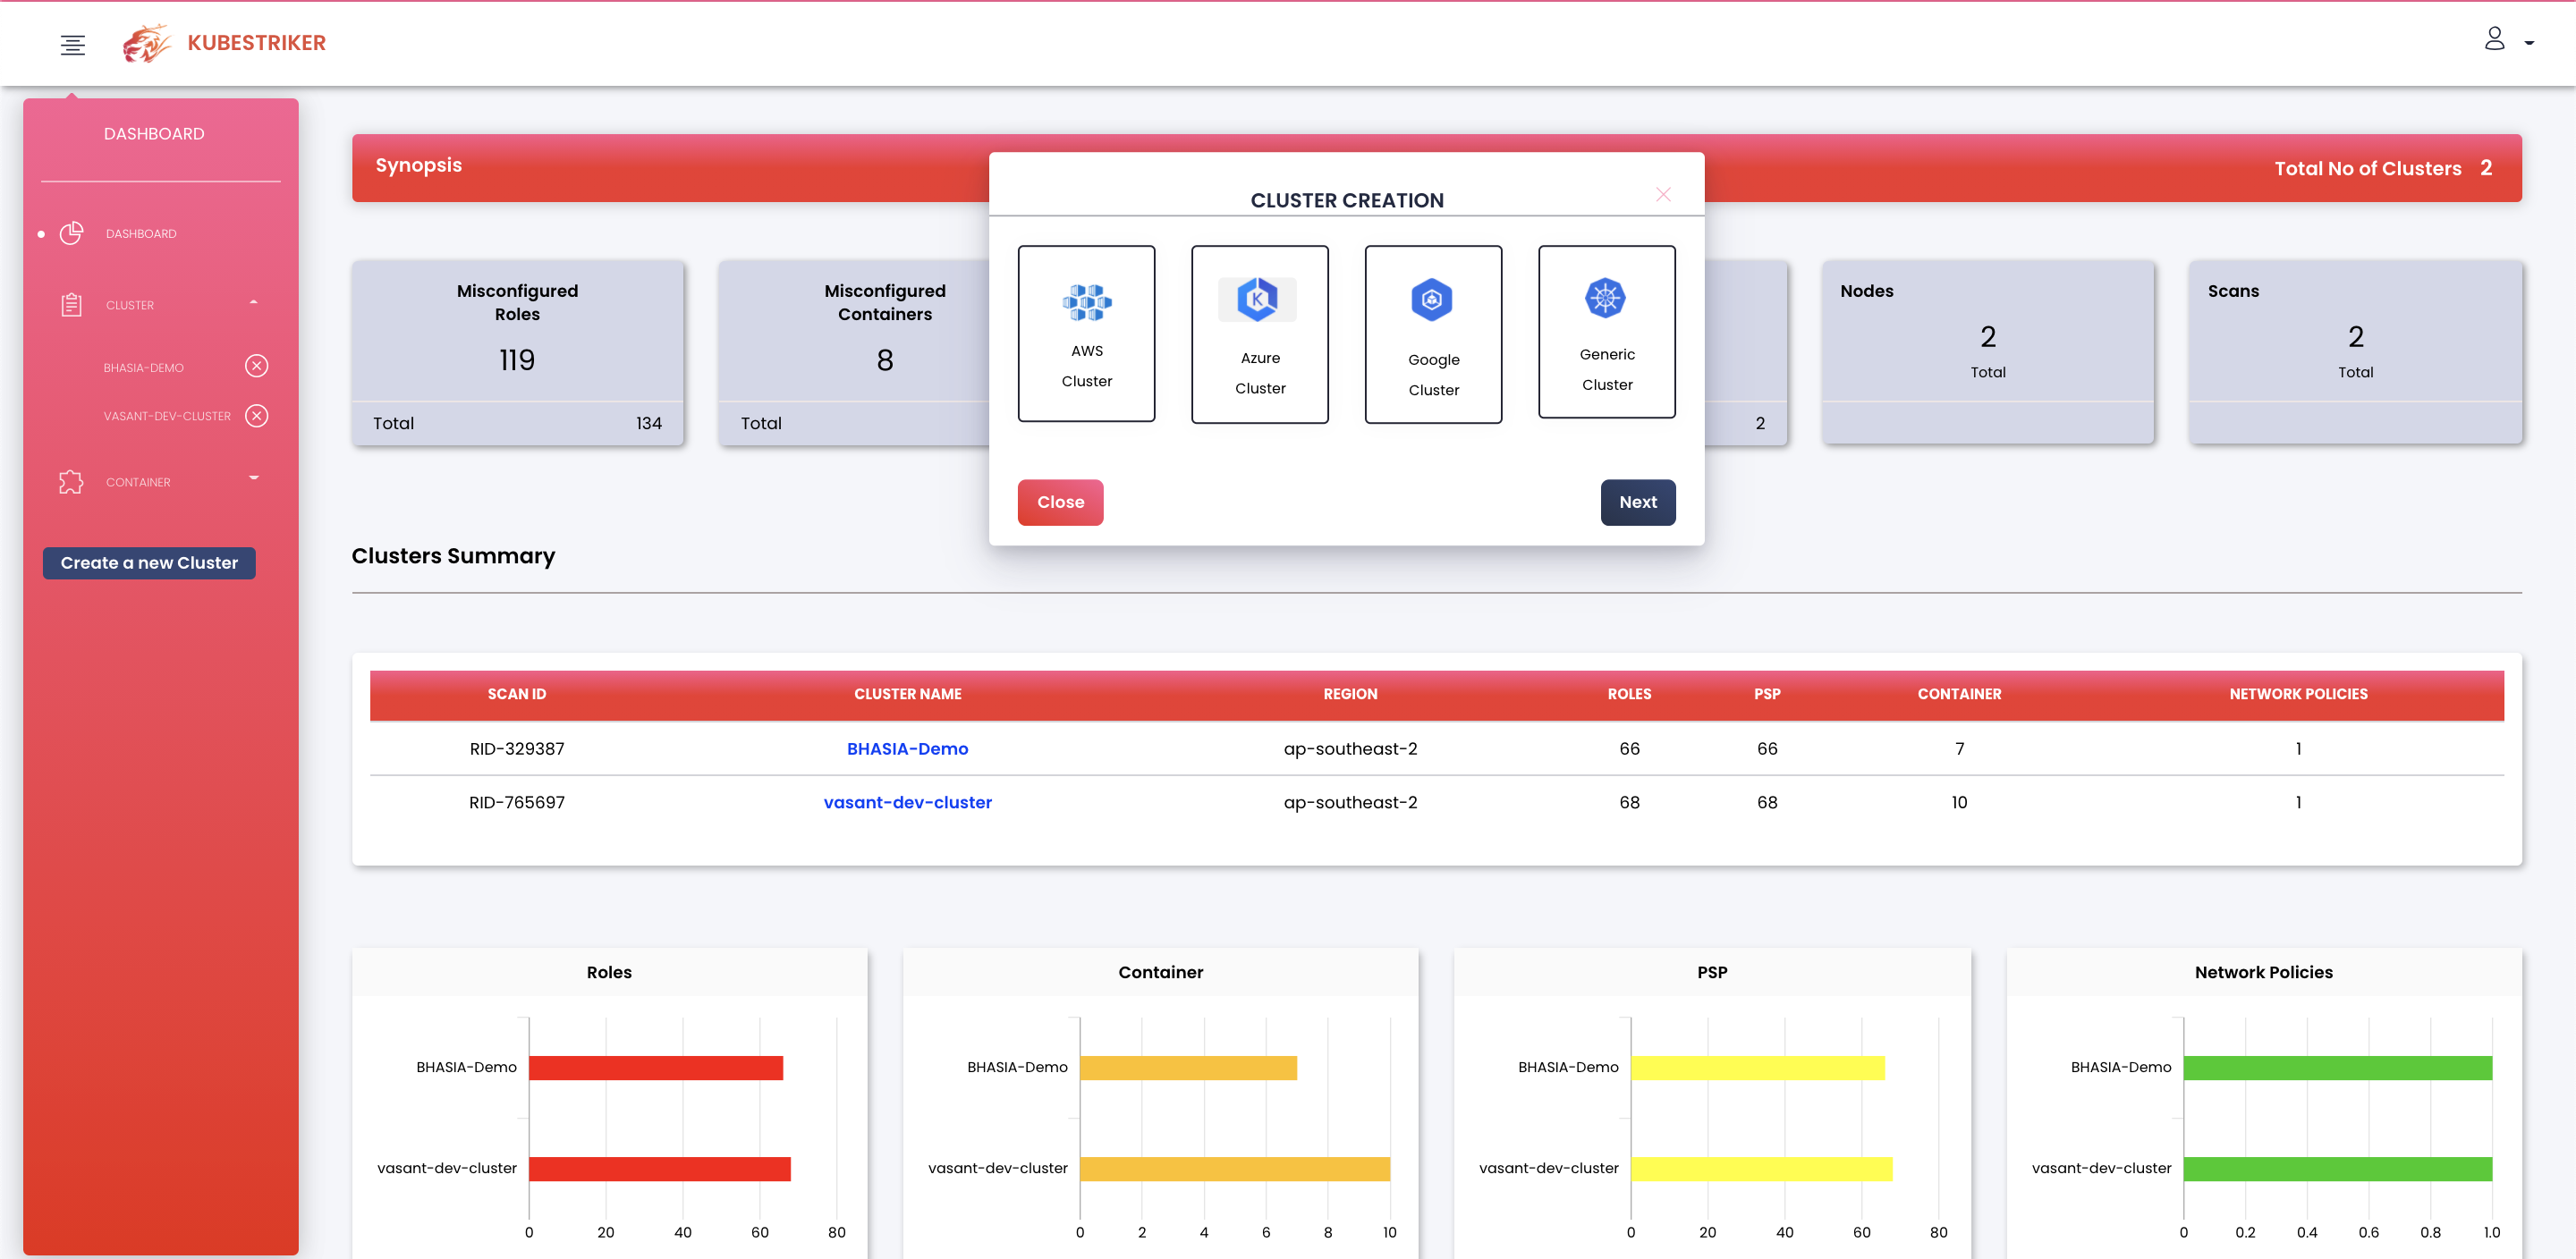 vchinnipilli/kubestriker
A Blazing fast Security Auditing tool for Kubernetes
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 shoucheng3/fabric8io__kubernetes-client_cve-2021-4178_5-0-2
Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…
 shoucheng3/kubernetes-client__java_cve-2020-8570_client-java-parent-9_0_2_fixed
Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 cved-sources/cve-2016-6515
Docker container providing a vulnerable environment for CVE-2016-6515 exploitation, part of the Cved framework for managing and testing against known…
 cved-sources/cve-2018-15473
Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.