
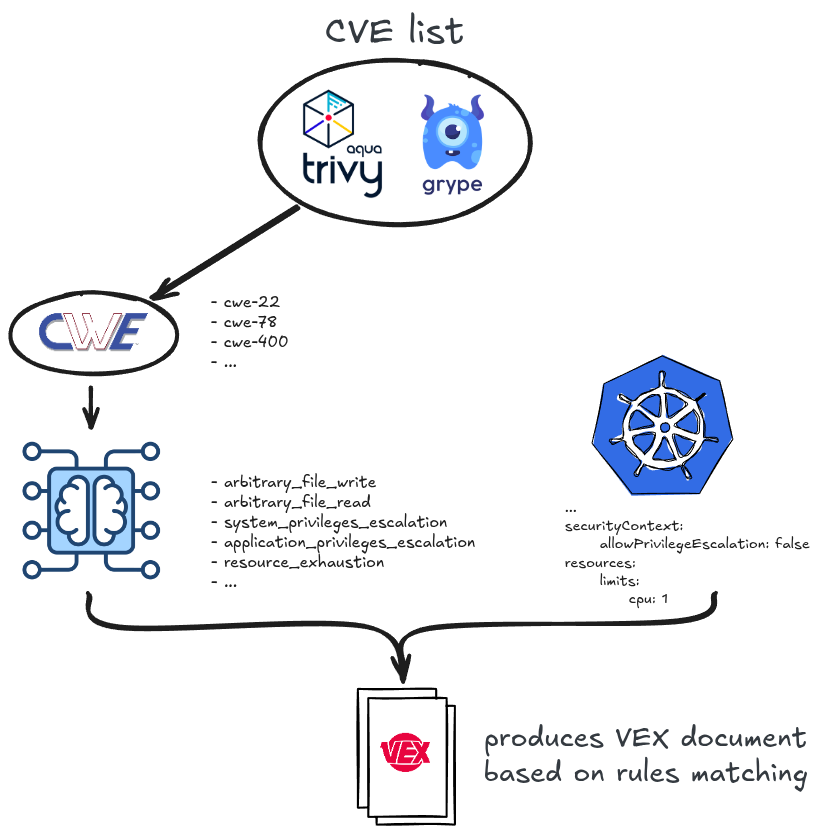
vex8s
 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
alegrey91/vex8sSuppress vulnerabilities applying Kubernetes context to scans
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 rhysemmas/martian-packets
Crafting raw TCP/IP packets to send to poorly configured Kubernetes servers - CVE-2020-8558 PoC
 rishvic/xpdf-docker
Docker images of Xpdf 4.04, vulnerable to CVE-2022-30524
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 axelcurmi/log4shell-docker-lab
Log4Shell (CVE-2021-44228) docker lab
 yen5004/cve-2024-40635_poc
Proof of Concept code for proving CVE-2024-40635 vulnerability
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API