
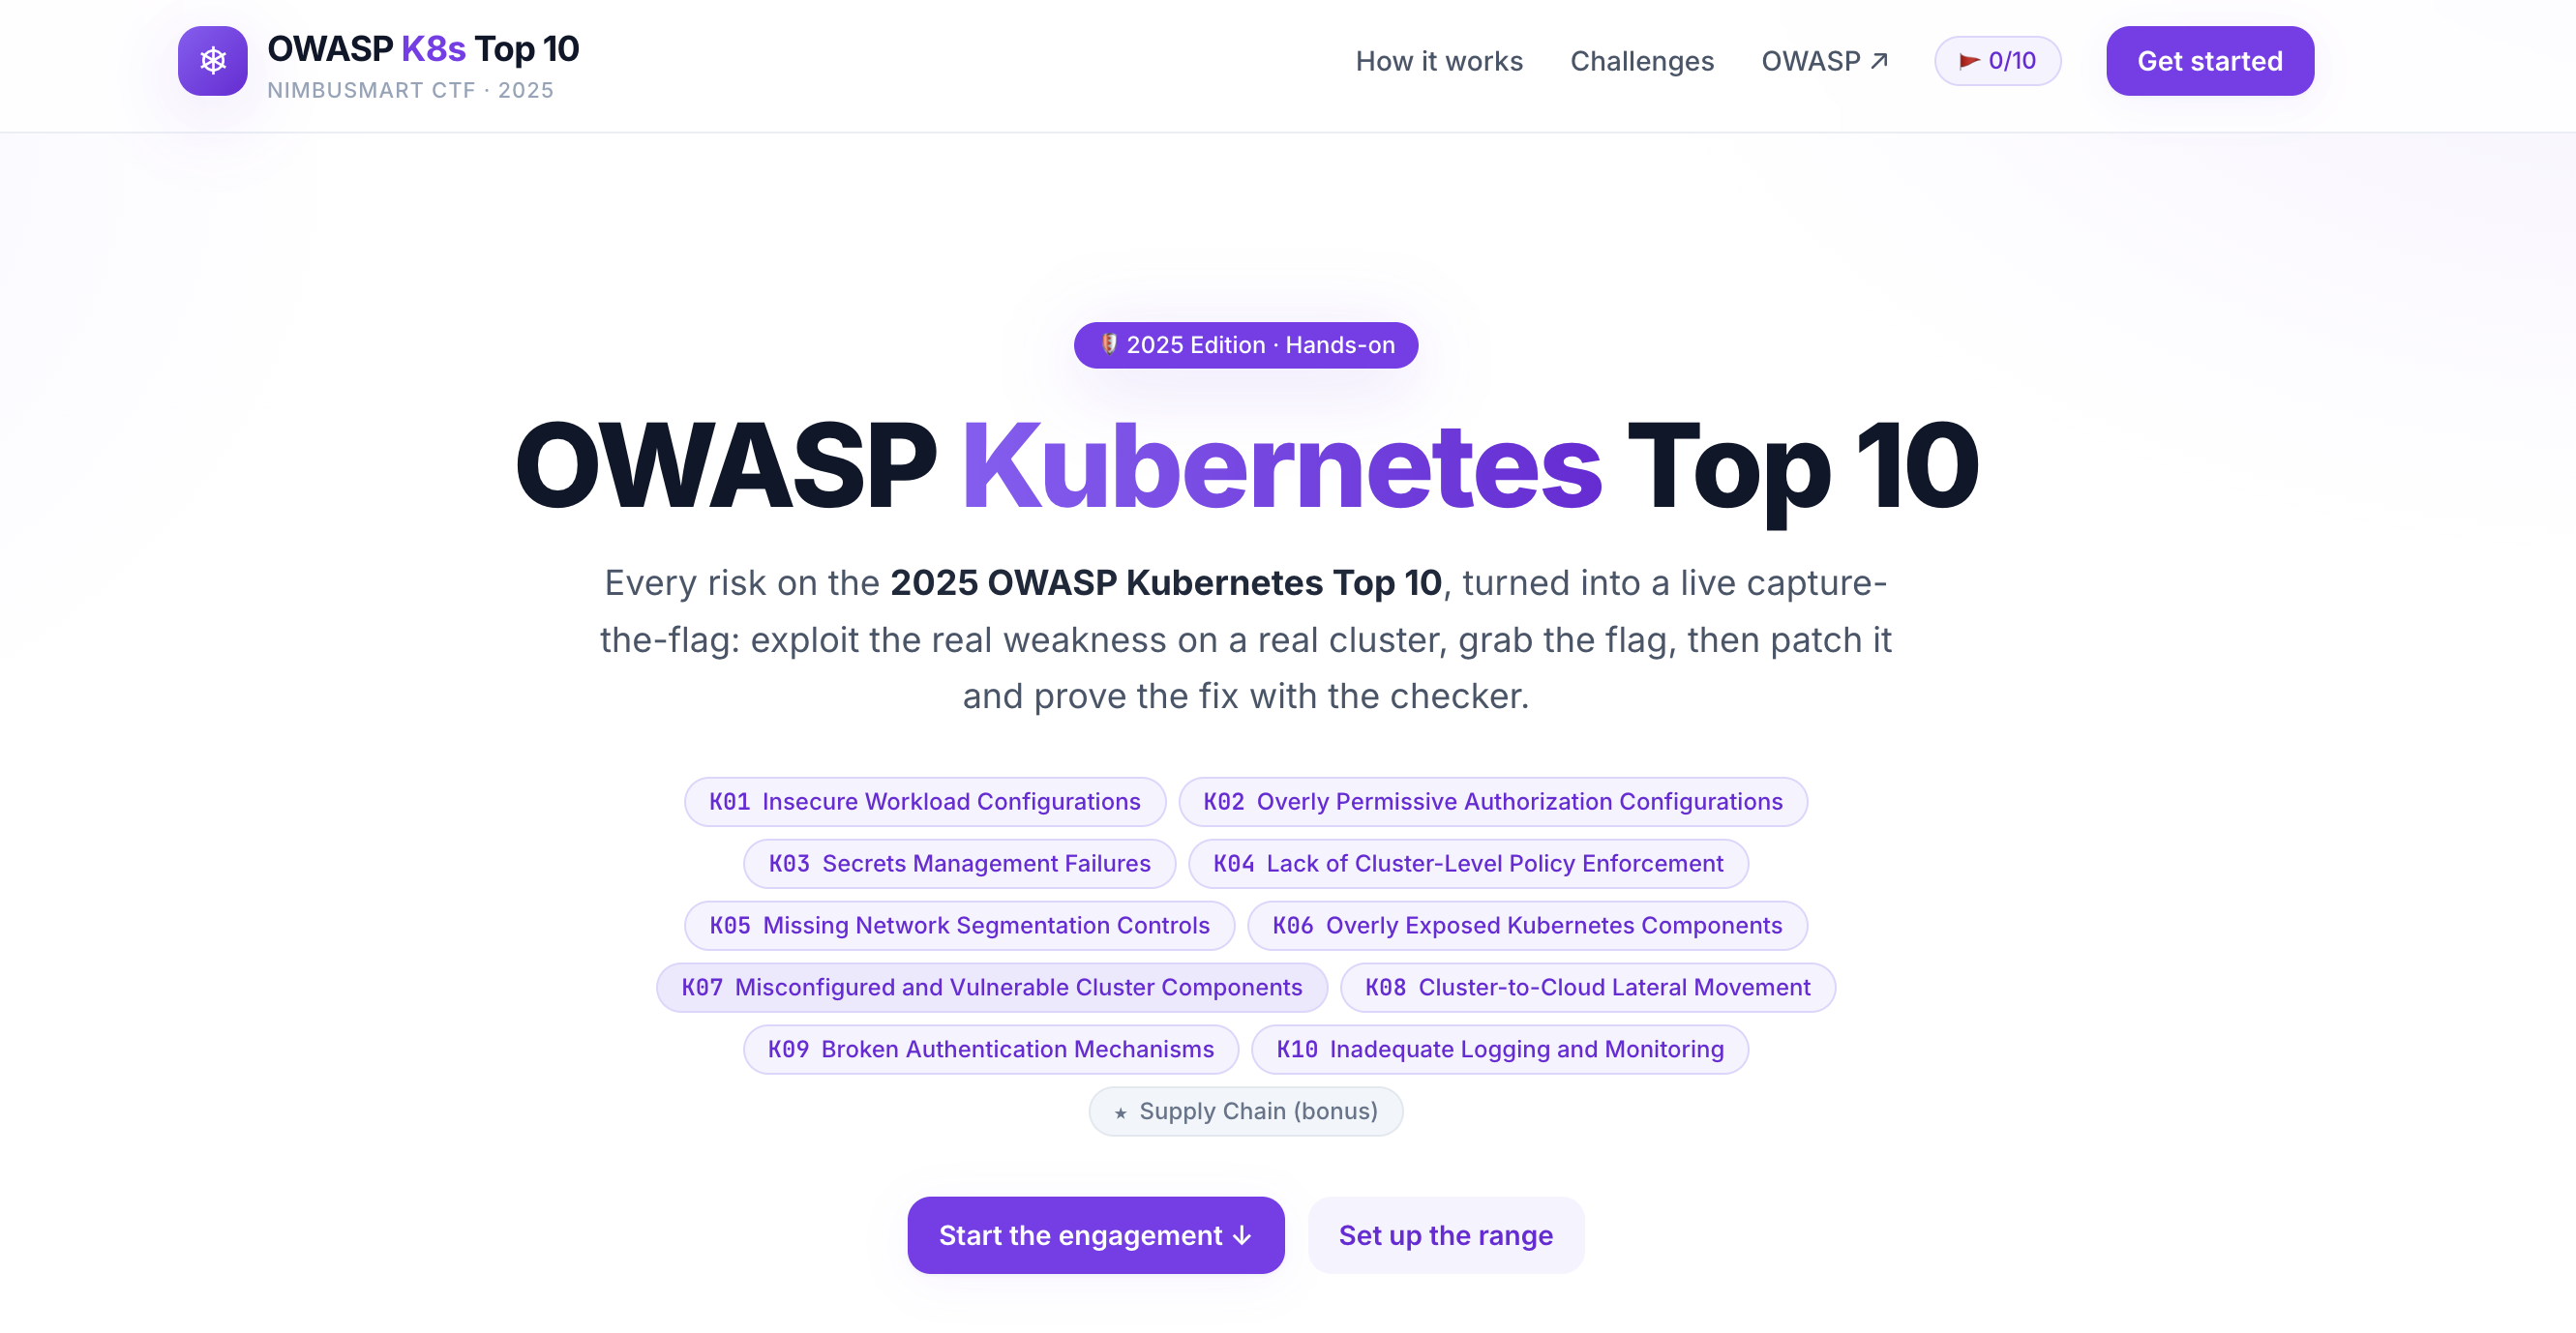
Owasp-top-10-k8s-2025
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
cloud-securitycontainer-securityctf+8
49
hac01/owasp-top-10-k8s-2025Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.