CyberStrikeAI
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+8
7.2k
aipentest/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 cloudflare/flan
A pretty sweet vulnerability scanner
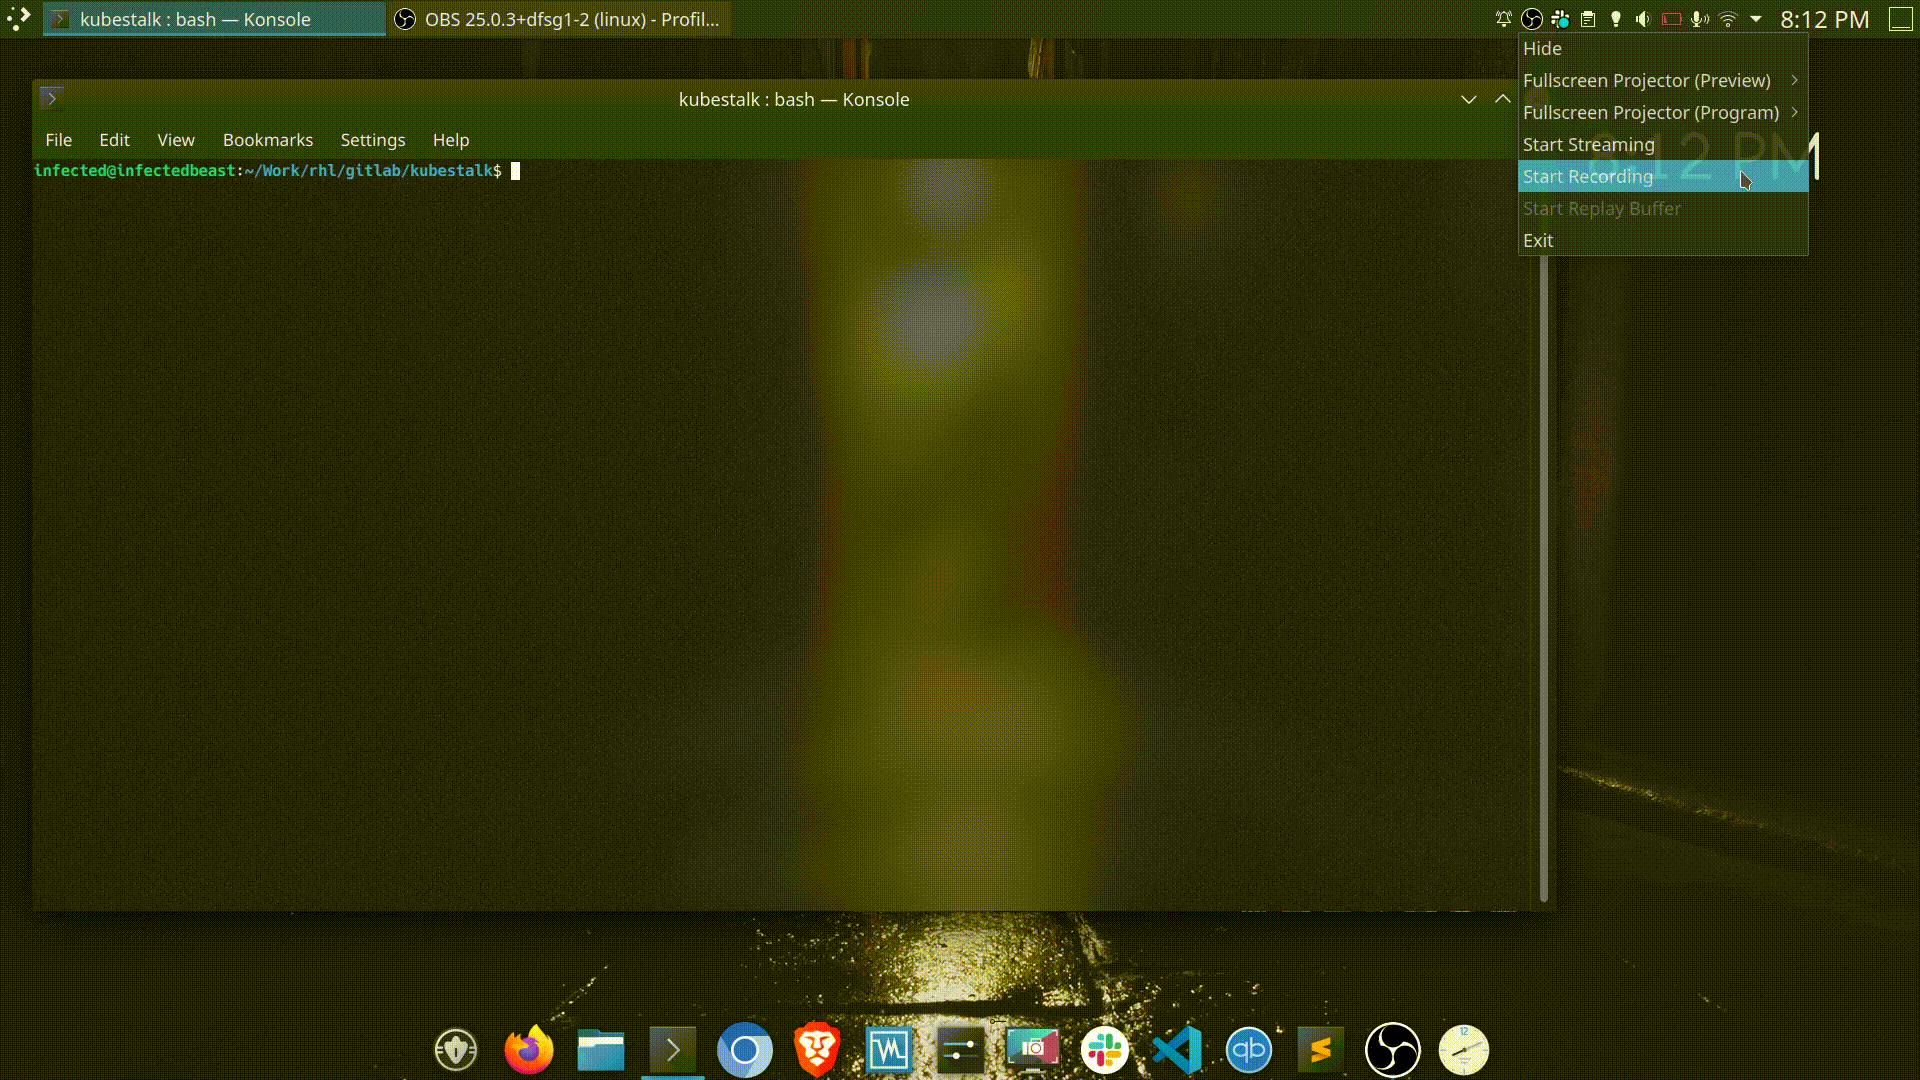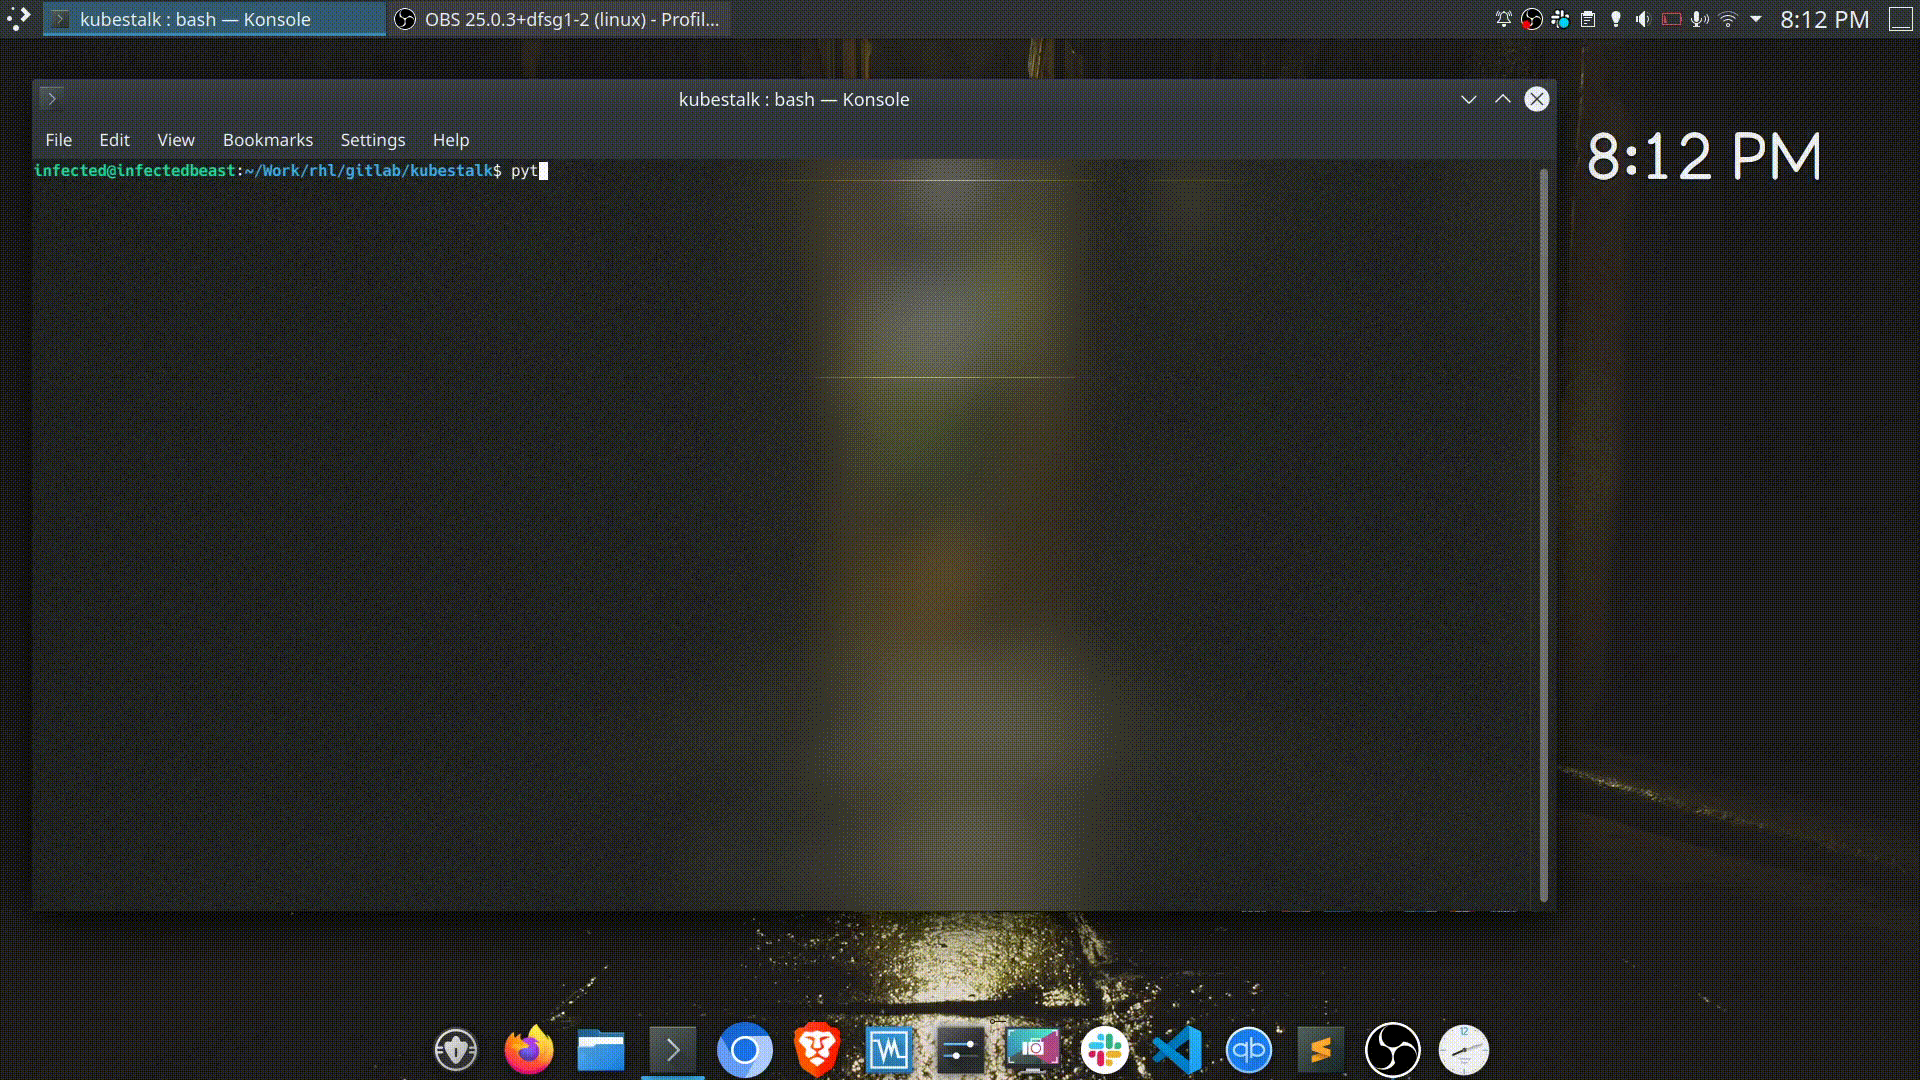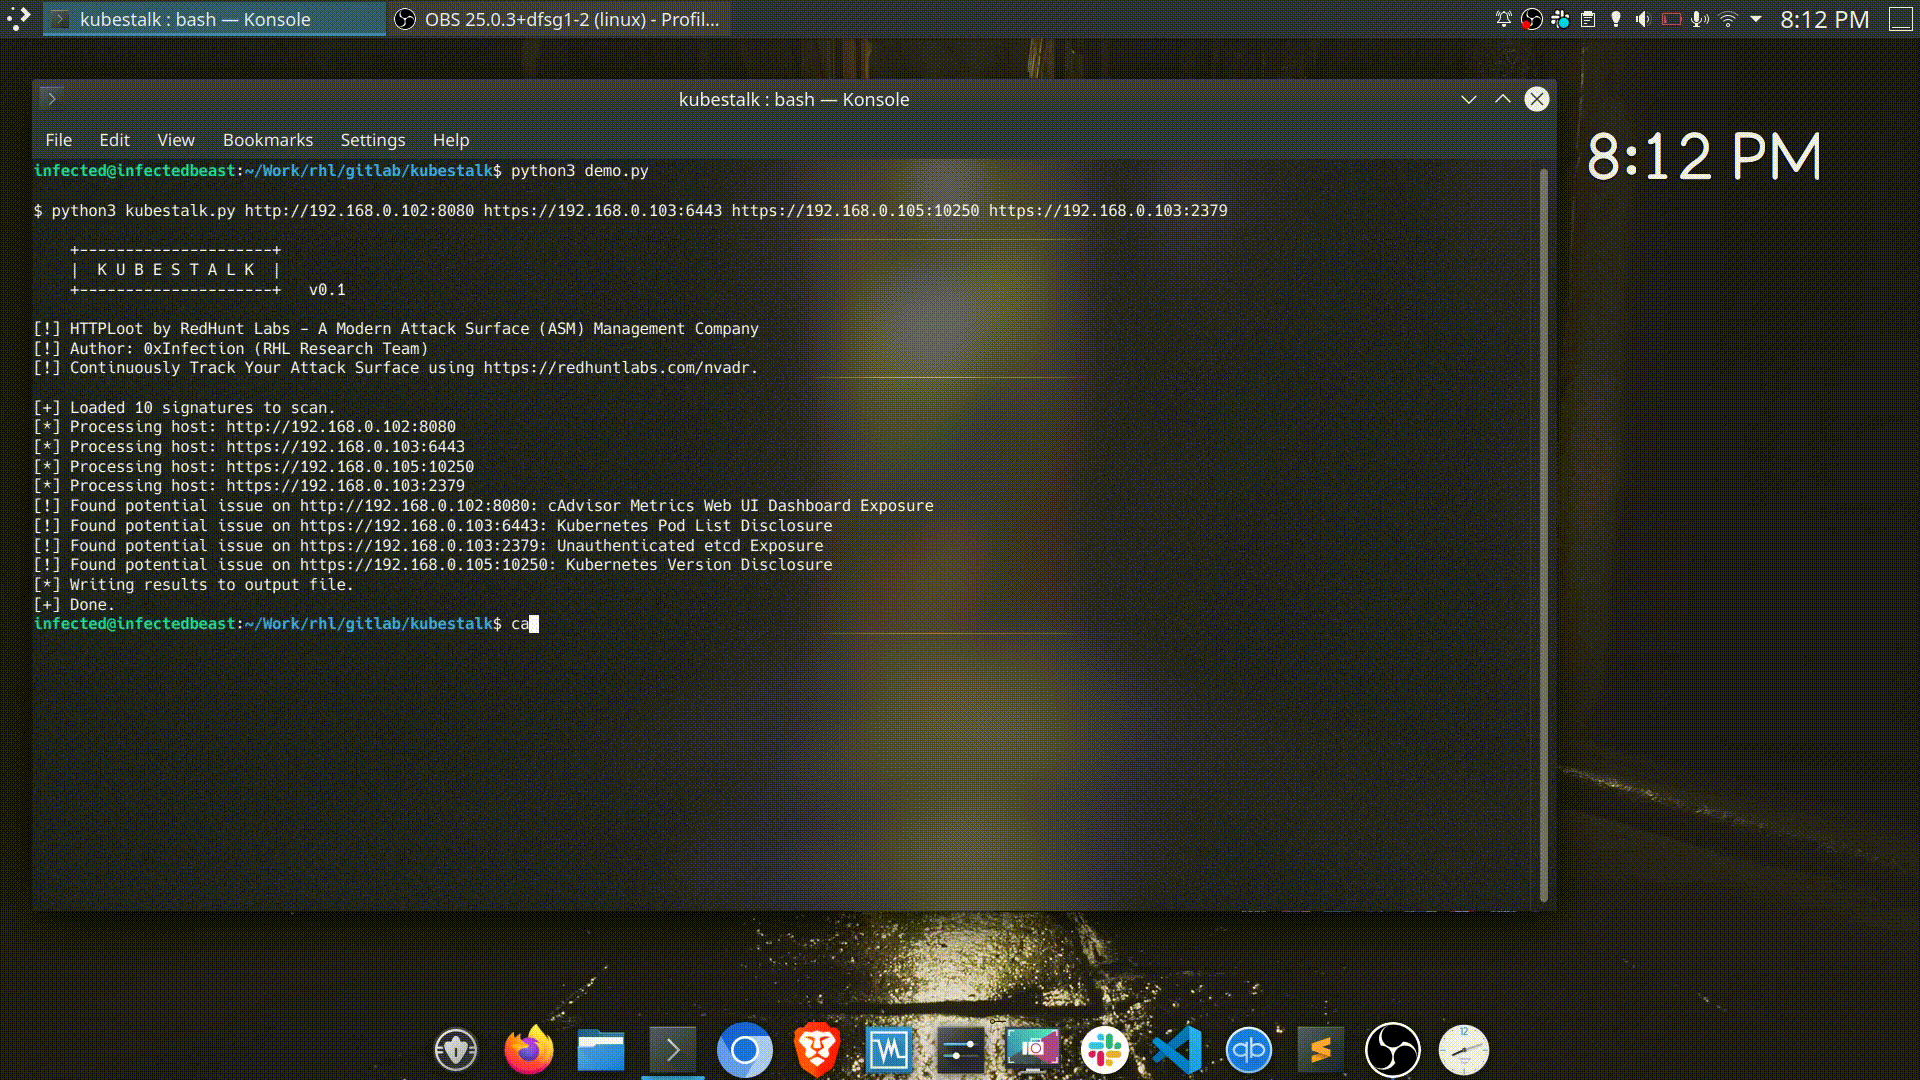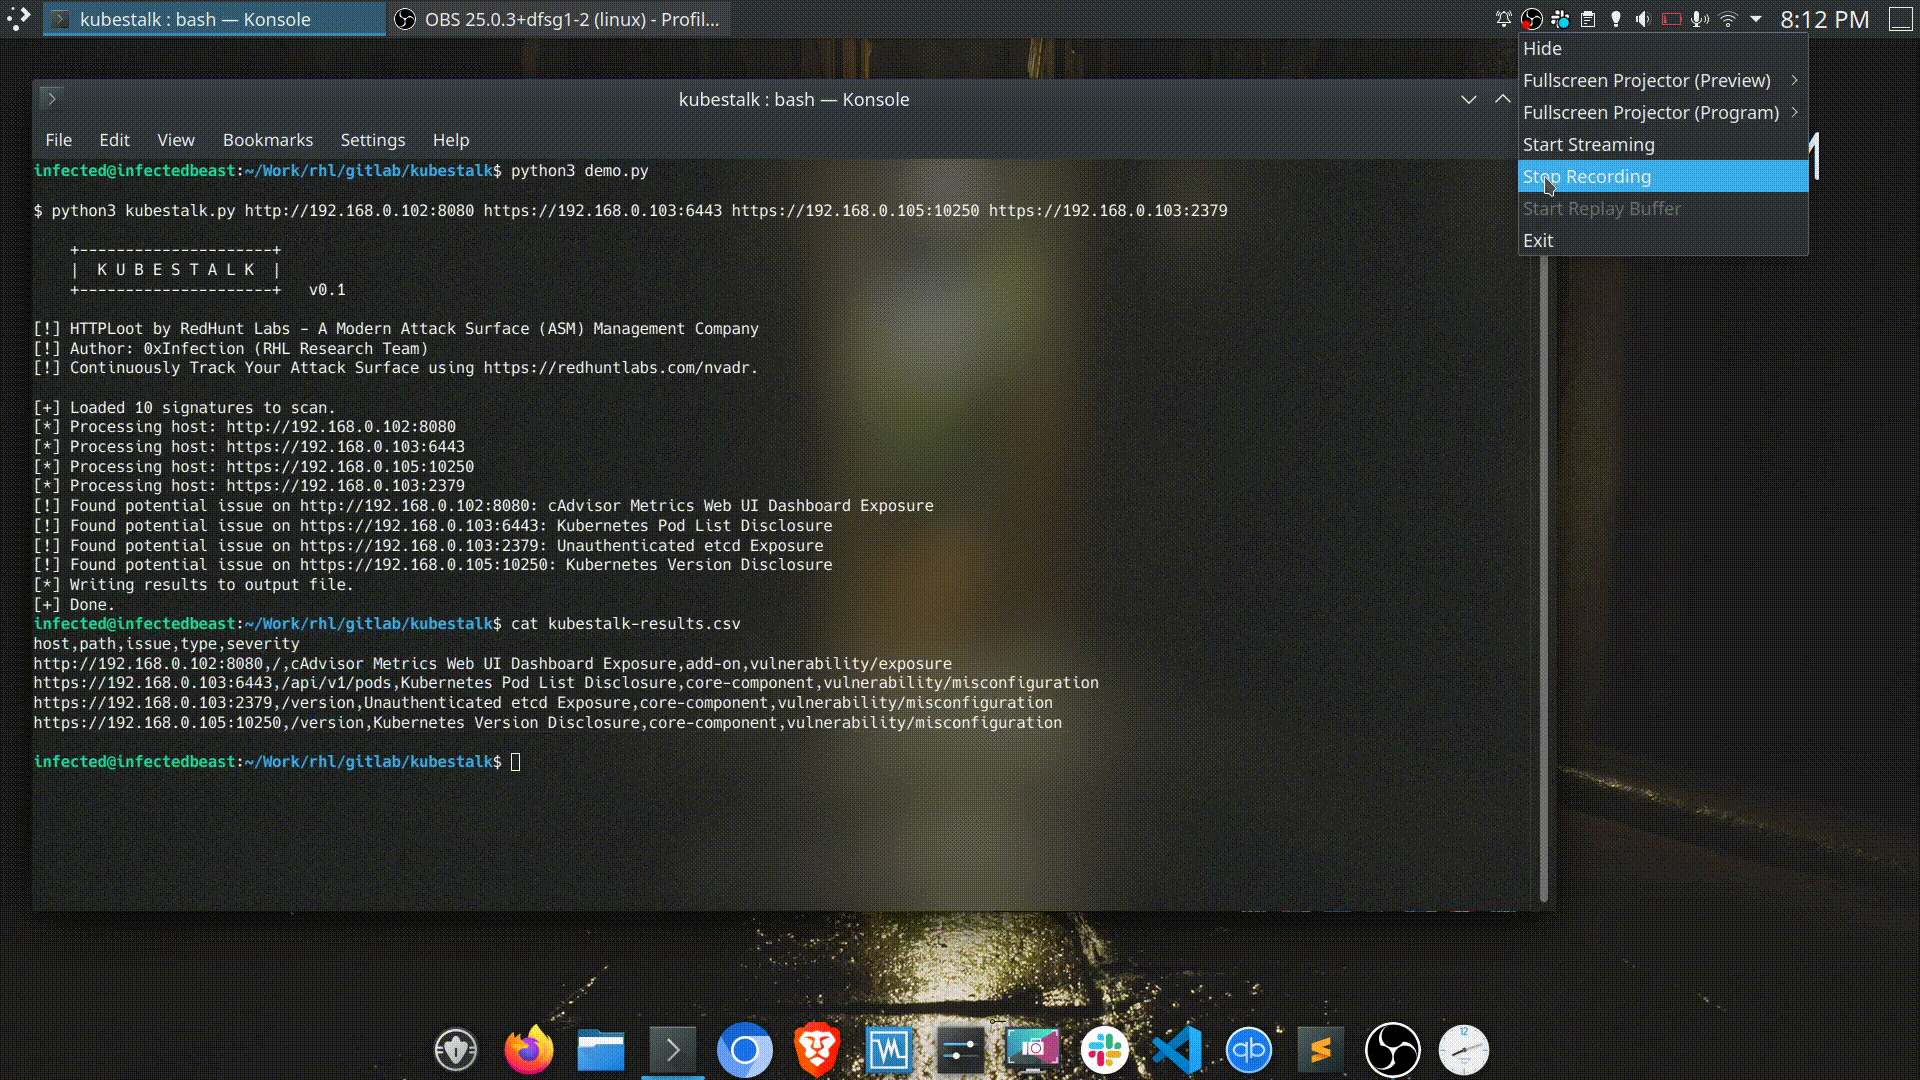 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
 hackerhouse-opensource/cve-2018-10933
Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…
 professionallyevil/harpoon
A collection of scripts, and tips and tricks for hacking k8s clusters and containers.
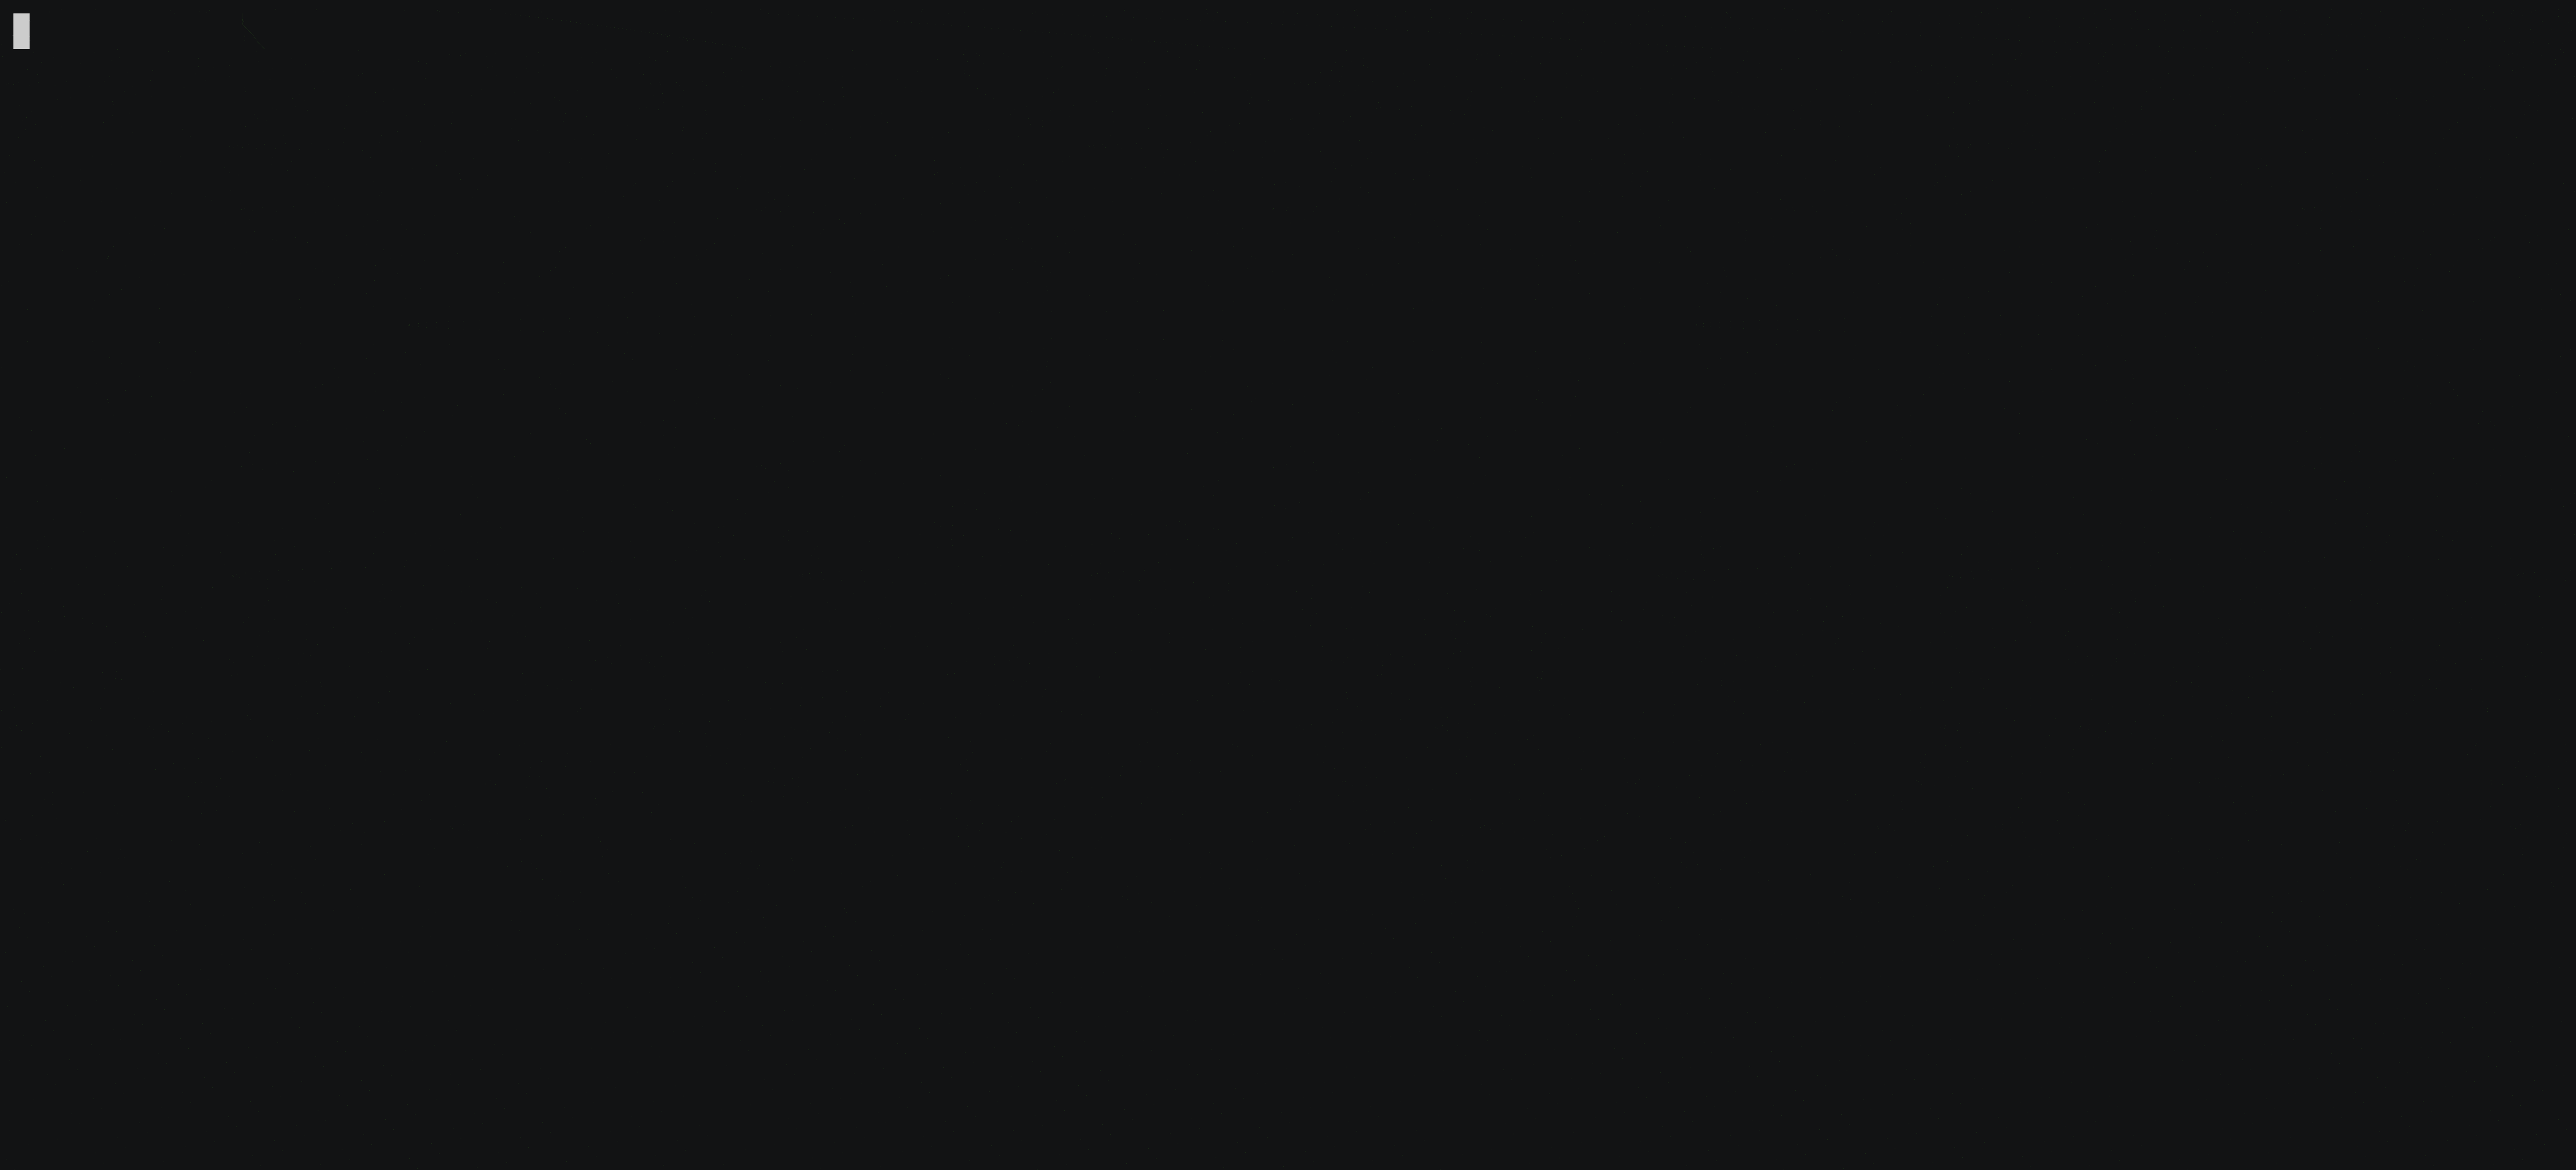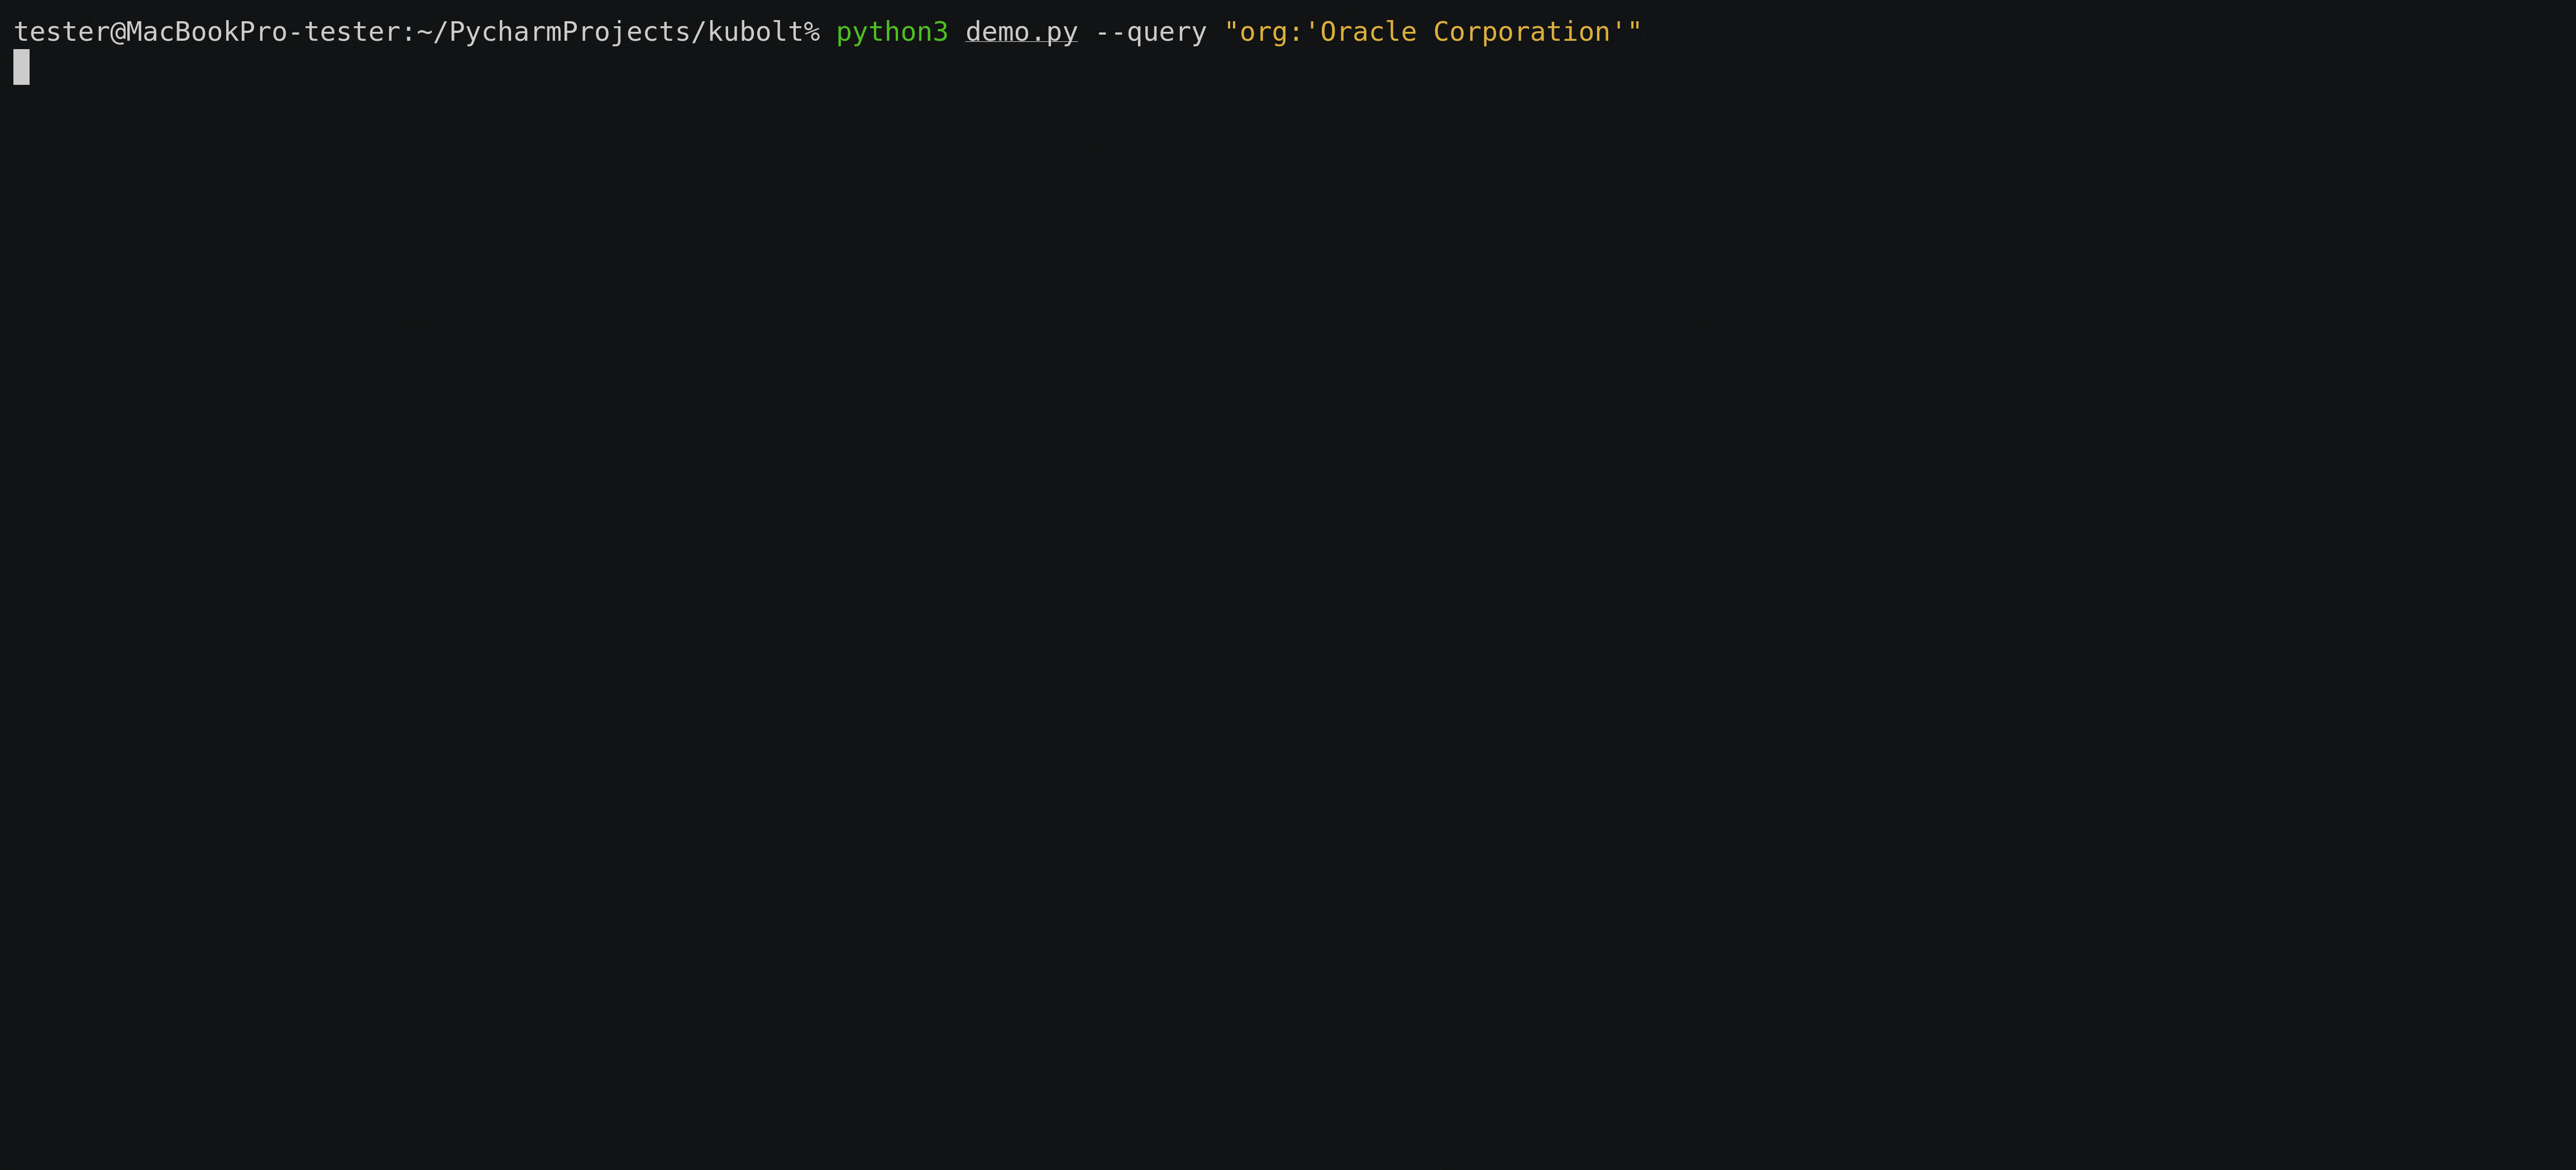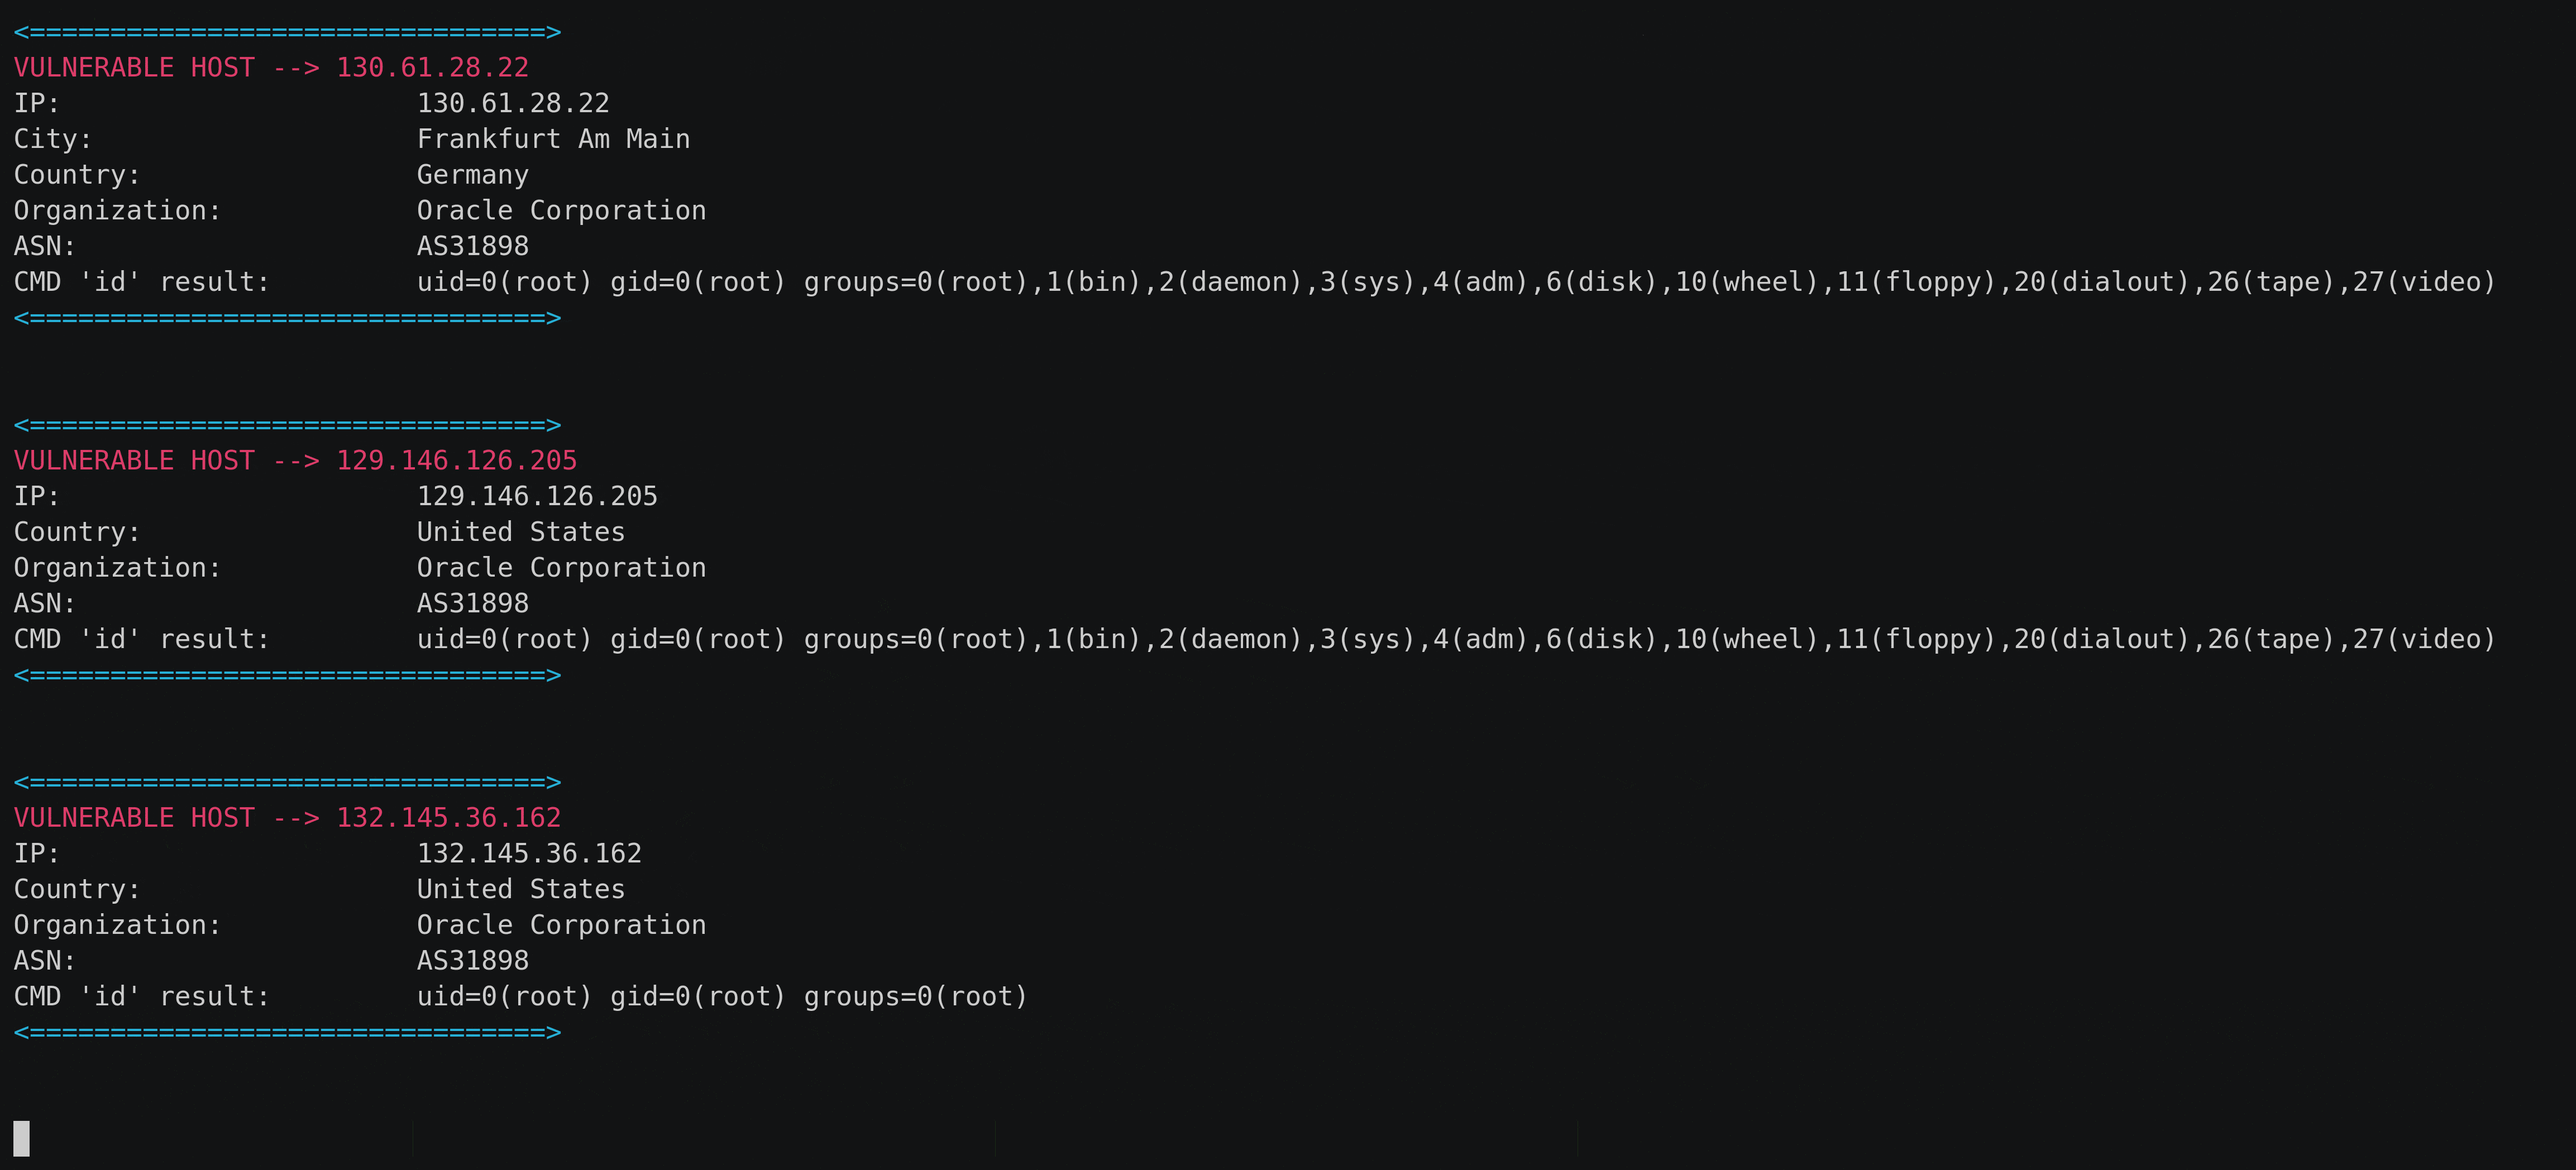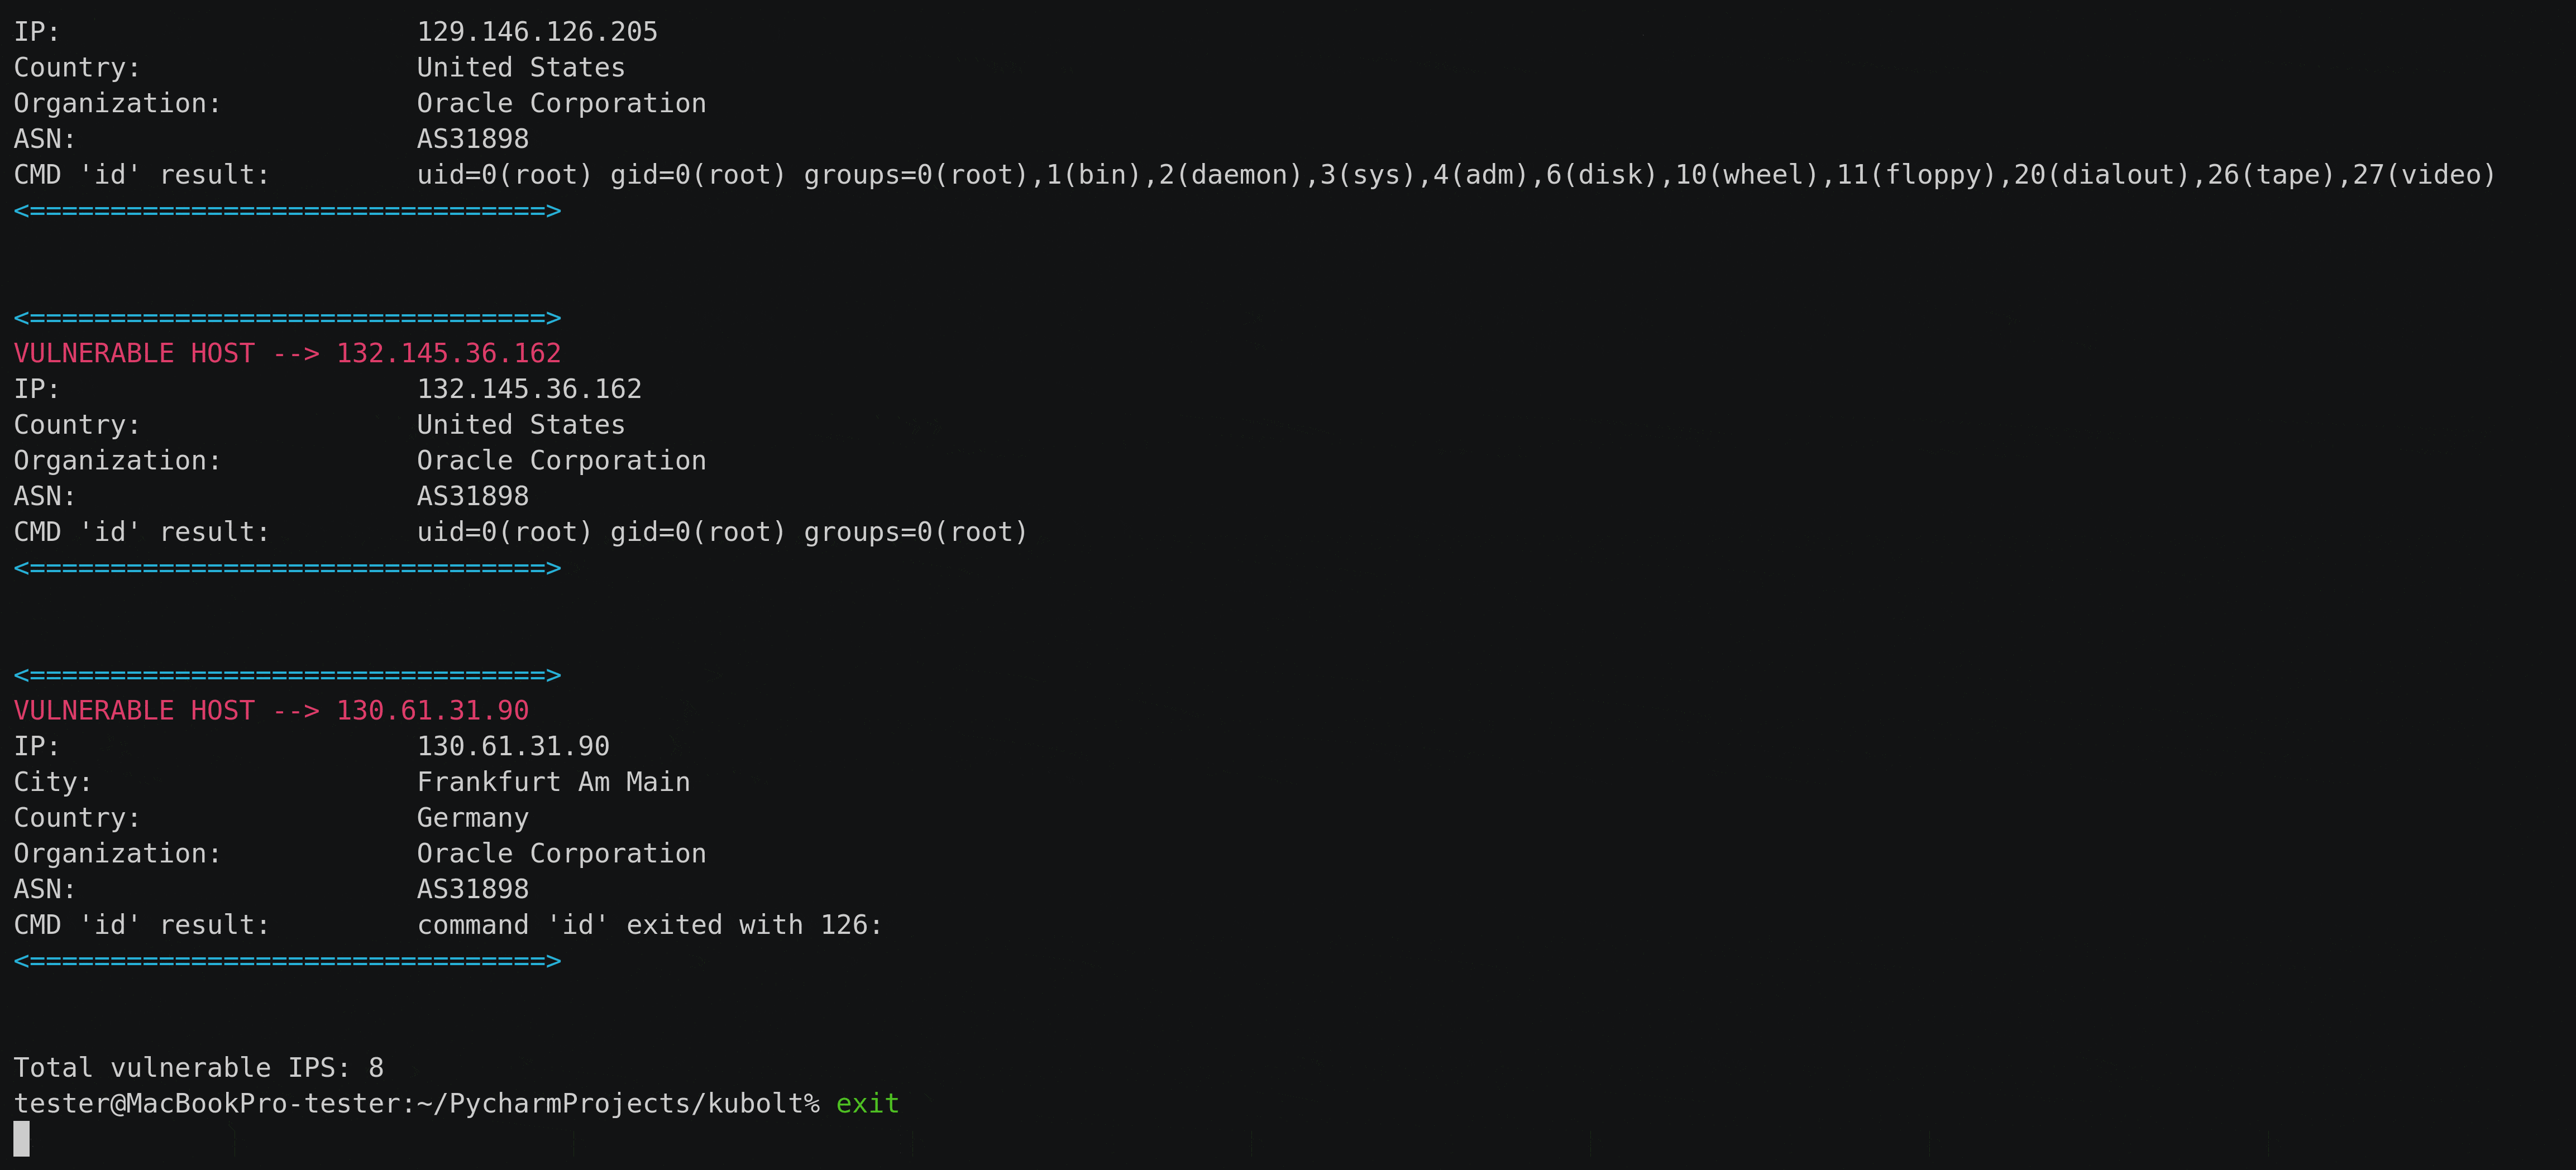 averonesis/kubolt
Kubolt utility for scanning public kubernetes clusters
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
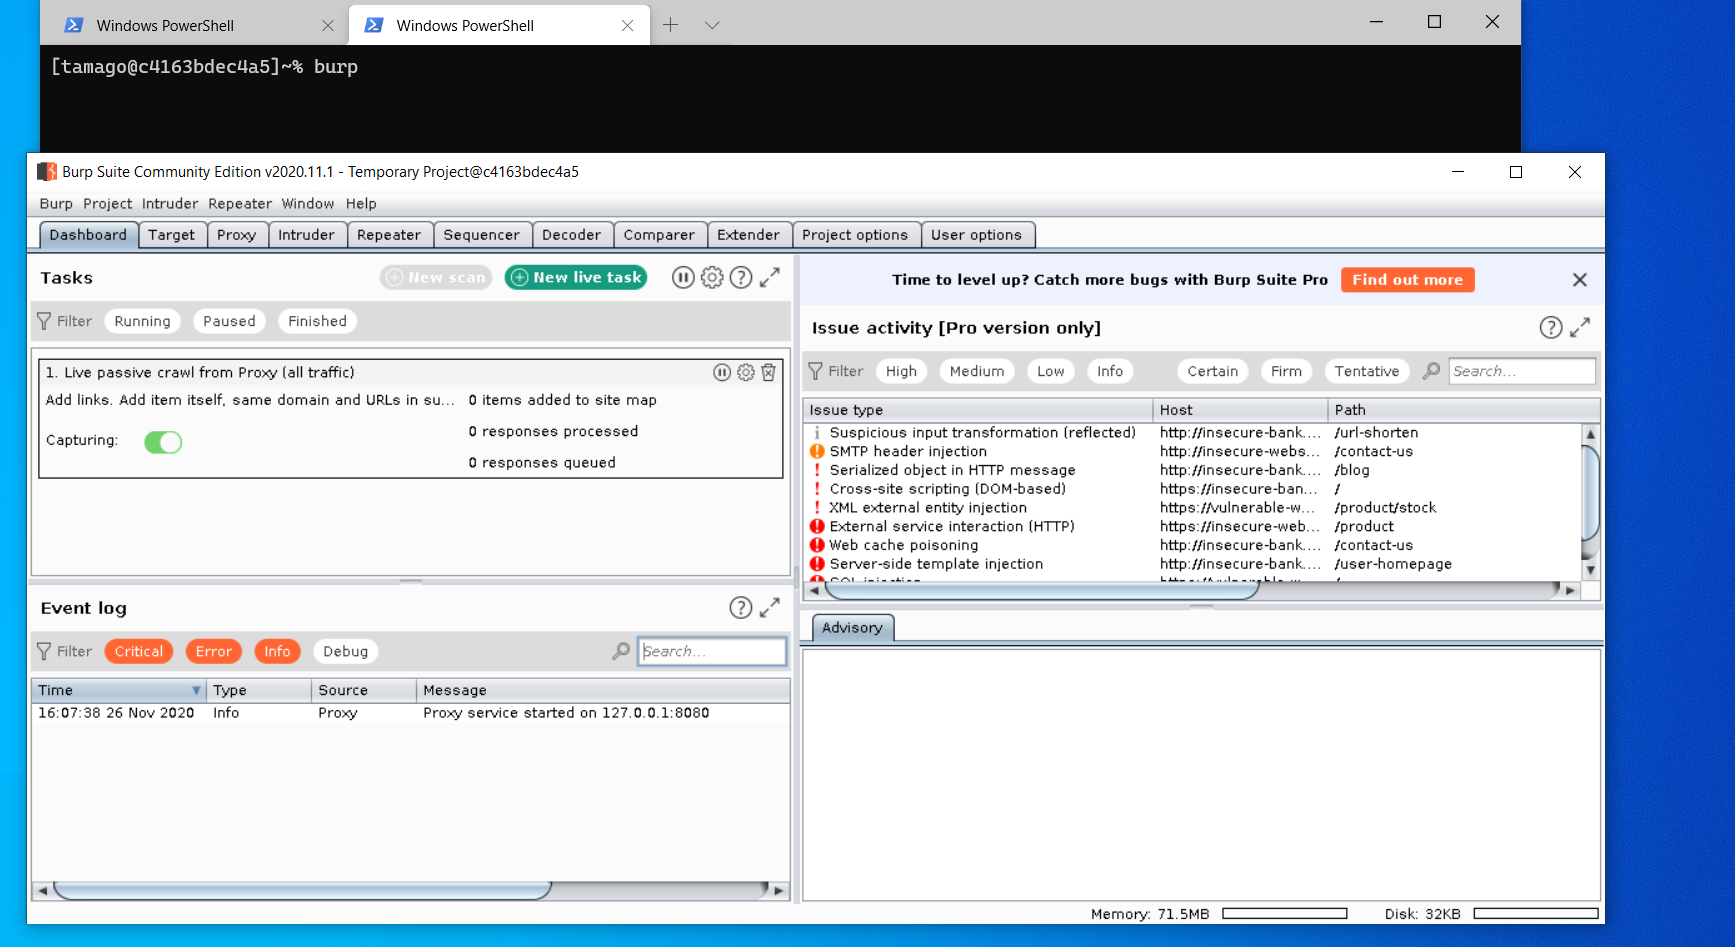 himazawa/bento
Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
 murrez/cve-2026-100835
Python PoC for CVE-2026-100835: audits Contrast manifests for AllowedChipIDs/AllowedPIIDs, detects versions, and probes Coordinator endpoints to…
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 bbo513/cve-2023-7231
PoC and Disclosure for CVE-2023-7231 – Memcached Gopher RCE chain
 shodanwashere/boatcrash
Exploit for CVE-2019-19030 that affects Harbor versions <1.10.3 and <2.0.1. Can also be used to enumerate and pull public projects from higher…
 deepfence/packetstreamer
⭐ ⭐ Distributed tcpdump for cloud native environments ⭐ ⭐