
Archived
CVE-2019-5736-POC
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC
container-escapecontainer-securityexploitation+2
ryanngwh/cve-2019-5736-pocProof of concept code for breaking out of docker via runC
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 seanrickerd/cve-2024-53677
Vulnerable Environment and Exploit for CVE-2024-53677
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 freshdemo/apachestruts-cve-2018-11776
Python proof-of-concept exploit for Apache Struts2 CVE-2018-11776 remote code execution vulnerability, with Docker container for testing against…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 sonatype-workshops/struts2-rce
Exploitable target to CVE-2017-5638
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 cilium/cilium
eBPF-based Networking, Security, and Observability
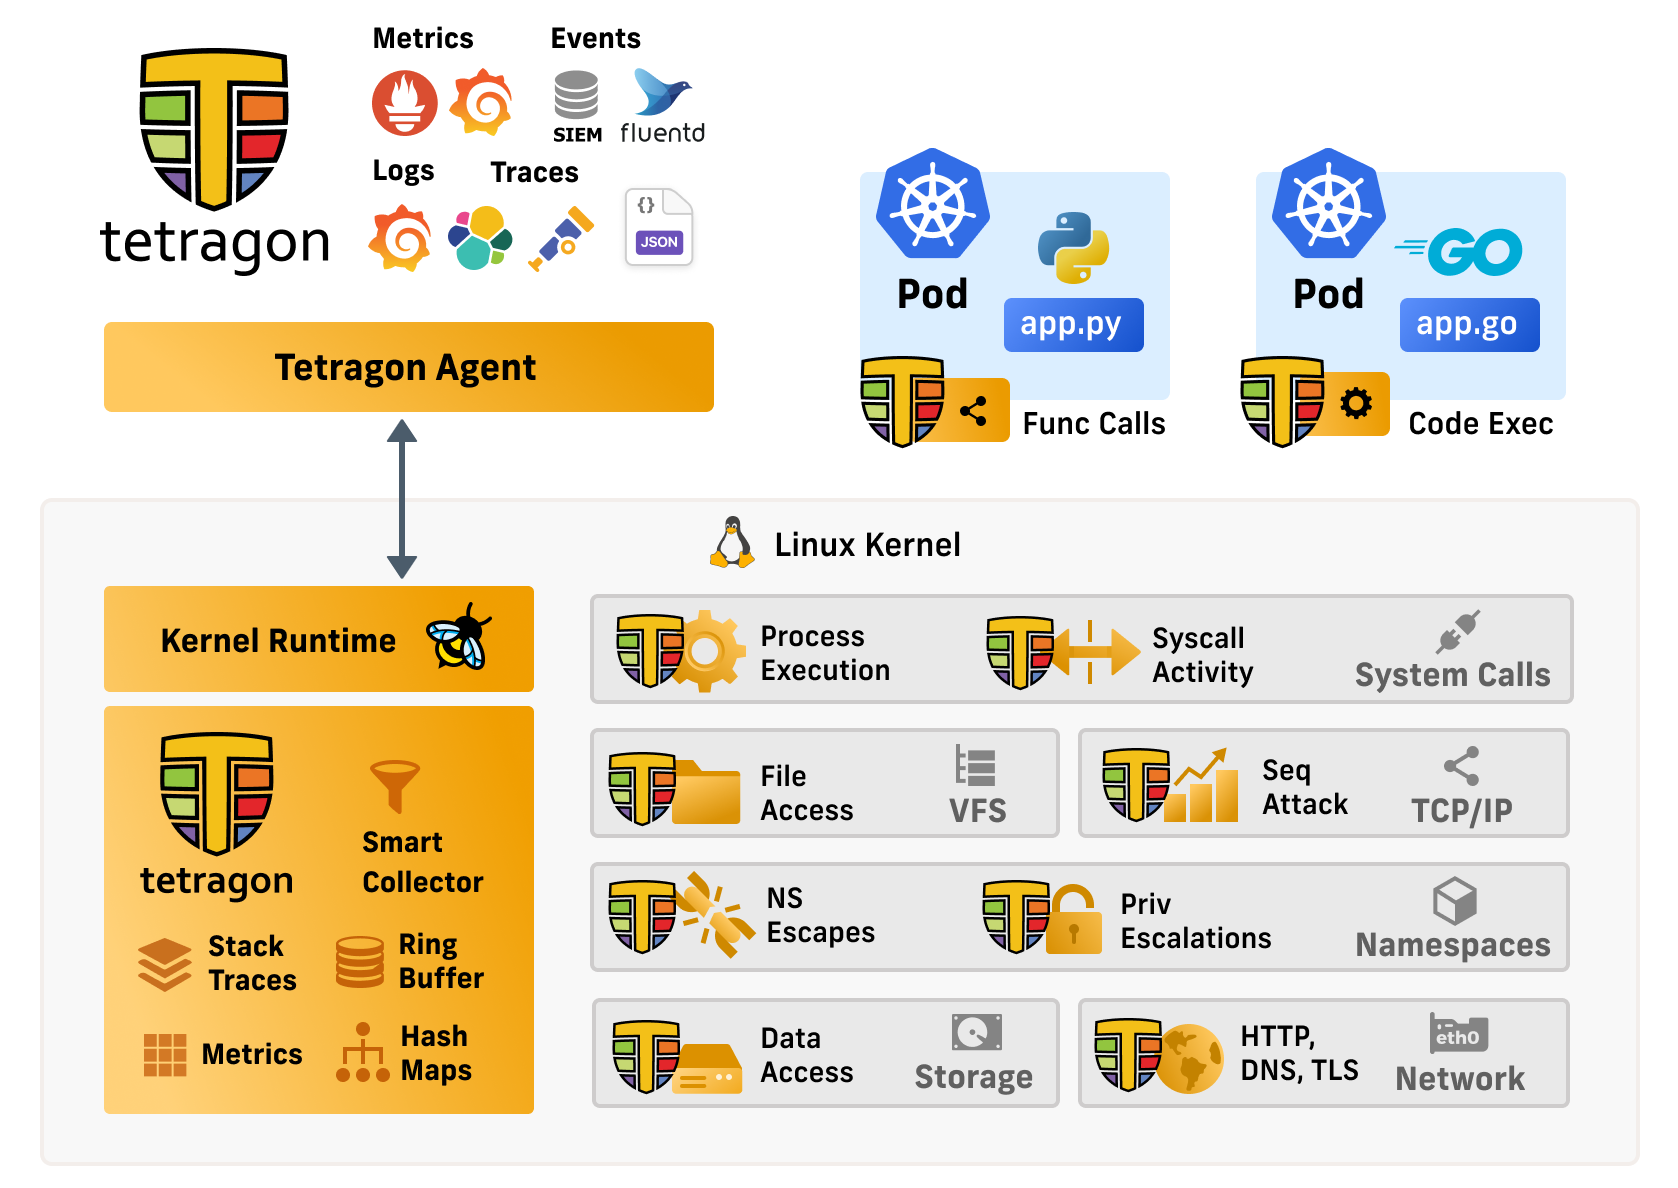 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement