
webmin_docker_and_exp
 hachp1/webmin_docker_and_exp
Dockerfiles for CVE-2019-15107(webmin RCE) recurrence including v1.890 and v1.920 with Exp for each version.
container-securityeducationexploitation+3
2
hachp1/webmin_docker_and_expDockerfiles for CVE-2019-15107(webmin RCE) recurrence including v1.890 and v1.920 with Exp for each version.
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 scherepiuk/container-escape-ebpf
POCs and Tetragon Rules for CVE-2024-21626 and CVE-2025-31133
 thirukguru/aws-perimeter
A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
 amnsecurity/helm-plugin-path-traversal-security-assessment
Professional vulnerability assessment report for Helm plugin path traversal risk, including technical analysis, impact, remediation, and mitigation…
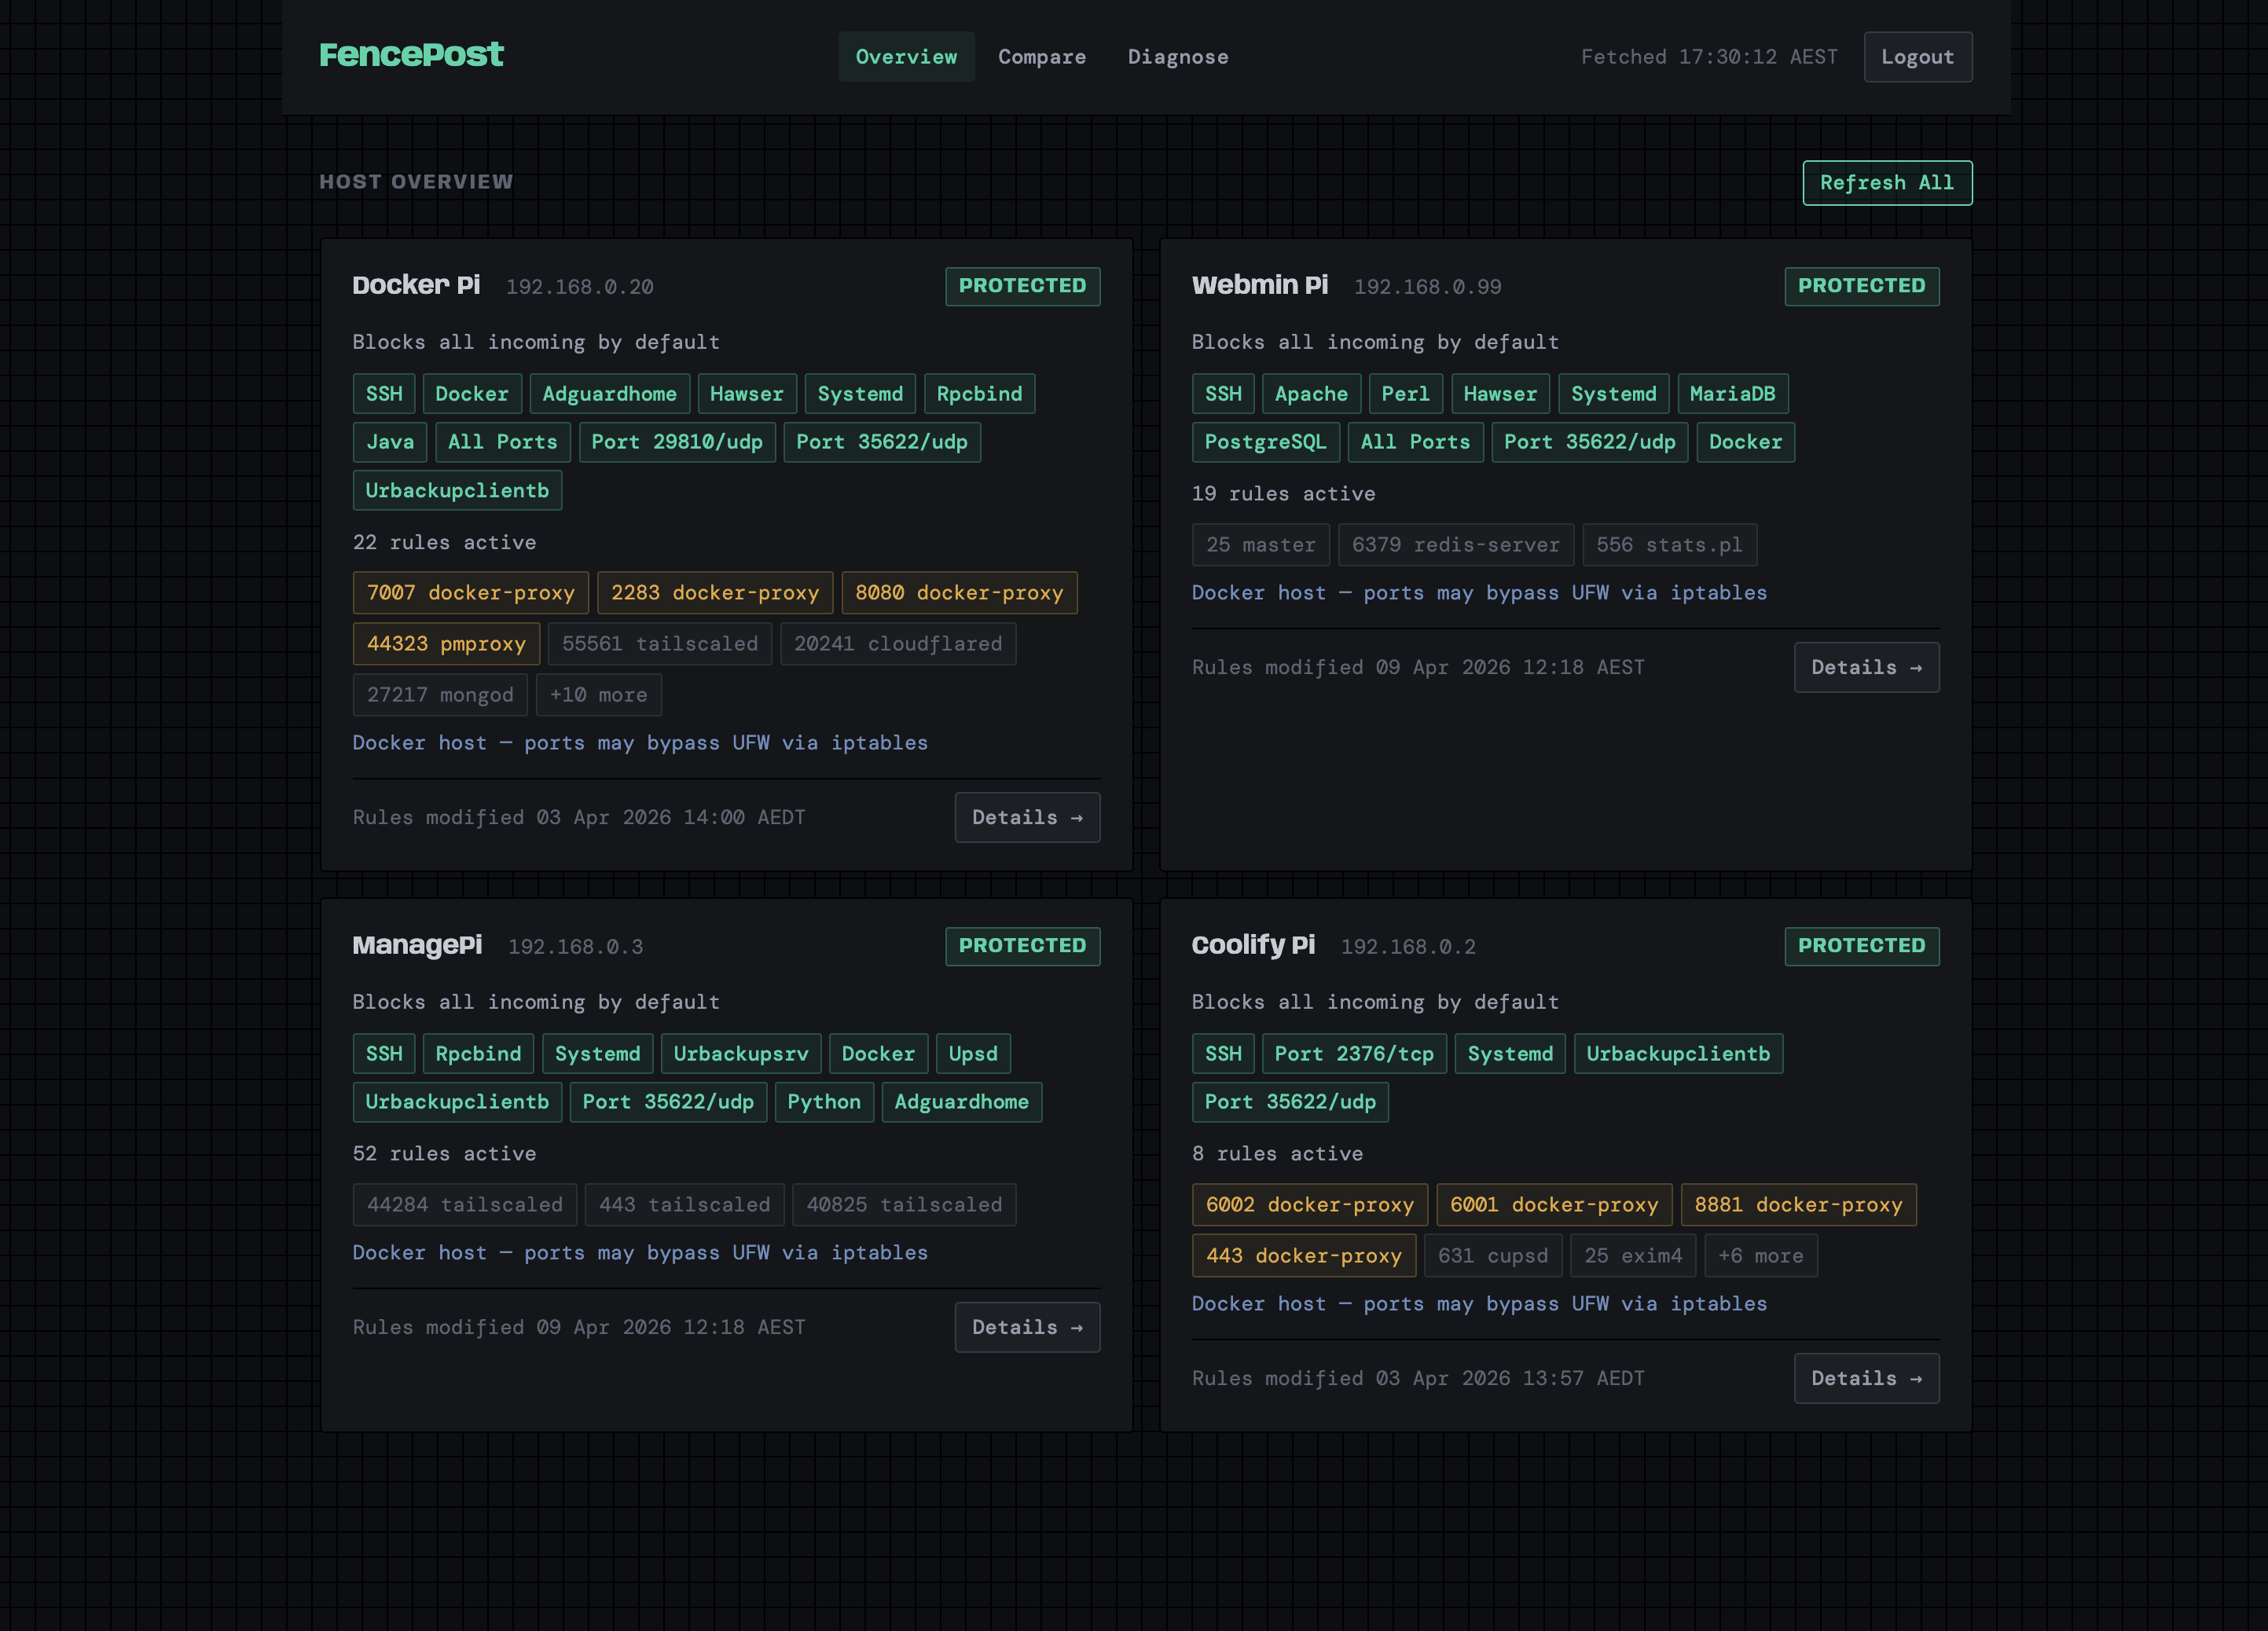 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
 sne-m23-sn/vulnerable-docker-engine
This exploit offers an in-depth look at the CVE-2021-41091 security vulnerability and provides a step-by-step guide on how to utilize the exploit…
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
 dolby360/cve-2022-27518_poc
Proof-of-concept exploit for CVE-2022-27518 targeting Citrix ADC and Citrix CPX containers, demonstrating remote code execution via crafted HTTP…
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 cybfar/cve-2021-42013-httpd
CVE: 2021-42013 Tested on: 2.4.49 and 2.4.50 Description: Path Traversal or Remote Code Execution vulnerabilities in Apache 2.4.49 and 2.4.50
 kiraly07/demo_cve-2025-3248
Educational lab simulating CVE-2025-3248 with a vulnerable Docker service and PoC exploit for hands-on security training and mitigation practice.
 visdev23/vulnerable-docker--cve-2023-30212-
This contains the necessary files and Docker to replicate A vulnerability in OURPHP that has a XSS Vulnerability (CVE-2023-30212)
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 certushack/cve-2024-3400-poc
Sets up a Docker-based Palo Alto firewall test environment and provides an exploit script to test CVE-2024-3400, enabling safe vulnerability…
 gartonchan/redis-cve-2025-62507
Exploit scripts for CVE-2025-62507, a stack buffer overflow in Redis 8.2.0. Provides x86-64 and ARM64 ROP chain exploits with shellcode generation…
 b0b0haha/cve-2026-29955
Proof-of-concept for CVE-2026-29955, a command injection vulnerability in KubePlus kubeconfiggenerator allowing remote code execution and…
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability