

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.1k3 days ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 skorokithakis/stavrobot
An AI personal assistant with a focus on security.
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 mdvpat/cve-2026-52832-poc-exploit-nuclio-dashboard
Nuclio Dashboard (NOP mode) accepts unauthenticated POST /api/functions. The spec.handler field isn't path-validated, so…
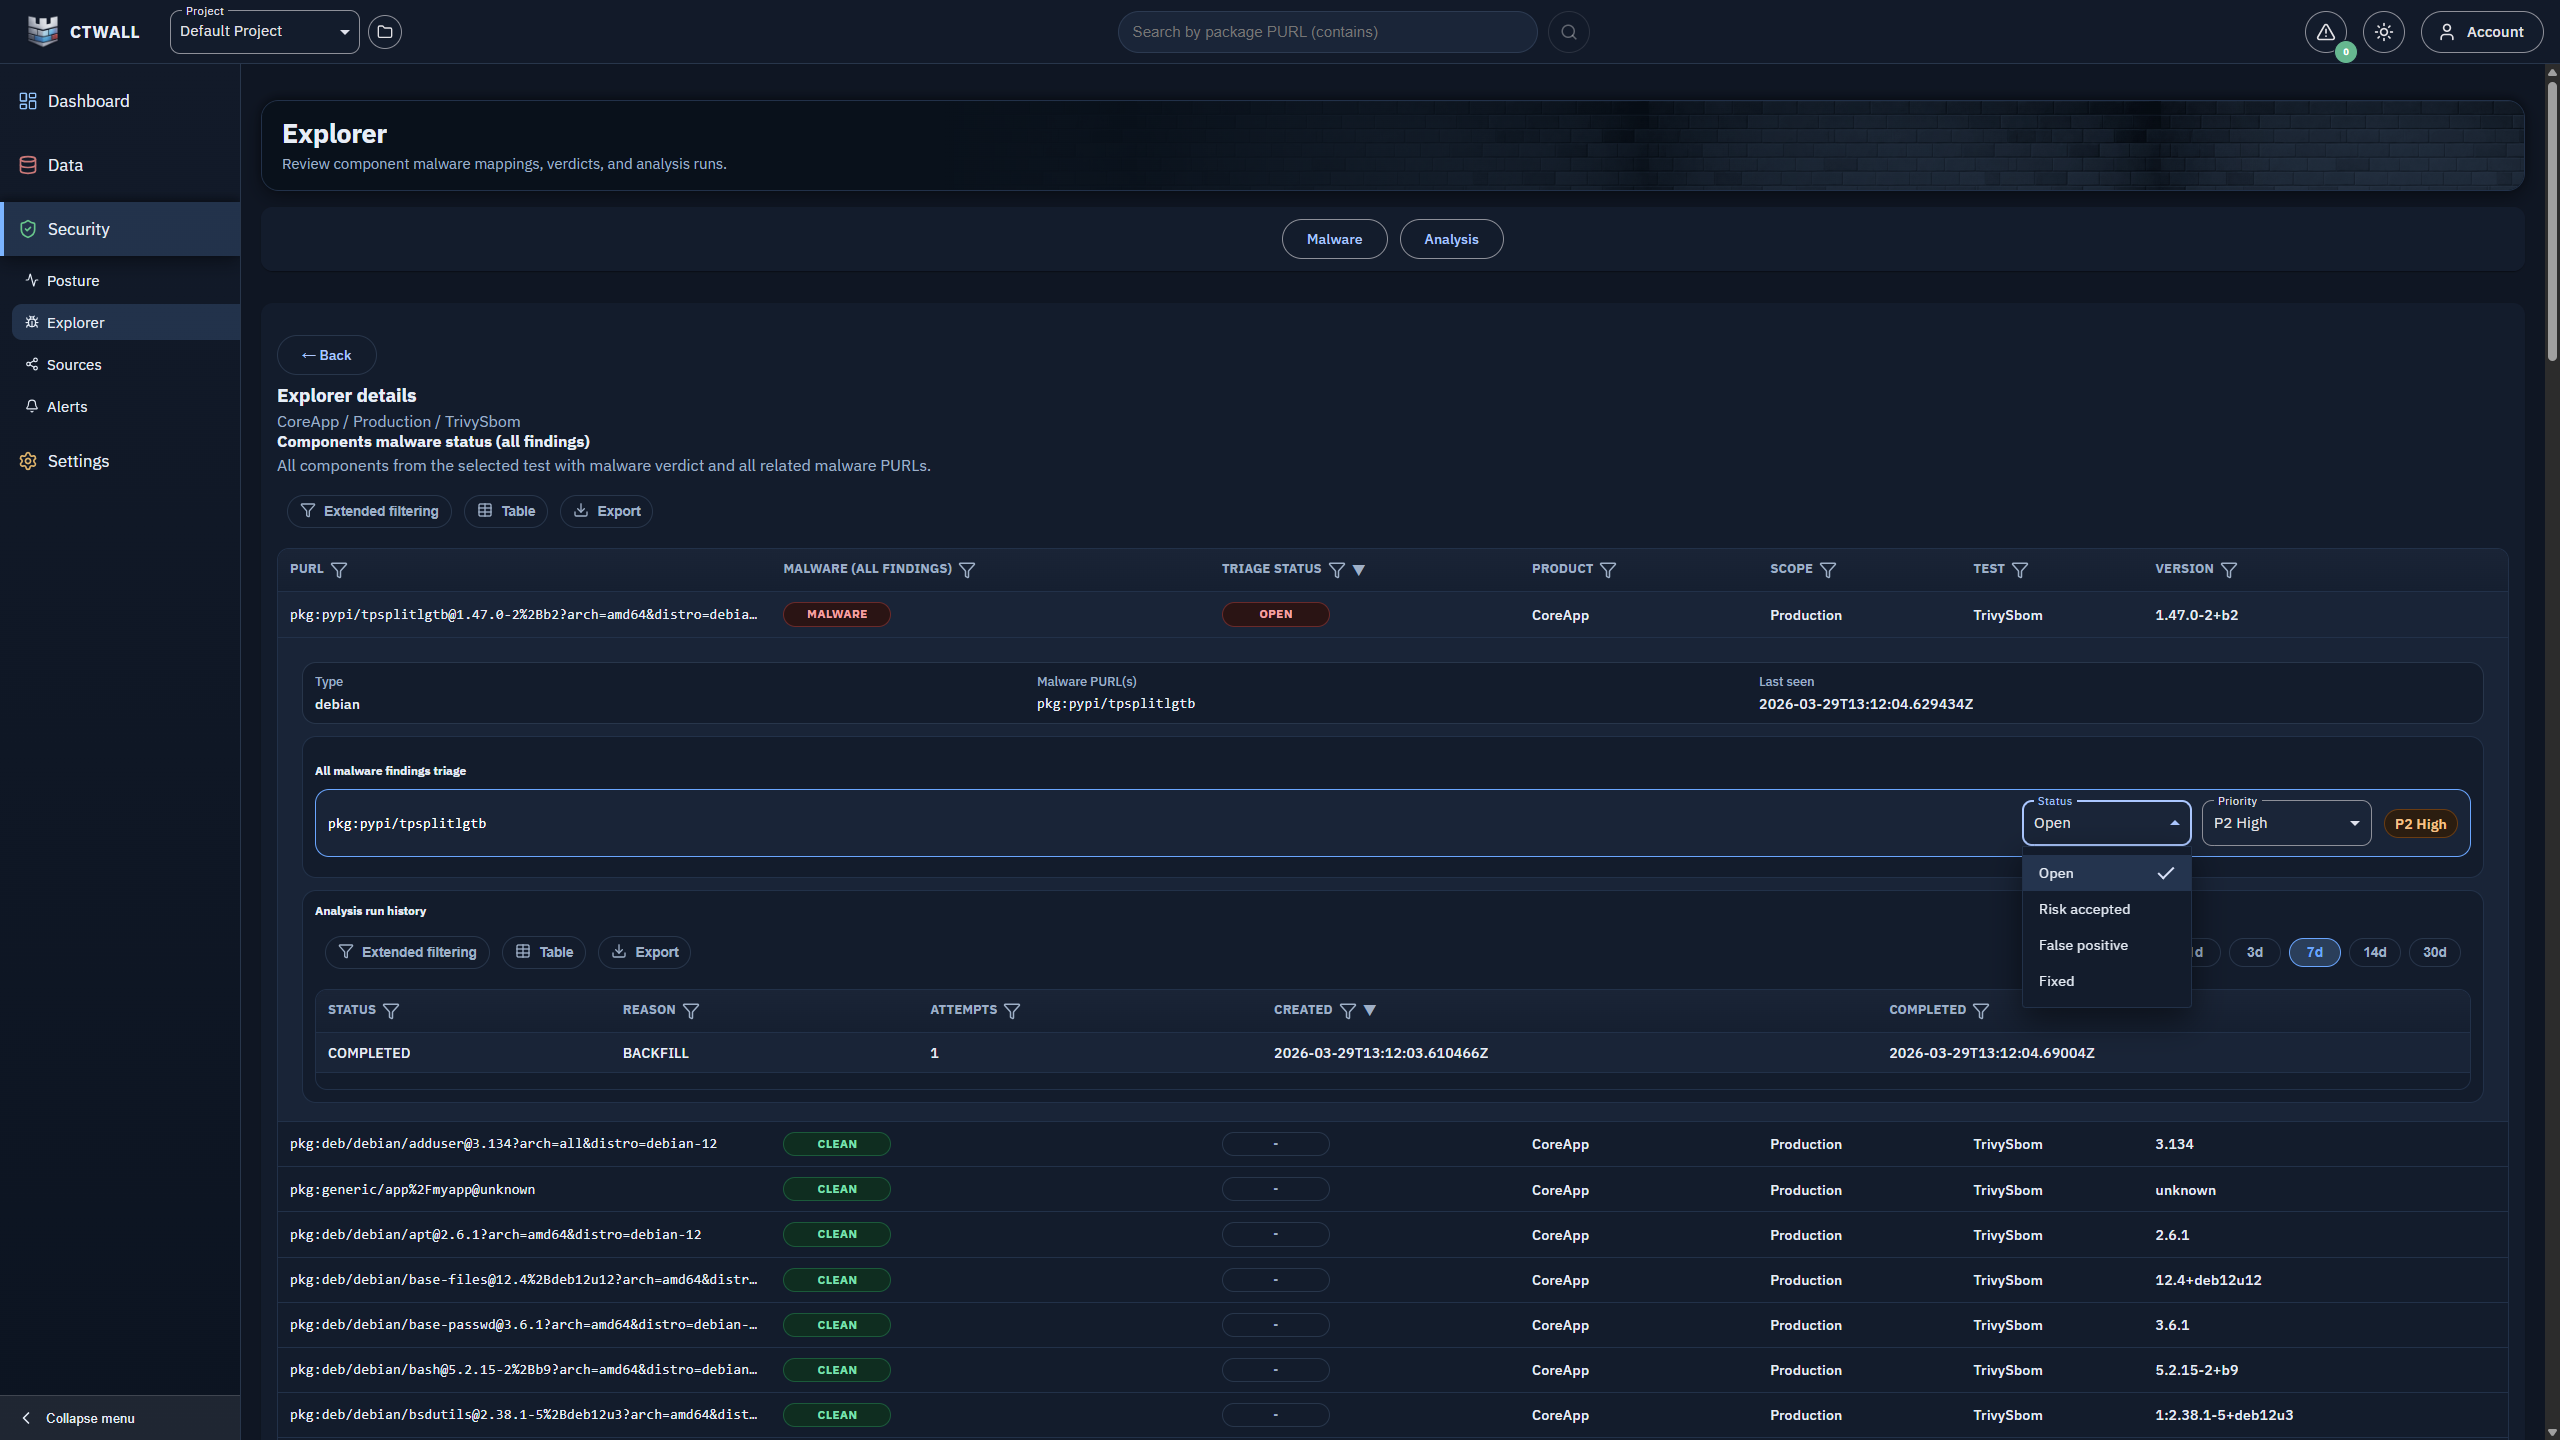 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 dolby360/cve-2022-27518_poc
Proof-of-concept exploit for CVE-2022-27518 targeting Citrix ADC and Citrix CPX containers, demonstrating remote code execution via crafted HTTP…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 cmnatic/dockerized-cve-2019-14287
Containerized and deployable use of the CVE-2019-14287 vuln. View README.md for more.