jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…

The easiest, and most secure way to access and protect all of your infrastructure.

Experimental Decoy Broker

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…

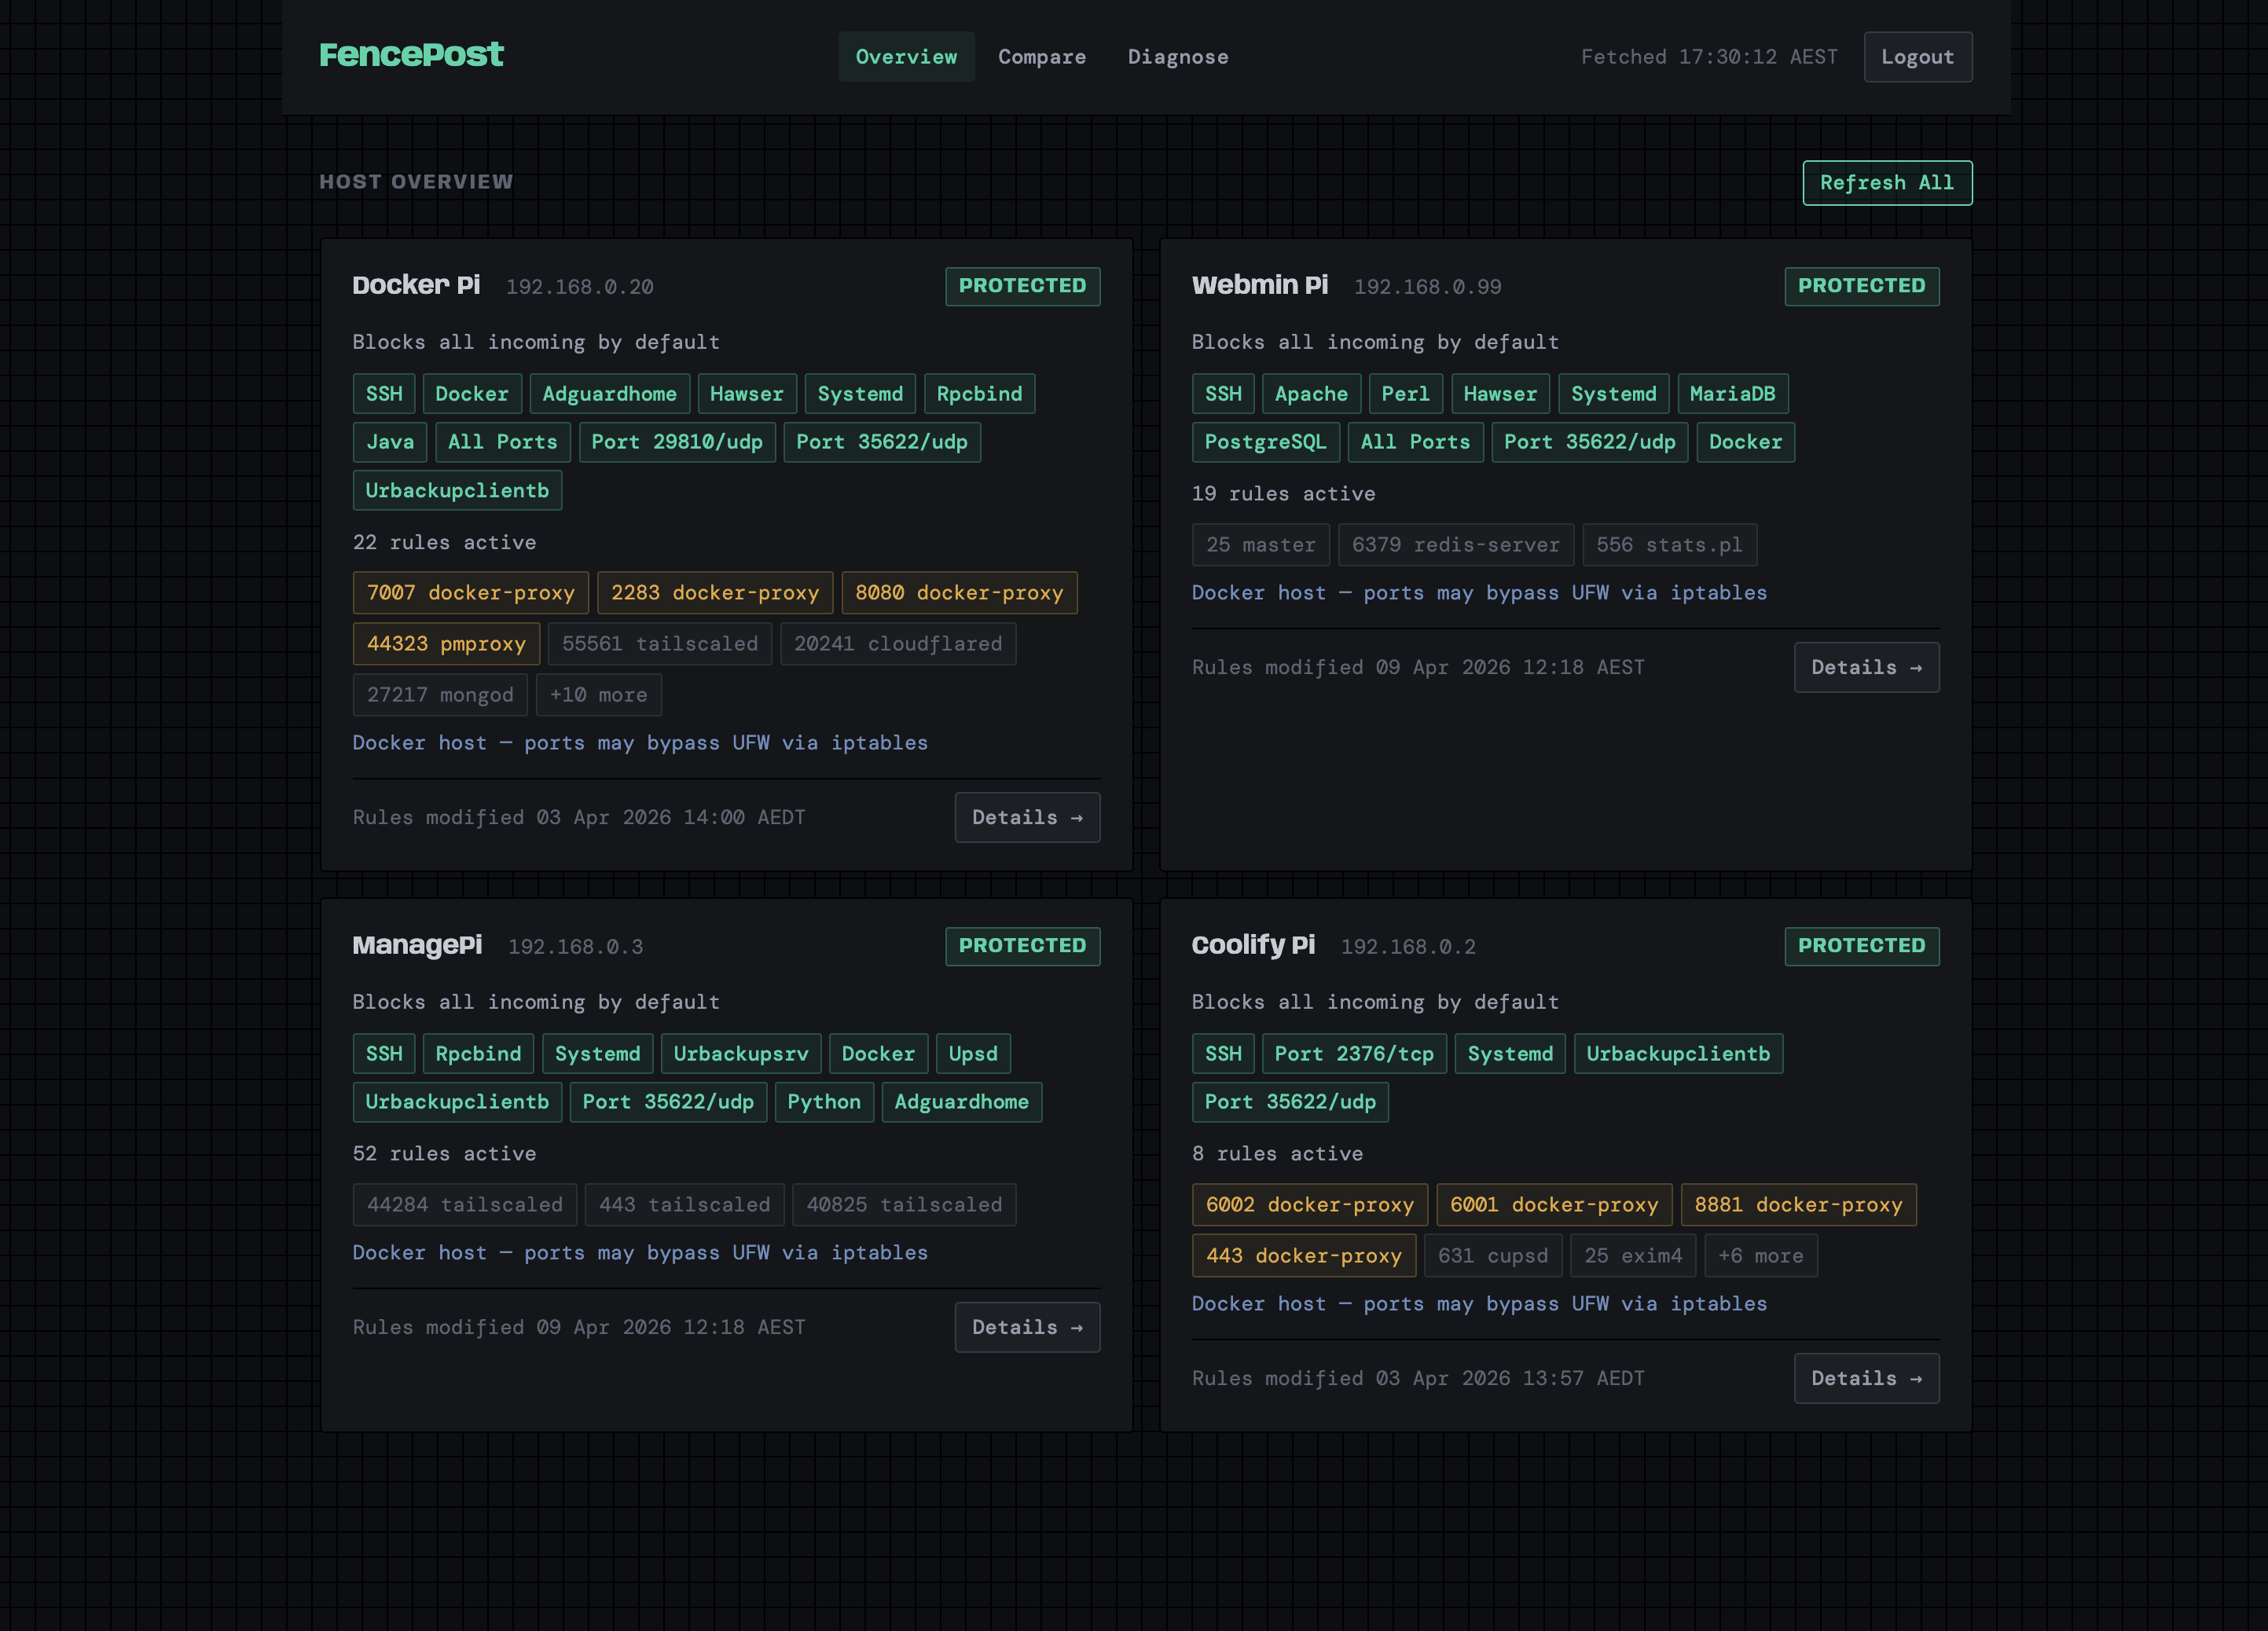
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics

Docker-based CVE-2018-10933 libssh authentication bypass exploit with patched client for testing SSH server vulnerabilities and unauthorized access…

Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…

Docker-based exploit for CVE-2018-10933, a libssh authentication bypass vulnerability, targeting SSH services on port 2222 for penetration testing.