
flatpak
 flatpak/flatpak
Linux application sandboxing and distribution framework
container-securitysecurity-virtualization
flatpak/flatpakLinux application sandboxing and distribution framework
 owasp/owasp-top-10-neocloud-and-ai-data-center-security-risks
OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…
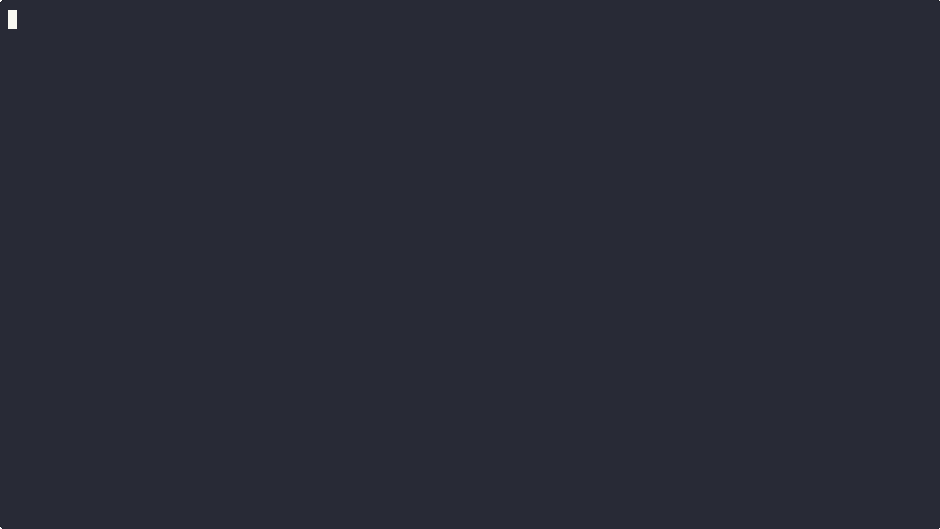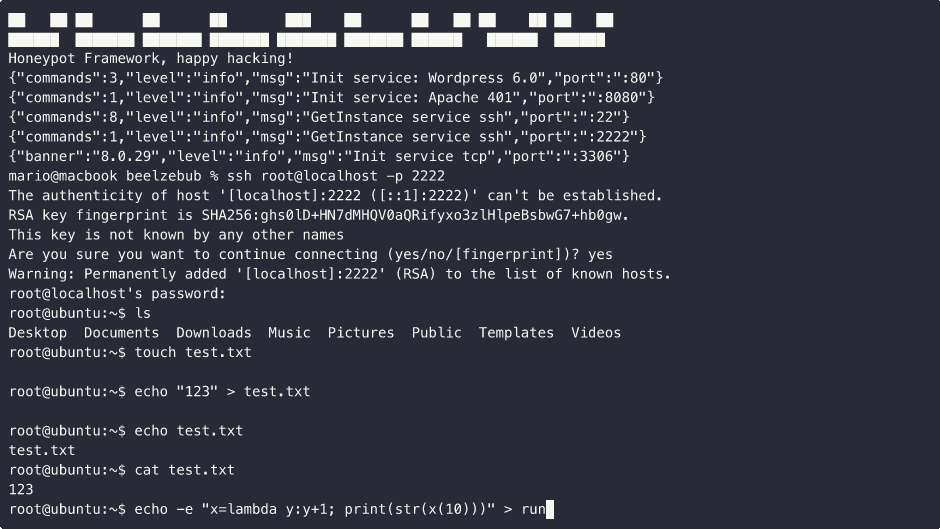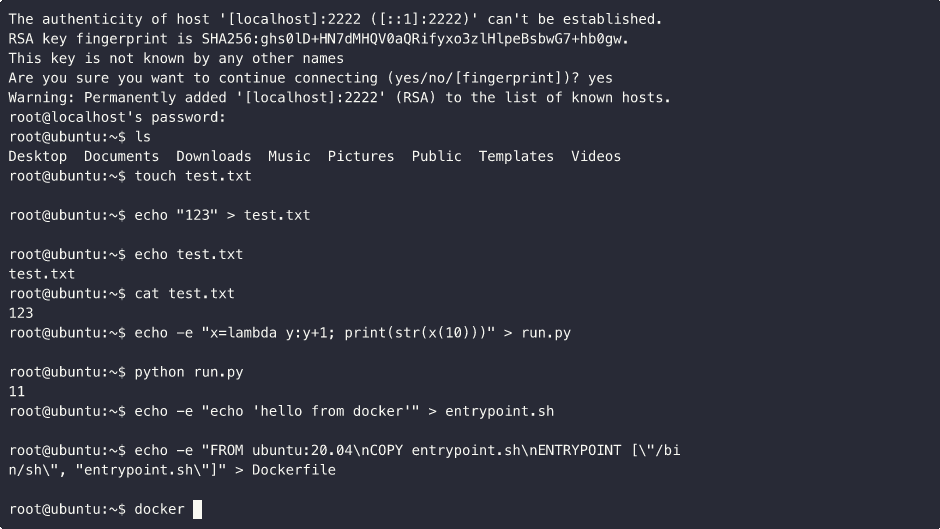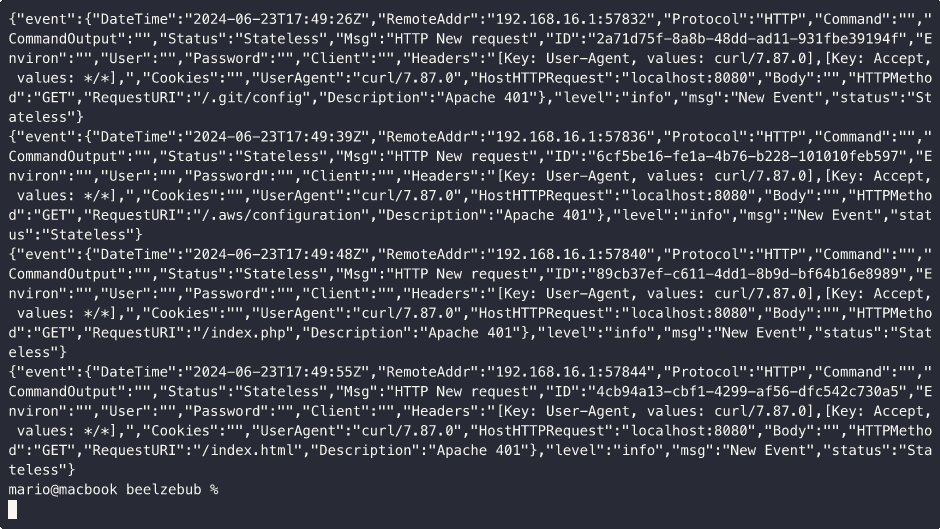 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.
 metarget/metarget
Metarget is a framework providing automatic constructions of vulnerable infrastructures.
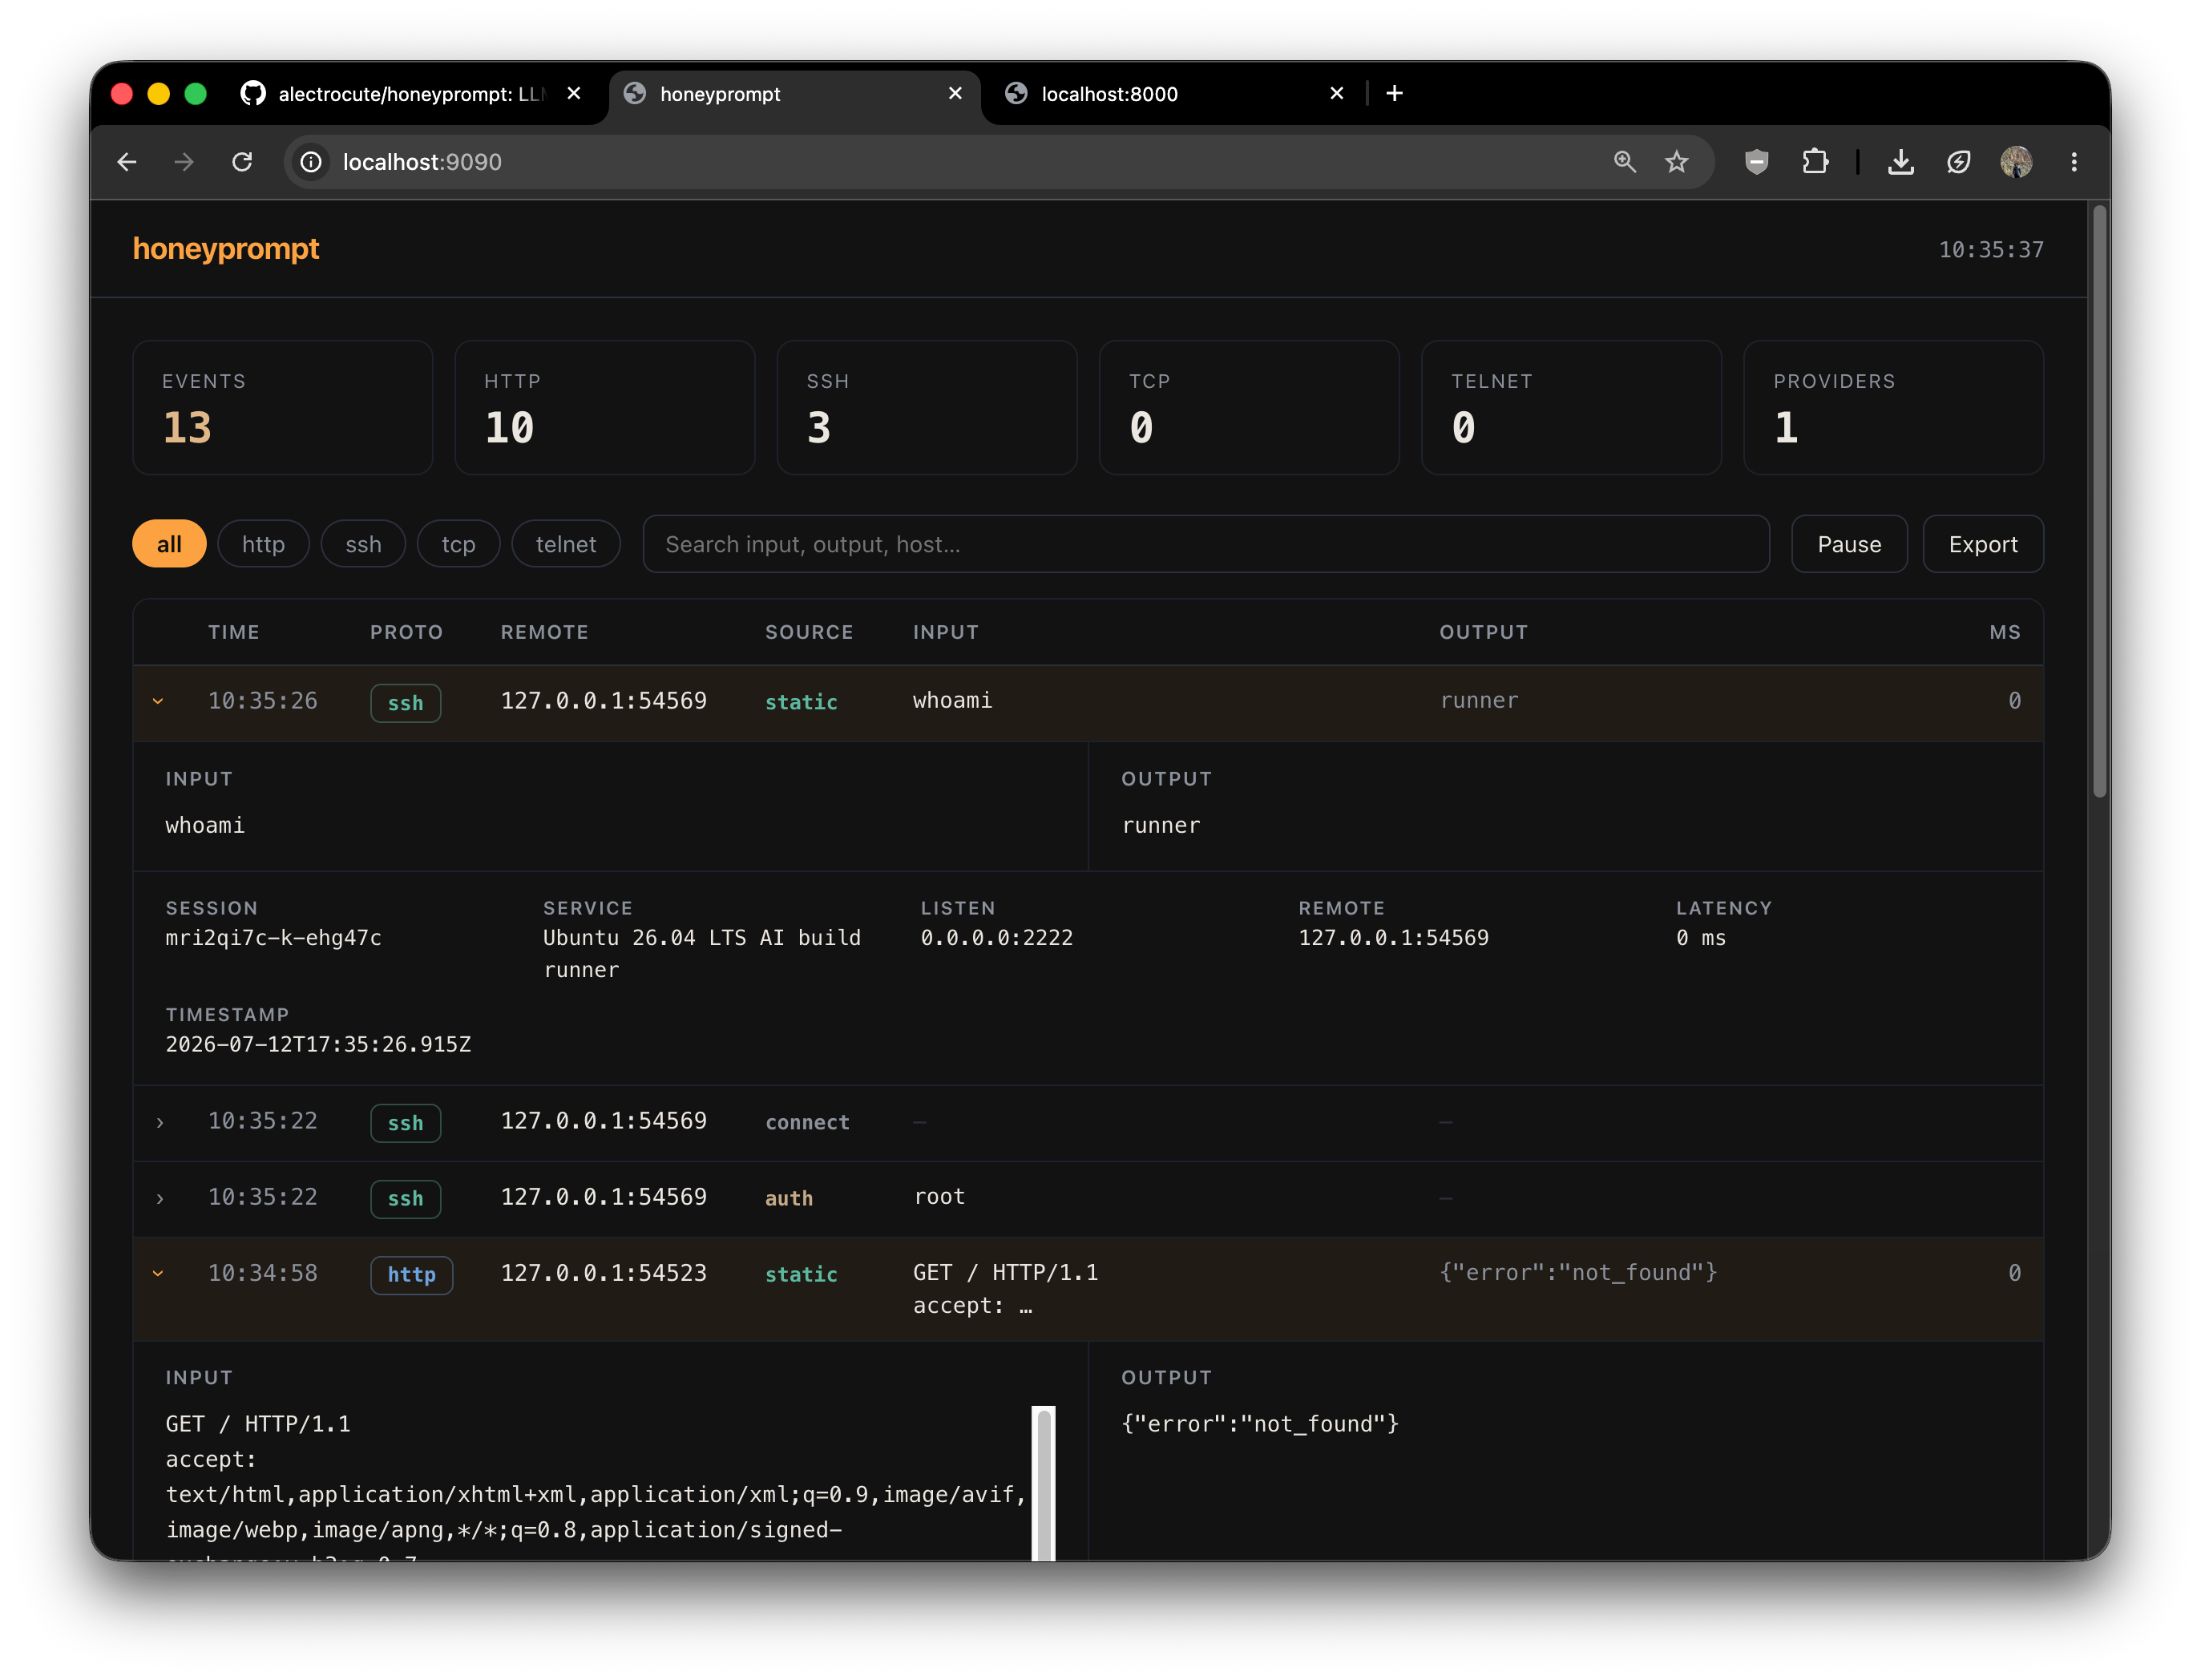 alectrocute/honeyprompt
LLM-first deception framework: "The honeypot that talks back!™"
 azdevops143/fragnesia-charan-cve-2026-46300
Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…
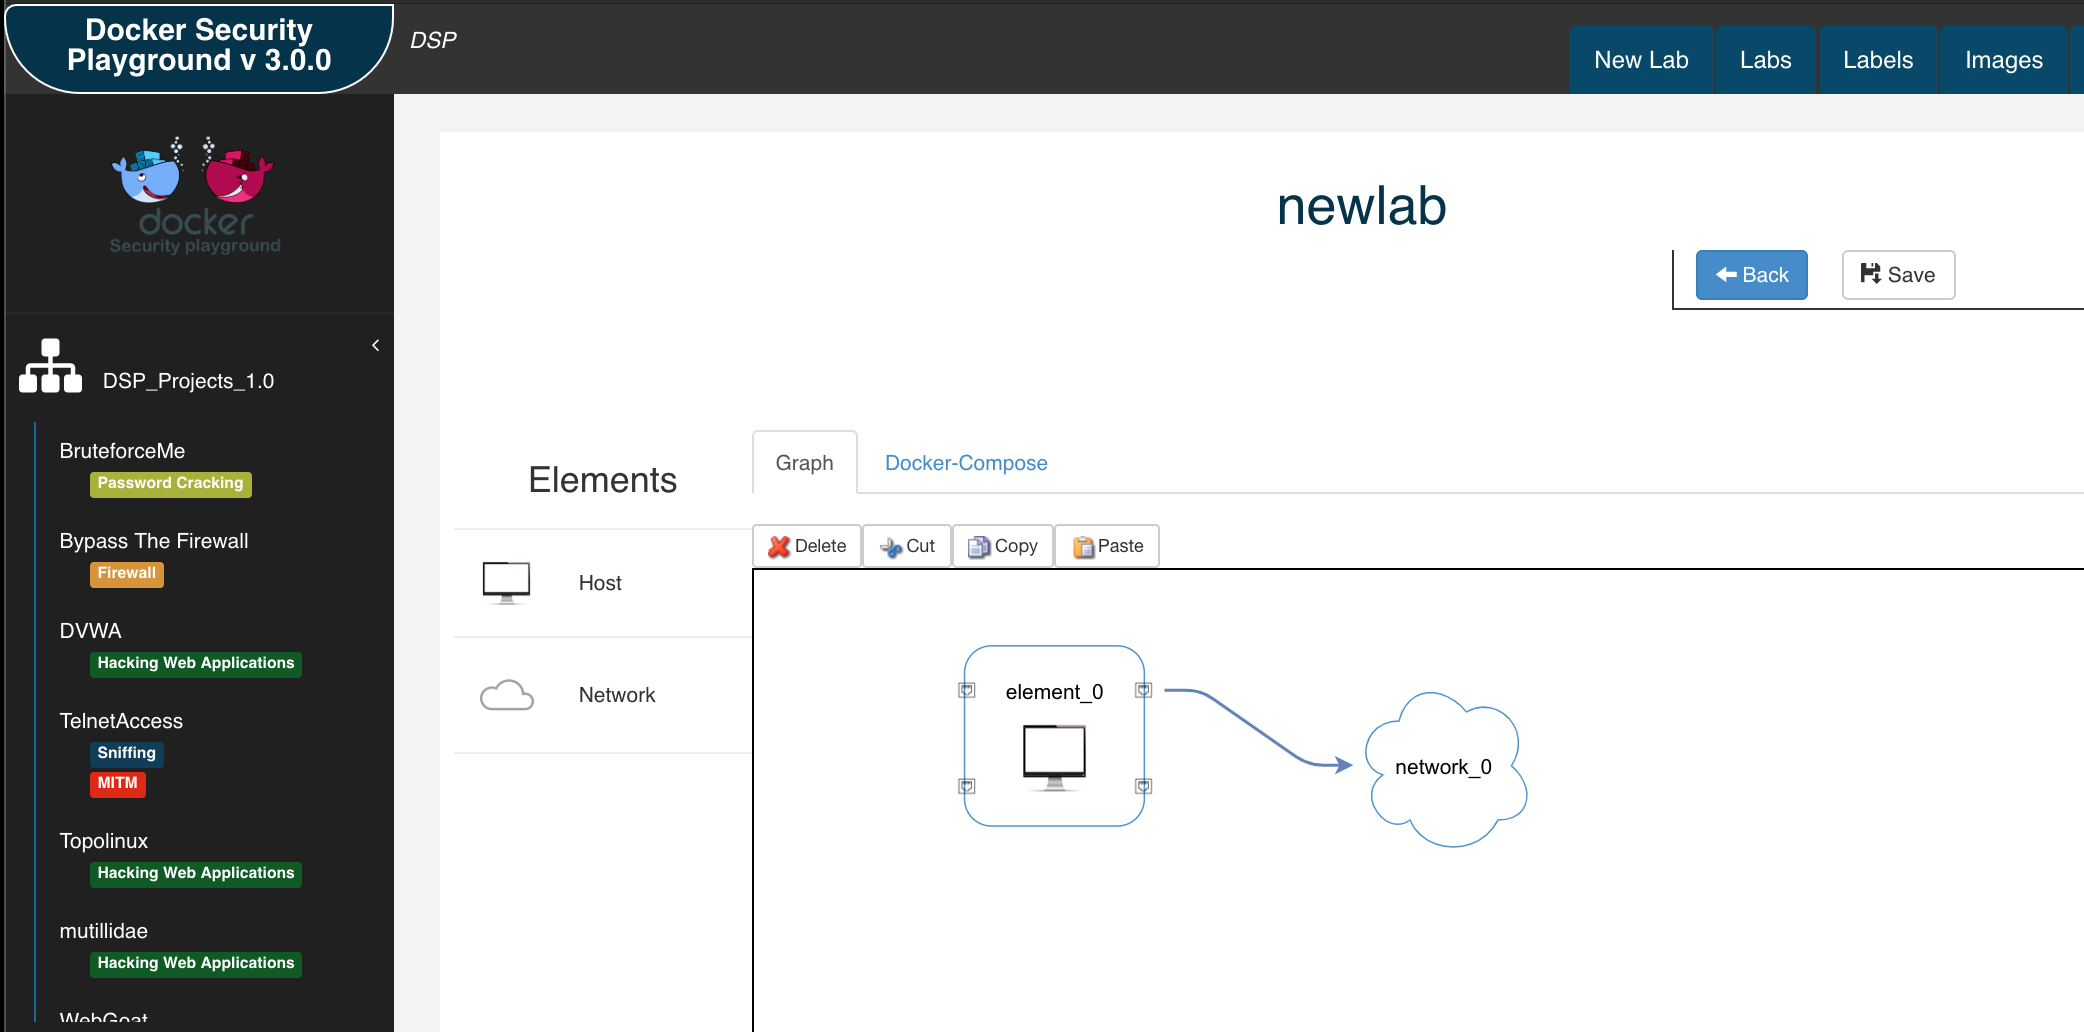 dockersecurityplayground/dsp
A Microservices-based framework for the study of Network Security and Penetration Test techniques
 flame-11/cve-2018-15133-laravel-framework
Reproducible Docker lab for CVE-2018-15133 (Laravel Framework token unserialize RCE) with a known APP_KEY and a /poc route for testing exploit…
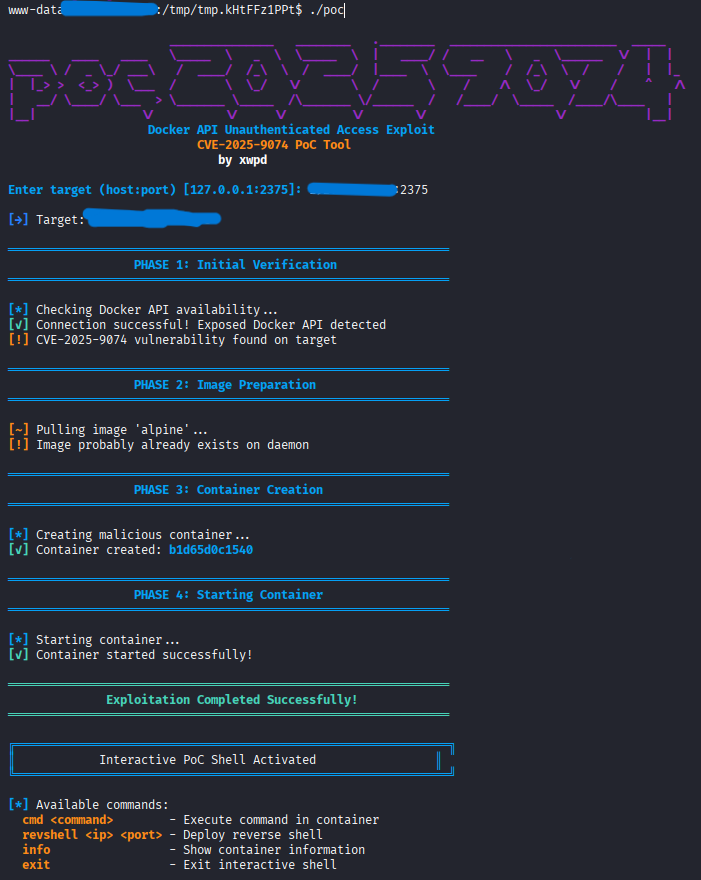 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
 fluidattacks/makes
A software supply chain framework powered by Nix.
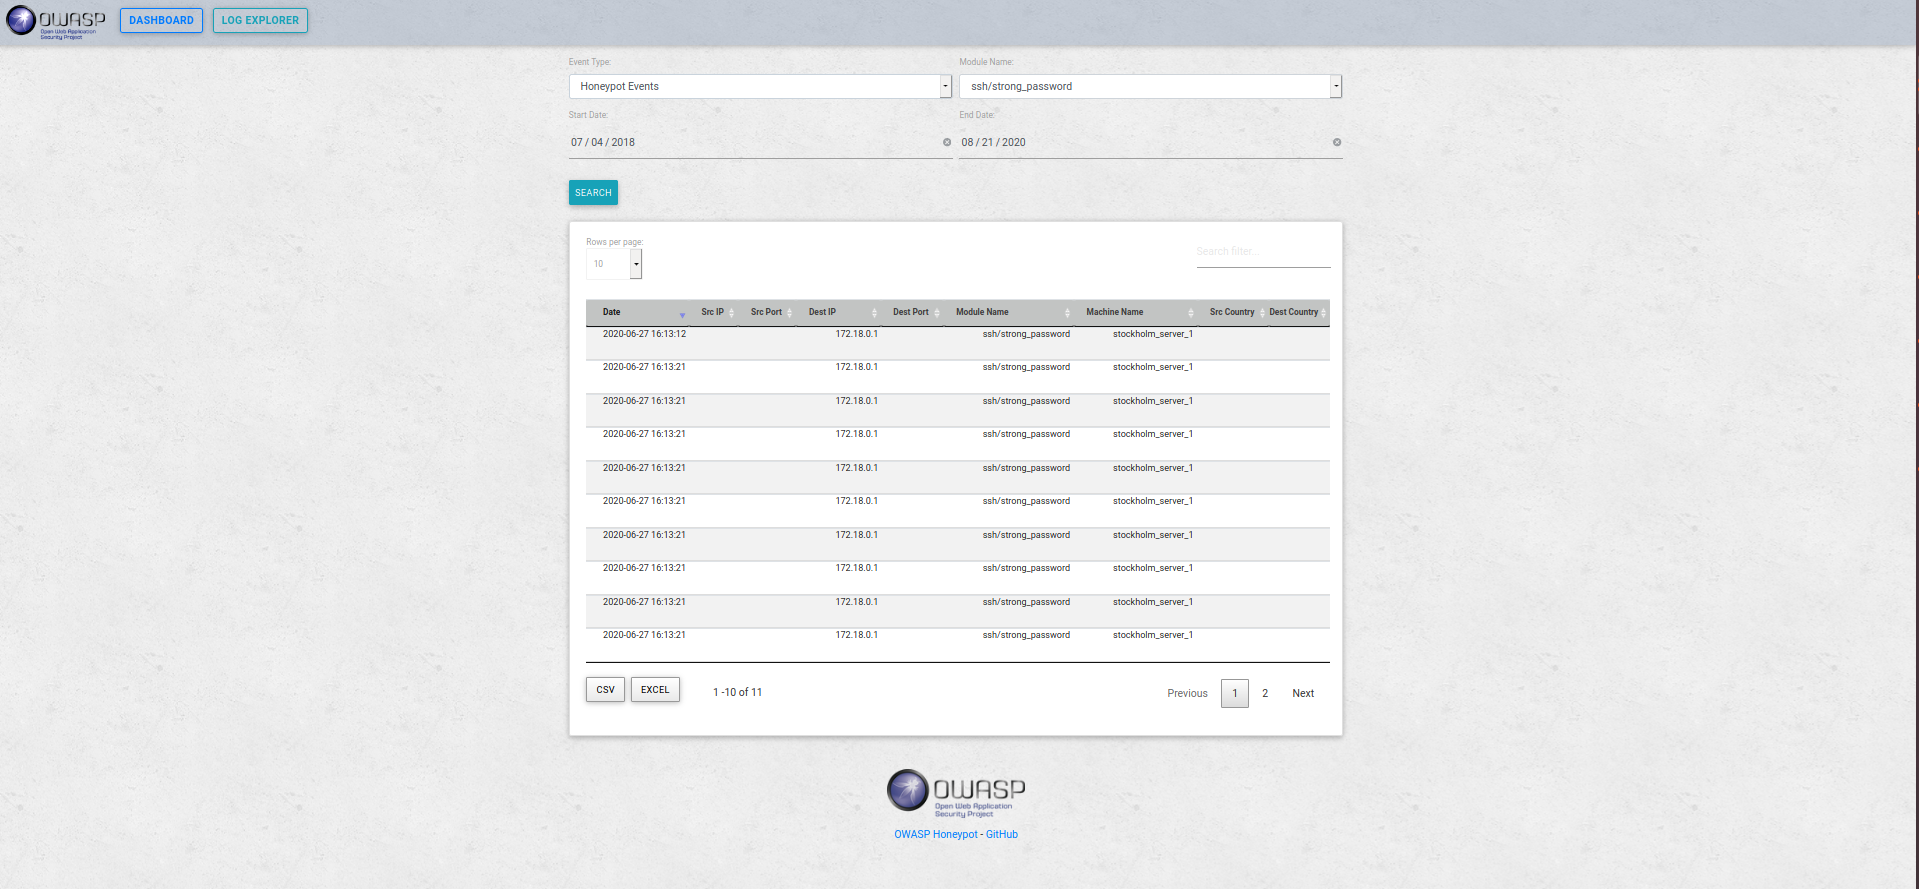 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 cybersecsi/dockerized-android
A container-based framework to enable the integration of mobile components in security training platforms
 sonatype-workshops/struts2-rce
Exploitable target to CVE-2017-5638
 cved-sources/cve-2019-9194
Docker container with CVE-2019-9194 for practicing vulnerability exploitation in a controlled environment. Part of the Cved vulnerable container…
 cved-sources/cve-2019-6340
Docker container for CVE-2019-6340 exploitation lab, part of the Cved vulnerable container management framework for practicing Drupal security…