

ziti
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
api-securityauthentication-authorizationcloud-security+7
4.4k
openziti/zitiZero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 portbuster1337/cve-2026-27771
CVE-2026-27771 - Gitea/Forgejo Container Registry Auth Bypass Exploit PoC - Pull private container images without authentication
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 ashleyt3/docker-socket-risk-demos
Companion source for YouTube video "Stop Mounting docker.sock — Run Trivy Without Giving Away Root Access — (inspired by CVE-2026-33634)"
 getanteon/anteon
eBPF-powered Kubernetes monitoring and performance testing platform that automatically generates service maps, tracks real-time metrics, and runs…
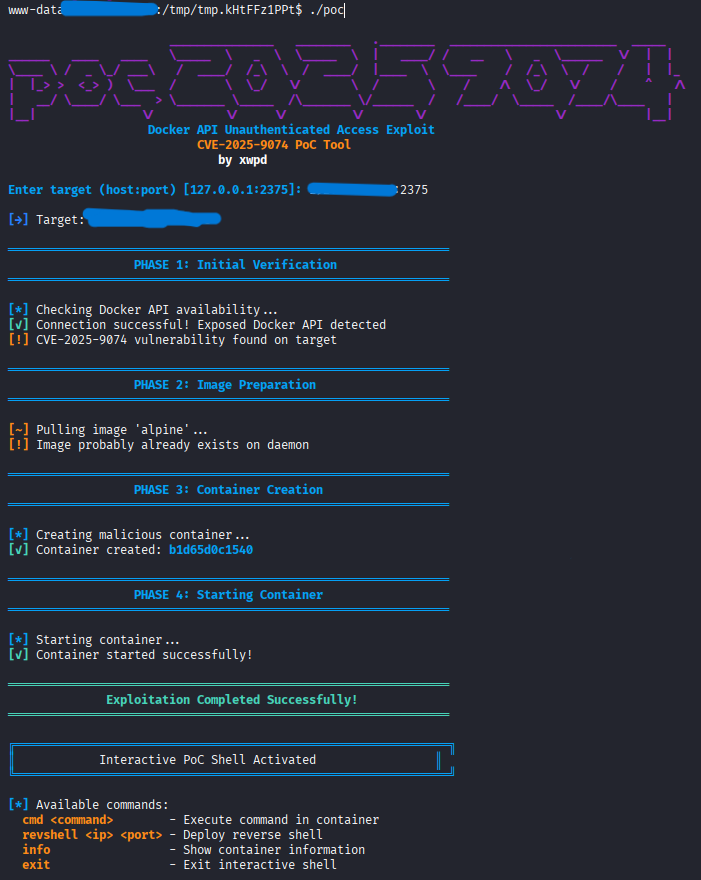 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 1w4y/ingressnightmare-rce-poc
PoC for CVE-2025-1974: Critical RCE in Ingress-NGINX (<v1.12.1) via unsafe config injection. Exploitable from the pod network without credentials,…
 vt0x78/cve-2024-31989
Exploit for CVE-2024-31989.