

owasp-ctf-in-a-box
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
container-securityctfdevsecops+6
21
owasp/owasp-ctf-in-a-boxSelf-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 androidteacher/cve-2025-64424-coolify-
Containerized CTF lab for learning and exploiting CVE-2025-64424, a command injection RCE in Coolify. Includes vulnerable environment, walkthrough,…
 xxxtectationxxx/react2shell-cve-lab
A self-hosted vulnerable Next.js environment running on Docker for simulating CVE-2025-55182. Built for educational security research and CTF…
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 controlplaneio/simulator
Kubernetes Security Training Platform - focusing on security mitigation
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
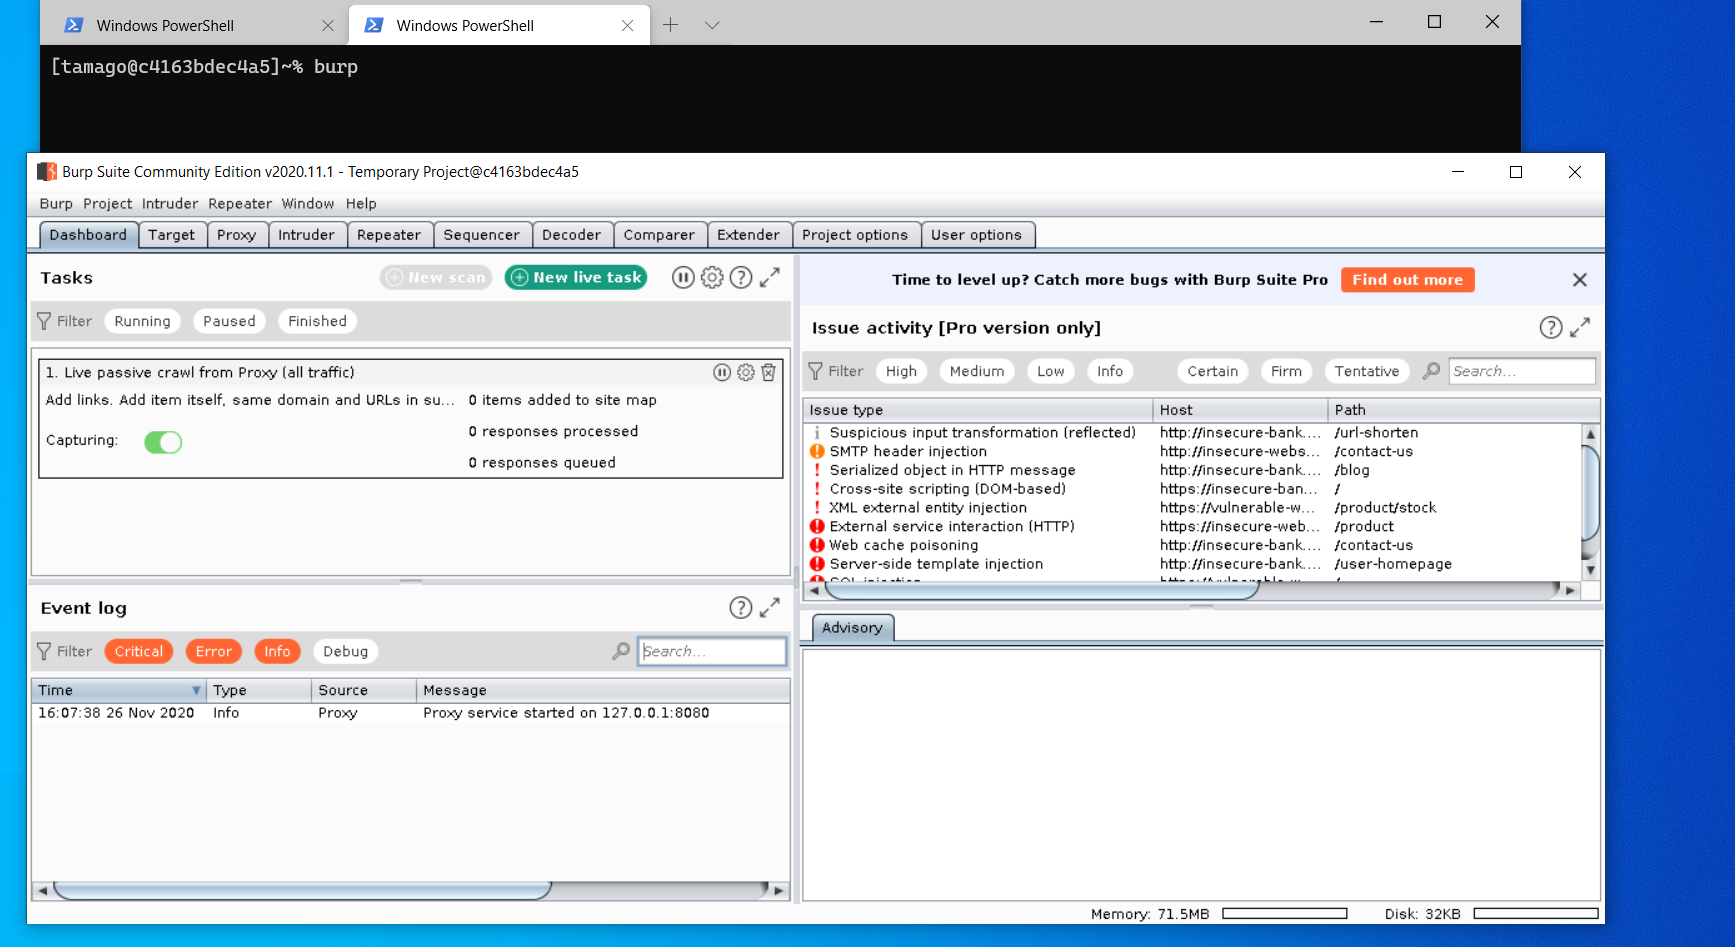 himazawa/bento
Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.