sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

This repository contains the scanner component for Greenbone Community Edition.

🛡️ Open-source and cloud-native Web Application Firewall (WAF)

Linux application sandboxing and distribution framework

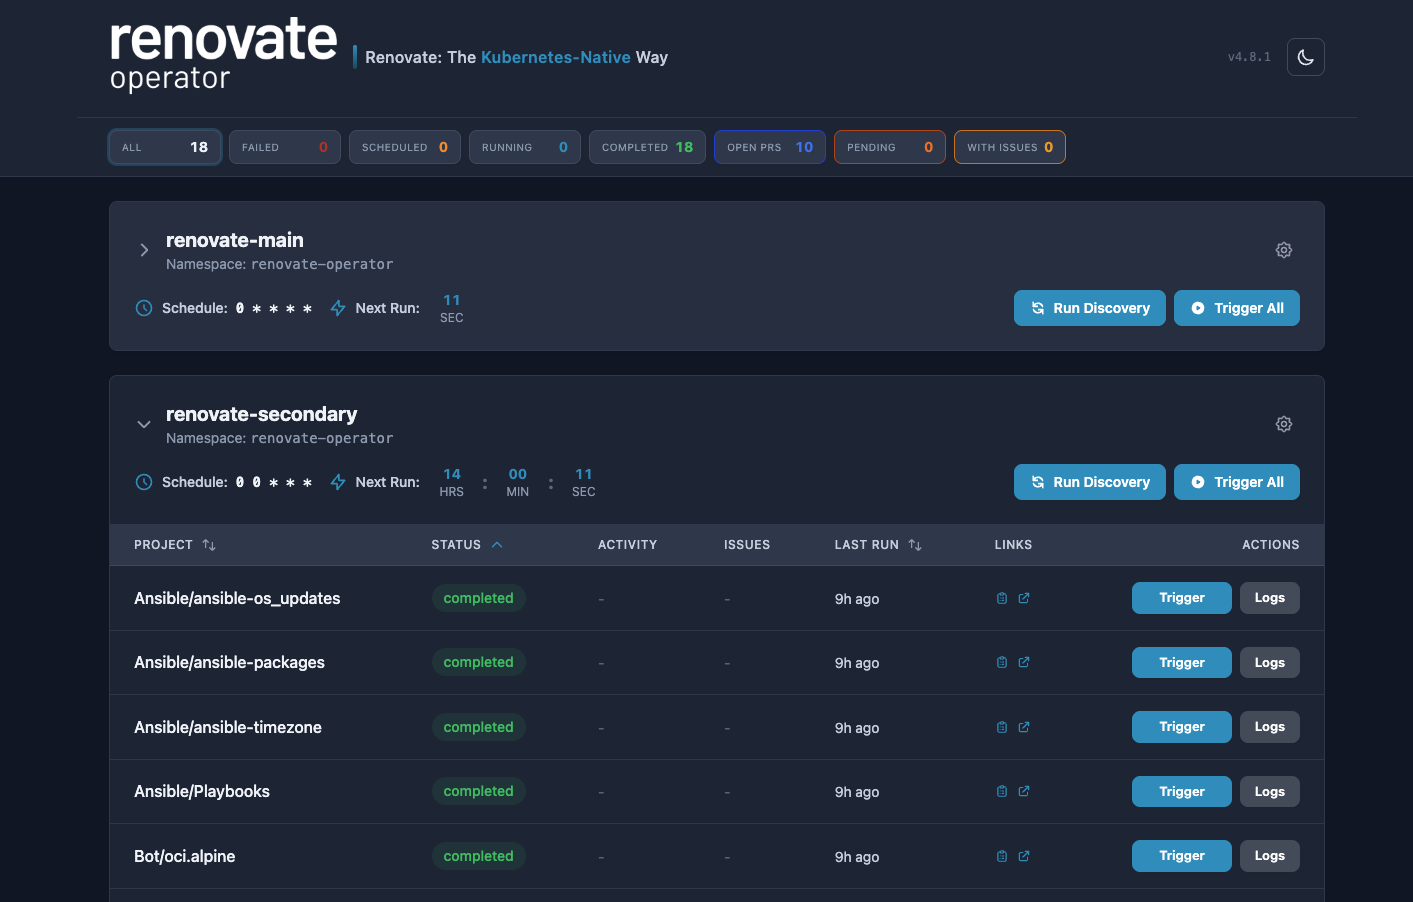
Operator to streamline renovate executions in Kubernetes

eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…

Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.

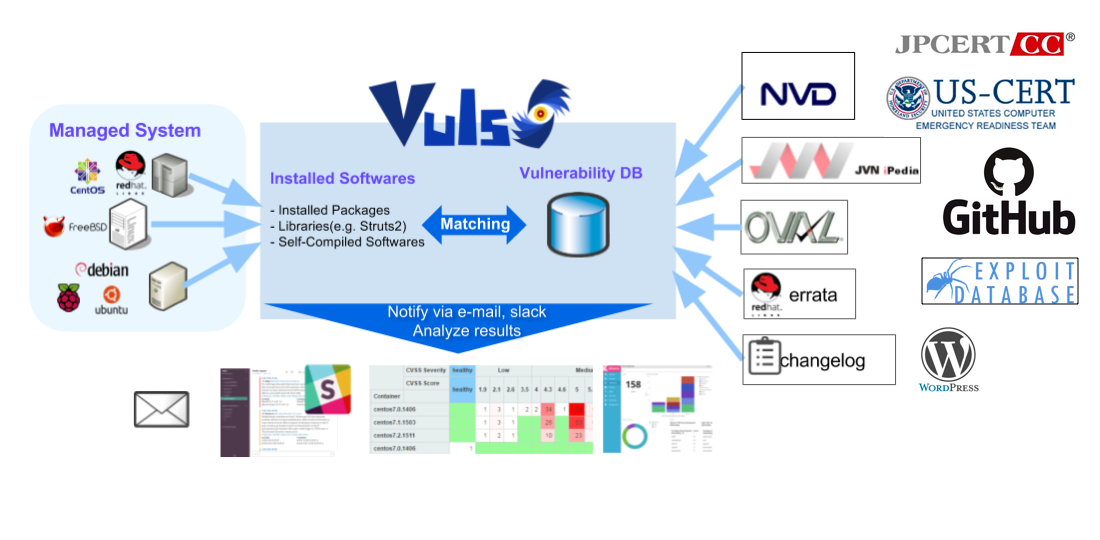
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

Dockerized vulnerable web application demonstrating the Log4j CVE-2021-44228 remote code execution vulnerability for educational exploitation and…

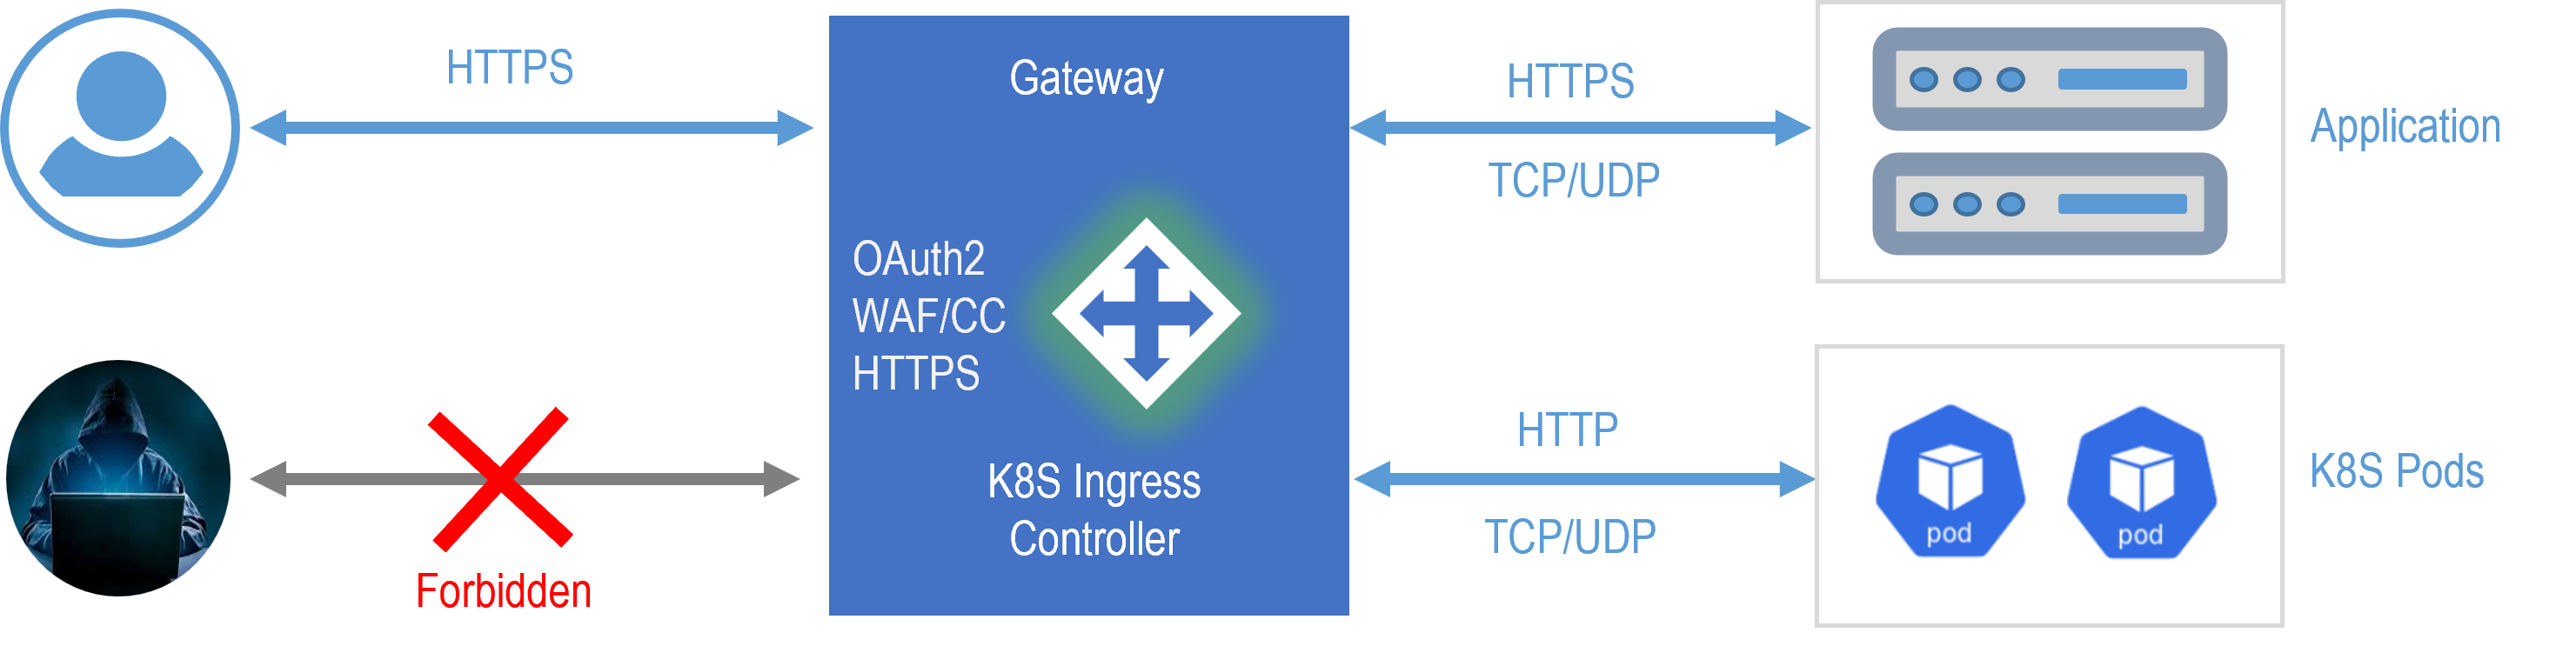
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…

AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…

Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.

Deliberately vulnerable web application portal with a containerized backend, designed for practicing exploitation of CVE-2021-44228 and container…

Superseded by https://github.com/aquasecurity/trivy-operator

CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具

Educational environment for LTAT.04.022 Homework 4.

Open Source Cloud Native Application Protection Platform (CNAPP)